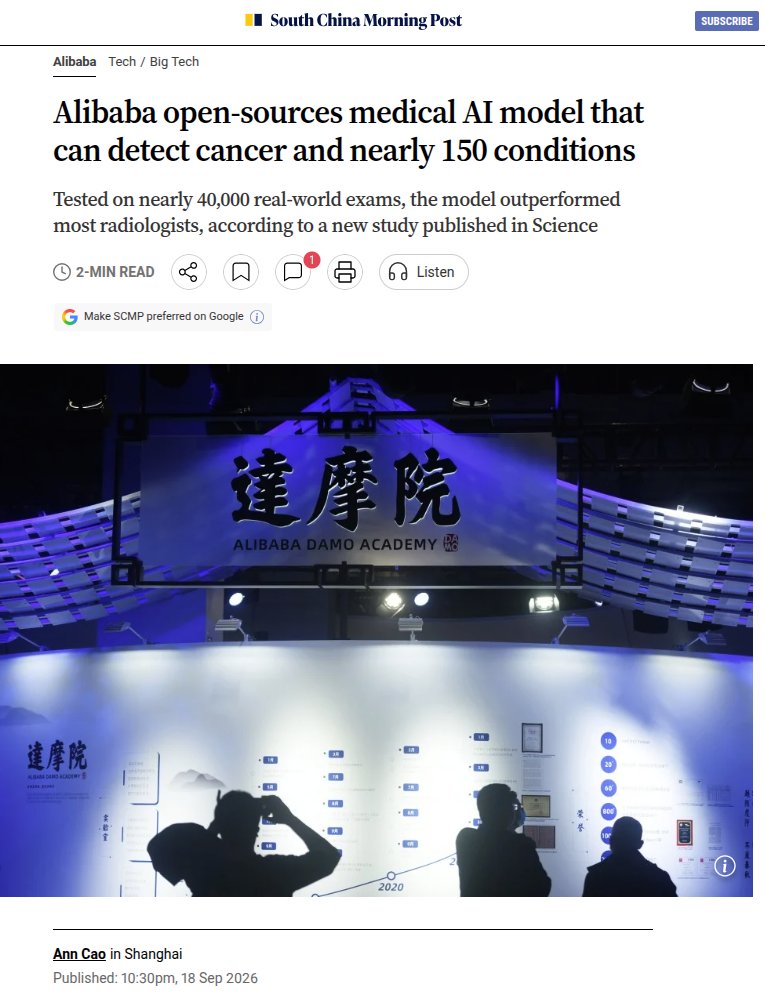
News like this one right here are the reason that the powers that be will do anything they can in order to prevent people from using self-hosted, open-source AI models
@CR1337@Google And with todays camera quality and how people would wave you can extract fingerprints. And we all know that this wont be done and stored because we trust big companies.
‼️ LG stops sending security updates to TVs if you do not consent to them wiretapping your home and sending your and your household's voice recordings to their AI.
And it gets worse. LG's new TV terms quietly turn you into the compliance officer: under section 6(d), it is your "sole responsibility" to get consent from anyone whose voice the set's AI features might capture, and to warn household members and guests, all to satisfy wiretapping and eavesdropping laws.
Those voice services ship enabled by default. If a guest objects, LG's remedy is that you go disable the microphone. And owners of older sets who refuse the new webOS terms stop receiving security patches.
@MoneyMoneyApp Ich habe inzwichen schon die 2.4.72 die hier noch gar nicht erwähnt wird und komme damit aktuell nicht mehr in die Comdirectbank. Sind da Probleme bekannt?
@soulver The AppStore isn't a real purchase as Apple can revoke/cancel it whenever they want and they already did it multiple times with Apps they dont like anymore. Never will use the AppStore.
@CR1337 Have you checked the password manager Enpass? In my opinion this is a good option too as it stores all the data local only. It's not that well known and missing in nearly every comparisson/test. It is more or less a replacement for 1Password7 bevor they went 'all cloud mode'.
„Dieses System soll Daten aus Hunderten NHS-Einrichtungen zentral zusammenführen. Interne Dokumente zeigen nun, dass externe Palantir-Mitarbeiter „unbegrenzten Zugriff“ auf personenbezogene, identifizierbare Patientendaten erhalten – nicht nur auf anonymisierte Statistiken.“
https://t.co/JQMT3JtV1D
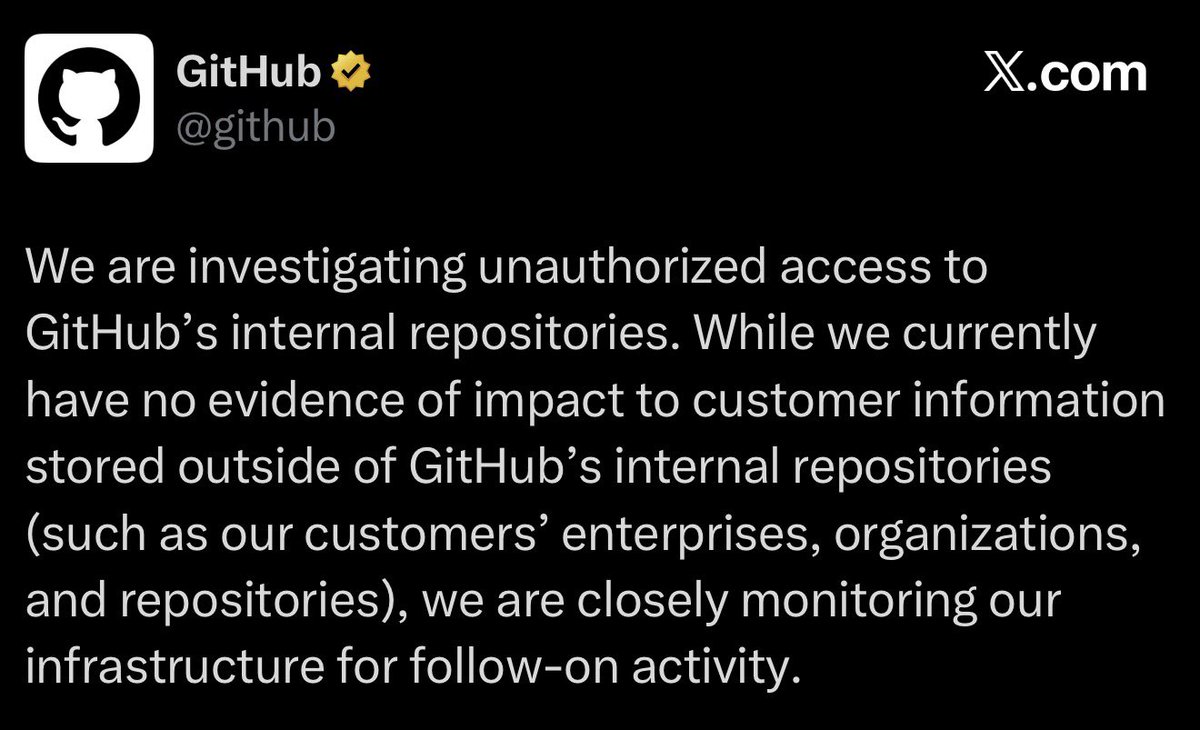
‼️🚨 BREAKING: GitHub has been compromised by TeamPCP. GitHub has confirmed the internal breach. A poisoned VS Code extension on an employee device exfiltrated ~3,800 internal repositories.
TeamPCP is already selling the data on a cybercrime forum.
A free game on Steam called Beyond The Dark contained hidden malicious software.
The game originally started as a simple title named Rodent Race. Someone hijacked the developer’s account and quickly changed the name, images, and other details. This tricked Steam, which does not verify updates.
The malware was hidden in a file called UnityPlayer.dll. The game often crashes when run, but the malware keeps operating in the background.
It searches for crypto wallet extensions in Chrome, such as MetaMask, connects to a malicious server, and downloads tools to steal passwords, browser data, and cryptocurrency. Some reports say it may also steal Roblox information.
YouTuber Eric Parker discovered the malware and made a video about it. Steam then removed the game completely.
If you downloaded or played it:
>Delete the game immediately.
>Run a full virus scan with updated antivirus software.
>Change all important passwords, especially for email, browsers, and crypto accounts.
>Check your crypto wallets for missing funds and transfer any remaining balance to a new secure wallet on another device.
This is a common tactic on Steam now
Is there a way to downgrade to the last version again? The current 26 and 26.0.1 have too many bugs like constant blinking refreshing of my windows or not showing correct disk/free size of my disks. According to 26.0.1 my disk has 0 free space and all 245Gb used while Finder correctly shows 80GB free. Also is there a way to get the fully highlighted folder texts in tag color back as I don't like those little dots?
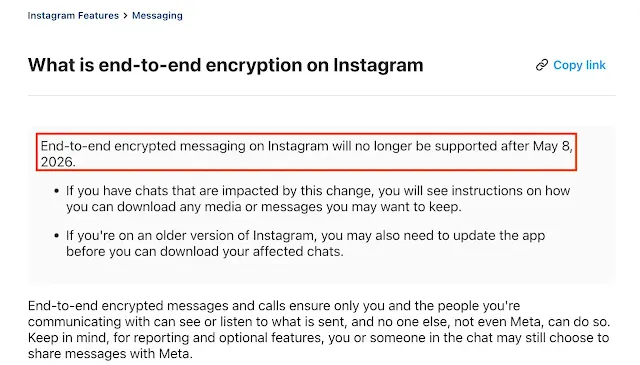
Reminder that Instagram is shutting down end-to-end encrypted messaging on May 8, 2026 - from this day on, Meta will have full access to your conversations:
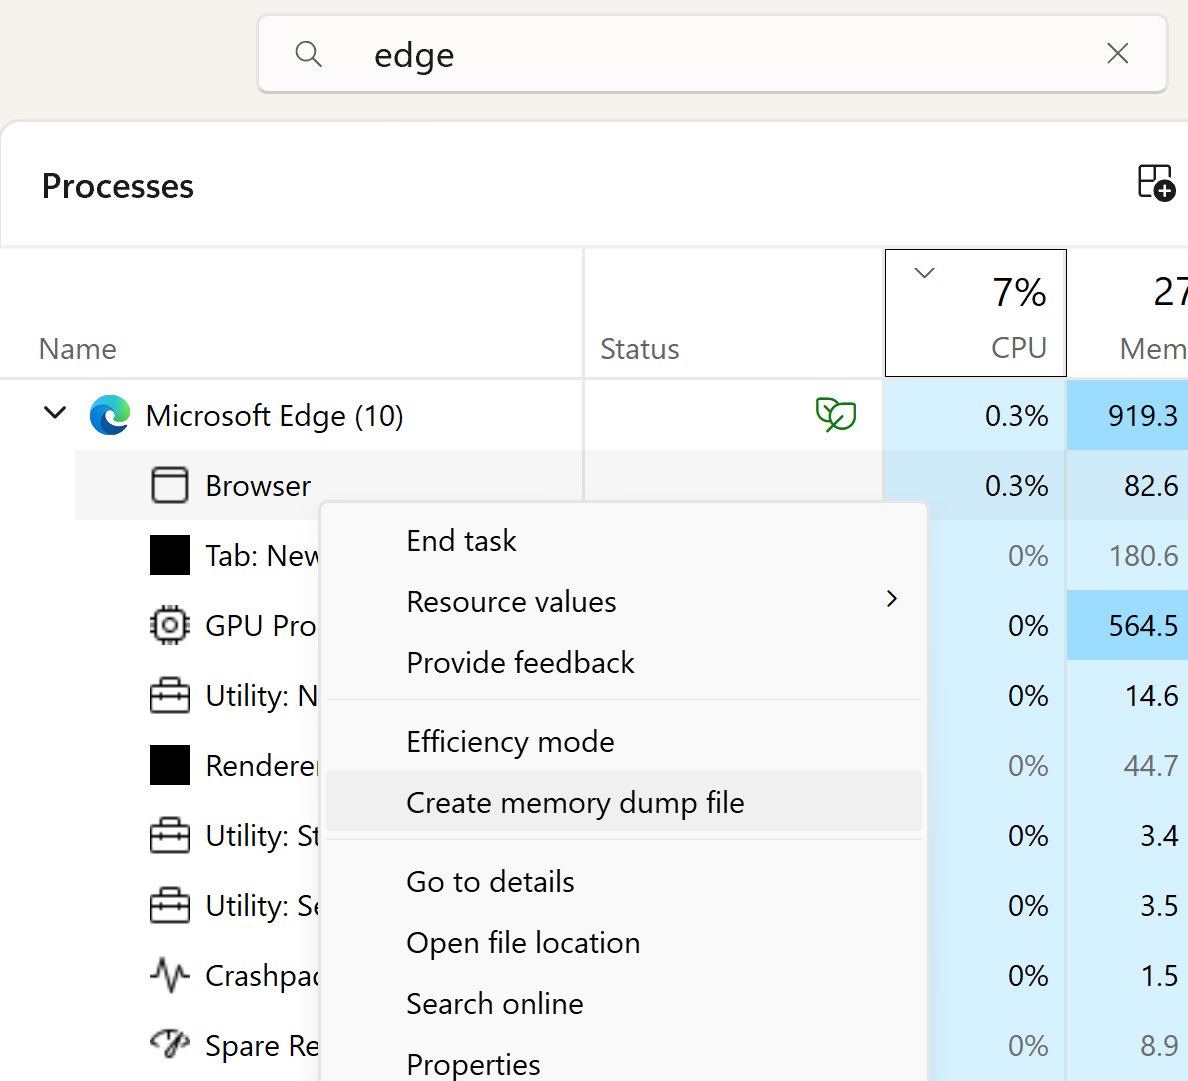
‼️🚨 Microsoft calls this "intended behaviour," so here we go.
How to dump the credentials of every user stored in Microsoft Edge:
1. Open Edge. Don't browse anywhere, just open it.
2. Flip to Task Manager, find Edge, expand the task.
3. Highlight the "browser" sub-task, right-click, and choose "Create Memory Dump."
4. Open the dump file and look for credentials.
The logged-in Windows user can dump every stored Edge credential with no additional rights. Which means any malware that user executes has those credentials for the asking.
Thanks to Rob VandenBrink at SANS: https://t.co/ebtVZxne4L
Microsoft Edge keeps every saved password as plain readable text in its memory as soon as you open the browser. This includes passwords for websites you have not even visited yet.
Google Chrome only unlocks passwords when you actually need them.
A security researcher created a tool that shows how admins can easily copy passwords from other users’ Edge browsers on shared computers or work setups.
Microsoft says this is “by design.” But the browser still asks you to log in again, even while it holds all the passwords unprotected in memory. This creates real risks on shared devices.
Digital ist besser
Das ist das Schöne an der EU: Die überzeugendsten Gegenargumente für all ihre dämlichen Projekte liefert sie immer kostenlos & zeitgleich mit.
Hier sehen Sie die (guten!) Gründe Nr. 1 - 2.378, warum es der EU niemals, aber wirklich NIEMALS!, gelingen darf, digitale IDs, Chatkontrolle, Altersverifikation, Gesichtserkennung, biometrische Datenspeicherung und digitales Geld einzuführen...
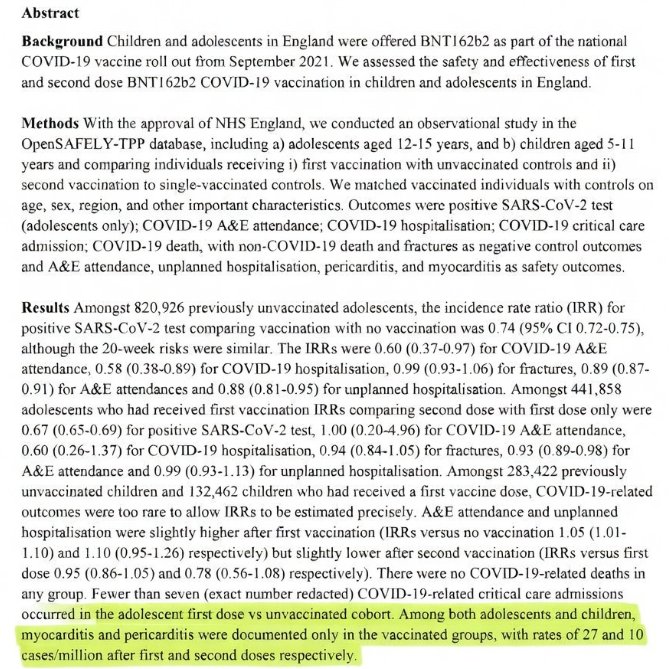
🚨Study involving 1.7 million children has found that Myocarditis & Pericarditis only appeared in children who had received COVID mRNA vaccines.
Not a single unvaccinated child in the group suffered from these heart-related problems.