MacSec Labs major release is live.
MRTO (macOS Red Team Operator) and MRE (macOS Reverse Engineer) are now open for exam booking.
MRTO is an 8-hour hands-on operator exam built around a realistic multi-Mac internal network, covering recon, native macOS privilege escalation, lateral movement, evidence capture, and operator decision-making under time pressure.
MRE is an 8-hour practical reverse engineering exam built around a custom macOS application. Students work through triage, Mach-O analysis, symbols, Objective-C and Swift behavior, LLDB, runtime validation, and hidden-key recovery.
We also shipped a major Red Team Tradecraft refresh with new and updated modules covering TCC boundaries, Gatekeeper and quarantine tradecraft, Apple-native Remote Events execution paths, SMB-based movement, and more macOS-specific operator workflows.
Book your exam now: https://t.co/imt8WeGdUv
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining
MacSec Labs macOS Reverse Engineering has received a complete refresh for macOS 27.
The course still builds the fundamentals: Mach-O, ARM64, Objective-C, Ghidra, and LLDB. It now goes further into AI-enabled Mac software, with hands-on work mapping Foundation Models call boundaries and inspecting a Core ML model’s interface, graph, and predictions.
Students work through course-built apps and lab packages, connecting static analysis to runtime behavior and documenting what the evidence actually shows. Whether you reverse apps for security research, malware analysis, or AI integration review, there is more to explore in this release.
https://t.co/1PklqeNNNX
#MacSecLabs #macOSSecurity #iOSSecurity #RedTeam #ReverseEngineering #CyberSecurity
⏳ Final 2 days to save $500 on MacSec Labs All Access!
Get lifetime access to all 5 tracks for $2,499 (regularly $2,999):
• Red Team Operations
• Reverse Engineering
• Vulnerability Research
• Detection Engineering
• iOS Pentesting
One payment. Lifetime access.
If you’ve been planning to build your macOS and iOS security skills, now is the time to join.
Take advantage of the offer before it ends!
https://t.co/6MapxU5I6t
#MacSecLabs #macOSSecurity #iOSSecurity #RedTeam #ReverseEngineering #CyberSecurity
MacSec Labs Detection Engineering course has been rebuilt for macOS 27.
The refresh covers macOS telemetry, Endpoint Security sensor engineering, detection as code, validation, threat hunting, and evidence packaging against current platform behavior.
Every module, rule, and lab is being reviewed for macOS 27 and Apple Silicon.
The offensive curriculum is moving forward. The defensive curriculum is moving with it.
Our promotional offer is available through October 10, 2026.
https://t.co/6MapxU5I6t
#macOS27 #DetectionEngineering
MacSec Labs MRTO has been rebuilt for macOS 27.
This is not a bolt-on phase. It is a complete 109-module refresh with 14 hands-on labs covering delivery, execution, dyld, XPC, Apple Silicon, privilege escalation, C2, and operator evidence.
MRTO is the first course on the market built specifically for macOS 27 red team tradecraft.
Every module has been revised against current platform behavior. The labs focus on practical operator workflows in authorized environments.
Note: All other MacSec Labs course tracks will also receive a complete macOS 27 refresh in the coming months and to mark the update, we are extending our promotional offer through October 10, 2026.
Buy now https://t.co/6MapxU5I6t
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining
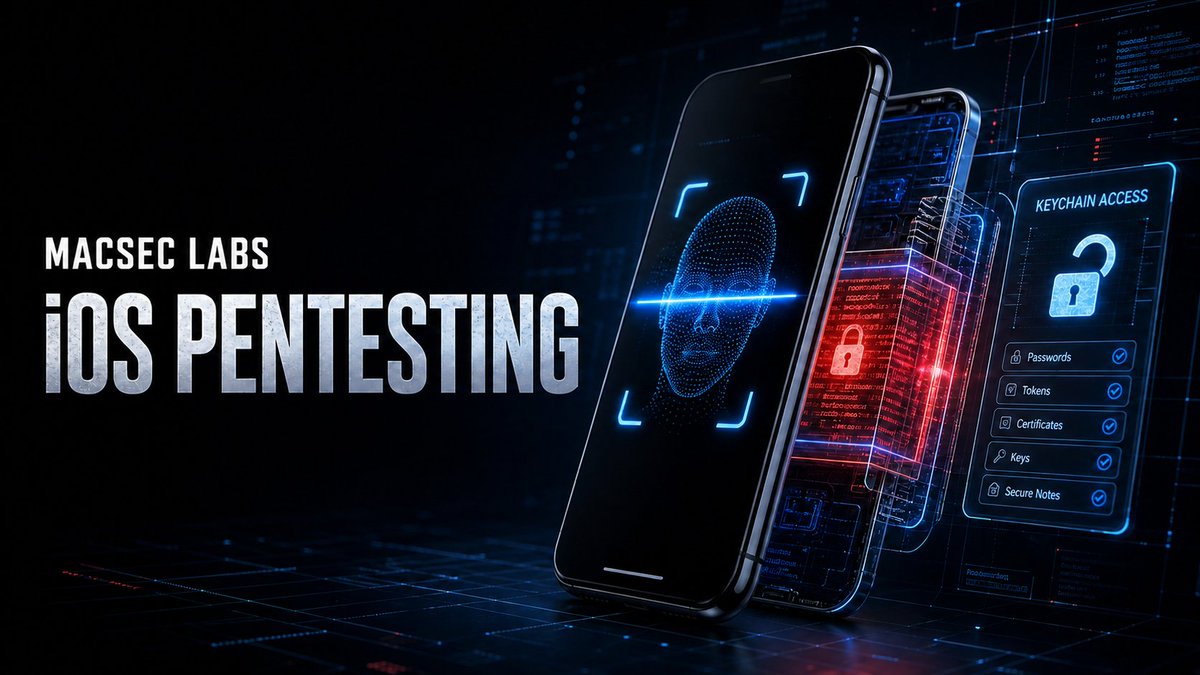
MacSec Labs iOS Pentesting course goes beyond basic mobile testing.
Face ID can protect an iOS screen without protecting the secrets behind it. When an app uses LAContext as a UX gate instead of binding data to a Keychain ACL, bypassing a single decision can expose the underlying design flaw.
Learn advanced iOS pentesting through live, reproducible examples at MacSec Labs.
https://t.co/G7mC1PmKzJ
#macOS #IOS #PenetrationTesting #RedTeam #infosec #OffensiveSecurity
The most-awaited iOS Penetration Testing course is now live on MacSec Labs.
Run a virtual iPhone with iOS 26 directly on your Apple Silicon Mac and every lab is reproducible.
Go hands-on with certificate-pinning bypasses, Keychain and data-at-rest analysis, Frida runtime manipulation, IPC and WebView vulnerabilities, authentication and cryptography, anti-tamper evasion, binary patching, dylib injection, and Frida Gadget.
You’ll assess MediVault, a purpose-built clinical-records app with 15 planted finding surfaces, from initial IPA analysis through a professional capstone report with CVSS scoring and OWASP MASVS, MASWE, and MASTG mapping.
https://t.co/G7mC1Pniph
#macOS #IOS #PenetrationTesting #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining
All Access. One purchase.
$2,499 through September 30, 2026.
Lifetime access to all 5 tracks and 8 current courses - macOS red team, advanced evasion, agentic operations, reverse engineering, kernel and iOS vulnerability research, detection engineering, and iOS application pentesting.
Future modules added to those tracks stay included.
https://t.co/6MapxU5I6t
#OffensiveSecurity #Redteaming #ios #mac #detectionengineering #penetrationtesting #securitytraining
The most-awaited iOS Penetration Testing course is now live on MacSec Labs.
Run a virtual iPhone with iOS 26 directly on your Apple Silicon Mac and every lab is reproducible.
Go hands-on with certificate-pinning bypasses, Keychain and data-at-rest analysis, Frida runtime manipulation, IPC and WebView vulnerabilities, authentication and cryptography, anti-tamper evasion, binary patching, dylib injection, and Frida Gadget.
You’ll assess MediVault, a purpose-built clinical-records app with 15 planted finding surfaces, from initial IPA analysis through a professional capstone report with CVSS scoring and OWASP MASVS, MASWE, and MASTG mapping.
https://t.co/G7mC1Pniph
#macOS #IOS #PenetrationTesting #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining
MRTE: Advanced Evasion course.
Visibility Islands - New phase is in the catalog.
Mac red team with SIP on. You load into an allowed process so EDR never sees a new unsigned exec, or you spawn under a parent the hunt is not written for.
Also in this drop: the Virtualization.framework entitlement gate, and why stripping quarantine still fails Gatekeeper on ad hoc code.
Live labs. Evidence you can put in a report. For operators who already know Windows and just got a fleet of managed Macs, this is for you..
https://t.co/w6RuS7MAYG
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining #DefCon
The macOS threat landscape is entering a new platform era.
MacSec Labs has begun preparing MacOS Red Team Operator (MRTO) for macOS 27 “Golden Gate” through a new preview research phase:
Behind the Golden Gate
We added a new phase to MRTO syllabus and this phase examines how macOS 27 changes the operator landscape, including:
• Kernel and system-daemon changes
• Siri and Apple Intelligence services
• Visual Intelligence
• App Intents and related XPC attack surfaces
• Apple Foundation Models and fm CLI workflows
• estrace visibility testing
• The practical tradecraft decisions connecting these surfaces
Once macOS 27 officially launches, the complete MRTO course will receive a platform-wide refresh based on the final release including updated attack-surface research, operator workflows, evidence collection practices, and enterprise-focused scenarios.
This is more than a version update. macOS 27 introduces a new operating environment, and MRTO is evolving with it.
https://t.co/aN5uvXWuLn
#macOS #RedTeam #CyberSecurity #ReverseEngineering #infosec #OffensiveSecurity #EthicalHacking #PenTesting #SecurityTraining
We just upgraded our Apple Kernel Vulnerability Research course for macOS 27 beta.
Built for researchers who want more than theory:
- Updated kernel tradecraft for macOS 27
- Detailed PoCs, lab evidence, and reporting workflow
- Bug classes, reachability, panic triage, variant hunting, and proof construction
- Apple Silicon-focused workflow throughout
This is the first MacSec Labs kernel track built around macOS 27 beta.
https://t.co/x6Eg2J6vqL
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining #bugbounty
Our DEF CON Metal evasion research is now fully live in MRTE.
We kept this private for 6 months, battle-tested it on real engagements, and validated it against top-tier macOS EDRs before shipping it into the course. This is operator tradecraft for Apple Silicon, not slideware.
If you want to go deeper into Apple Silicon tradecraft, GPU private memory, blit-driven staging, sandboxed accelerator abuse, and the real visibility boundaries defenders still struggle with, this is now part of the track
https://t.co/w6RuS7MAYG
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining #DefCon
MRTE exam booking is now live.
The macOS Red Team Expert exam is an advanced 8-hour macOS assessment focused on real enterprise attack paths: AD-bound Macs, lateral movement, multi-hop access, MDM abuse, privilege escalation, and evasion tradecraft.
Built to test how you think and operate in a real Mac environment, not how well you memorize tools.
https://t.co/bwuWAH0q6L
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining
Our DEF CON Metal evasion research is now fully live in MRTE.
We kept this private for 6 months, battle-tested it on real engagements, and validated it against top-tier macOS EDRs before shipping it into the course. This is operator tradecraft for Apple Silicon, not slideware.
If you want to go deeper into Apple Silicon tradecraft, GPU private memory, blit-driven staging, sandboxed accelerator abuse, and the real visibility boundaries defenders still struggle with, this is now part of the track
https://t.co/w6RuS7MAYG
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining #DefCon
We just upgraded our Apple Kernel Vulnerability Research course for macOS 27 beta.
Built for researchers who want more than theory:
- Updated kernel tradecraft for macOS 27
- Detailed PoCs, lab evidence, and reporting workflow
- Bug classes, reachability, panic triage, variant hunting, and proof construction
- Apple Silicon-focused workflow throughout
This is the first MacSec Labs kernel track built around macOS 27 beta.
https://t.co/x6Eg2J6vqL
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining #bugbounty
macOS Red Team Operator (MRTO) is officially here and the exam is open for booking.
This is not a 90 minute multiple choice test you can brain dump your way through. MRTO is an 8 hour, hands on, enterprise grade macOS Red Team assessment built to mirror what you actually face in the field.
The setup: multi hop infrastructure, an air gapped target, no SSH, no VNC, no easy footholds. You have to move through a real macOS enterprise environment the hard way, the same way advanced threat actors do.
What you are proving that you can operate tradecraft on Apple silicon and macOS endpoints under pressure, without the usual Linux or Windows crutches. Native macOS TTPs. Living off the land. Privilege escalation. Persistence. Lateral movement. Exfiltration. All against hardened, realistic defenses.
If you have been waiting for a macOS specific Red Team certification that actually tests operator skill instead of memorization, this is it.
Book the exam. Clear the assessment. Earn the MRTO.
https://t.co/tZv9A8kFhk
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining
macOS Red Team Operator (MRTO) is officially here and the exam is open for booking.
This is not a 90 minute multiple choice test you can brain dump your way through. MRTO is an 8 hour, hands on, enterprise grade macOS Red Team assessment built to mirror what you actually face in the field.
The setup: multi hop infrastructure, an air gapped target, no SSH, no VNC, no easy footholds. You have to move through a real macOS enterprise environment the hard way, the same way advanced threat actors do.
What you are proving that you can operate tradecraft on Apple silicon and macOS endpoints under pressure, without the usual Linux or Windows crutches. Native macOS TTPs. Living off the land. Privilege escalation. Persistence. Lateral movement. Exfiltration. All against hardened, realistic defenses.
If you have been waiting for a macOS specific Red Team certification that actually tests operator skill instead of memorization, this is it.
Book the exam. Clear the assessment. Earn the MRTO.
https://t.co/tZv9A8kFhk
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining
@fhlipZero Yes! One of our researchers is speaking at DEF CON this Saturday at 10:00 AM.
The talk is “Memory Laundering via Metal: What EDR Can’t See on Your Mac.” He’s also one of the author for the Red Team track.
If you’re attending DEF CON, feel free to stop by and meet him in person!
MacSec Labs major release is live.
MRTO (macOS Red Team Operator) and MRE (macOS Reverse Engineer) are now open for exam booking.
MRTO is an 8-hour hands-on operator exam built around a realistic multi-Mac internal network, covering recon, native macOS privilege escalation, lateral movement, evidence capture, and operator decision-making under time pressure.
MRE is an 8-hour practical reverse engineering exam built around a custom macOS application. Students work through triage, Mach-O analysis, symbols, Objective-C and Swift behavior, LLDB, runtime validation, and hidden-key recovery.
We also shipped a major Red Team Tradecraft refresh with new and updated modules covering TCC boundaries, Gatekeeper and quarantine tradecraft, Apple-native Remote Events execution paths, SMB-based movement, and more macOS-specific operator workflows.
Book your exam now: https://t.co/imt8WeGdUv
#macOS #RedTeam #ReverseEngineering #infosec #OffensiveSecurity #CyberSecurity #EthicalHacking #PenTesting #SecurityTraining