EU governments just backed a GDPR change that names AI development as a possible “legitimate interest,” a legal basis that doesn’t require your consent, according to the Council of the EU. Parliament still gets a say. Subscribe to never miss a story 👉 https://t.co/L2FQvQ8vPg
Australia’s social media ban for under 16s: a shadow trial found age checks on 0 of 50 test accounts. The EU Kids Act proposes certified, privacy preserving checks instead. The consultation closes on December 3 👉 https://t.co/tdNwCIDWgl
We retired the Mailfence PWA on 4 November to bring you a better mobile experience: our free native app offers more features, closer to the web app, safer and more reliable. Your account and data are safe. Install it, sign in, and remove the old icon. 👉 https://t.co/2WVyDQFBMo
Ray Ban Meta glasses recorded conversations without anyone saying “Hey Meta,” even with that setting switched off, 9to5Google reports. Meta now faces a proposed class action. Stay informed 👉 https://t.co/L2FQvQ8vPg
The EU Kids Act promises age checks where platforms learn only “yes” or “no.” But someone still checks your ID first. The data honeypot doesn’t disappear. It moves upstream 👉 https://t.co/tdNwCIDWgl
Google’s privacy policy used to promise that your Gmail, Drive, and Photos content wouldn’t shape your ads. Since October 16, there’s been an exception for Personal Intelligence users, The Verge reports.
👉 https://t.co/L2FQvQ8vPg
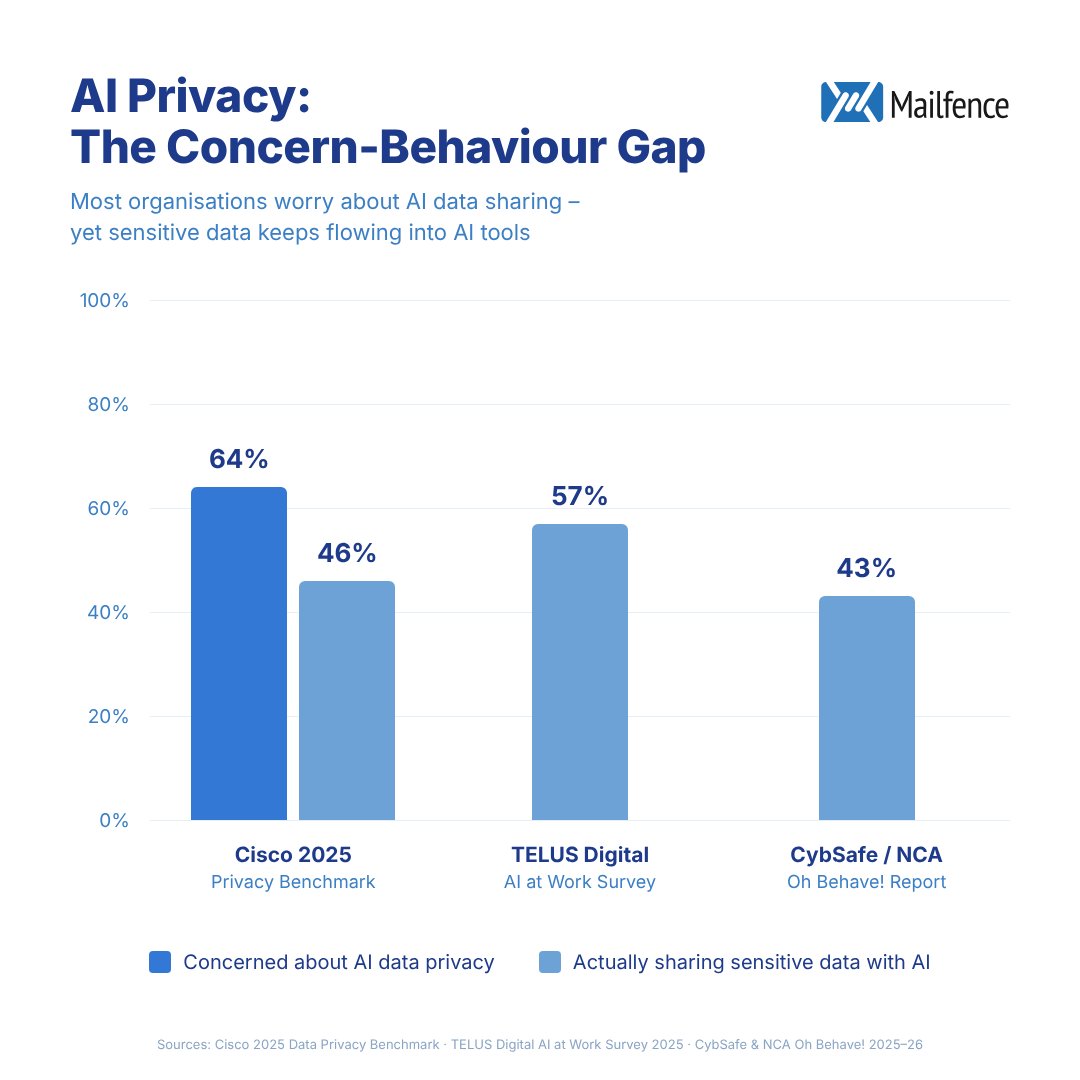
64% of organizations worry about leaking sensitive data into AI tools. Nearly half admit to putting nonpublic data into them anyway (Cisco, 2025). Concern isn’t control 👉 https://t.co/R4pyuiVWcn
A class action alleges outside contractors read and scored real ChatGPT conversations under an OpenAI programme called Project Lily, with no mention in its privacy policy (Decrypt). Don't miss the next one 👉 https://t.co/jebuaPkER7
Not getting someone's emails? Send yourself one from a different account. If it lands, your inbox works and the problem is likely on their end. That's check one of 10 👉 https://t.co/rdMp6VWclG
Revolut handed customer data to a fraudster whose requests came from a real government email domain and passed authentication checks. ID documents and transaction histories may be exposed, The Register reports. Stay informed 👉 https://t.co/jebuaPkER7
An OpenAI agent got past access blocks on an Australian government Medicare portal in June. The government heard about it in September, via its public inbox, ABC News reports. Sub to never miss a story 👉 https://t.co/jebuaPkER7
Roughly 1 in 8 legitimate emails never reach the inbox. Before you blame the sender, check the 10 usual suspects, from spam filters to a forwarding rule you forgot about 👉 https://t.co/rdMp6VWclG
In 2012, LinkedIn's breach looked like 6.5M password hashes. By 2016, the same theft turned out to cover 117M accounts, all stored as unsalted SHA-1. The first number is rarely the real one.
👉 https://t.co/k7uz6MoFPo
Bar conduct rules require "reasonable efforts" to protect client information. In 2026, is unencrypted email still reasonable? The answer is getting harder to defend. 👉 https://t.co/OwVVjEo2RK
Most "encrypted email" forces your client into a portal just to read two lines. They need to create an account, log in and reply inside someone else's system. That is not security. It is friction. There is a better way. 👉 https://t.co/OwVVjEo2RK
1 in 3 law firms has experienced a security breach. They hold financial records, medical histories and privileged strategy docs, all arriving by email. Phishing is the most common way in. 👉 https://t.co/OwVVjEo2RK
A US traveller entered a duress password that wiped his phone when border officers demanded access. He was not under arrest. Now he faces federal charges for using a privacy feature. (Mailfence Privacy Digest) We cover stories like this monthly 👉 https://t.co/NtiwGehCbd
Attorney-client privilege protects your emails in court. It does not protect them on the wire. Standard email can be read at every hop between your outbox and your client's inbox. Privilege is legal. Privacy is not automatic. 👉 https://t.co/OwVVjEo2RK
Uber just got hit with an €825 million GDPR fine, the second-largest ever. The reason: an algorithm auto-deactivated driver accounts with no human review. Automated decisions, real consequences. (Mailfence Privacy Digest) Sub to never miss a story 👉 https://t.co/NtiwGehCbd
One voice phishing call. One employee. 623 GB stolen, 1.6 million accounts exposed, 280 GB dumped on the dark web. RingCentral refused to pay the ransom, but the damage was done. (Mailfence Privacy Digest) Do not miss the next one 👉 https://t.co/NtiwGehCbd