Main Event Managed Services serves the insurance industry in the Tampa area. We are a specialty MSP that keeps your tech running and business compliant.
The real compliance risk for most agencies isn't the audit, it's the vendor nobody's ever asked about. A short list of who touches your data, with real answers on file, closes that gap. #InsuranceAgency
Your password isn't enough anymore. MFA blocks the vast majority of account takeovers, but not all MFA is equal. Text codes, authenticator apps, push, passkeys, and security keys compared in our new video.
https://t.co/S2eWr5o2PC
#MFA#Cybersecurity#TampaBay
Scammers watch LinkedIn for "started a new position" posts, then time a fake-urgent request for week one, when someone's most eager to please and least familiar with how things work. Tell new hires it's always fine to double check. #SecurityAwareness
A backup that's never been tested is really just a file you're hoping works. Pick one folder, restore it on purpose, see what happens. Ten minutes now beats a bad surprise later. #DataBackup
A call asking to change banking details might sound exactly like your client. Voice cloning makes that possible now. Always confirm with a callback to a number you already have on file. #CybersecurityAwarenessMonth
Quick exercise: search your email at Have I Been Pwned and see how many breaches it's in. Then change any reused passwords and turn on MFA. Five minutes, genuinely worth it. #DataBreach
That email "from your boss" is only as trustworthy as the address behind the display name. Check the real sender before you act on anything urgent or money related. #EmailSecurity
Could your Florida insurance agency hand over a written information security program tomorrow? Rule 69O-128.032 asks for one with administrative, technical, and physical safeguards. It should be real, current, and scaled to your size. #InsuranceAgency
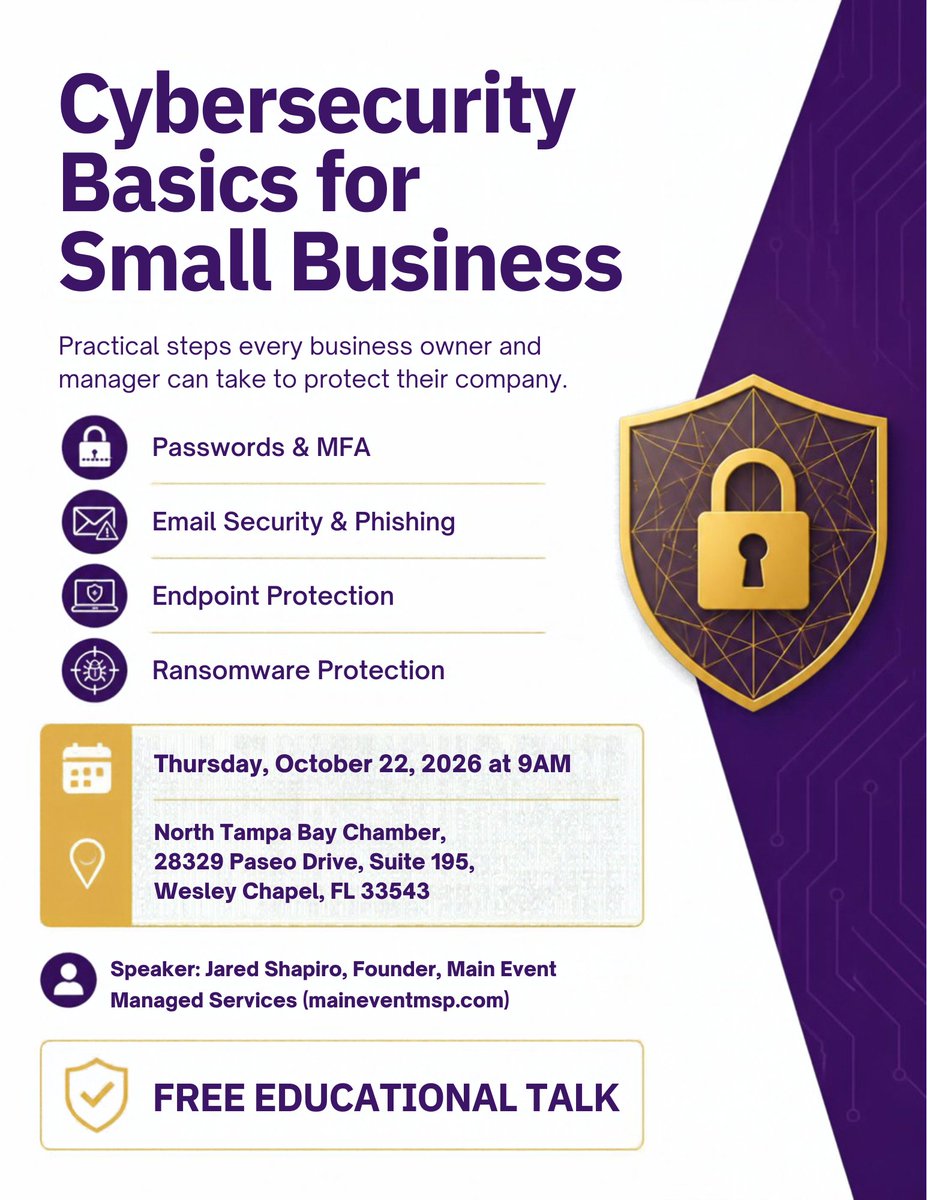
With next month being Cybersecurity Awareness Month we'll be giving a talk at the North Tampa Bay Chamber office covering cybersecurity basics for small business owners and managers.
Most small businesses do not have a security problem. They have a "nobody owns it" problem. Name one person for each area: access, backups, devices, vendors, training, response. Ten minutes of naming fixes a lot. #SmallBusinessIT
Is your team pasting client info into AI chatbots? Most people are just trying to work faster. A one-page policy helps: approved tools, a never-paste list, and a human read before anything goes to a client. #AIatWork
Ransomware is mostly automated, not personal. It looks for open doors like accounts without MFA or backups nobody has tested, not company names. Close the doors and test your restore. Small businesses in Wesley Chapel can do both. #SmallBusinessIT
"Your SunPass balance is overdue." Sound familiar? Skip the link, open the official SunPass site or app yourself, forward the text to 7726, then delete it. The same red flags show up in work email too. #ScamAwareness
Quick check for your Microsoft 365 mailbox: open your inbox rules and look for anything you did not create, especially forwarding to outside addresses. Then ask IT to block auto-forwarding and alert on new rules. Ten minutes, big payoff.
#CybersecurityAwarenessMonth
MFA fatigue is when an attacker repeats sign-in prompts until someone taps "Approve" to make them stop. The fix: turn on number matching, use passkeys where you can, and make "report, never approve" a team habit.
#CybersecurityAwarenessMonth
You review your E&O coverage every year. When's the last time someone reviewed your actual IT security posture?
Annual risk assessments catch gaps before they become incidents.
Phishing's sneaky cousin doesn't need you to click a link. It just needs you to answer the phone and trust the wrong voice. Train your team to verify, not just react.
A written incident response plan tells you what's supposed to happen.
A tabletop exercise tells you what will actually happen.
Here's what almost always breaks the first time an insurance agency tests theirs. 🧵
https://t.co/tStV95JoU7
Your employees' passwords might already be sitting on a dark web marketplace right now. Reused login from some other breach, forgotten account, doesn't matter how it got there. You won't know until someone monitors for it.
The ransom demand isn't the expensive part. The 2-3 weeks of downtime rebuilding your systems after is. If your agency doesn't have a tested recovery plan, you're not backed up, you're just hoping.