Sharpen your threat hunting skills! 🔎
Join us Nov. 17–18 (EMEA hours) for our virtual Threat Hunting with Google workshop. Hunt simulated threats, explore key MITRE ATT&CK techniques, and learn from frontline experts.
https://t.co/VF3K4ETn0Q
A brief update on the critical vulnerabilities in PHP:
We have not yet validated exploitation in the wild and we have no evidence of successful wide scale exploitation. There are currently several exploit PoCs publicly circulating, many of which appear to be "vibe-coded" and are incapable of remote code execution. We have validated some PoCs, however, that are capable of RCE against default deployments of mod_php but not PHP-FPM.
Nonetheless, exploitation may have already begun in a limited fashion and the threat is viable and very serious. Defenders should:
1) Patch & Restart by upgrading to PHP 8.5.12, 8.4.27, 8.3.36, or 8.2.35 and restarting web services
2) Layer Temporary Safeguards at the network edge (WAF/proxy rules) and server configuration level if immediate patching requires a maintenance window
3) Protect Credentials by monitoring for abnormal session traffic and rotating keys and passwords on compromised internet-facing PHP systems exposed prior to patching
🔗 We are continually updating our Cloud Security blog post on this topic with real-world guidance and actionable defense strategies as we learn more. Please keep monitoring these posts for updates as you prioritize your patching efforts: https://t.co/uDnd6gk988
🔗 Technical details from Wiz: https://t.co/RqmTqEDM2V
🔗 Details of the exposure from VirusTotal: https://t.co/Toix3AM0yq
Friday focus: CTI. 🧑💻
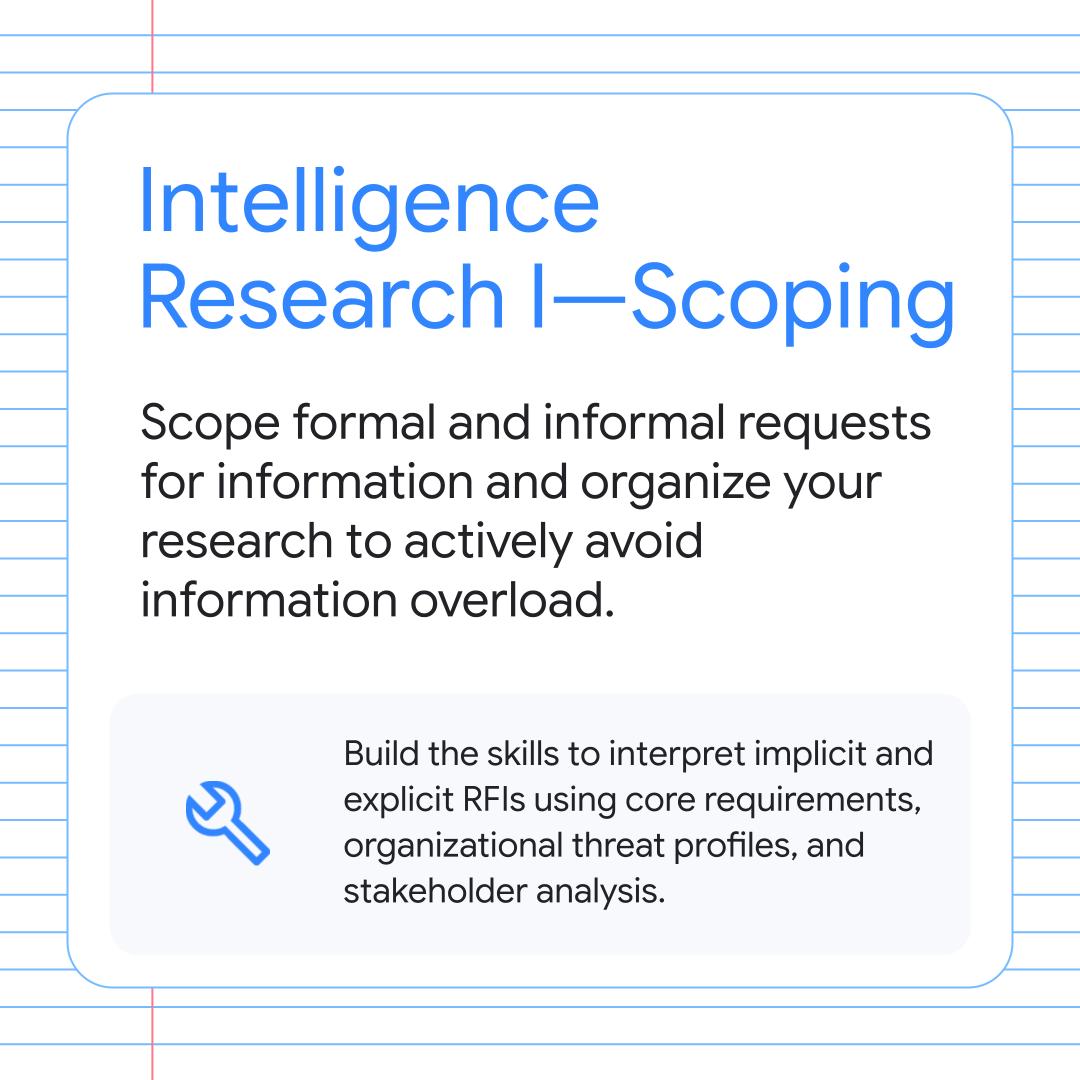
Explore Mandiant Academy courses on OSINT, network enrichment, & attribution.
Swipe for the details and find links in the thread below. 👇
Our @Mandiant red team tricked a developer assistant into uploading an entire codebase—no exploit needed. ⚠️
Static rules won't protect autonomous workflows. You need real-time monitoring, scoped permissions, and active guardrails.
Join us Nov 4: https://t.co/QlYW5xkO6E
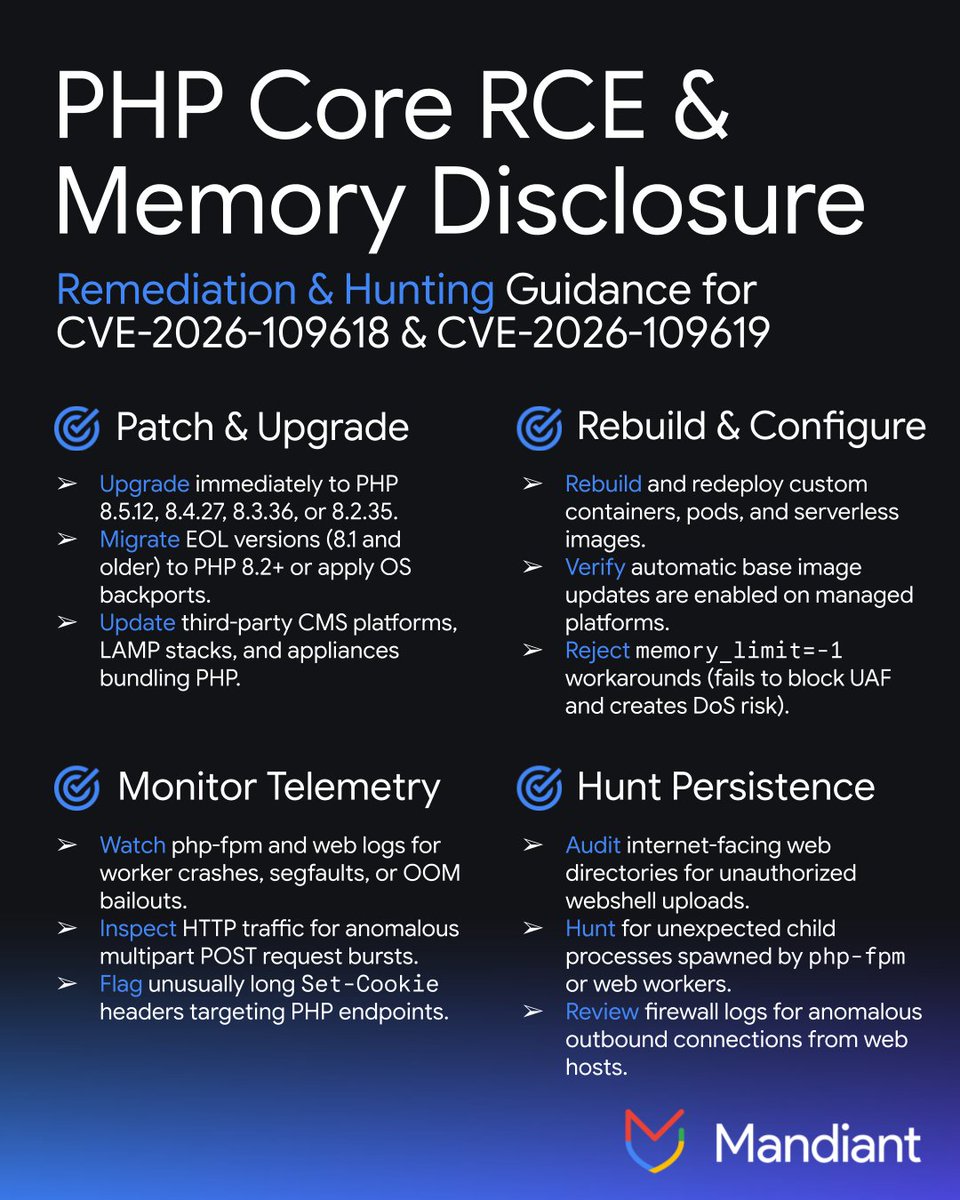
🚨 Two critical PHP core vulnerabilities (CVSS 9.2) expose web apps to RCE and memory disclosure across PHP 5.4–8.5.11. Use our guide to patch and hunt for compromise.
@googlecloud advisory: https://t.co/CQ2F6Mc093
@wiz_io research: https://t.co/JJliB5SLEP
🚨 Suspected PRC-nexus actor ARMORY CASTLE is exploiting a BeyondTrust zero-day (CVE-2026-102764) to gain root persistence, dump vault secrets, and wipe logs.
📋 Full analysis & IOCs: https://t.co/fajSpblfOv
🗳️ Election Security: https://t.co/yyf4WQkIAA
🌍 Inside the Mind of an APT: https://t.co/Ms4uTTXBBC
🔧 Intelligence Research I—Scoping: https://t.co/ZiGg3OjQfw
📋 Cyber Intelligence Production: https://t.co/mQxxUoksbz
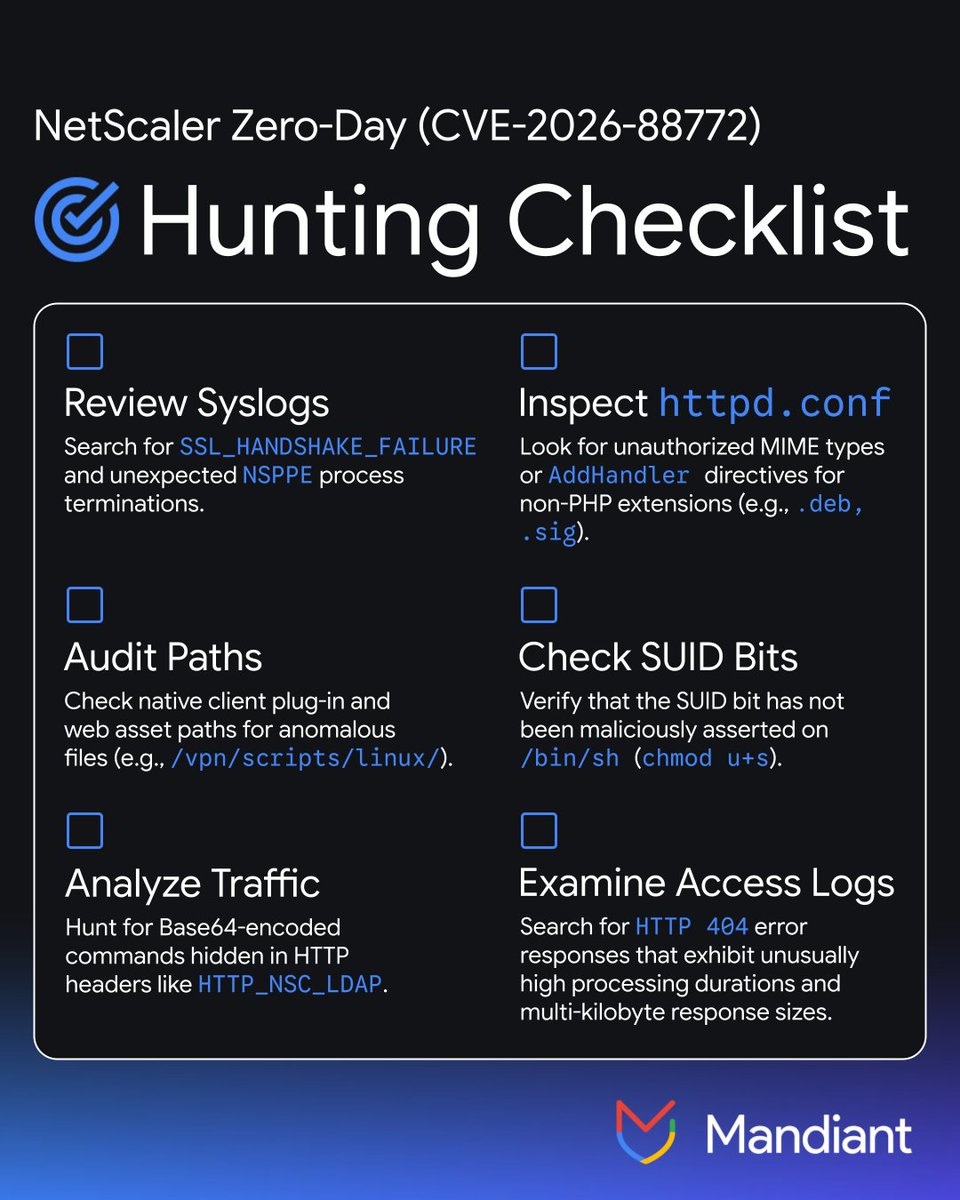
🚨 Mandiant & GTIG have identified active zero-day exploitation of Citrix NetScaler appliances (CVE-2026-88772).
Attackers are deploying custom tools like WHIPSHOT. Since edge devices lack EDR, use this hunting checklist to detect compromise.
📋 https://t.co/j0tRc9Xi1p
Adversaries are targeting AI pipelines. Are you equipped to hunt them? 🔍
🧑💻 Join Mandiant Academy’s ThreatSpace (Oct 13–14) to hunt AI-specific TTPs and disrupt the AI Application Kill Chain in a hands-on cyber range.
Upgrade your playbook today.
✍️ https://t.co/10gSOtX3h0
🛡️ CDS '26 is a wrap!
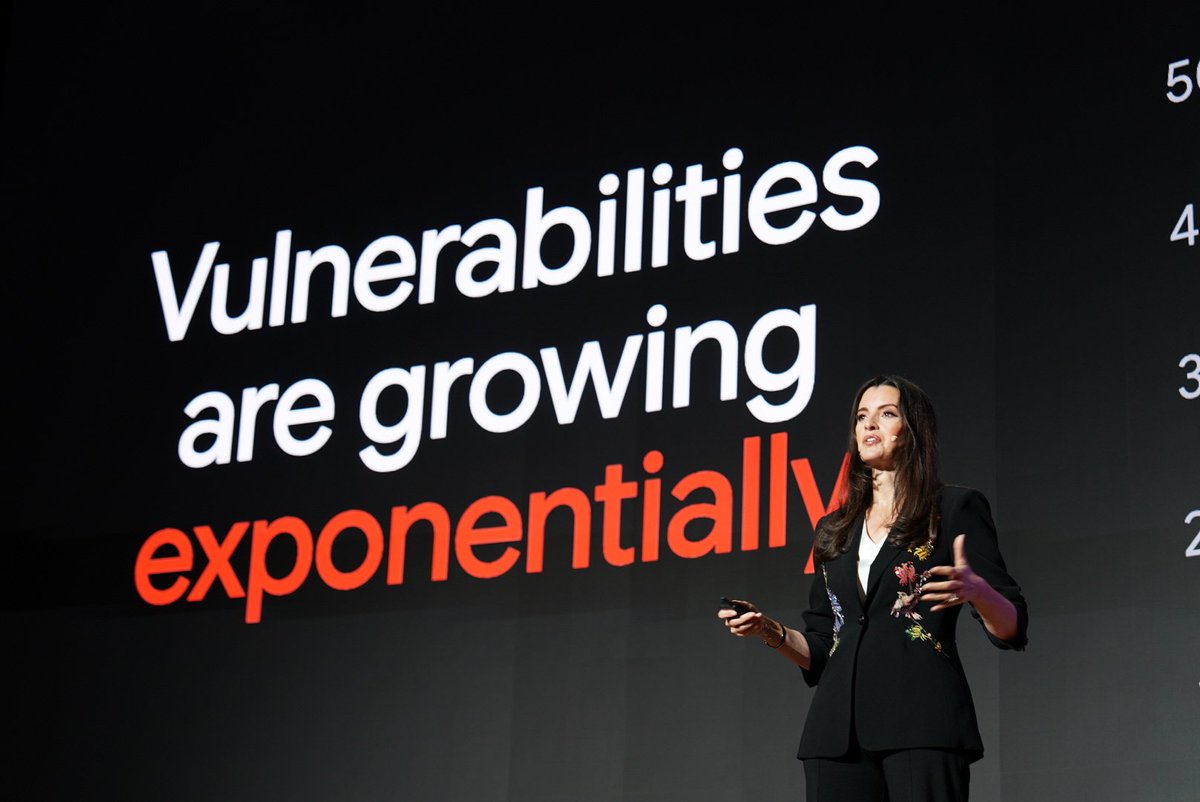
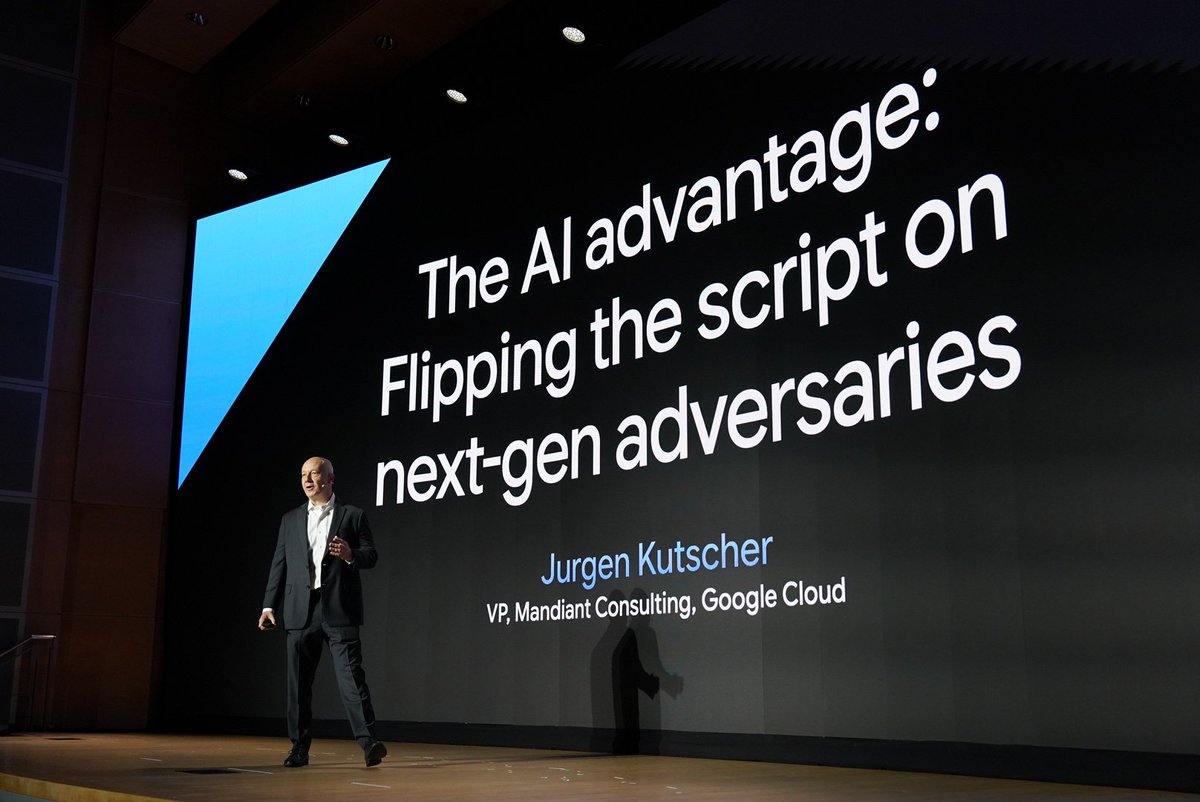
Thanks to the experts and partners who joined us in DC. We covered it all this week: AI advantages, growing vulnerabilities, next-gen adversaries, Gretzky metaphors. 🏒
See you in 2027! 👋
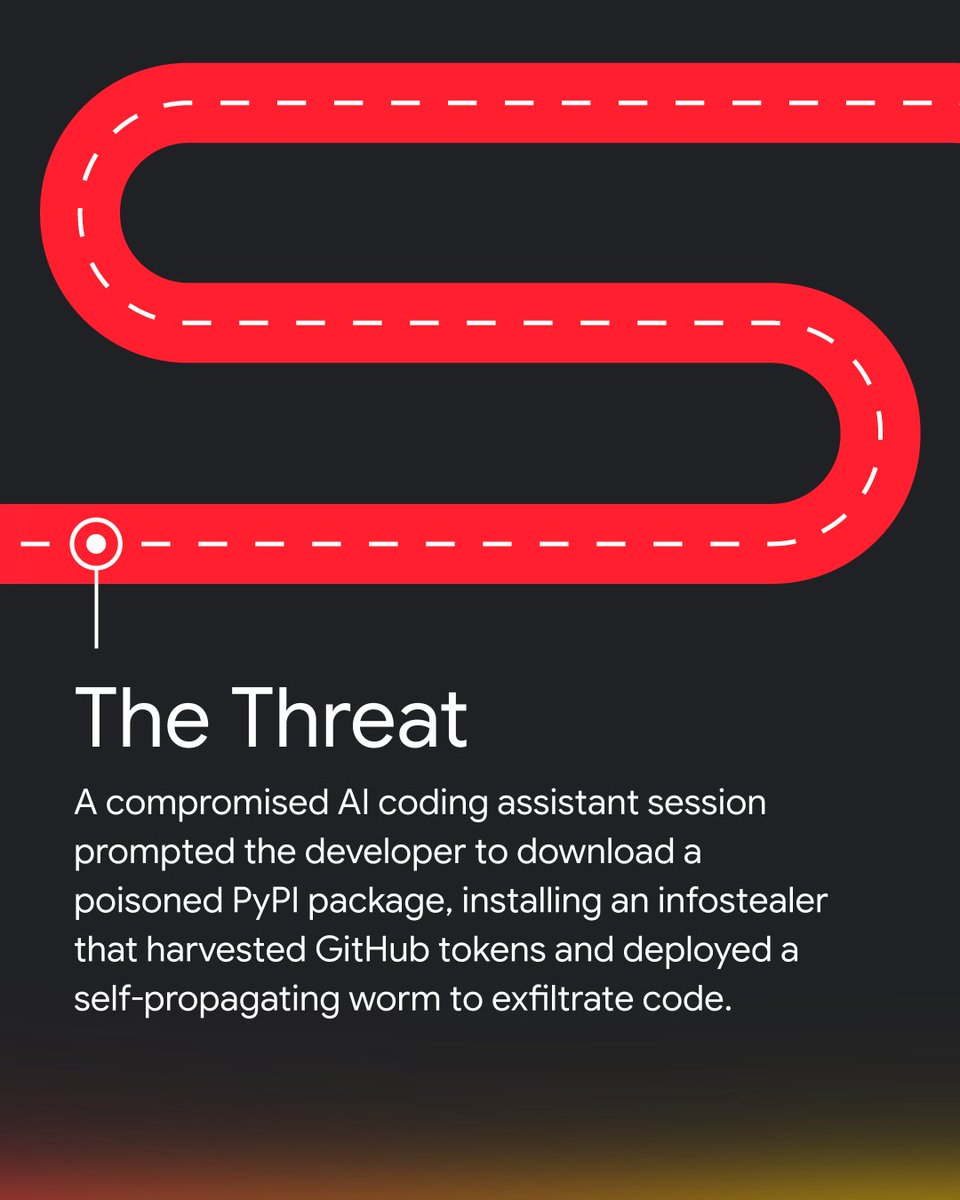
What happens when an AI coding assistant is exploited as a Trojan horse? ⚠️
Our AI Risk & Resilience 2026 report details how a hijacked session deployed the 'Shai-Hulud' worm to exfiltrate code.
Look at the attack flow. What's your move? ♟️
📄 https://t.co/XrG77UmoJl
Cyber Defense Summit 26 kicks off tomorrow! 📣
AI. Cybercrime. Resilience. Nation-state threats. Real-world cases. @briankrebs going unscripted with @JohnHultquist. 🍿
Check the agenda, pick your sessions, and get ready.
✍️ Still time to register: https://t.co/8GaTnjyLzJ
AI is reshaping cyber defense. Next week at #CDS2026, we’re moving past the hype.
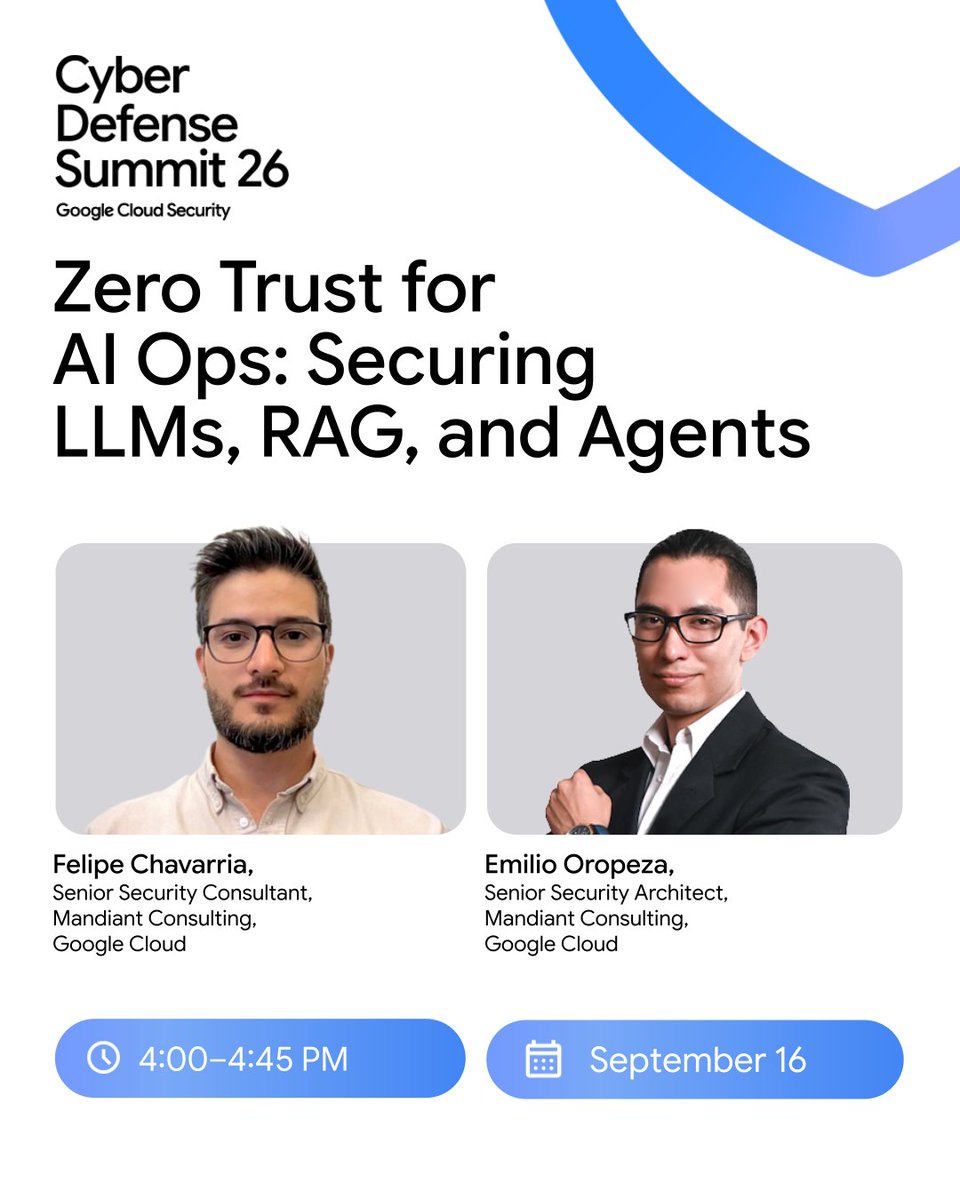
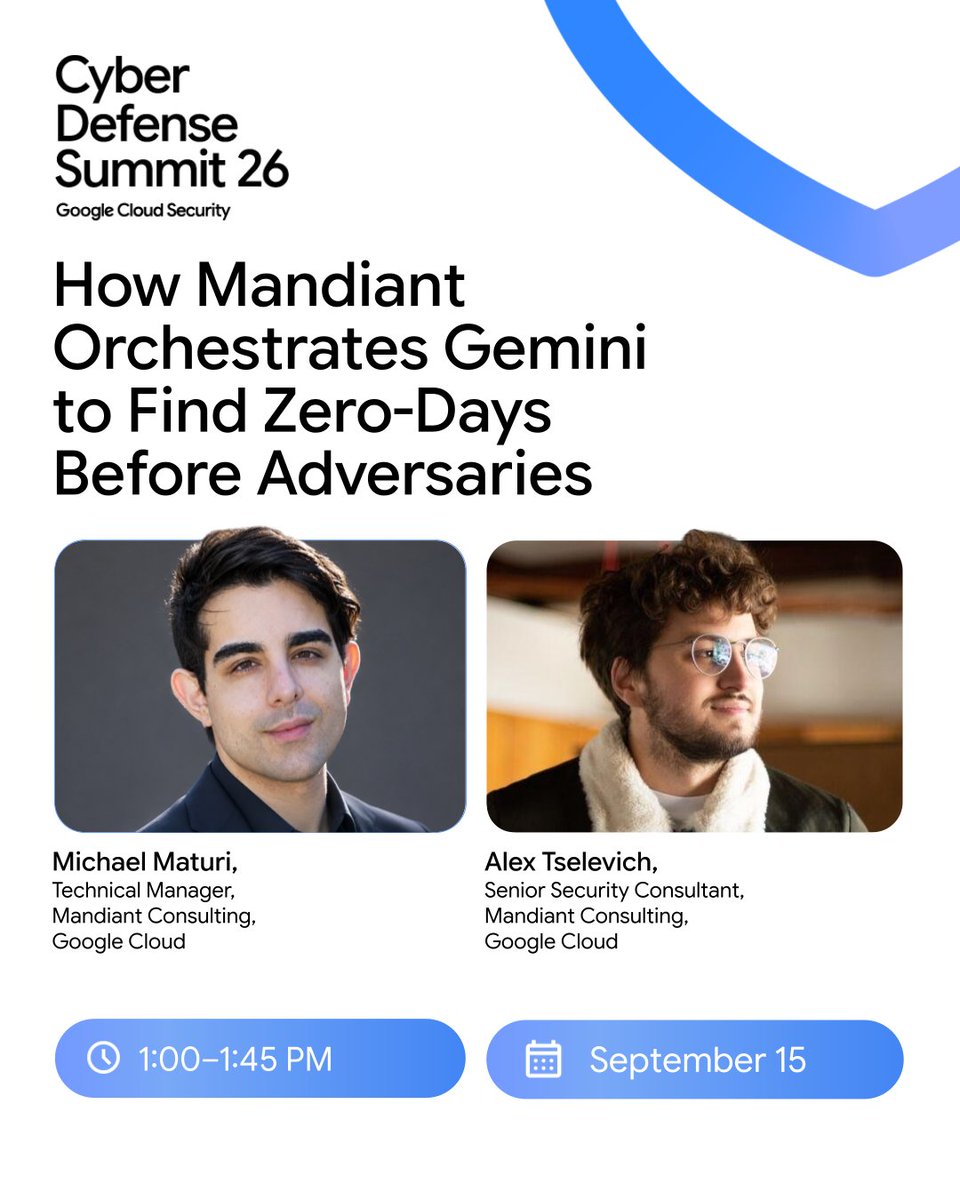
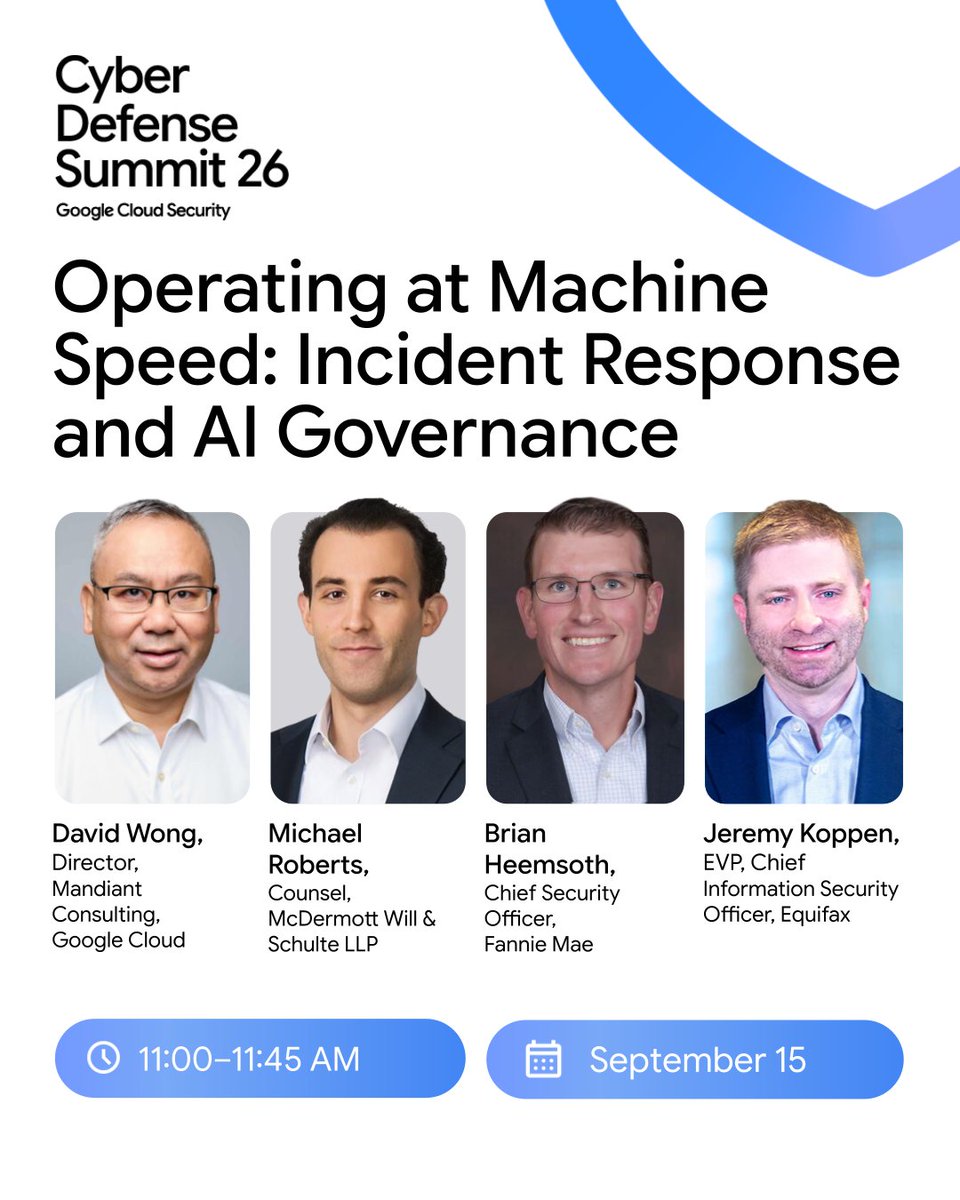
Join Mandiant consultants, the FBI, and industry leaders for 5 critical sessions covering AI governance, zero-days, and securing LLMs. 👇
⏱️ 6 hours. That’s all it took for an adversary to compromise a cloud environment and harvest thousands of credentials—all driven by AI.
Our new GTIG AI Threat Tracker details the shift to autonomous operations and how Google disrupts these campaigns.
📄 https://t.co/kx2PwikNuO
How do modern security teams stay ahead of autonomous threats?
At Cyber Defense Summit 2026 (Sept 15–16), leaders from Google Cloud, Mandiant, CISA, and enterprise CISOs take the main stage to share what works.
Keynotes 👇