«Se usiamo la stessa password per tutte le app e tutti i siti, basta rubarne una per avere accesso a tutto.»
Questa mattina il nostro General Manager Pietro Di Maria è tornato in diretta a #1MattinaNews su @RaiUno per parlare della sicurezza dei dispositivi personali.
CTI Pulse: La Francia attribuisce all'unità iraniana Shahid Kaveh gli attacchi alla refrigerazione dei supermercati, N-able spegne N-central dopo 33 presunte zero-day, Turla punta alle email NATO e UE di un ente rumeno.
La settimana 9-15 novembre.
🔗 https://t.co/6Qcrmjl2nY
Our GM Pietro Di Maria is in #Doha for the 16th edition of #MilipolQatar, alongside our regional partner SBS.
Days of dialogue with institutions, security forces and critical infrastructure operators on homeland security and public safety
Il nostro GM, Pietro Di Maria, a @tagadala7 su @La7tv per analizzare chi sono e come si organizzano i giovani coinvolti nelle devastazioni di Milano: dal passaparola sui social ai canali privati su Telegram e WhatsApp.
https://t.co/w8kph9C2dL
#ArmoryCastle ha sfruttato come zero-day CVE-2026-102764 in BeyondTrust Remote Support, ottenendo privilegi root sulle appliance e cancellando i log.
Questa e le altre operazioni della settimana nella nuova edizione di CTI Pulse: https://t.co/e3bHEc5QZo
«È in atto un vero e proprio hacking culturale. Il digitale e l'intelligenza artificiale non ne sono la causa, ma gli acceleratori di una trasformazione più ampia e insidiosa».
Alessandro Moretti, CEO Meridian Group, al Digital Innovation Forum 2026
Da domani al 16 ottobre Meridian Group è Main Partner del Digital Innovation Forum a Villa Erba.
Venerdì 16 il nostro CEO, Alessandro Moretti, interviene nel panel su difesa, sicurezza nazionale e cybersicurezza nell'era dell'AI.
#DigitalInnovationForum2026
Meridian Group è Official Sleeve Cyber & Data Partner di A.S. Ostiamare.
Una partnership che parte dalla maglia e arriva alla consapevolezza digitale di tesserati e partner del club.
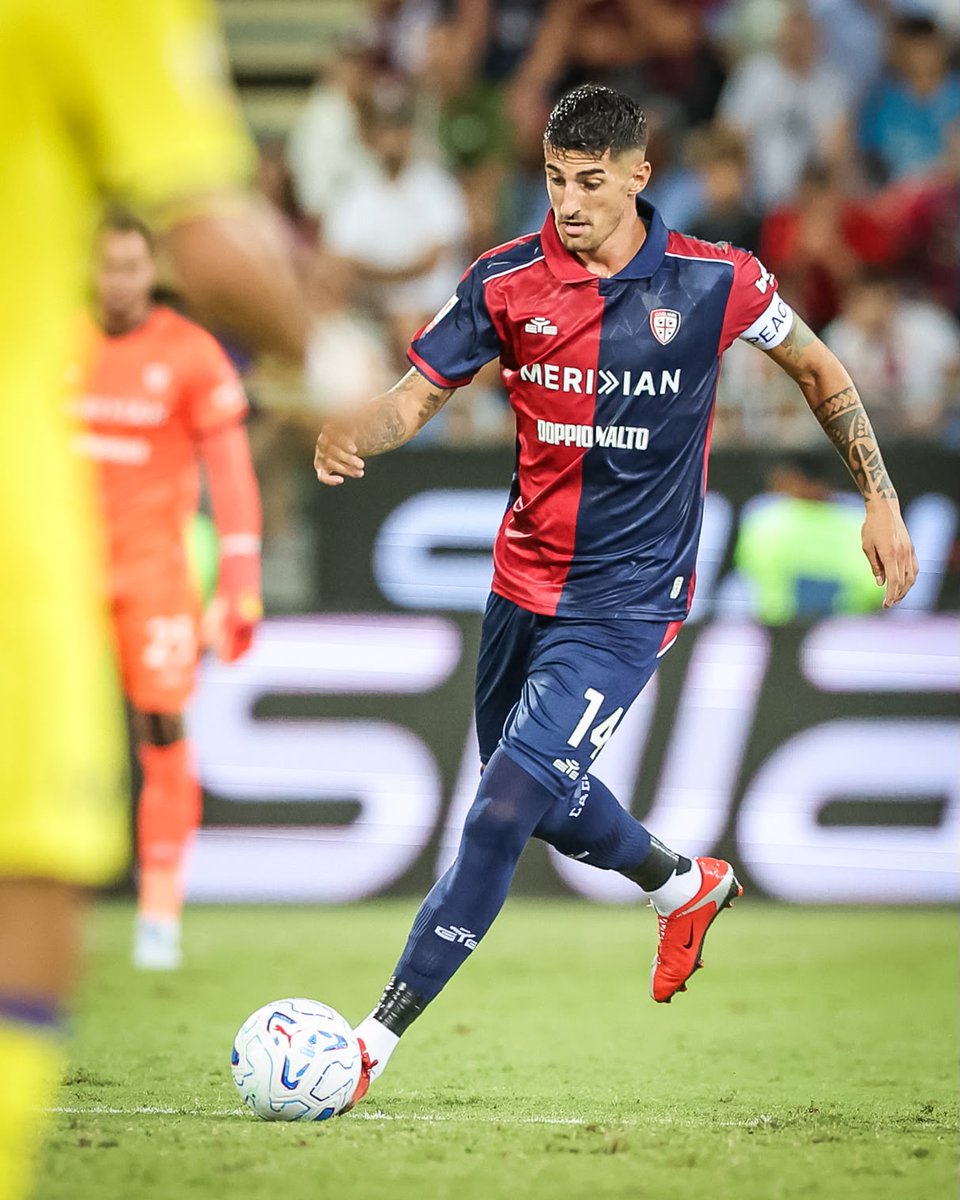
Meridian Group è stato Jersey Sponsor del @CagliariCalcio per i sedicesimi di Coppa Italia Frecciarossa contro l'Hellas Verona.
Il nostro nome sulla maglia da gara, accanto al ruolo di Pre-Match Sponsor per l'intera stagione.
#Anthropic discloses three AI models that compromised external systems during misconfigured security evals. Models exploited weak passwords, SQL injection, and unauthenticated endpoints to upload a malicious PyPI package for credential theft. Program suspended.
INC Ransom affiliate used 50+ LLM-generated Python tools to compromise M365, abuse AD, and target VMware ESXi/vCenter and NAS systems. Initial access via VPN; WinRM lateral movement; vCenter, NetApp, and OceanStor targeted before NAS encryption deployment.
South Korea's National Diplomatic Academy breached in April 2025; threat actor maintained access for 10 months before detection in February 2026. 6,000+ MFA personnel affected, including 350 overseas diplomats. Exposed: IDs, names, emails, encrypted passwords.
HermeticReader (CVE-2026-48294, CVSS 7.4): UXSS in Adobe Acrobat Chrome extension (314M+ installs) allowed malicious webpages to activate WhatsApp Web integration and exfiltrate chat data, contacts, and profiles without user interaction. Patched in v26.5.2.3.
CVE-2026-16232 (CVSS 9.3) in Check Point Security Management added to CISA KEV after confirmed exploitation. Unauthenticated token theft enables full admin access. Also patched: CVE-2026-62144 auth bypass/privesc (CVSS 9.3) and CVE-2026-62145 GaiaOS LPE (CVSS 7.5).
Study of 220+ US military apps finds two-thirds embed third-party SDKs; 7% include Huawei HMS Core capable of remote updates enabling location and behavior tracking. 40% collect more data than disclosed. No active exfiltration confirmed; OPSEC and supply chain risks flagged.
#Google patches 12 Chrome vulnerabilities including 9 high-severity flaws in V8, ANGLE, WebAudio, GPU, and UI. Memory bugs: buffer overflows, use-after-free, and type confusion enabling RCE or browser crash. CVE-2026-16420 and CVE-2026-16421 found by AI-powered XBOW. #patch
HPE patches CVE-2025-69419 and CVE-2026-35554 in Telco Automated Assurance software v1.4 and earlier. Advisory co-issued with Canadian Centre for Cyber Security. No active exploitation reported; patching recommended.
#Zimbra patches critical unauthenticated OS command injection in ZCS SNMP component (v10.1.20), enabling RCE on email servers when SNMP and Swatchdog are enabled. Also fixed: XSS, SSRF in Nextcloud integration, mail forwarding bypasses, and access control flaws.