@Okellami Я читала что их выкупили, а не специально создали, но whatever 🤔 про бету да, там концепты и что в итоге это 2 разных игры, но они так-то даже с этим таргетили мужиков, а внезапно получили китайских лесбиянок и такие "ну значит работаем на них"
@Okellami@omoshi_chan ну как дочерняя, ппг их купили как студию, но бюджеты не сильно увеличились ‐ в одном из интервью для 2 годовщины разрабы рассказывали как снимали задники для ивента с бюджетом в ветку и чуть ли не убегая от ментов в парке (запрещено снимать), так что связь там чисто по нужде
@ririnaeo_o I came here later to see the source to find out that I blocked the account
so I had to bring awareness about the artist because this shit is disgusting (NO THIS IS NOT ABOUT FICTIONAL CHARACTERS) https://t.co/6pjLPq195L
🌟 Reverse: 1999 Halloween Repost Giveaway! 🌟
To celebrate the spooky season, we're giving away some Halloween treats! 🎃
☔ We'll randomly select 3 Timekeepers to win Everecho's or Cornerstone's Halloween-themed Garment! ($14.99 Crystal Drops )
🍊 How to Enter:
1⃣ Follow @1999_timekeeper
2⃣ Like + Repost this post
We're so grateful for your support!
Winners Announced: Nov 5 on @1999_timekeeper
#Reverse1999
Earlier today, we detected evidence of a security incident on #AO3. We are still in the early stages of investigating. No AO3 data has been deleted. All your works, bookmarks, kudos, etc., are safe. Learn more at https://t.co/xzGXE5HyaB
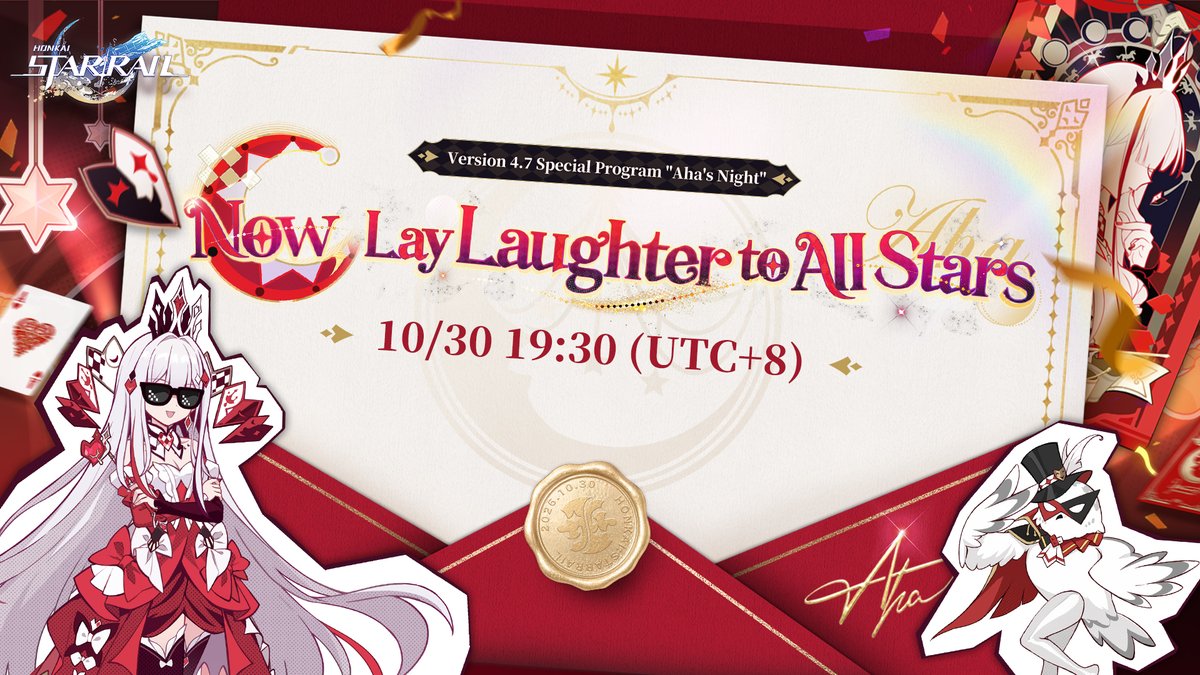
🎁#HSRSpecialProgram - Share for a chance to win Star Rail Passes
The Honkai: Star Rail Version 4.7 "Now, Lay Laughter to All Stars" Special Program will release on 2026/10/30 19:30 (UTC+8).
▼YouTube
https://t.co/z5DO29swzv
▼ How to Participate and Event Rewards
Quote this post with the hashtag #HSRSpecialProgram. We will select 50 participants, and each will be rewarded with 10 Star Rail Passes.
▼ Event End Date:
2026/10/30 23:59 (UTC+8)
Attention
https://t.co/UHYNmphSrR
#HonkaiStarRail
We estimate that service restoration for #AO3 will take around 2 weeks but it could be up to 4 weeks. We are hopeful that we will be able to bring the site back up in a degraded state sooner. Refer to our status page for updates: https://t.co/YAyyoTDOpE
BREAKING: Israeli spyware is confirmed on our phones. This should be headline news but none of our mainstream media is covering it, of course. So we will.
An Israeli ad company called Discover-Tech used ordinary online ads to plant spyware on people’s devices, and nobody had to click anything. The ad just had to load on a website or inside an app for you to be infected.
Citizen Lab and the ad security firm Confiant published the findings yesterday. Researchers went through roughly 4 billion ad-bidding records and found Discover-Tech ads running on more than 120,000 websites and 70,000 apps between March and June of this year. Confiant says the company was serving at least 10 million ads a day.
The platform was called Controlium. According to Citizen Lab, it let spyware companies use ad auctions to profile and unmask users, then send an infected ad to the one person they wanted to hack. The ads were also pulling cookies and login tokens from the sites they ran on. Israeli corporate records list Dekel Boni as the company’s founding director and sole shareholder.
The main spyware customer was Candiru, the Israeli firm the U.S. government blacklisted in 2021, which now goes by Integrity Labs. Five years after that blacklisting, it was still reaching devices through ad inventory on Google, Comcast-owned Beeswax and Russia’s Yandex. Google had Discover-Tech on its approved vendor list from 2020 until this week.
At least 45 Al Jazeera devices were targeted in 2024 and 2025. Candiru’s 2021 shareholder filings reportedly listed a minority investor described as a proxy for Qatar’s sovereign wealth fund, and Qatar also funds Al Jazeera. If that holds up, Qatari state money was sitting inside the company whose spyware was later aimed at Qatar’s own news network.
The heaviest targeting was in the Palestinian territories, where Discover-Tech served almost 2% of all digital ads and about 10% on April 7. Traffic also reached the Armenian prime minister’s office, courts, universities and defense organizations.
Google and the other ad platforms cut Discover-Tech off after the report came out. What nobody has answered yet is who paid for the ad buys, and how a company working with a U.S.-blacklisted spyware vendor passed vendor review for six years.
I am going to look into this today to see if we can figure out who was buying the ads. Interesting timing considering my article yesterday....
Here's what to do to protect yourself:
(1) Use an ad blocker. Citizen Lab calls ad-blocking a cybersecurity best practice and says there is no consistently safe way to be exposed to targeted ads. On iPhone, add a Safari content blocker. On Android, use Brave or Firefox with uBlock Origin. Ad blockers only work in your browser, not inside apps, so it also helps to delete free ad-supported apps you don’t need.
Kill your advertising ID.
(2) iPhone: Settings > Privacy & Security > Tracking, and turn off “Allow Apps to Request to Track.” Then Settings > Privacy & Security > Apple Advertising, and turn Personalized Ads off.
(2) Android 12 or later: Settings > Privacy > Ads > Delete Advertising ID. Then in Settings > Google > All Services > Privacy & security > Ads > Ads privacy, turn off Ad topics and Ad measurement.
(3) Windows 11: Settings > Privacy & Security > General, and turn off personalized ads using your advertising ID.
(4) Update your phone and restart it often. Many zero-click exploits don’t survive a reboot, so a daily restart forces attackers to reinfect you.
Stay tuned!
@creaturemiel@trashsmokish Path to Nowhere exists, their main target audience is literally CN lesbians. Like, yes, they still have male characters but they're for women, queer and not
@surtada1n not surprised that no one mentioned but it's Sigh of an Old Friend that plays only in one place in Inazuma strictly during the night (main shrine)