🚨Cyber Alert‼️
🇦🇪UAE - Scammers are taking advantage of the situation in the UAE.
The caller claims to be from the Ministry of Interior (MOI) and asks you to confirm that you received the national alert.
They request your Emirates ID (EID) number for verification.
Please do not provide any personal information or data.
The government would never call you to ask for such details.
Stay safe,
Hackmanac Team
#لا_حج_بلا_تصریح
أتيحت لي أكثر من فرصة #الحج بفيزا تجارية لكن آثرت الرسمي والحمدلله.
ما آخذه على بعض الإخوة #السعوديين هو التطاول على مصر والمصريين في العموم.
متطلبات الحج مكلفة في مصر مما يدفع النصابين للنصب على من ليس له علم بأمور الفيز وهذا مازاد العدد هذا العام
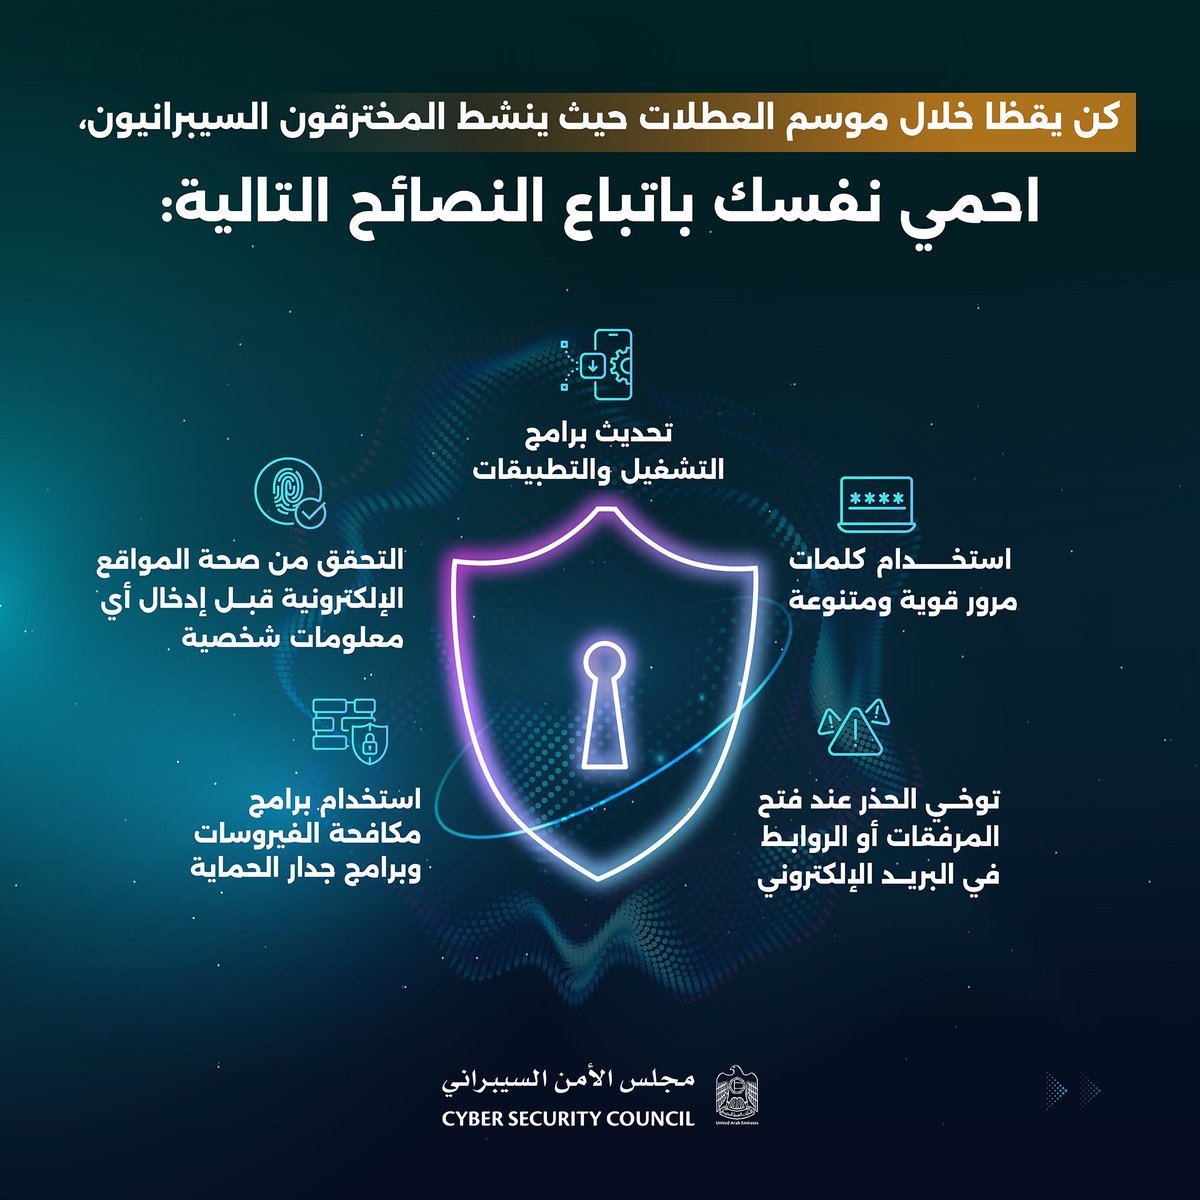
مع اقتراب العام الجديد وموسم الأعياد، يدعو مجلس الأمن السيبراني جميع الأفراد والمؤسسات إلى ضرورة أخذ الحيطة والحذر وتفعيل منظومة دفاعهم السيبراني واتباع التوجيهات الأمنية السيبرانية والحرص على تحديث برامجهم الأمنية بانتظام لتفادي الوقوع ضحية للهجمات السيبرانية المختلفة.. معًا، نستطيع خلق بيئة رقمية آمنة للجميع.
#مجلس_الأمن_السيبراني #حماية_البيانات #الإمارات #الفضاء_السيبراني #أبوظبي
As the new year and holiday season approach, the Cyber Security Council urges individuals and institutions to exercise caution. It emphasizes the importance of activating their cyber security defenses, following cyber security guidelines, and regularly updating security software to avoid falling victim to various cyber attacks. Together, we can create a safe digital environment for everyone.
#CyberSecurityCouncil #CSC #DataProtection #UAE #CyberSpace #AbuDhabi
UPDATE: 🇪🇬Fawry Removed from LockBit Wall of Shame
LockBit criminal group has removed Fawry from its data leak site, suggesting a possible agreement between the company and the cybercriminals.
On November 26th, Fawry released a statement announcing the conclusion of its cybersecurity investigation following a suspected breach by the LockBit ransomware group. The investigation, led by Group-IB, revealed that Fawry's main production environment, responsible for key applications, was not compromised. However, a breach occurred in an isolated testing environment, leading to file encryption and potential data exfiltration. This compromised data included personal customer details, though Fawry assures it won't impact financial transactions. The company has successfully removed LockBit code from its systems and is coordinating with Egyptian regulators to recover any stolen data. Fawry's CEO reaffirmed the security of customer financial records and the company's dedication to preventing similar incidents in the future.
#ransomware #databreach #CTI
Not a Borat Sketch! The IDF Spokesman points to a random calendar at the Rantisi hospital as "evidence" of a "hostage keepers' list" with "terrorists' names".
But the ONLY thing on that "list" is literally the days of the week (Saturday-Friday).
No tunnels, no weapon stash...🧵
🎓 Get ready for new #openSAP courses about #AI! Enroll now through the links below! @SAPCloudERP
Generative AI at SAP: https://t.co/6BhAJFC0Fs
SAP Signavio: https://t.co/dQyPA0Y3tR
SAP Customer Experience: https://t.co/aABcvl241e
AI Ethics at SAP: https://t.co/mCryGVZhQK