Become an absolute Web3 Security beast in 2026!!
Resources:
1. Owen Thurm - Web3 Security 101 playlist (Youtube)
2. Past audit reports - https://t.co/zICiqIDvki
3. DeFi bible - https://t.co/v1tIwvc1yQ
4. Books & Blog - https://t.co/ms43aQU3sv
5. Use AI to your advantage
Took the week off to enjoy a little staycation and not have any daily routines or calls. Just doing things that bring me joy. It’s been nice bouncing in between Warzone and bug bounties.
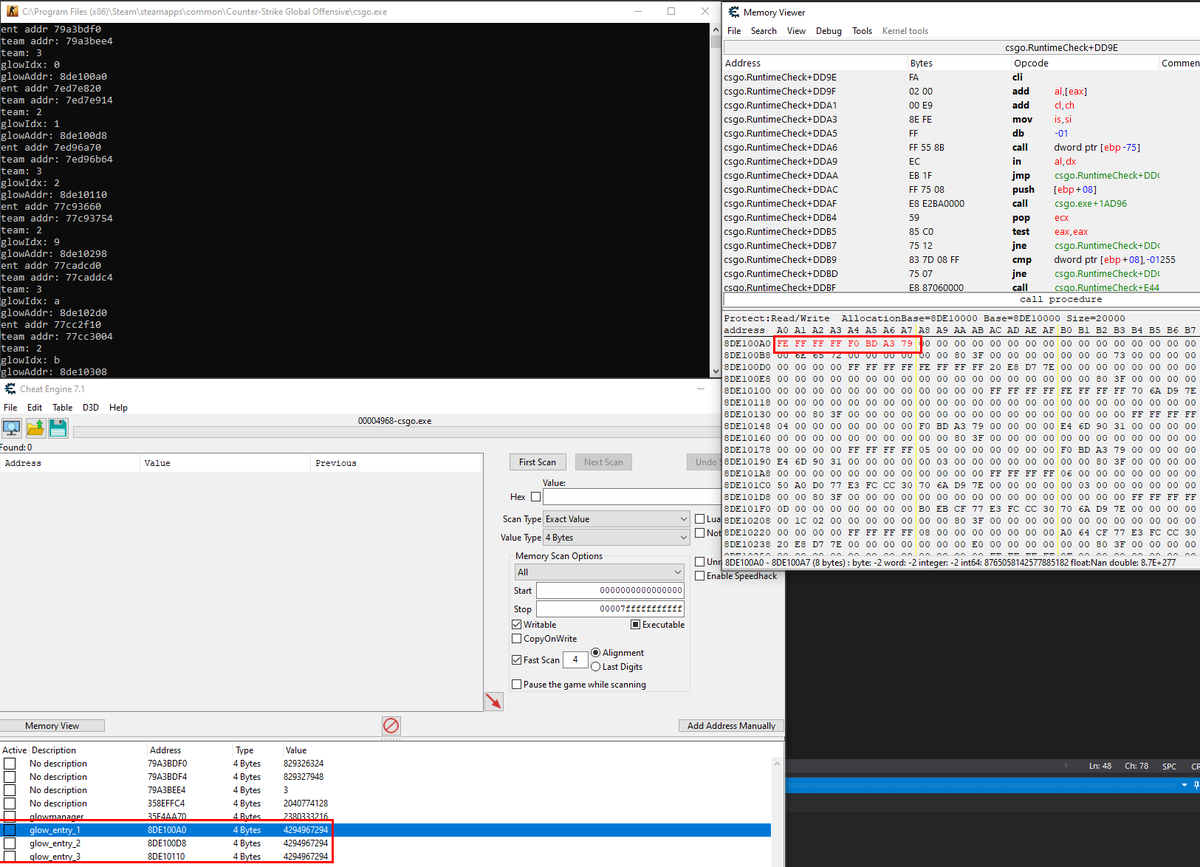
👾 Game Hacking: A Comprehensive Guide on Game Hacking
Part 0: https://t.co/xK4MAo1qwU
Part 1: https://t.co/upl5n5zQp5
Part 2: https://t.co/sri4iuQkTE
Part 3: https://t.co/UKsoGXIkaq
Part 4: https://t.co/jszNkTVgHH
Part 5: https://t.co/i6I8G2sASZ
#infosec#gamehacking
1. Web Application Hacker’s Handbook
2. The Hackers Playbook 2
3. Hacking: The Art of Exploitation
4. Ghost in the Wires
5. Social Engineering: The Art of Human Hacking
6. Computer Hacking Beginners Guide
7. Kali Linux Revealed : Mastering Pen Testing Distribution
8. The Basics of Hacking and Penetration Testing
9. Nmap Network Scanning
10. Practical Malware Analysis: The Hands-on Guide
11. RTFM: Red Team Field Manual
12. Hash Crack: Password Cracking
13. Mastering Metaspoilt
14. Advanced Penetration Testing
15. Hacking: A Beginners Guide to Your First Computer Hack
16. CISSP All in One Exam Guide
17. Web Hacking 101
18. Blue Team Handbook: Incident Response Edition
19. Black Hat Python: Python
20. Gray Hat Hacking: The Ethical Hacker’s Handbook
A thread🧵
💸Secrets of automation-kings in bug bounty💸
Finding 1day (or 1month) web exploits that haven't made their into scanners yet can make you big money.
Read more to understand where and how to get an edge in this area!
🚨Retweet, follow, & like for more! 🚨
1/x
🎉 Just wrapped up my 4th week as a Cloud Security Engineer Intern at @VTFoundation ! 🚀 Exciting journey exploring Microsoft Security Solutions, Azure's capabilities, and mastering Microsoft Sentinel. Ready for what's next! 💡 #CloudSecurity#internship#CyberSecurity 🌐🔐
🚀 Excited to share insights from my "Enhancing Security with Microsoft Defender" presentation at the Virtually Testing Foundation! 🛡️ Explored Azure tools too. Slides attached for a deep dive! #CloudSecurity#MicrosoftDefender#Azure#Cybersecurity#Internship
🤫 Unveiling a Hidden Technique: Bypassing 403 Access Denied Resources 🚀
Have you ever been frustrated by a 403 error on a specific web resource while others remain accessible? 🔒 Well, here's a secret you might find intriguing! Some websites use custom rules that rely on poorly crafted path-blocking to enforce restrictions, and we've discovered a clever way to bypass them.
🕵️♂️ Let's take an example: imagine you're trying to access https://target/api/admin/users/123, but it's blacklisted and shows a 403 access denied error. However, In most cases the underlying endpoint is actually vulnerable to an IDOR If you can actually get past these restrictions.
To bypass this protection - You can try appending a fake path like https://target/api/fakepath/..%2f/admin/fakepath/..%2f/users/123.
This technique tricks the server into thinking you're not trying to reach https://target/api/admin/users/123. When it successfully bypasses the poorly designed custom rule meant to prevent access, the outcome depends on how the backend interprets ..%2f. In some cases, it might end up being treated as https://target/api/admin/users/123, granting you unauthorized access to protected resources!
🛡️ Deceive the Web Application Firewall (WAF) or Servers, gain access to restricted resources, and potentially earn handsome bounties! 💰
🚀Lesson: Always remember to explore different techniques for breaking through these restrictions. There are numerous secrets waiting to be uncovered! 🔐 #CyberSecurity #Bypass403 #Hacking #HackerOne #BugCrowd #bugBountyTips #SecurityTips