Imagine being CZ for a sec
You are an old convicted felon
Your wife is not getting any younger
You're the most hated person in the industry
Your exchange keeps losing market share to this new competitor that came out of nowhere
Hyperliquid?
The founder is younger, smarter, more handsome
You're confident your wife has thought about him more than once, in what manner? who can say
And to make it even worse, he used to work for you
This "Hyperliquid" competitor keeps gaining marketshare and attention
Very good attention
24/7 trading? leader of onchain perps? CFTC license to trade in the United States?
What the fuck
Trump goes on national TV and starts saying "Hyperliquid"
ICE partners up with TradeXYZ?
Stanley Druckenmiller creates an X account just to shill Hyperliquid?
Elon Musk joins in???
HYPE starts climbing up to $100
什么鬼!!!
It's time to do what you do best
Liquidate the market again and blame it on a "hack"
The root cause? Simple, no one will question it
Just say our DevOps engineer left their laptop open in a Luckin Coffee shop
Explosive diarrhea from uncooked shrimp wontons
Everyone can relate
We could risk $6B in a "hack" to make it look real
Coordinate with Tether and Circle to freeze most of it
User recovery funds handles the rest!
Entire market starts nuking and HYPE falls from $97 to $90
CZ and Binance will do everything possible to stop Hyperliquid from growing and shift attention back to them
Remember 10/10 happened because Hyperliquid hit open interest all time highs and Aster completely failed
@vgarc1ar Haiti doesn’t have a government structure they can’t do shit by themselves. Please educate yourself on geopolitics before posting retard ass shit
Pou chèf gang yo ak manm gang yo k ap kenbe kat konpatriyòt nou yo an otaj ann Ayiti:
Mesye nou kidnape yo pa konbatan. Yo se teknisyen nan domèn avyasyon ki fè pati misyon nou ann Ayiti, nan kad yon misyon entènasyonal. Misyon nou an gen sèlman pilòt ak pèsonèl teknik, ki gen kòm travay prensipal fè evakyasyon medikal epi sove lavi moun, pa fè lagè.
Men, nou te kidnape yo yon fason lach pandan yo t ap retounen apre yo te fin achte manje nan yon makèt nan zòn nan.
Se poutèt sa, jodi a nou te lanse yon operasyon militè pou pote yo sekou. Nou gen yon sèl objektif: fè kat konpatriyòt nou yo retounen lakay yo vivan, san okenn mal.
Men, mwen vle pou nou menm, chèf gang yo, konprann yon bagay byen klè: atak jodi a pa anyen devan sa k ap vini si nou pa remèt toule kat otaj yo vivan.
Epi pa pran pawòl nou yo pou menas san fondman. Nou deja fini ak gang yo nan El Salvador, e nou kapab fini ak nou tou.
Nou toujou gen tan pou evite sa.
Remèt nou kat konpatriyòt nou yo vivan, san okenn mal, epi tout bagay ap retounen jan sa te ye anvan kidnaping lan.
Desizyon an nan men nou.
🚨Avoid critical web 2 interactions right now.
As I called the reverse engineering vector is actively being used to attack traditional web apps.
Crypto requires a private key. These antiquated systems are open text centralized and easy to break.
This is only the start we have been raising the alarm for weeks.
Read this asap all web 2 devs.
Critical PHP vulnerabilities (nicknamed PHP2Shell) are driving widespread website takedowns and scrambling today (October 21, 2026). This is the dominant story affecting traditional “Web 2” platforms and sites.
Two severe remote code execution flaws in PHP (CVEs 2026-109618 and 2026-109619) were disclosed. PHP underpins a large share of the web estimates put it around 70% of sites, including many WordPress, Drupal, Joomla, MediaWiki, and similar stacks. The bugs can let attackers run code on vulnerable servers without logging in. They were discovered using AI tools and had existed for years. Patches were released today; national cyber agencies (including the US NSA, UK NCSC, and others) advised organizations to update immediately or take systems offline if they could not.
Cloudflare and others reported seeing early exploitation attempts. Many sites are offline preemptively rather than after confirmed breaches, while operators race to patch. This is not primarily a classic DDoS campaign, though related cyber activity and other issues are also in play.
Platforms and sites reported affected or taken offline
• Government and public services: Finnish government public web services; multiple Dutch sites (NCSC, Port of Rotterdam, https://t.co/uRpSL8q4r4, DigiD, parliament/Tweede Kamer, KNVB football association, political parties, hospitals); French sites including Paris police and local government; German, Belgian, Danish, and Czech government sites; UK councils (Edinburgh, Oxford, Bristol, Lambeth, Barnet, etc.) and Metropolitan Police.
• Other notable: 4chan, Something Awful forum, Wikimedia/Wikipedia supporting services, parts of BBC sites, Asana, GOG, and various others.
Other concurrent issues
The same day brought additional cybersecurity problems: high-severity Node.js vulnerabilities (including remote code execution), a compromise of the LiteLLM proxy, and a certificate authority (eMudhra) private-key issue. Earlier in October, Ubuntu/Canonical sites faced a sustained DDoS.
In short, large numbers of traditional web platforms and government sites are offline or disrupted right now primarily because of these PHP flaws and the advice to patch or go dark. The situation is evolving as patches are applied; widespread confirmed data breaches from this specific issue have not been the main reported outcome so far. Major social platforms (X, Facebook, etc.) are not the focus of the current outages.
Exactly one year ago, we saw one of the worst crash in the history of crypto.
Bitcoin crashed $20,000 in 8 hours.
$16.4 billion in longs were liquidated.
Altcoins nuked by 40–70%.
Some coins literally went to zero.
So Many lives were destroyed that day, but no one was ever held accountable.
This is another reason why we need Clarity Act and other clear regulations in crypto.
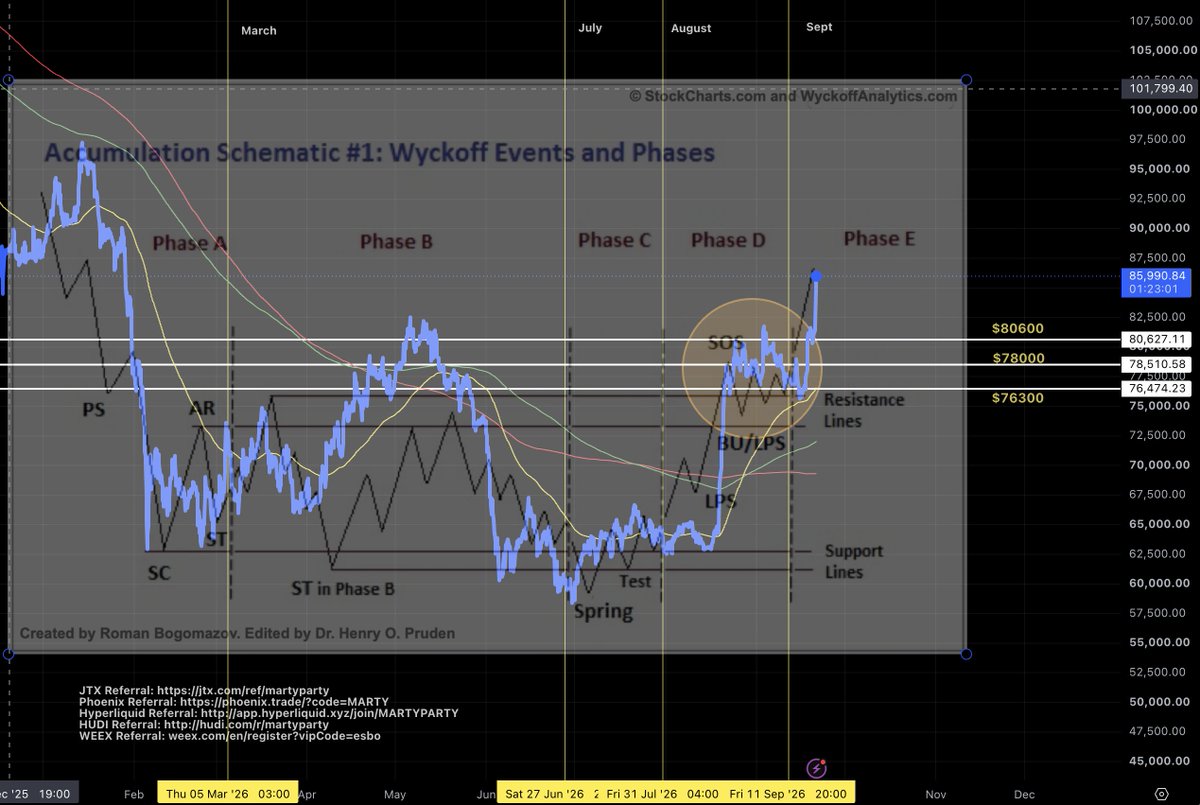
$BTC #Wyckoff Accumulation Schematic #1 is complete - the "composite man" has trapped retail out of the market.
Congrats to my subscribers who entered with me at the $58k Spring.