OMB M-26-14 replaces M-21-31 with a risk-based approach to federal logging. Network flow remains essential for visibility, threat hunting, and investigations. Is it in your Agency Logging Plan?
https://t.co/pnGzgPuTfk
#NetFlow#CyberSecurity#FederalIT
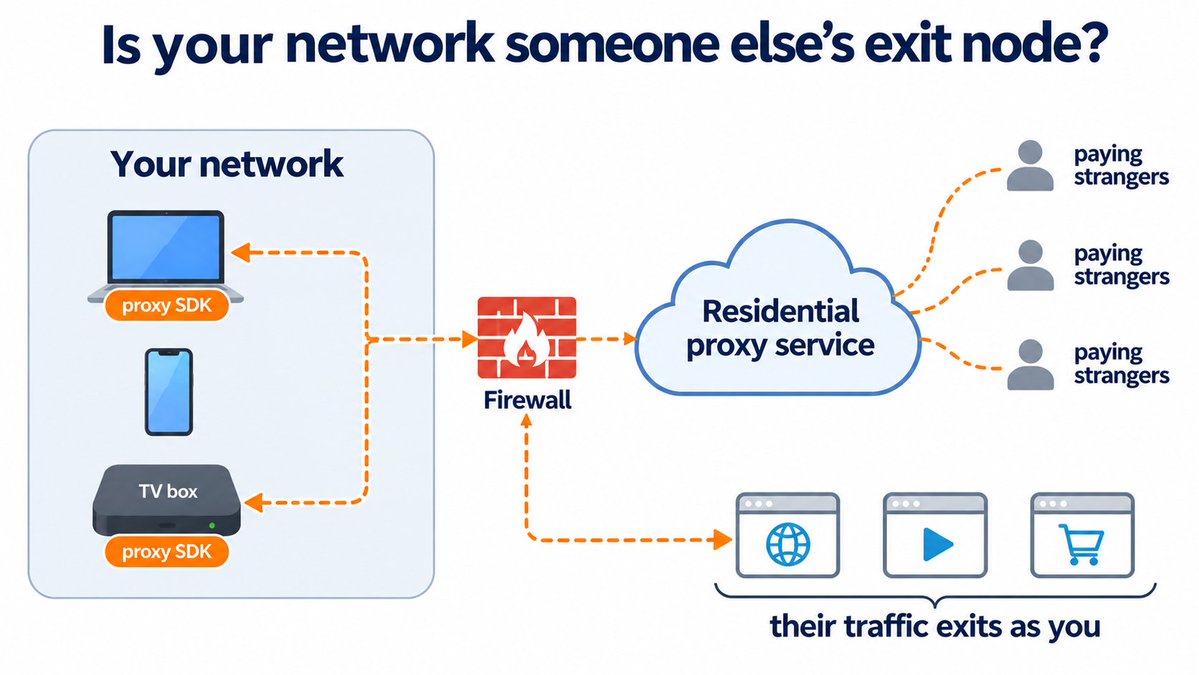
Could your devices be residential proxy exit nodes? Learn how NetFlow helps uncover suspicious connections and hidden proxy activity.
https://t.co/p0kAMeQX1y
#NetFlow#CyberSecurity
When a vulnerability is exploited, the clock is already ticking. Network evidence must exist before the attack to help security teams investigate, understand exposure, and respond.
https://t.co/yWkHjCpr0u
#CyberSecurity#NetFlow#ThreatDetection
Zero Trust for OT doesn't mean touching controllers. Network telemetry provides visibility into industrial communications, helping teams assess activity without disrupting critical operations.
https://t.co/1qYXQt10DQ
#OTSecurity#ZeroTrust#NetFlow
No agent? You still need visibility. Network telemetry helps reveal unmanaged device activity and provides a second perspective alongside access controls.
https://t.co/BwB1xVntOz
#NetworkSecurity#NetFlow#NetworkVisibility
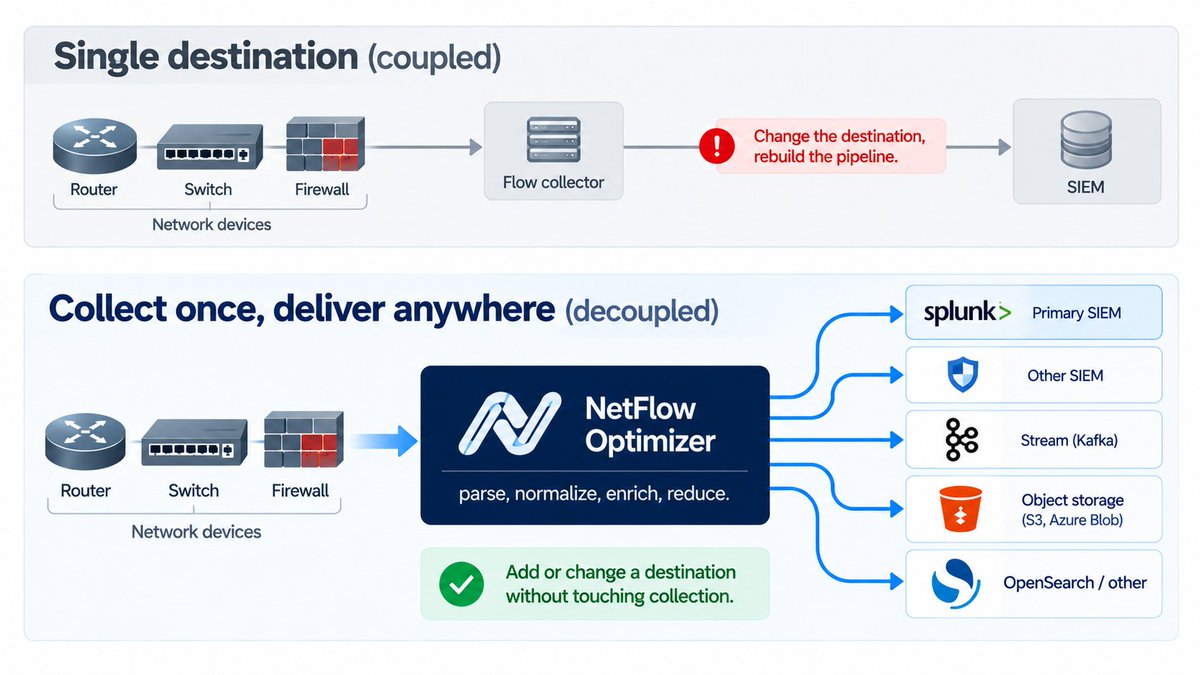
Collect once, deliver anywhere. Network telemetry shouldn't be locked into one destination. Send enriched data to your SIEM, analytics, and monitoring tools as your needs evolve.
https://t.co/AZCFHwrq0g
#NetFlow#NetworkTelemetry#SIEM
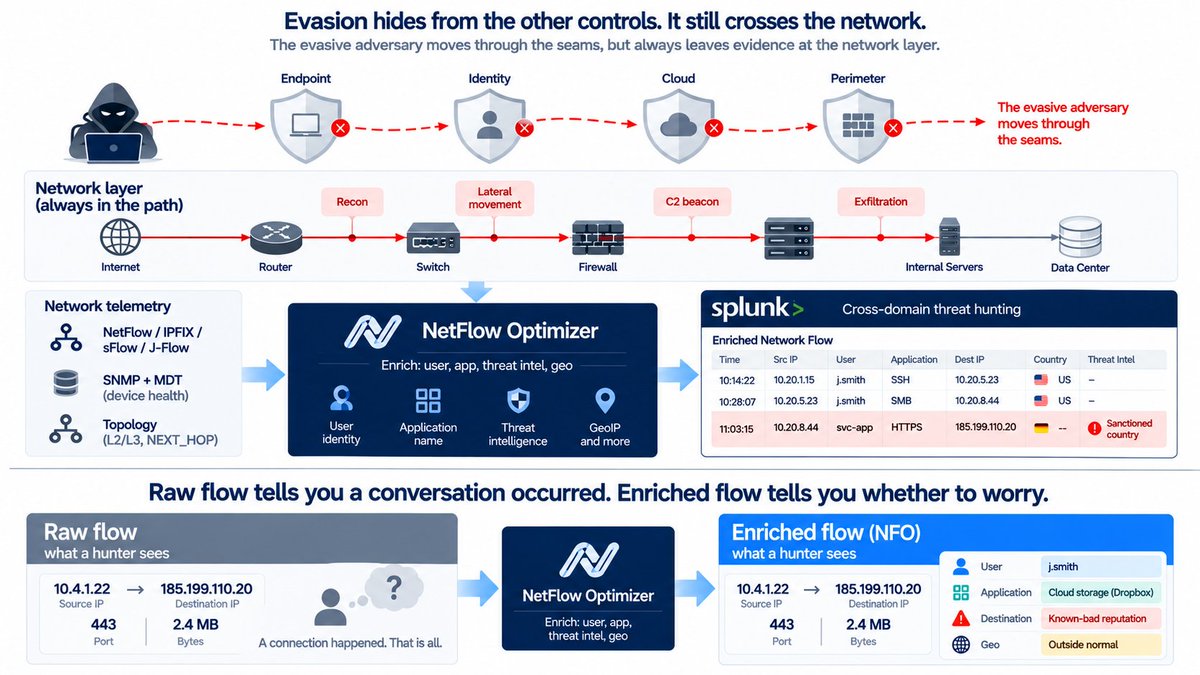
Evasive threats are harder to find when defenders lack network context. The 2026 Threat Hunting Report highlights why network visibility remains essential for finding what endpoint & identity data can miss.
https://t.co/MH93GP4hGm
#ThreatHunting#NetworkVisibility#CyberSecurity
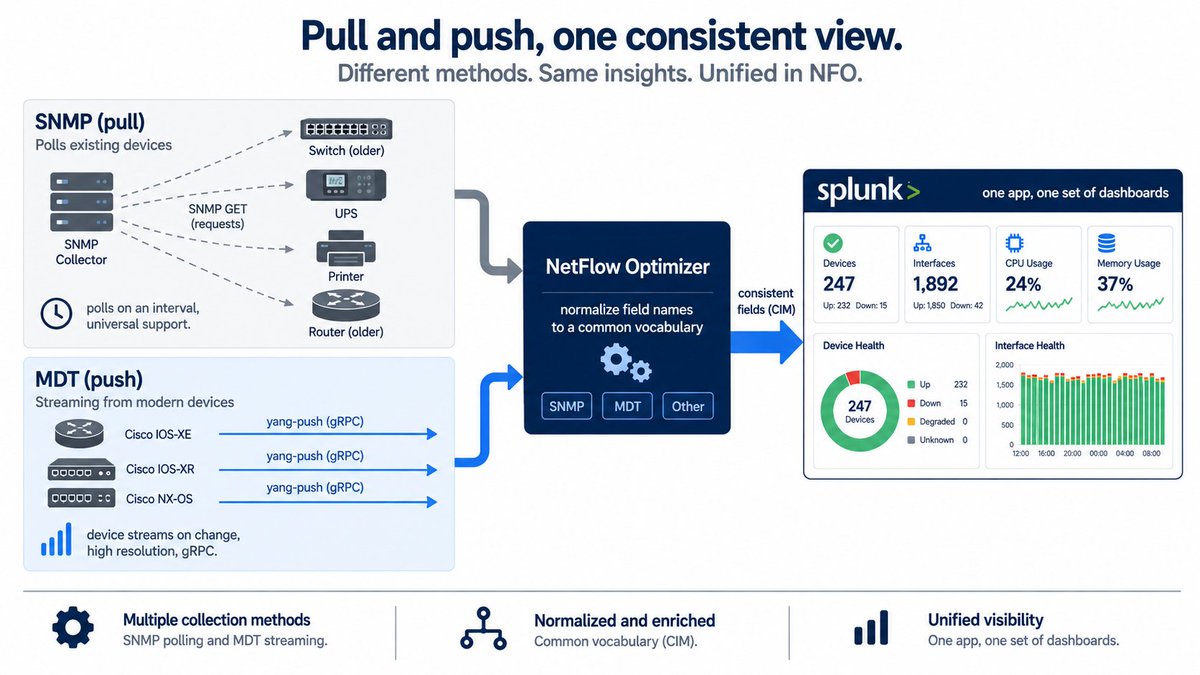
SNMP, MDT, and NetFlow each reveal a different part of the network. A common vocabulary connects them, turning separate telemetry streams into one consistent view.
https://t.co/z9vfvJqSBc
#SNMP#NetFlow#NetworkTelemetry
Correlated observability starts with consistent data. Normalized multi-vendor telemetry connects network data across vendors and tools, giving teams a more complete view.
https://t.co/q1Yqj7u5jG
#NetworkTelemetry#Observability#NetFlow
Model-driven telemetry provides richer, more frequent network data. SNMP remains valuable for device health and broad coverage. Why choose one when you can use both?
https://t.co/nxsMhXnAM5
#NetworkMonitoring#Telemetry#SNMP
Raw network telemetry creates noise. Enriched and normalized telemetry creates context—and gives SOC teams decision-ready data for faster detection and response.
https://t.co/9A5yt1gkWr
#NetFlow#NetworkTelemetry#SOC
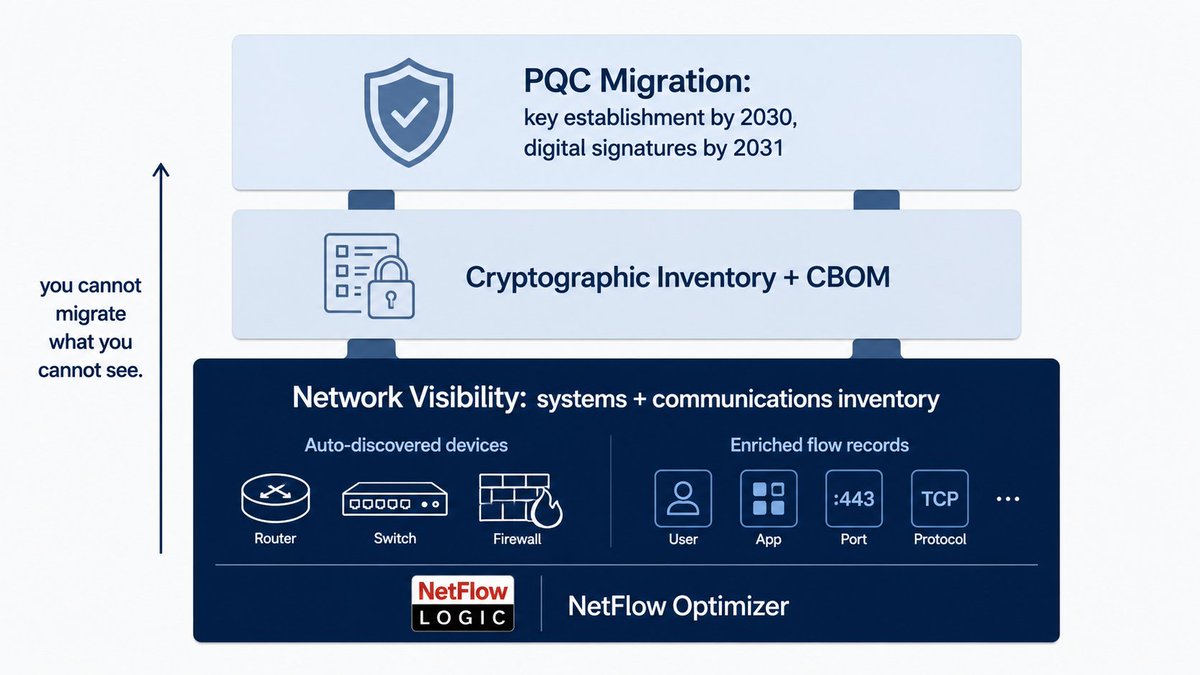
You can’t migrate what you can’t see. Post-quantum cryptography starts with knowing which systems exist and what they communicate. See how network visibility supports PQC migration.
https://t.co/BphVdYf1bS
#PQC#NetworkVisibility#CyberSecurity
SNMP shows how your devices are performing. NetFlow shows what traffic is crossing them. Correlating both gives network teams the full picture—without switching between tools.
https://t.co/kKBkdlugM2
#NetFlow#SNMP#NetworkMonitoring
Full-fidelity network telemetry doesn’t have to mean full-fidelity storage costs. Learn how a Machine Data Lake can make enriched network data more affordable to retain and analyze.
https://t.co/1k2EXGz0AJ
#NetFlow#NetworkTelemetry#DataLake
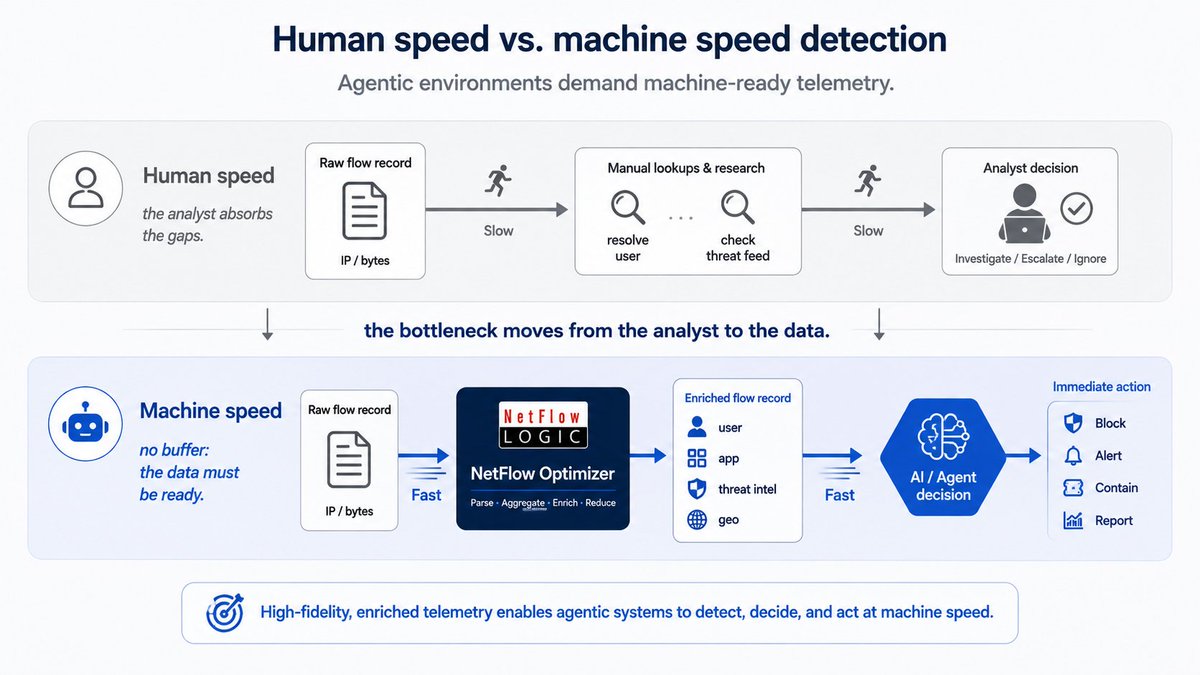
AI can detect threats in seconds—but only if it's fed the right data.
Raw telemetry creates blind spots. Enriched network data gives AI the context it needs to detect, prioritize, and respond faster.
https://t.co/O6fUHQqXb0
#CyberSecurity#AI#NetFlow#SOC
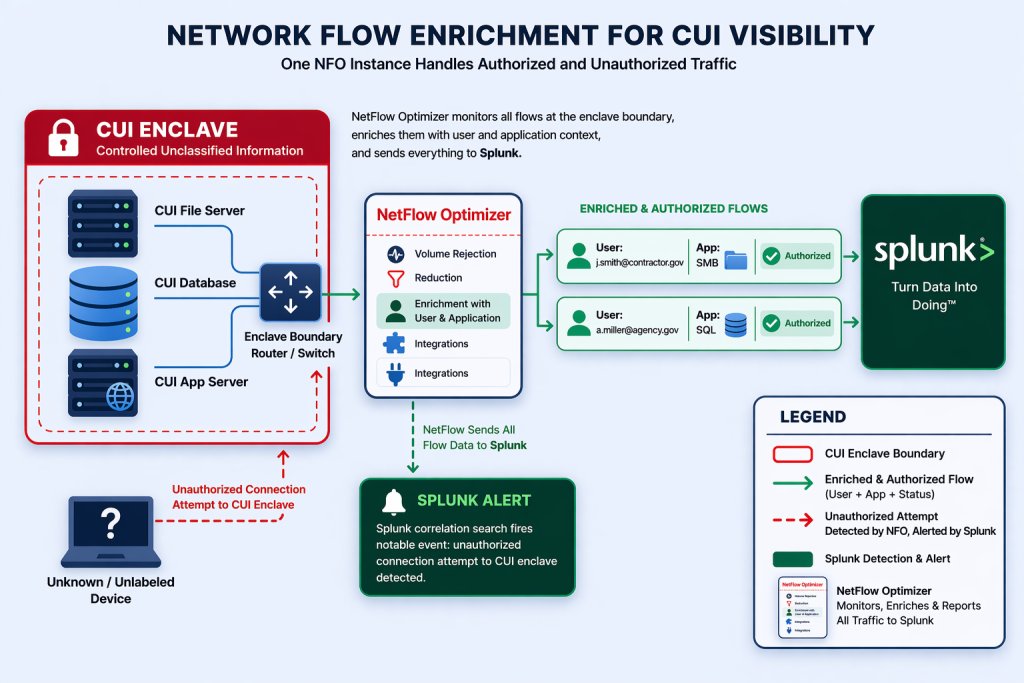
We've updated our "CUI on the Wire" post after the July 2026 CMMC Phase II suspension.
Certification paused. The requirement did not: DFARS 7012, NIST 800-171, and CUI protection still apply.
Enriched NetFlow is how you prove it.
#CMMC#CUI#NIST800171
https://t.co/KjLcNFjB7R
Migrating to a new SIEM? Don't lose network visibility during the cutover.
Learn how enriched NetFlow keeps monitoring continuous, reducing blind spots, helping SOC stay operational throughout the migration.
https://t.co/nkWyGySM6p
#SIEM#NetFlow#CyberSecurity#NetworkMonitoring
Agentic AI can generate 4.5× more network traffic than traditional applications.
Without enrichment and data reduction, flow telemetry can overwhelm your SIEM and hide critical insights.
Learn why enriched NetFlow is becoming essential:
https://t.co/eNbuXIRveJ
#AgenticAI#NetFlow
OT/ICS devices often can’t run security agents—but they still need protection.
See how NetFlow telemetry provides agentless visibility to monitor industrial networks, detect anomalies, and secure critical infrastructure.
https://t.co/5CF3bVxXI0
#OTSecurity#ICS#CyberSecurity
"Data quality is the primary constraint for agentic systems."
- Kamal Hathi, Splunk, Cisco Live 2026
AI agents need enriched NetFlow - users, apps, threat intel - not just IPs and bytes.
https://t.co/o2lYcUGQ5g
#AgenticSOC#NetFlow#Splunk#CyberSecurity#NetworkSecurity