CVE-2026-116945: RCE in Microsoft SQL Server, 9.8 rating 🔥
Heap-based buffer overflow in Microsoft SQL Server allows an unauthorized attacker to execute code over a network.
👉 https://t.co/pTjo1q15vl
CVE-2026-120017 and others: Missing authentication in SAP NetWeaver AS ABAP and other vulnerabilities, up to 10.0 rating 🔥
SAP published multiple vulnerabilities in its products. The most severe is a missing authentication vulnerability in SAP NetWeaver AS ABAP, which occurs when the SAML2 service provider fails to properly verify login assertions under certain configurations. An attacker could submit specially crafted data to bypass authentication and impersonate arbitrary users, including privileged accounts.
👉 https://t.co/eAilC5yF4I
CVE-2026-19868: SSLVPN Authentication Enforcement Vulnerability in SonicWALL SonicOS, 7.5 rating 🔥
An authentication enforcement vulnerability in SonicWALL SonicOS SSLVPN service could allow a user with valid credentials for an alternate method to bypass SAML authentication controls. This vulnerability is already being actively exploited in the wild!
👉 https://t.co/GK15HELzy5
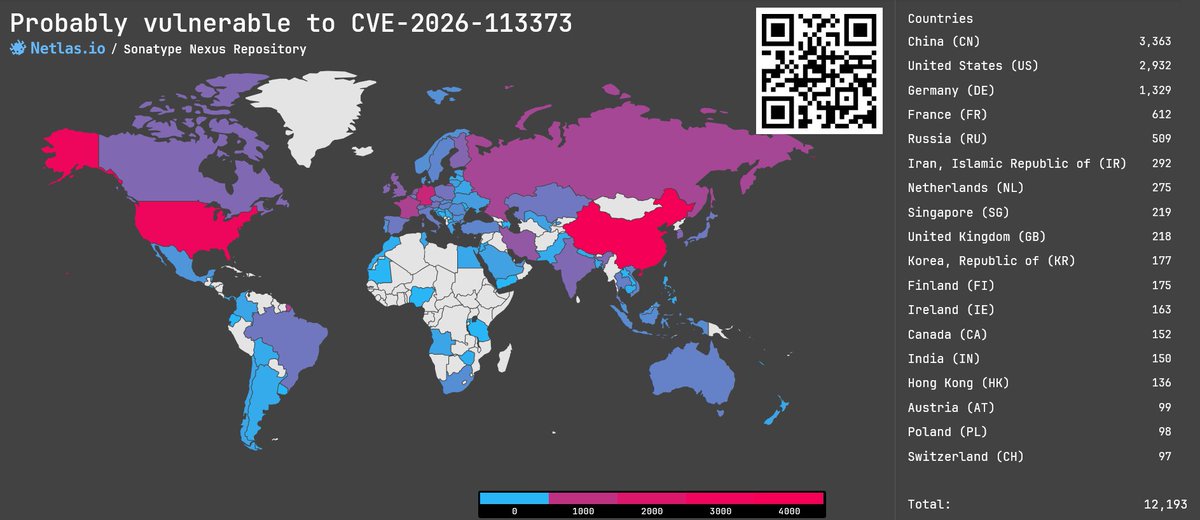
CVE-2026-113373 and others: Multiple vulnerabilities in Sonatype Nexus Repository, up to 9.1 rating 🔥
Sonatype disclosed multiple vulnerabilities in Sonatype Nexus Repository including a critical single sign-on bypass, admin takeover, SQL injection, and other security issues.
👉 https://t.co/EPrwQFsUqH
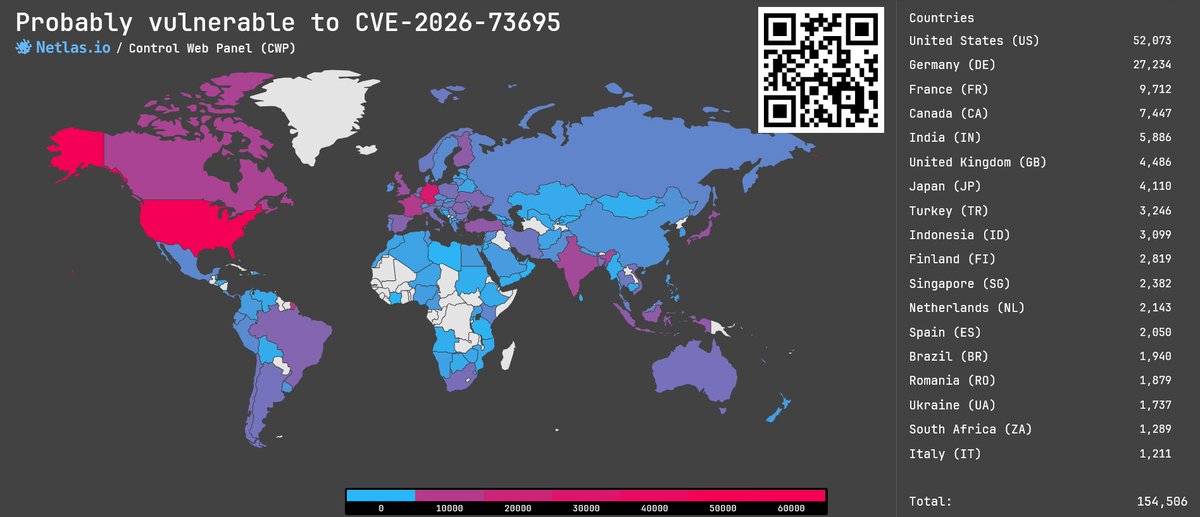
CVE-2026-73695 and others: Ten-vulnerability chain in Control Web Panel enables root access, 10.0 rating for the full chain 🔥
A recently disclosed chain of ten vulnerabilities in Control Web Panel (CWP) allows an attacker to execute code as a hosting user and escalate privileges to root.
👉 https://t.co/mqgMETITap
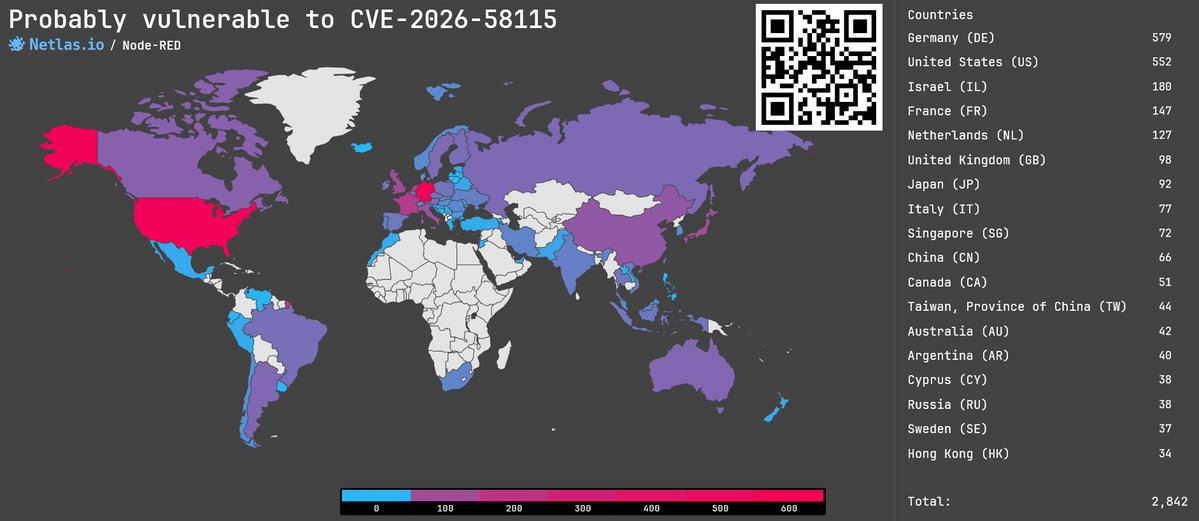
CVE-2026-58115: Actively exploited RCE in Node-RED, 10.0 rating 🔥
Disclosed in August'26, the missing-authentication vulnerability in Node-RED allows unauthenticated remote attackers to execute arbitrary system commands on exposed hosts. This CVE was assigned by Siemens, but other products and standalone Node-RED instances may also be affected. This flaw is currently being actively exploited in the wild!
👉 https://t.co/bgKUra2it3
CVE-2026-116241 and others: RCE via OS command injection and other new pgAdmin 4 vulnerabilities, up to 9.4 rating 🔥
The pgAdmin Development Team recently disclosed fifteen new vulnerabilities in pgAdmin 4. The most severe is an incomplete fix for CVE-2026-17566 that allows an attacker to execute arbitrary operating system commands on the pgAdmin host by using a specially crafted program clause.
👉 https://t.co/f1UL6oKAnC
Actively exploited RCE and other new WordPress vulnerabilities, no CVE assigned yet, 8.1 rating 🔥
The recently disclosed unauthenticated race-condition vulnerability in the WordPress Core update process can lead to remote code execution. This flaw is known to be actively exploited in the wild!
Other disclosed vulnerabilities include stored XSS, DoS, information disclosure, and authorization weaknesses.
👉 https://t.co/IsKa09DHjD
☀️Fingerprinting Exposed Solar Inverters with Netlas
In March 2025, Forescout's SUN:DOWN report showed that reaching enough inverters at once could nudge the grid. And a surprising number of them are reachable.
See what inverters reveal about themselves — and how Netlas turns that into a map.
👉 https://t.co/2G7X4Se4Hi
CVE-2026-103594 and others: Multiple vulnerabilities in WatchGuard Fireware OS, up to 9.5 rating 🔥
WatchGuard disclosed seventeen vulnerabilities in Fireware OS. The most severe flaws allow unauthenticated attackers to cause a DoS condition and potentially execute arbitrary code or invoke privileged system-level administrative actions.
👉 https://t.co/gjRpEUoSm5
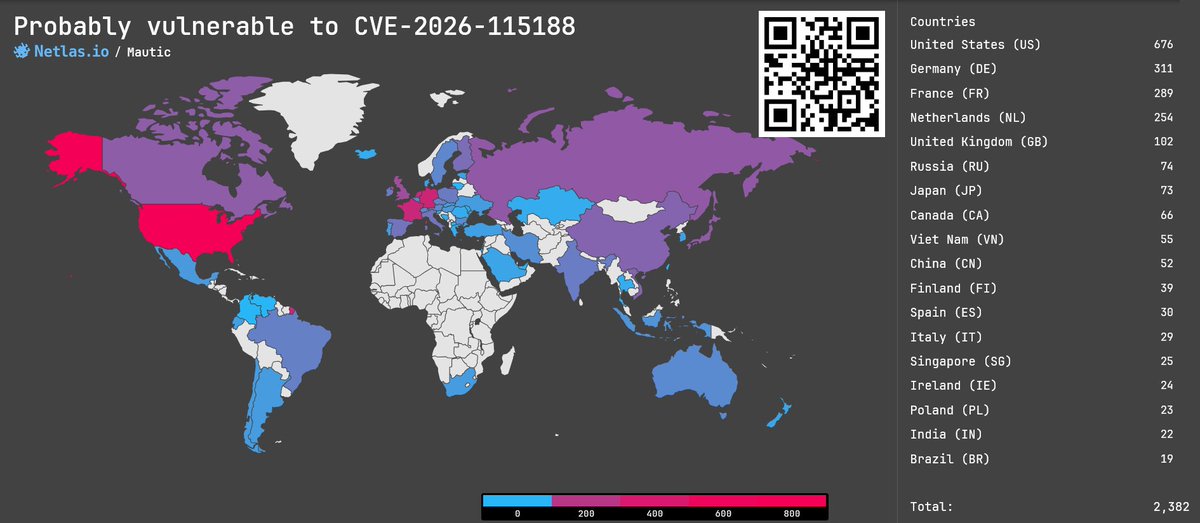
CVE-2026-115188 and others: Multiple vulnerabilities in Mautic, up to 9.9 rating 🔥
The Mautic project disclosed multiple vulnerabilities in the open-source Mautic marketing automation platform, including remote code execution (RCE) via unrestricted file upload, sandbox escape, PHP object injection, blind SQL injection, stored XSS, and other security flaws.
👉 https://t.co/5mInRTV198
CVE-2026-89078, CVE-2026-93577, CVE-2026-97229, and CVE-2026-110264: Four CVEs in Ruby’s regular expression engine, discovered by GitLab, up to 10.0 rating 🔥
Last week, the Ruby team released patches for several bugs in Ruby’s regular expression engine (Onigmo). GitLab found that these bugs could be exploited for RCE on GitLab servers. The same risk applies to any other Ruby application that compiles user-supplied regular expressions.
👉 https://t.co/YsKHXoiAtr
CVE-2026-114625: Actively exploited SQL injection flaw in Arista VeloCloud Orchestrator, 9.9 rating 🔥
Arista has disclosed a new SQL injection vulnerability in VeloCloud Orchestrator that allows any authenticated user to gain operator privileges and impersonate a local user with "superuser operator" privileges. This issue is known to be actively exploited!
👉 https://t.co/Vx07qoOjfg
📟Fingerprinting Exposed Siemens S7 PLCs with Netlas
In 2010, Stuxnet targeted Siemens PLCs. Over 15 years later, thousands still expose their model, firmware version, and internal names on TCP port 102.
See how a few Netlas queries narrow thousands of exposed S7 services to the ones worth a closer look.
👉 https://t.co/nUAKyidgqw
🎥Turning Recon Data into Findings with Netlas
In his video, ZACK0X01 walks through the reconnaissance and scanning workflow behind his AI agent, showing how Netlas turns raw recon data into actionable findings.
You'll see how certificate and favicon hash searches find assets missed by subdomain enumeration, and how scanning reveals services and tech in JSON.
👉 https://t.co/WgTYGc8Yub
CVE-2026-110264 and others: 12 new vulnerabilities in GitLab, up to 10.0 rating 🔥
GitLab has disclosed 12 new vulnerabilities affecting GitLab CE & EE. The most severe allows an unauthenticated remote attacker to execute arbitrary code on the GitLab server.
👉 https://t.co/F3PqRxVMU3
CVE-2026-109618 & CVE-2026-109619: Two RCE vulnerabilities in PHP (PHP2Shell), rating 9.2 for both 🔥
Today the PHP security team released an emergency update addressing two critical vulnerabilities in the PHP core, which allow unauthenticated remote code execution as the web worker account.
Details of the two vulnerabilities were disclosed by researchers yesterday, ahead of today’s release.
👉 https://t.co/5CEkPY6KPT
🔍Using Netlas in Houdin
One ThreatFox indicator, one default certificate, and Netlas data in between: Houdin traces how a single alert turns into a list of servers running CyberStrikeAI, an open-source platform for AI-assisted attacks.
👉 https://t.co/qXrn3bputc