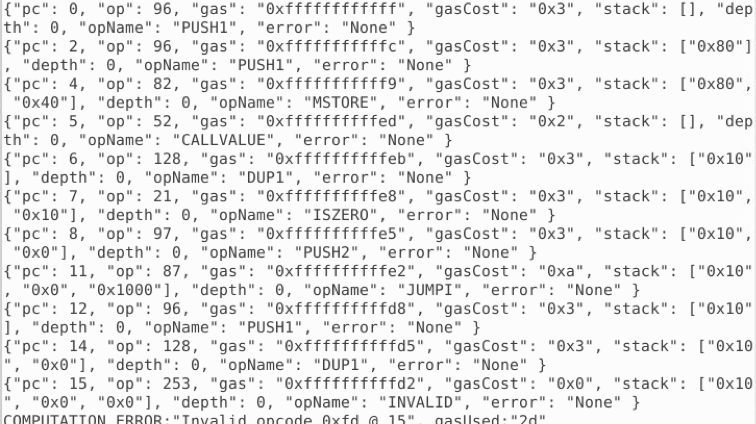
It is not our intention to cause confusion. We are proud that our algorithm detected a vulnerability in a minor EVM implementation. Meanwhile we are testing go and js implementations. Our goal is to make blockchain ecosystem more secure through our research.
We would like to emphasize that the vulnerability we found is in the python implementation of EVM, not in parity-evm or Geth. Our purpose is to let the community to know about the existence of such an issue in py-evm and fix the bug as soon as possible.
Following the discovery of the EVM vulnerability that is accepted by CVE, Vitalik communicated immediately with us at Netta Labs and confirmed that the vulnerability is in py-evm. Afterwards Parity Technologies, the company founded by Dr. Gavin Woods that implements parity-evm,
Meanwhile, we are testing the js and go EVM implementations. We at Netta Labs want to do more research and build more secure systems for blockchains, starting with Ethereum.
Netta Labs discovered an Ethereum EVM vulnerability, which could be exploited by hackers. The vulnerability can cause smart contracts can be executed indefinitely without gas being paied.