We’re an information security practitioner-focused company dedicated to providing impactful, high quality training and education. Founded by @chrissanders88.
You can learn more about our Analyst Skills Vault and sign up here:
https://t.co/a2oPMmt5OT. We have monthly and annual subscription options and add new videos every month.
Adversaries can manipulate filesystem timestamps to confuse defenders and evade detection. In this lesson, @DunhamSec will look at how adversaries perform timestomping and how to identify it on Windows and Linux host artifacts.
Practical Threat Hunting is a structured system to ensure you’re never at a loss for what to hunt for, where to find it, and how to see it amongst the noise. https://t.co/U8RcTRnlrY
You can learn more about our Analyst Skills Vault and sign up here: https://t.co/a2oPMmt5OT. We have monthly and annual subscription options and add new videos every month.
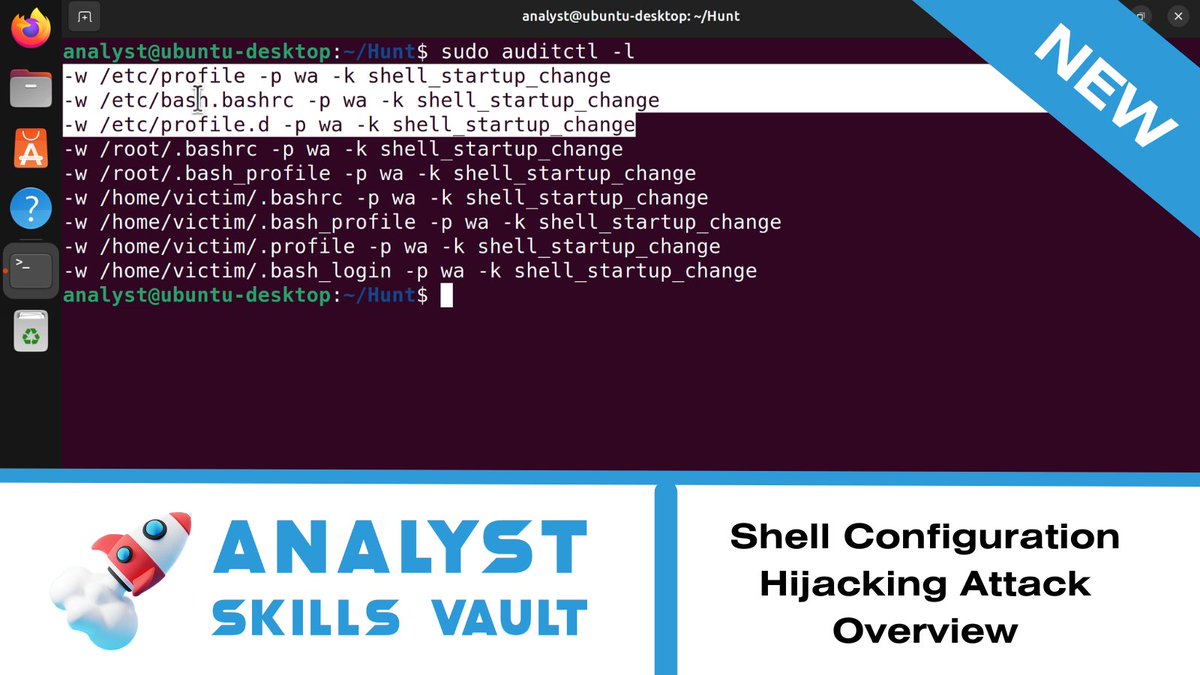
In our latest Skills Vault lesson from Dan Marr, learn how attackers abuse shell startup configuration files to harvest credentials, establish persistence, and perform other malicious actions. We'll also show you how to detect and investigate the attack!
Practical Threat Hunting is a structured system to ensure you’re never at a loss for what to hunt for, where to find it, and how to see it amongst the noise. https://t.co/U8RcTRnlrY
Detection Engineering with Sigma will teach you how to write and tune Sigma rules to find evil in logs using real-world examples that take you through the detection engineering process. https://t.co/esMzhlnNWP
You can learn more about our Analyst Skills Vault and sign up here: https://t.co/a2oPMmt5OT. We have monthly and annual subscription options and add new videos every month.
Attackers love creating mailbox forwarding rules to hide persistence and exfiltration. In our latest Skills Vault lesson, @DunhamSec will show you how they do that and techniques to finding and investigating those artifacts. He'll give you the techniques and queries he uses!
Detection Engineering with Sigma will teach you how to write and tune Sigma rules to find evil in logs using real-world examples that take you through the detection engineering process. https://t.co/esMzhlnNWP
Practical Threat Hunting is a structured system to ensure you’re never at a loss for what to hunt for, where to find it, and how to see it amongst the noise.
https://t.co/U8RcTRnlrY
You can learn more about our Analyst Skills Vault and sign up here: https://t.co/a2oPMmt5OT. We have monthly and annual subscription options and add new videos every month.
Ever wondered how attackers leverage WMI for persistence? In our latest Analyst Skills Vault lesson, Dan Marr demonstrates the technique and how to detect and investigate it.