a new era for @HyperliquidX starts with @Enter_Elysium
from day one, Elysium users can automate their trades using Bloom features like Copy Trading, AFK setups, Spot + X Automation.
e/acc
All Refunds Successfully Processed | 9,408 SOL Refunded
We confirm that 100% of the affected funds, totaling 9,408 SOL, have been fully refunded to all 9 users impacted by the recent security incident.
As part of our commitment to transparency, all refund transactions are publicly verifiable on Solscan.
1. https://t.co/31A4x5mFJt
2. https://t.co/leRXXtomok
3. https://t.co/sHwCbIDOcm
4. https://t.co/bBaVzvr440
5. https://t.co/1O3maPUxM6
6. https://t.co/cH2Y6K5Dzm
7. https://t.co/bhR4zmfnRP
8. https://t.co/CrsZ2Jvi80
9. https://t.co/kJRZySMmpC
Our commitment to our users, their security, and their trust remains our highest priority.
The Bloom Team
@ColerCooks Up to u if u believe it or not.
I said what happened.
There is no point for lying for onchain stuff cause like what happened now u would know that.
I just told u what I checked.
No I was not lying
Due to our investigation our system dashboard was not working correctly that’s why I didn’t see ur wallet in our system. Also I checked bloom route.
https://t.co/OcL6FavNGj
No activity. Thats why I said that.
I didn’t say bloom was not attracted
I said urs was not related to what happened to bloom.
Check ur drainer wallet, timing etc.
what happened to u was not because of bloom.
@ModoMonkeyMan@ColerCooks This case is not related to bloom.
The drain that happened we address it and made an announcement about
But for this wallet it was not because of bloom.
U can check the drainer wallet, timing etc.
it’s not related to the attack happened to us.
Official Statement | Security Incident Update
TL;DR: No private keys were compromised, unaffected wallets are safe, and all affected users will be fully reimbursed by Bloom.
Following our investigation, we have identified the exact attack vector and confirmed the scope of the incident.
The attack exploited a third-party module through a complex Remote Code Execution (RCE) vulnerability. No private keys were accessed or compromised, and we have ruled out broader exposure of users' wallets.
Incident Overview
Affected: 49 wallet addresses belonging to 9 users.
• Total losses: Approximately 9,408 SOL ($947,000).
• Root cause: Exploited third-party module enabling an RCE vulnerability.
• Refunds: Bloom will fully reimburse 100% of the stolen funds directly to secure wallets designated by the affected users.
• We are also working to trace the stolen funds, explore recovery and freezing options, and identify the attacker.
Our team has been developing software since 2018 and operating in crypto since 2021. We are an established team, committed to building for the long term and protecting the trust of our users.
Security threats are an unfortunate reality of this industry, even with extensive precautions in place. Our commitment to user safety, transparency, and business continuity remains unchanged.
The Bloom Team
This is not an exit scam. We're actively investigating the security incident and have already committed to fully reimbursing all 9 affected users.
Our team has been building software since 2018. We're well-established and would never compromise our reputation or integrity.
Our priority is making every affected user whole and identifying the root cause. Further updates will follow.
this is what you missed while being AFK.
$SI → $67M
$AGENCY → $29.7M
$CRAWL → $7.1M
$HUMAN → $6.2M
or you set your filters once and let AFK Auto Buy catch the next one for you.
your call, anon.
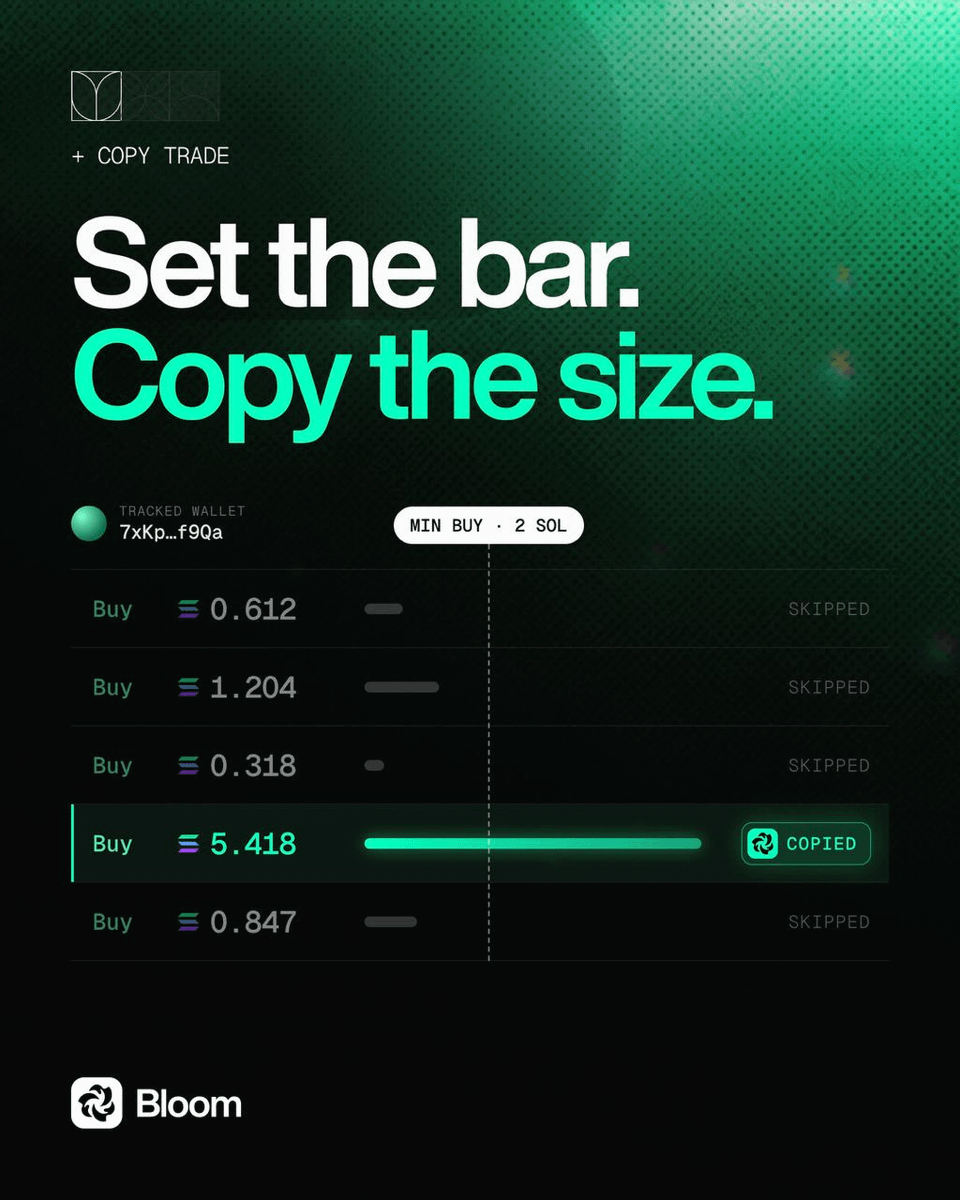
𝚌̶𝚘̶𝚙̶𝚢̶𝚝̶𝚛̶𝚊̶𝚍̶𝚎̶ copy conviction.
With Bloom's Copy Trading, set a minimum buy size for the target wallet.
Bloom ignores smaller entries and copies only the buys that meet your minimum size.
Skip the small buys. Copy conviction.