Creating this book with you has been a true honor!
I’m deeply grateful for your mentorship, your intention, and the care you brought to every detail. I’m so proud of what we created together. 🥰
Working with you taught me so much...not just about clarity and attention to detail, but about intention. Your “why” for this book, helping your daughters understand what you do and why it matters.. really touched my heart. ❤️
The past few years in crypto and web3 have been incredibly difficult for so many of us. There were moments where I questioned myself: Is this really how I want to identify myself?
Being able to create alongside someone who has dedicated nearly a decade to this space, especially through its darkest most uncertain moments, was truly humbling. It gave me a deeper sense of purpose and reminded me why thoughtful, human-centered work like our book matters.
Thank you for your trust, your guidance, and your belief in this story. It was a privilege to build Nyla the NFT with you, and I’m incredibly proud of what we put into the world together.
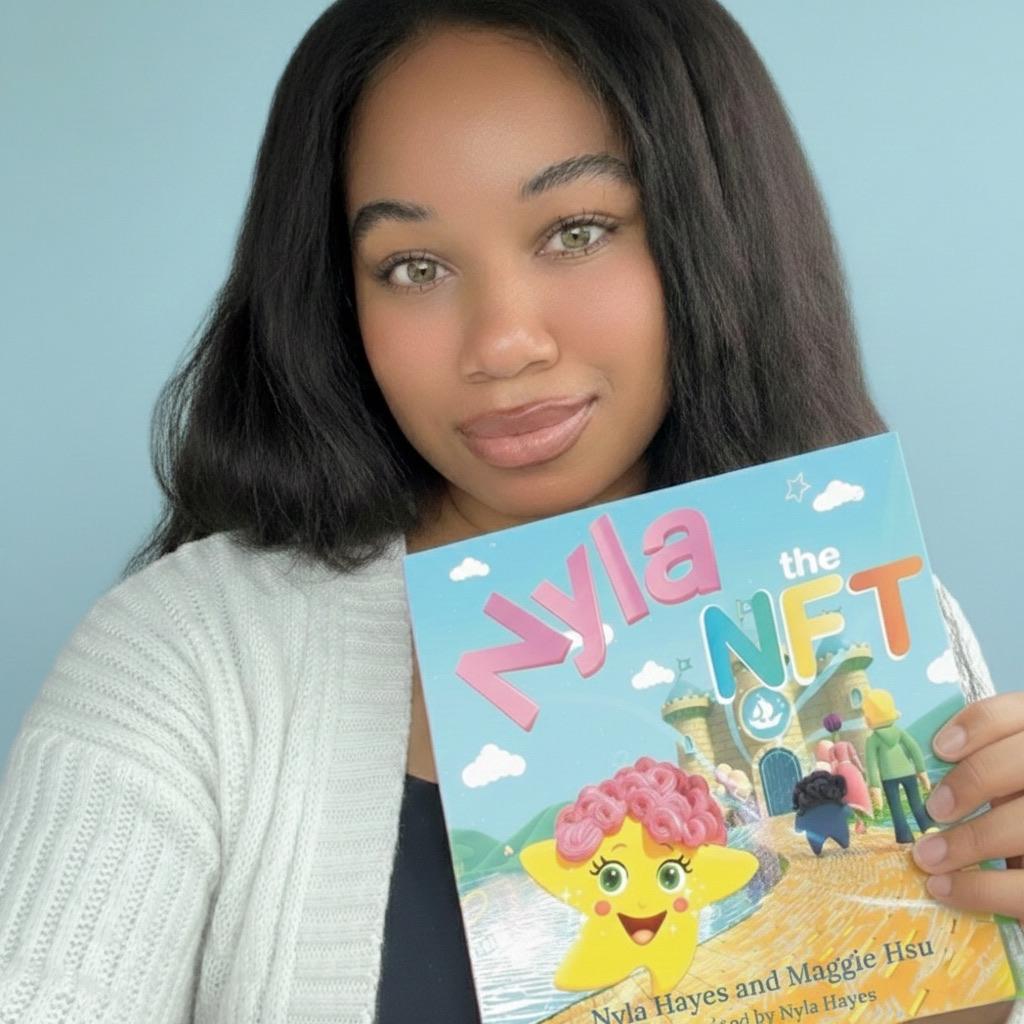
As I return from maternity leave, I'm excited to share the result of a fun maternity leave side quest: Nyla the NFT is a children's book about a star named Nyla, who learns that her unique characteristics are what make her an NFT. I enjoyed collaborating with the real-life Nyla @NylaCollection on this project
What a brutal day today...
Major vulns people are struggling to fix right now
- PHP2Shell allows unauthenticated remote code execution on affected PHP servers. CISA is advising organizations to patch or take affected systems offline (this is absolutely nuts, basically the majority of websites w/known server-side language ~70% are being told to immediately upgrade or shut down). There’s also a disclosure controversy: Chainguard co-founder Dan Lorenc released patched builds over six hours early. The PHP Foundation says that exposed the fix for attackers to study and Dan says existing leaks and reports of active exploitation justified making the builds available to everyone.
- Node.js just patched ten vulnerabilities, including remote code execution through its Brotli decoder and separate TLS validation bypasses. There are so many codebases built on Node that a lot of teams now need to check whether they’re affected
- One of eMudhra’s (an Indian certificate authority whose certificates are trusted by browsers) certificate authority private keys was literally 4. Eight keys were trivially recoverable since April 2025.
- GitLab also recently patched a 10/10 vulnerability allowing unauthenticated code execution. Researchers dream of scoring a 10/10 CVSS score, and this one was on a version control system running half of all F100s.
Major exploits and breaches
- LiteLLM is a widely used library for connecting applications to AI models. Its 1.107.0 release on PyPI was compromised and shipped with a credential stealer and a backdoor. People installing what looked like a normal update were downloading malware.
- Railway disclosed that attackers may have accessed customer environment variables and decrypted some of them, potentially exposing API keys and database passwords. They’re asking all users to rotate stored secrets.
- OpenCode disclosed a breach affecting 1.4% of Console users a few days ago, tied to what it describes as a large-scale distillation attack. I’d just started using OpenCode, so this one hit a little to close to home.
- State Bank of India confirmed that personal and loan data belonging to 3,897 customers surfaced on the dark web.
- PHP2Shell is already being targeted too. AWS observed exploitation attempts dating back to October 17. Also the CEO of Cloudflare said they've seen it be attempted millions of times within several hours of the release.
I mean serious what the fuq...
we’re opening the opensea app to the public today. three big things about this launch:
social trading is now open
social trading is here, but it’s fragmented. what’s done in public on one app just lives on that app. onchain social graphs and profiles should be aggregated, open, and easy to traverse
starting today, traders from fomo, pump, and farcaster show up on opensea with their profiles and their trades in your feed. follow them, open any profile or wallet, and dig into what they’re doing. if one of those profiles is yours, import the wallet that owns it and claim it
today it’s basic aggregation. next we get smarter about what to show you, and give you more and more customization, so the most relevant trading signals rise to the top
your portfolio, your trading, and your profile in one place
today’s crypto users have balances across a few apps. you can start that way on opensea too: create a fresh wallet in a couple taps, fund it with Apple Pay, and trade without thinking about chains or wallets
but over time we think you will want more control. so we’re launching:
- track everything: link any wallet into one view and track everything you own. wallets you’ve used on opensea before link in a couple taps via web
- trade from any of it: every account comes with a wallet ready to trade. import the wallets you already use and trade coins, memes, art, trading cards
- pick what people see: choose which wallets show on your profile, set an NFT as your onchain pfp, and start creating your own native trading signals on opensea. this becomes one home for your onchain history, across every wallet and app.
trade everything, together
this is all built on top of cross-chain liquidity, real-time pricing, reliable execution, and increasing coverage for onchain assets, which we believe are tablestakes for all noncustodial consumer trading apps.
this launch: everything onchain, assets, markets, people, in one open place.
next: making it easier to trade and build together onchain. open markets, open profiles, and track records you can check, so anyone, anywhere can find each other, trust each other, and team up
lots to build. come try the new opensea: https://t.co/sHJokCjoIn