🚨 AI changed how software gets built. Security is still playing catch-up.
Agents now write code, connect to tools, provision infrastructure, and execute workflows in real time—while AppSec and CNAPP remain built for a human-led world.
OX Security is the first prompt-to-runtime platform built to secure the full agentic development lifecycle, defining the emerging AINAPP category.
The Mythos Age needs a new security model.
OX built it.
➡️ https://t.co/W2ZVFUfdSC
--
#AINAPP #AISecurity #CyberSecurity
🚨 24 hours later, 99.3% of measurable PHP instances are still unpatched.
📊 FULL REPORT: https://t.co/IIi7D81PEA
CVE-2026-109618 + CVE-2026-109619 allow unauthenticated RCE.
The patch is out. The exposure isn’t.
Patch now: 8.2.35, 8.3.36, 8.4.27, or 8.5.12.
#CyberSecurity #PHP #CVE
🚨 3 critical Pillow CVEs. RCE + heap overflows.
📊 FULL REPORT: https://t.co/YqKvKl2RMB
CVE-2026-112900, CVE-2026-112393 + CVE-2026-112403 can lead to code execution, memory corruption, data exposure and crashes.
Upgrade Pillow to 13.0.0+
#CyberSecurity#Python#CVE
❗ If 2 PHP vulns weren't enough for one day (or, 0-day?) - LiteLLM were compromised today by a combined RAT Infostealer malware!
TLDR - LiteLLM PyPI ver 1.107.0 is compromised, if you installed it - revoke keys and change passwords ASAP.
The malware combines two threats in one package: an infostealer that harvests secrets from the machine, and a remote access trojan (RAT) that lets the attacker connect remotely and control the affected machine.
The malicious code was injected only into the “wheel” package, so reviewing the repository and the “clean source” would not have revealed anything wrong. The malware also contacts the URL litellm[.]dev, which is an attacker bought domain that could easily be seen as a legitimate domain instead.
While this might look like “yet another PyPI malware”, hiding inside the wheel file is one of the new ways attackers use to stay hidden and bypass common detections, like in npm, whenever a new protection is added – such as blocking preinstall hooks, threat actors will go out of their ways to find new techniques to reach their goals and execute code without being detected.
If you’re yet to pin versions or add a time-based installation delay, this should be yet another wake up call to take the time and do so before it is too late. Once these passwords and credentials are out, remediation will take longer than it takes threat actors to get what they want.
Read the full blog:
https://t.co/3n5Pf3wFMi
🚨 PATCH NOW: two critical PHP flaws allow unauthenticated RCE.
CVE-2026-109618 + CVE-2026-109619 are fully disclosed and patched. Both carry a CVSS 9.2.
📊 FULL REPORT: https://t.co/ZWmUU5RytG
Two flaws in PHP session handling can allow arbitrary code execution without authentication.
Patch now: 8.2.35, 8.3.36, 8.4.27, or 8.5.12.
#CyberSecurity #PHP #CVE
🚨 BREAKING: Two critical PHP CVEs. No patch yet.
FULL STORY: https://t.co/5S2t41VXlv
CVE-2026-109618 + CVE-2026-109619 are rated 9.2.
Until the fix drops:
✅ Disable unused file uploads
✅ Be ready to patch fast
❌ Don’t trust leaked version lists
❌ Don’t run unofficial PoCs/scanners
More to come.
#CyberSecurity #PHP #CVE
Next stop on Moshe’s fall tour: Orlando 🎸
OX Research Team Lead @moshetov is taking the stage at @InfoSec_World for:
𝐒𝐡𝐚𝐝𝐨𝐰 𝐈𝐧𝐟𝐫𝐚𝐬𝐭𝐫𝐮𝐜𝐭𝐮𝐫𝐞: 𝐁𝐥𝐢𝐧𝐝𝐬𝐩𝐨𝐭𝐬 𝐢𝐧 𝐎𝐫𝐠𝐚𝐧𝐢𝐳𝐚𝐭𝐢𝐨𝐧𝐚𝐥 𝐒𝐞𝐜𝐮𝐫𝐢𝐭𝐲
A look at the infrastructure organizations create, inherit, and depend on — and the security blind spots hiding outside the places teams are actually watching.
📅 Wednesday, October 14
⏰ 3:15 PM ET
📍 Orlando, FL
See you in Orlando 🤘
🔗 More info: https://t.co/lseKcGwKgc
⏰ Less than 24 hours left to register!
🎟️ REGISTER NOW: https://t.co/YYxfV85mv0
Tomorrow, @JamesBerthoty, Founder & CEO of @latiotech, and Chris Lindsey, Field CTO at OX, break down what happens when AI workloads and autonomous agents become part of your cloud attack surface.
We’ll cover:
→ Where agentic risk is showing up
→ How AI is changing the cloud threat landscape
→ How reachability can help separate real risk from noise
→ What security teams should be doing now
📅 Oct 13
⏰ 12 PM ET | 9 AM PT | 6 PM CET
👉 More info: https://t.co/YYxfV85mv0
#CloudSecurity #AI #Cybersecurity
🚨 Shai-Hulud just hit an AI sandbox.
OX Research found [email protected] infected with Shai-Hulud — a package with 12K+ weekly downloads.
FULL REPORT: https://t.co/wTPbiO9OOb
5 GitHub repos were found with stolen credentials. If you installed it, isolate the host and rotate creds.
#CyberSecurity #SupplyChainSecurity #npm
🚨 One webhook. Your cloud credentials are gone.
FULL REPORT: https://t.co/3wuORLvImi
OX Research disclosed an SSRF flaw in Harbor that could let a registered user reach cloud metadata and steal IAM credentials — no admin required.
6,370 pre-fix instances were internet-reachable.
#CyberSecurity #CloudSecurity #CVE
MCP marketplaces have a trust problem.
@OX__Security analyzed 15,465 publicly indexed MCP servers across 5 registries and found no marketplace vetting.
Among the findings:
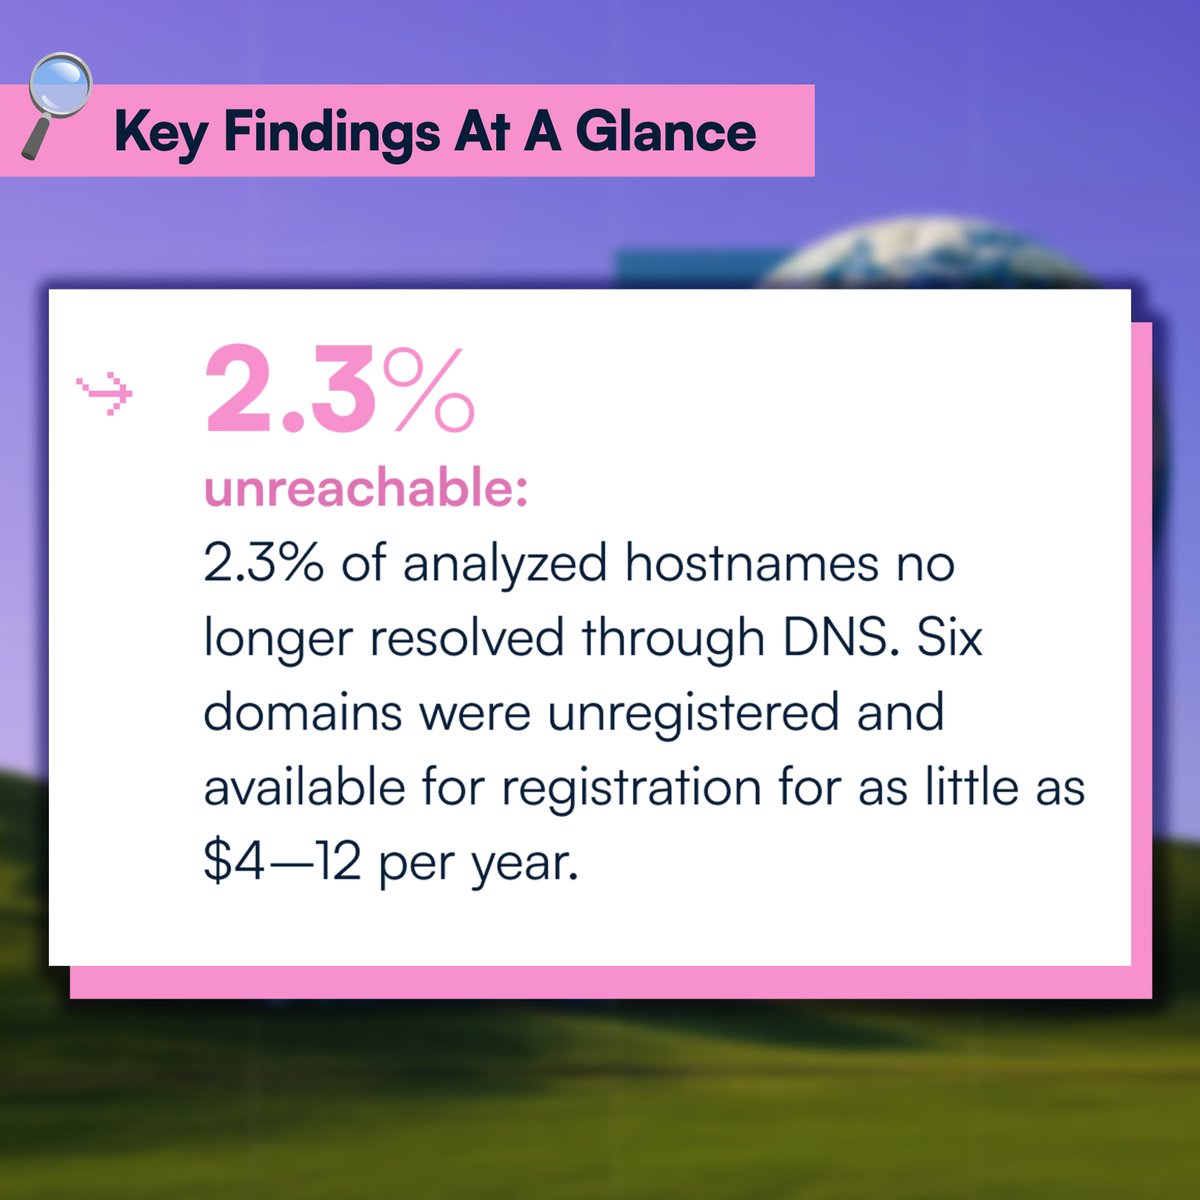
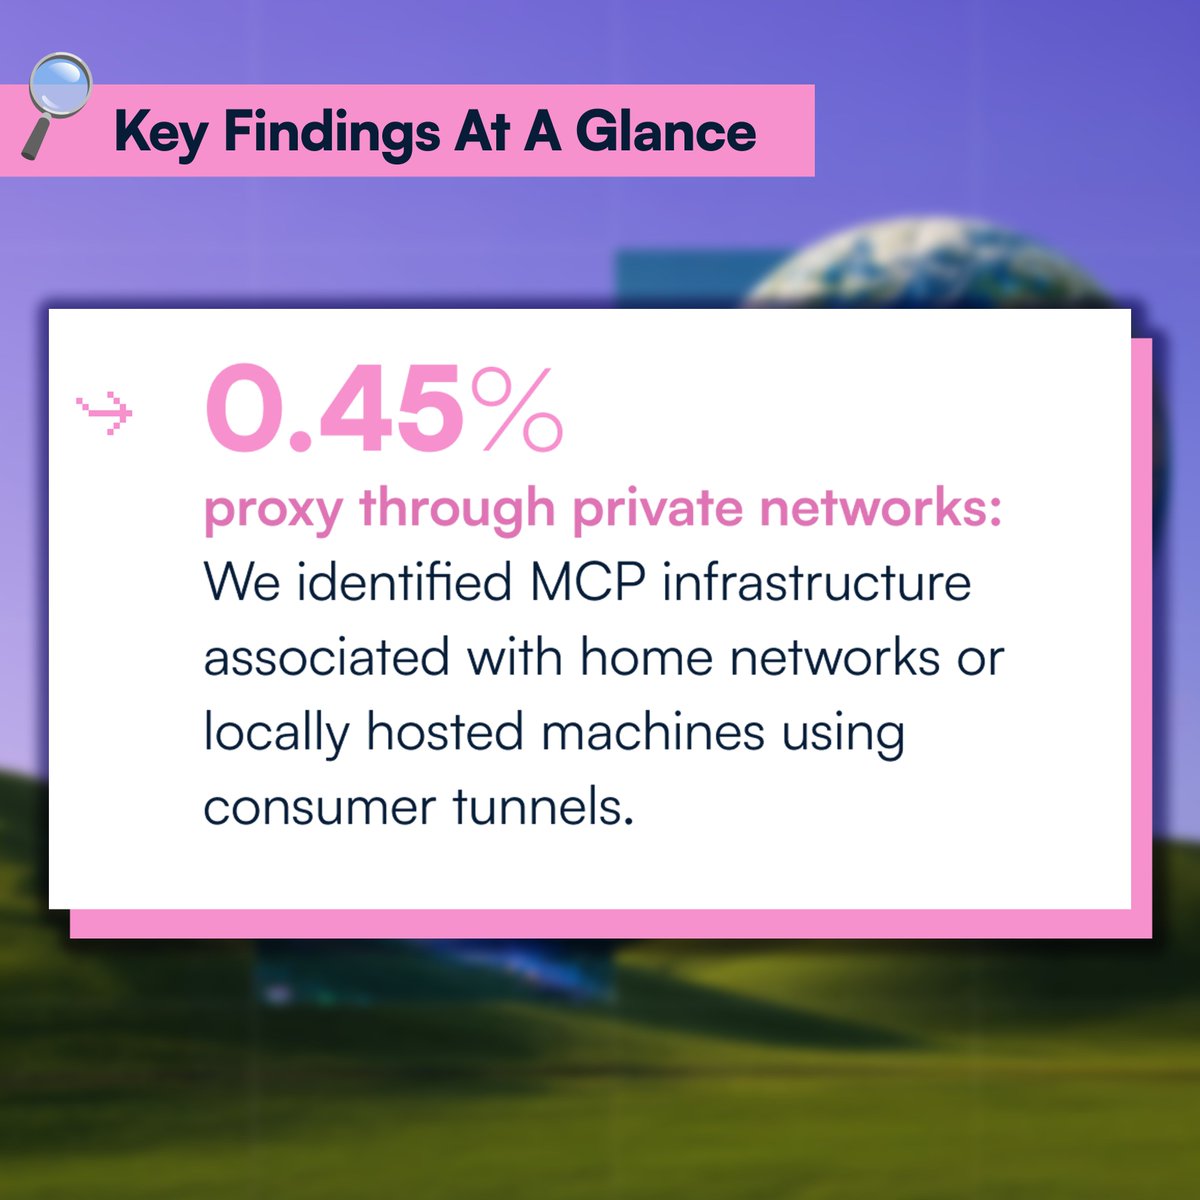
• 2.3% of hosts no longer resolve
• 6 use expired domains anyone could re-register
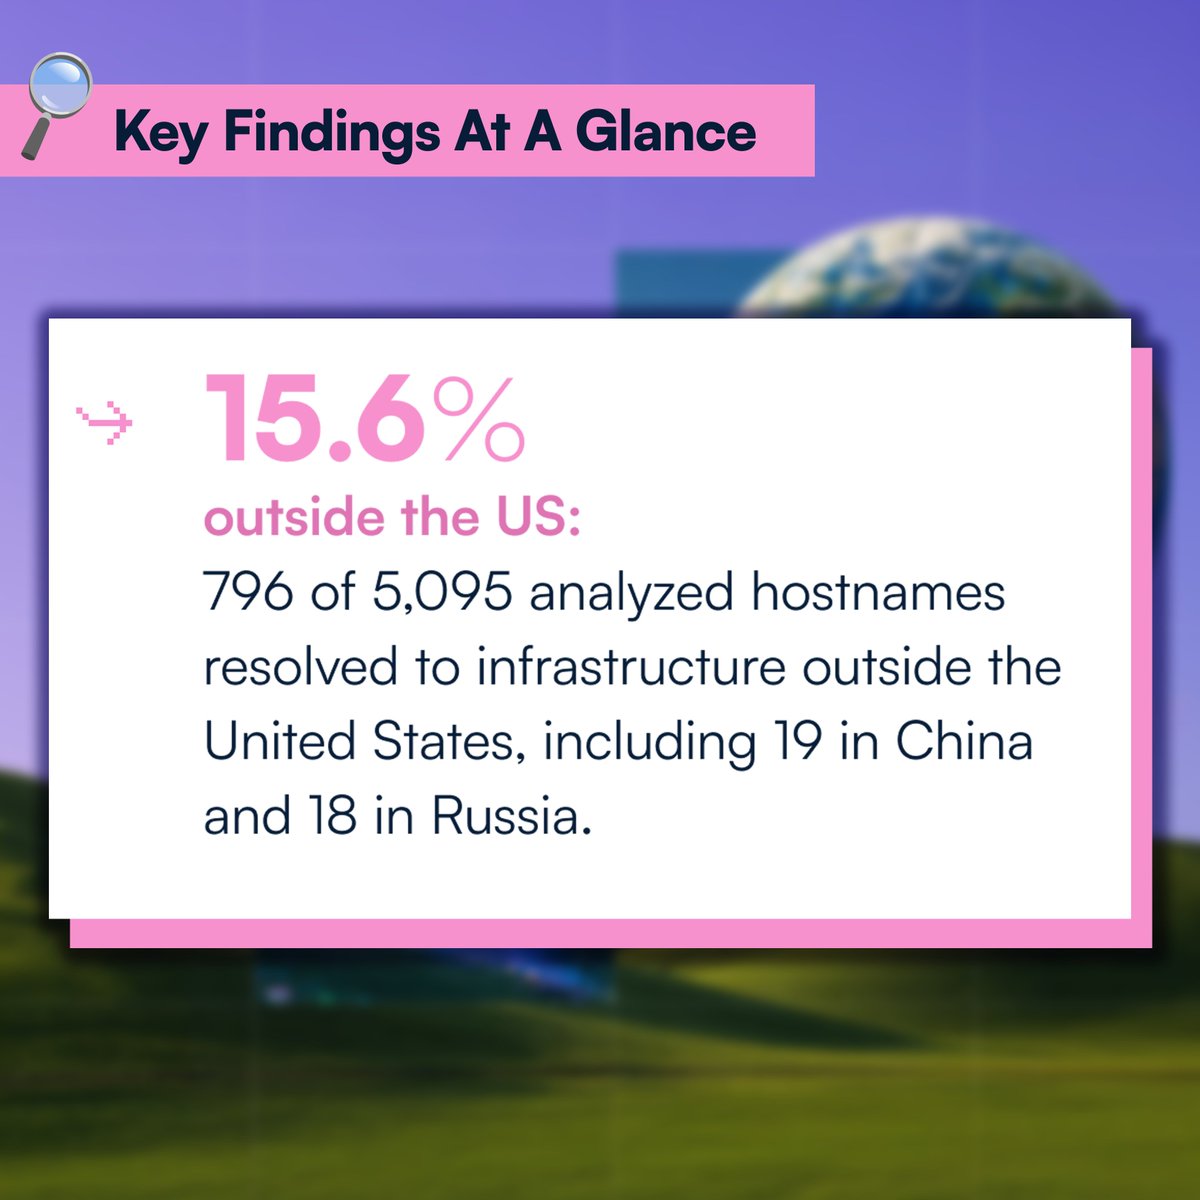
• 15.6% resolve outside the US
The risk is not MCP itself. It is trusting servers without verifying who runs them or where your data goes.
Read - https://t.co/WuOGrI6lUO
First stop on @MosheTov's fall tour: Toronto. 🎸
@BSidesTO — 10/03 at 1 PM ET
One IDE to Rule Them All — Securing Your Supply Chain’s Weakest Link
More info: https://t.co/V17UiJpFgJ
The cloud threat model is changing. So should the tools defending it.
🔗 Register:
https://t.co/YYxfV85mv0
AI workloads and autonomous agents are introducing a new class of risk into cloud environments — one traditional posture management wasn’t designed to handle.
Join @JamesBerthoty (Founder & CEO of @latiotech) and Chris Lindsey (Field CTO at OX), for a live discussion on agentic risk, detection, governance, reachability-based prioritization, and what security teams should be doing now.
📅 Oct 13
⏰ 12 PM ET | 9 AM PT | 6 PM CET
🎯 The AI Attack Surface Is Already in Your Cloud
#CloudSecurity #AI #Cybersecurity
🚨 15,465 MCP servers. The deeper we looked, the stranger it got.
📊 Full report → https://t.co/wVtyjDnWeb
OX analyzed 5,095 unique hostnames associated with published MCP servers.
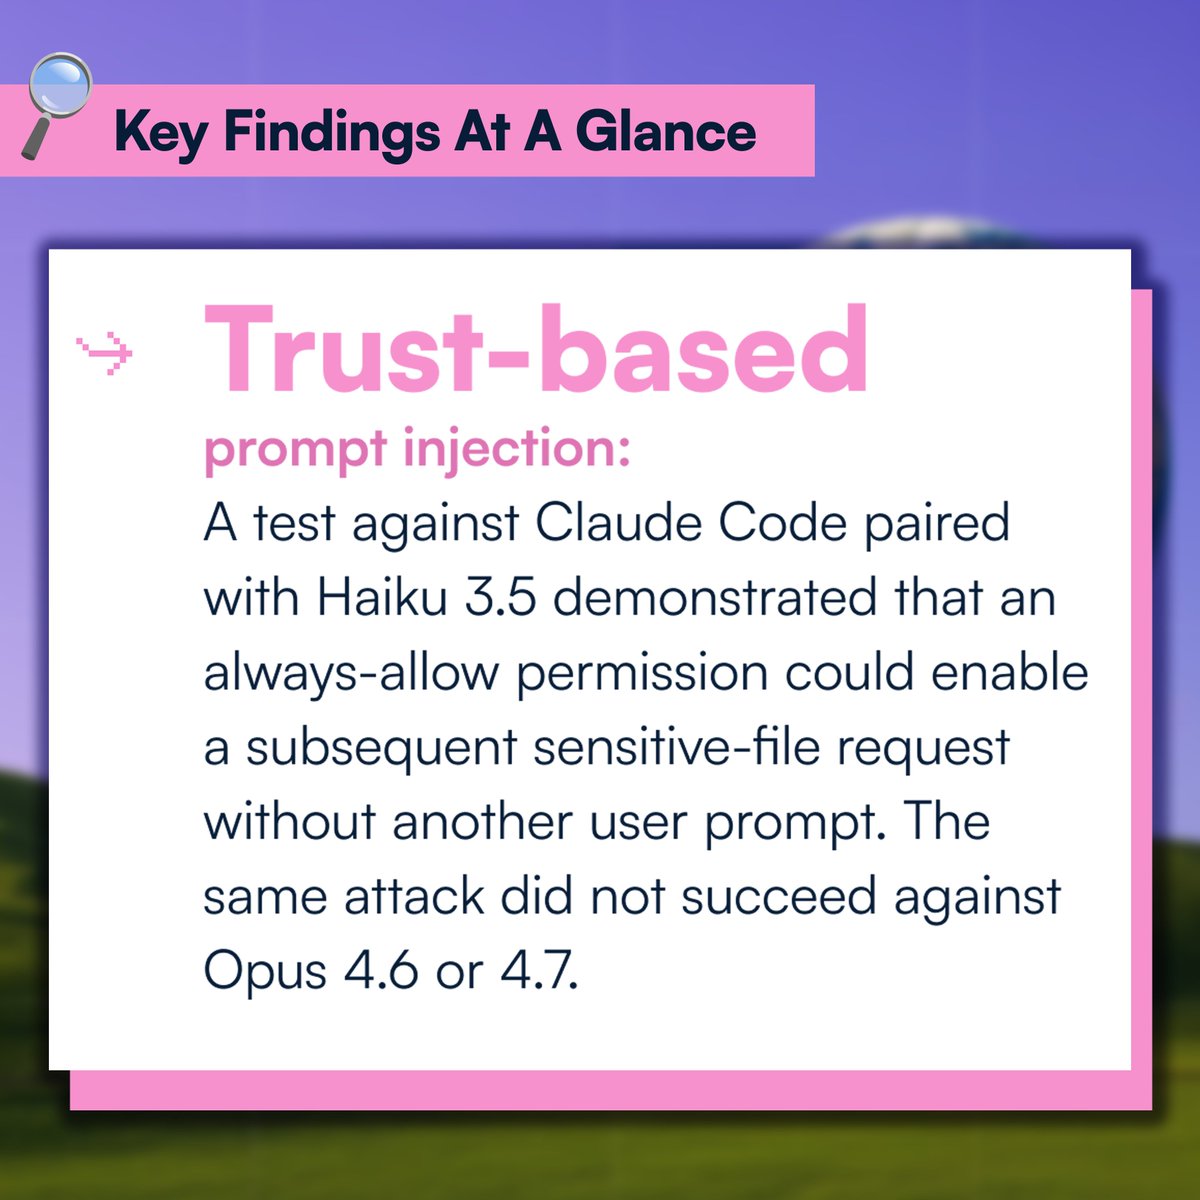
The findings span infrastructure outside the U.S., dead domains, home networks, and trust-based prompt injection risk.
The bigger issue: MCP infrastructure is moving faster than the governance built to control it.
#MCP #AISecurity #CloudSecurity
What would you do if your enterprise data was reaching a private home network in China? Or a server in Russia?
Read our full report → https://t.co/wVtyjDnWeb
New OX Security research shows how agentic workflows can bypass cloud security governance built for a very different era.
15,465 MCP servers. 0 governance.
#CloudSecurity #MCP #AISecurity
Security research, but make it a world tour. 🎸💻
OX Research Team Lead @MosheTov is hitting the road for a run of speaking engagements this fall:
10/03 @BSidesTO — Toronto, Canada
10/14 @InfoSec_World — Orlando, FL
11/04 @RBLN26 — San Francisco, CA
11/05 @Owasp — San Francisco, CA
More details on each stop coming in the weeks ahead🤘
We’re building security for today’s AI agents.
That may already be the wrong target.
Read @neatsun's latest on Agentic Darwinism → https://t.co/kJ1zxLS6Mm
Agents are gaining more autonomy, more context, greater reach, and more authority to act.
What exists today is just one stage in that evolution.
#AgenticAI #AISecurity #AgenticDarwinism
Your cloud isn’t just running infrastructure anymore. It’s running agents. 🤖☁️
See what’s new with OX Cloud → https://t.co/DKFakp7Y4W
Posture management + live AI detection + deep runtime inspection + reachability to show what’s running, what it’s doing, and what actually matters.
The runtime pillar of OX AINAPP. From prompt to runtime.
#CloudSecurity #AINAPP #AISecurity