Attackers don't need to break everything. Sometimes, they just need to know where to look.
Active Directory can become an attacker's playground if you don't know where its weaknesses are. Understanding those weaknesses is the first step toward building a stronger defense.
That's why I'm excited to share our upcoming Advanced Active Directory Attacks and Mitigations (AADA) training.
Over five intensive days, you'll dive into advanced attack techniques, explore defensive strategies, investigate suspicious activity, and learn how to monitor and secure Active Directory environments.
The training will be delivered by @Amr_Thabet and Artur Kalinowski, combining deep technical expertise with practical exercises in CQURE's custom labs.
November 16-20
If Active Directory is part of your security responsibilities, this is one training worth having on your radar.
Explore AADA and reserve your spot: https://t.co/86X9kEpcgq
#ActiveDirectory #Cybersecurity #WindowsSecurity @CQUREAcademy
We are going live in just a few hours.
Everyone talks about passkeys replacing passwords and eliminating phishing risks. Public key cryptography makes them incredibly strong, but there is an uncomfortable reality many teams overlook: when server side validation logic is flawed, passkeys can still be bypassed, leaving accounts vulnerable to full takeover.
Tonight, Artur Kalinowski and I are hosting a completely free live technical masterclass with @CQUREAcademy:
"Hacking Passkeys: How They Work, How They Fail, How to Secure Them"
🗓️ When: Today, Wednesday, November 11
⏰ Time: 7 PM CET | 1 PM ET | 10 AM PT
🦝 Dissecting WebAuthn registration and authentication ceremonies
🦝 Live testing using JavaScript monkey patching and browser API mocking
🦝 Exploiting server validation flaws beyond traditional Burp Suite proxy interception
🦝 Actionable rules for developers and defenders to enforce airtight native controls
Whether you are breaking authentication systems as a pentester or building them from scratch, this session will show you where the real risks hide.
🦝 Grab your free seat before we start tonight: https://t.co/L7uPdRU78O
#Cybersecurity #Passkeys #WebAuthn #AppSec #InfoSec #CQUREAcademy @msftsecurity@MSCloud@Microsoft@MicrosoftLearn
@CyberSec24com2 Exactly! 👏 Passkeys raise the bar a lot, but attackers just move to the next weak spot. Sessions and account recovery need just as much attention.
Passkeys are supposed to make authentication more secure. But does that mean they can't be hacked?
Not so fast.
There's a lot more to passkey security than simply getting rid of passwords. And if you want to understand what happens when things don't go according to plan, that's exactly what we'll be looking at this Wednesday.
I'll be joining Artur Kalinowski for a session on how passkeys work, where their weaknesses lie and what attackers can do when implementations get things wrong.
Two days to go. Hope to see you there!
November 11
Register here: https://t.co/DvQQGzs4TT
#Passkeys #IdentitySecurity #Cybersecurity #MicrosoftSecurity @CQUREAcademy
Amadeus has been breached! See which airlines!
I have over 200 flights each year (my record year 248, record month: 29). When I think about the impact - even on my personal schedule, this is just crazy…
Amadeus confirmed that a vulnerability in its booking-display system exposed reservation data. Its public statement does not list individual airlines, so the carrier-specific sources matter.
What concerns me the most about the Amadeus breach is how convincing a fake rebooking message could look between flights. My name, my next connection, my booking reference. All details you would expect the airline to know.
Yesterday, November 9, Finnair said the exposed flight lists included about 116,000 of its reservations. Around 750 individual bookings were opened for closer inspection. @feelfinnair issued new booking references for affected trips that were still active. Singapore Airlines had already reported on November 3 that about 46,000 of its booking records had been accessed.
As of today, November 10, 2026, these are the airlines I could verify had publicly reported the Amadeus incident or notified a regulator:
@Finnair@Fly_Norwegian@Condor@JAL_Official_jp@SolaseedAir_JP
StarFlyer
IBEX Airlines
Oriental Air Bridge
@SingaporeAir@cathaypacific@KoreanAir
Asiana Airlines
Malaysia Airlines
Thai Airways
@Qantas
Qantas also acknowledged the incident and said it was assessing whether its customers’ bookings were affected.
What it means to you and me?
Your connection has changed. Even if the flight number and booking reference match, open the airline app yourself and check your itinerary there.
Someone calls about a refund or rebooking fee. End the call and use the number in the airline app. Keep your card details and one-time codes to yourself.
You receive a breach notice before a trip. Contact the airline or your travel desk through a known channel. Ask which details were exposed and confirm which booking reference to use at check-in.
Source: https://t.co/s6XaROsjcg
Bonjour from Paris! We love the adjective GLOBAL. This time global was with @BNPParibas!
I had the honor of joining BNP Paribas at Cyber & Tech Risk Days 2026 at their campus in Louveciennes. It was an internal event, and being invited as one of the external guests is a kind of trust you never take for granted.
I delivered my session “World Cyber Threat Adventures” and ran a hands-on Red Teaming Workshop. The audience was amazing, and I enjoyed every minute.
A huge thank you to Nitish Kumar and YUE Ying for the invitation and for making it all happen, and to Frank Roncey, Chief Risk Officer at BNP Paribas, and Jayaraj Puthanveedu, Global Head of RISK ORM Cyber, Technology Risk, Fraud and Resilience, for welcoming us. It was a pleasure to be part of it!
Such a pleasure to grow together! Merci beaucoup, and see you at the next stop!
@BNPPARIBASOPEN@BNPPAM_COM@BNPPRE_UK@bnpp_recrut@BNPPAM_IT@BNPParibasCIB@BNPPAM_FR@BNPPAM_ID@CQUREAcademy #Cybersecurity #CyberRisk #RedTeaming #CQURE
Eighteen years in enterprise cybersecurity represents an entire technological era.
When our journey started, the threat landscape looked completely different. Through every shift, our guiding principle remained absolute: zero shortcuts, deep systems engineering, and actionable capabilities straight from our @CQUREAcademy Team
CQURE is officially turning eighteen, and stepping into adulthood happens only once in a lifetime!
To celebrate this milestone, we are keeping the momentum going until the end of the year (December 31) with special anniversary voucher -18% for all our @CQURE Academy courses:
🎟️ Your anniversary voucher code: CELEBRATE18
Technology changes rapidly, but the true core of this journey has always been our community. Across eighteen years, we have had the privilege to train, mentor, and collaborate with thousands of senior engineers, architects, red teamers, and CISOs worldwide.
👉 Apply your anniversary code and explore upcoming programs: www.https://t.co/aEfR2SPhN0
#Cybersecurity #CQURE #CQUREAcademy #WindowsSecurity
@MSCloud@Azure@Microsoft@msftsecurity
Great cybersecurity skills aren't built alone.
Want to learn something real and practical, and stay ahead of the game?
Hands-on training, real-world scenarios and knowledge you can use right away, shared by experts who are on the front lines of cybersecurity.
Follow CQURE on:
Instagram ➡️ https://t.co/WhFvokfDCA
Facebook ➡️ https://t.co/LoMpWpQRs6
X ➡️ https://t.co/zlNZjESyM1
YouTube ➡️ https://t.co/xKiycNdewG
Stay in the loop with a community of people who never stop learning.
Ready to join the team? Start with one of our most popular courses:
1. https://t.co/FLyRClvMJ4
2. https://t.co/86X9kEpcgq
Check out our next webinar:
https://t.co/DvQQGzs4TT
Learn with the right team. Stay CQURE! 🦝
#CQURE #CQUREAcademy #Cybersecurity #CyberSec #CybersecurityCommunity #Upskilling @CQUREAcademy
Day two at #WarsawFinanceWeek, done! 🙌
Yesterday I was on stage twice: first with “Cyber Threats in the AI Era: Visibility and Response at Scale”, and then with “Tales from the Crypt: Incident Response and the Cost of Getting It Wrong” (a little spooky, but very real 😉). Two great sessions and so much energy in the room. 😊
A special shout-out to our partners from Keepit. It was a real pleasure to listen to their talk! 👏 And with so many other interesting sessions, there was a lot to learn throughout the day.
Thank you to the organizers and to everyone who joined and stopped by to say hi! 👏
See you at the next stop! ✈️
@PKOBP@Mastercard@BGK_pl@dudkowiakputyra@okx@PwC@Equinix@Kontomatik@Paymentology@Revolut@Vonage@AWICglobal@bankier_pl https://t.co/U6L6fam4PF @puls_biznesu@CQUREAcademy
We've reached the grand finale of our 15 Days of Practical Security Skills series.
🦝 Skill #15/15: Modern Active Directory Tiering: Securing Privileged Access with PAWs.
Attackers don't need Domain Admin from day one. They need a path.
Modern Active Directory attacks often succeed because privileged accounts, administrative workstations, and identity boundaries are not properly separated. Once attackers gain access to a single privileged credential, they can move through the environment far faster than most organizations expect.
Developing this skill means understanding:
✅ Privileged Access Workstations (PAWs)
✅ Administrative tiering and identity separation
✅ Credential theft prevention
✅ Privileged account protection
✅ Modern Active Directory attack paths
✅ Reducing opportunities for lateral movement
If there's one skill that consistently helps organizations reduce the risk of domain compromise, it's learning how to properly secure privileged access.
That's exactly why we've built Hacking and Securing Windows Infrastructure, led by @Amr_Thabet and me.
Want to learn how attackers move through Windows and Active Directory environments and how to stop them? 🔗 https://t.co/FLyRClvMJ4
Looking for an even deeper dive into modern Active Directory attacks and advanced privilege escalation techniques?
Join Peter Kloep in Advanced Active Directory Attacks 🔗 https://t.co/CpTLsv1Jhz
Thank you for following our 15 Days of Practical Security Skills series. We hope it helped highlight some of the most important skills modern cybersecurity professionals should be developing today!
#CyberOctober #ActiveDirectory #PAW #IdentitySecurity #WindowsSecurity #MicrosoftSecurity #CyberSecurity #CQUREAcademy #CQURE
@MSCloud@Azure@Microsoft@msftsecurity@CQUREAcademy
Using passkeys or thinking of implementing them? Learn how to hack them (and secure them). 🔐🦝
Artur Kalinowski eats passkeys for breakfast. That's what it is.
Join our free live masterclass hosted by CQURE Academy:
🎯 Hacking Passkeys: How They Work, How They Fail, How to Secure Them
🗓️ Date: Wednesday, November 11, 2026
⏰ Time: 7 PM CET | 1 PM ET | 10 AM PT
🎙️ Speakers: Artur Kalinowski and Paula Januszkiewicz🦝
Key takeaways:
🦝 WebAuthn registration and authentication ceremonies dissected
🦝 Live exploit demonstrations of server validation flaws
🦝 Hardening guidelines to enforce resilient native controls
👉 Claim your free seat here: https://t.co/L7uPdRU78O
📢 Share this with or tag anyone dealing with identity protection
#Cybersecurity #CQUREAcademy #Passkeys #WebAuthn #AppSec @CQUREAcademy@msftsecresponse@Microsoft@msftsecurity@PortSwigger #stayCQURE
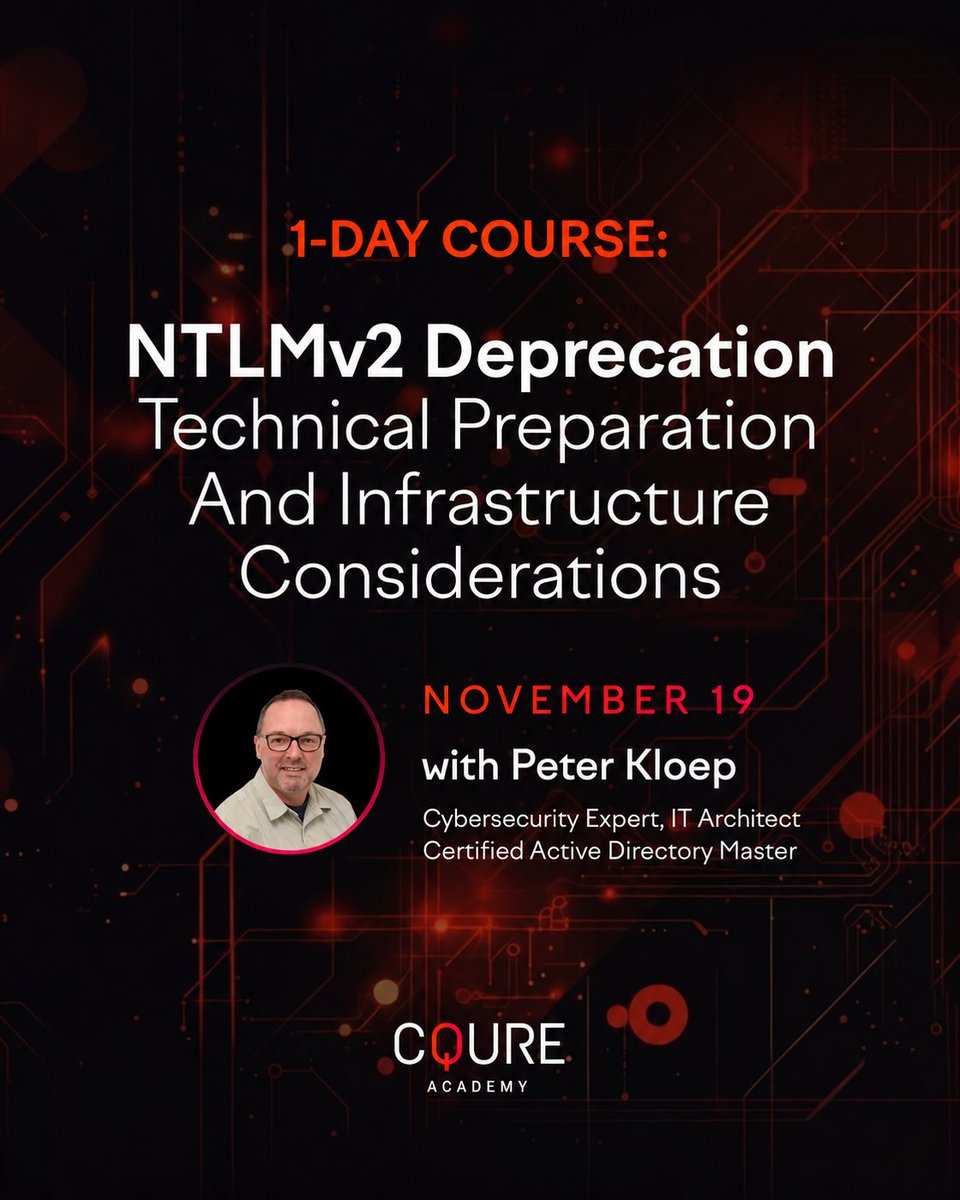
NTLMv2 is a good example of why security changes need more than a deadline and a configuration switch. Somewhere in your infrastructure, there may be a resource still relying on it. You won't necessarily find it in a settings page.
Audit first. Then plan the migration. Otherwise, you risk creating the very outage you're trying to avoid.
This is exactly the kind of challenge we want to tackle at CQURE Academy: real technical problems, approached with the depth they deserve.
I'm glad to have Peter Kloep leading our next CMAP module on NTLMv2 deprecation. It's an important topic, and Peter will get into the details that matter: Microsoft's roadmap, dependency discovery, migration to Kerberos, remediation and keeping services running throughout the transition.
If you work with enterprise infrastructure or authentication security, put this one on your calendar.
November 19
Join Peter and the CMAP community:
https://t.co/G5CgcpuOGS
#Cybersecurity #CMAP #Microsoftsecurity #CQURE @CQUREAcademy@Microsoft
#CQURE turns 18 today! 🦝 Est. 2nd of November 2008 🙌
I founded CQURE on my own on a rainy day 18 years ago. One ambitious lady, a lot to figure out and one thought in my head: go big or go home. The world was my city. And I was determined never to compromise on quality.
I have been building and leading CQURE ever since. Through difficult decisions, lessons learned, ambitious projects and plenty of reasons to keep thinking bigger.
Today, CQURE operates in four countries: Poland, the USA, the UAE and Switzerland. Just two weeks ago, we also launched our another US company, stay tuned 🔥 The plans keep getting bigger, too 😉
But what makes me proudest is the Team behind all of it. People who investigate, research, teach, challenge assumptions and keep pushing for better answers. People who care deeply about the work they deliver.
THIS is what the CQURE Team is about.
To our Team: thank you for your knowledge, commitment and care. I started this company alone, but everything we deliver today takes all of us. It is awesome to be surrounded by people who keep growing with us. Some joined recently. Others have been part of this journey for over ten years 😍 🙌!
To our Clients, Partners and Friends: thank you for trusting us with your security, your development and your time. That trust comes with responsibility. I never forget that. World-class delivery is what drives me!
Every minute someone spends with CQURE is an investment of their time. We have to make it count.
Happy 18th birthday, CQURE! I have a feeling our biggest adventure is still ahead of us.
3… 2… 1…! 🚀🦝 Cheeeeeeeers!
#CQURE #CQUREAcademy @CQUREAcademy
Learn something useful and lightweight today 🙌🦝 #CyberOctober
A certificate request leaves a trail. Practise following it before an attacker gives you homework 🦝
@Microsoft’s research published on 30 October 2026 documents two intrusions that progressed from help desk impersonation to AD CS abuse.
🦝 One useful learning exercise: connect a certificate request to the certificate actually issued.
Use an isolated Active Directory domain, an (enterprise) CA and a test account permitted to enrol through an approved template. You’ll need administrative access to configure CA auditing.
1. Enable Audit Certification Services and the CA’s request/issuance auditing.
2. Request one ordinary certificate for the test account through normal enrolment. No impersonation, vulnerable template or relay required are necessary 🥲
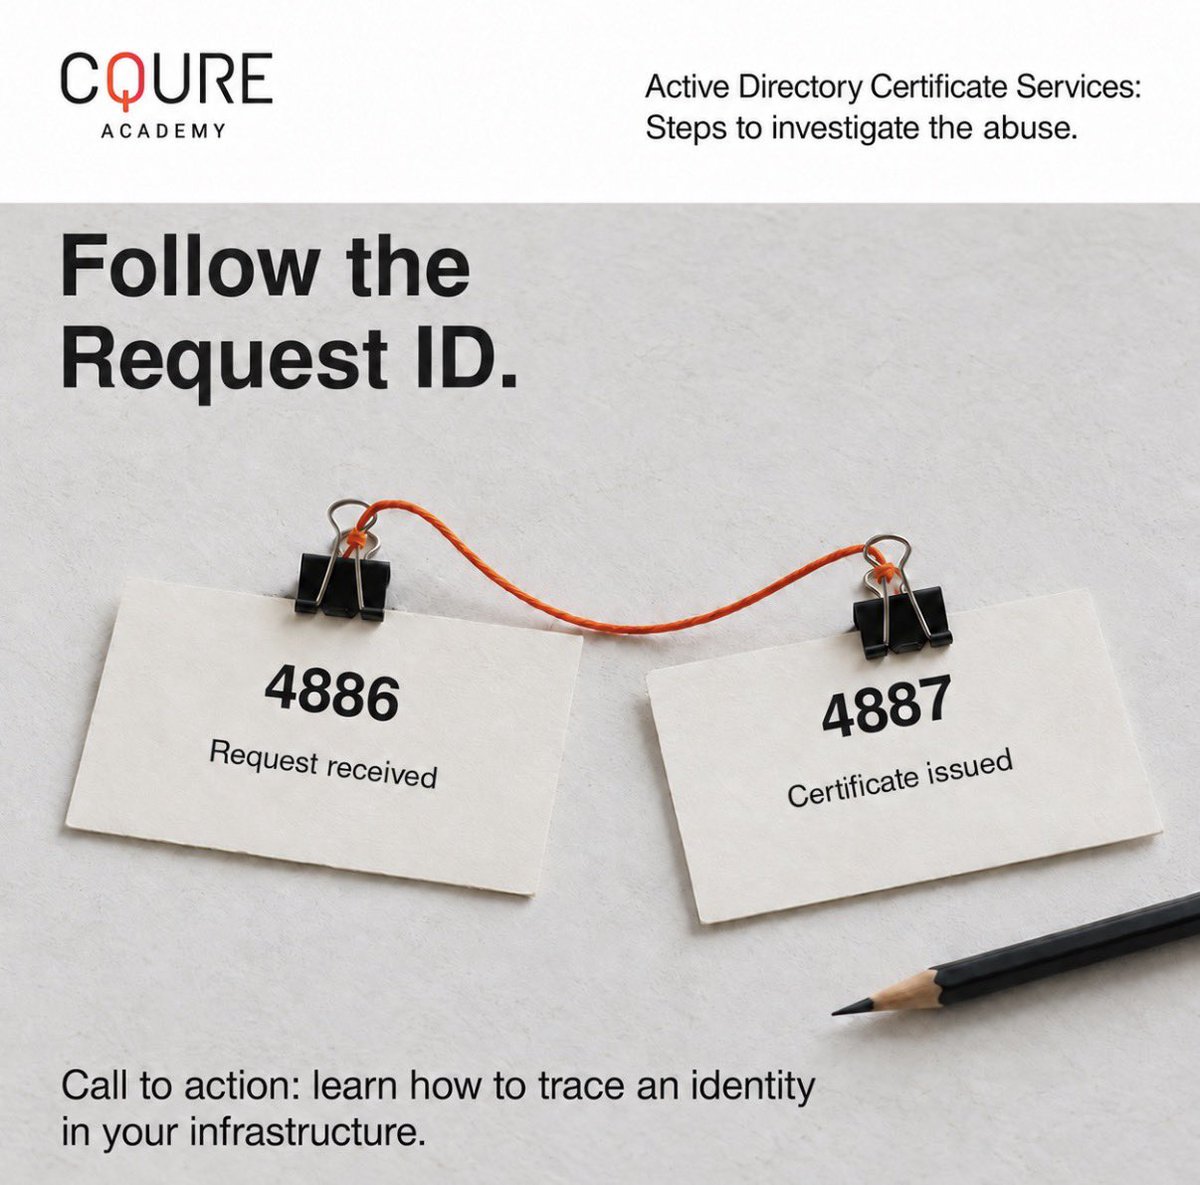
3. Find Security events 4886, request received, and 4887, certificate issued, on that CA. Correlate their Request ID and requester.
4. Follow that Request ID into the CA’s Issued Certificates view. Inspect the template, subject, subject alternative name where present, and serial number.
These events establish request and issuance activity correlation.
Follow @CQUREAcademy and #CQURE for more useful tips 🙌
Additional resources:
CQURE’s Threat Hunters Guide: https://t.co/JCaOr5ubhO
@MSFTResearch (30 October 2026): observed intrusions and investigation guidance: https://t.co/qFCJ6DiIW2
@MicrosoftLearn auditing configuration for ADCS: https://t.co/dEXkKTle5F
CC @msftsecurity
Missed our webinar? You can still catch up!
On October 21, I joined @samilaiho and Artur Kalinowski for “Secure Users: Designing Workstations for Threat Resistance.” We explored how to strengthen workstation security, from Privileged Access Workstations (PAWs) and passkey deployment to security monitoring.
It was a great session, with practical demonstrations and plenty of insights on designing workstations and verifying that security controls work as intended.
If you missed it live, the recording is still available. Just fill out the form to watch it:
https://t.co/kpnvr6k3VX
Want to take your cybersecurity skills further?
AMSC 2027 has already started, but late enrollment is still available! Learn directly from industry Experts and deepen your @Microsoft security expertise.
Use my personal code AMSC27PAULA to access exclusive AMSC 2027 pricing.
Learn more:
https://t.co/sUZp22KzZV
Prices are rising! 🔥 𝐃𝐨𝐧'𝐭 𝐦𝐢𝐬𝐬 𝐨𝐮𝐫 𝐬𝐩𝐞𝐜𝐢𝐚𝐥 𝐰𝐞𝐞𝐤𝐞𝐧𝐝 𝐜𝐨𝐝𝐞: 𝐂𝐘𝐁𝐄𝐑𝐖𝐄𝐄𝐊𝐄𝐍𝐃 and buy the course for lower price!
Upgrading cybersecurity capabilities across an entire engineering team requires a shared tactical foundation.
If you are planning advanced training for your security operations center, infrastructure admins, or red team specialists, we offer dedicated team seat packages for AMSC 2027.
💡 𝐂𝐚𝐧𝐧𝐨𝐭 𝐜𝐨𝐦𝐩𝐥𝐞𝐭𝐞 𝐲𝐨𝐮𝐫 𝐩𝐮𝐫𝐜𝐡𝐚𝐬𝐞 𝐭𝐨𝐝𝐚𝐲? Send us an email at [email protected] with the subject line AMSC. We will lock in today’s price and team discount rate, or we will issue you an invoice or direct payment link so your company can pay later next week.
Train four engineers for the price of three or request a customized bulk seat plan tailored to your organization.
Here is why enterprise leaders send their teams to this course:
🦝 Consistent Execution Standard: Your team learns unified threat hunting procedures, incident response frameworks, and identity boundary enforcement directly from frontline practitioners.
🦝 CQURE Training Lab: Real world simulation environments where your engineers test detection workflows and mitigate complex attack scenarios together.
🦝 CPE Credits & Certification: Every participant receives 24 CPE hours and earns the official CQURE Microsoft Security Master 2027 certification upon passing the final examination.
👉 𝐁𝐮𝐲 𝐭𝐞𝐚𝐦 𝐬𝐞𝐚𝐭𝐬 𝐚𝐧𝐝 𝐚𝐩𝐩𝐥𝐲 𝐜𝐨𝐝𝐞 𝐂𝐘𝐁𝐄𝐑𝐖𝐄𝐄𝐊𝐄𝐍𝐃 𝐡𝐞𝐫𝐞:
https://t.co/sUZp22KzZV
@CQUREAcademy@Azure@Azure@Microsoft
𝐃𝐢𝐬𝐜𝐨𝐮𝐧𝐭 𝐜𝐨𝐝𝐞 𝐞𝐱𝐩𝐢𝐫𝐞𝐬 𝐭𝐨𝐝𝐚𝐲 𝐚𝐧𝐝 𝐭𝐨𝐦𝐨𝐫𝐫𝐨𝐰 𝐩𝐫𝐢𝐜𝐞𝐬 𝐢𝐧𝐜𝐫𝐞𝐚𝐬𝐞!
If you are planning your advanced technical training for the coming year, here is your opportunity to CQURE a seat in our most advanced cybersecurity course at a special price!
Together with @samilaiho, me and the @CQUREAcademy Team, we deliver seven weeks of high intensity course built around attack vectors that will shape infrastructure security in 2027.
We have something special for our experts-followers: you can use my personal expert code at checkout to reduce your tuition by 150 EUR:
🎟️ 𝐏𝐚𝐮𝐥𝐚'𝐬 𝐜𝐨𝐝𝐞: 𝐀𝐌𝐒𝐂𝟐𝟕𝐏𝐀𝐔𝐋𝐀
👉 Apply for your seat and claim your 150 EUR discount here: https://t.co/gzEIxxNDXh
@Azure@Microsoft@MsftSecIntel
Thousands of file operations. One timeline. A lot more to investigate.
In CQURE Hacks #85, I walk through the CQUSNDeepAnalyzer tool and show how it can turn raw USN Journal data into a clear forensic timeline with many useful indicators that helps investigators quickly identify suspicious activity.
Watch the demo and see what the USN Journal can reveal: https://t.co/P3huqhyLfL
#CQUREHacks #DigitalForensics #DFIR @CQUREAcademy
The next battle for AI may not be fought in a lab. It may be fought in your inbox.
Artificial intelligence is becoming a geopolitical battleground. But understanding how the West will regulate and secure AI is just as valuable as understanding the technology itself.
According to a recent @proofpoint report, a China-aligned threat group known as TA419 has been targeting U.S. AI policy experts, researchers, and legal professionals through highly tailored impersonation campaigns.
The approach is particularly concerning because it starts with something completely ordinary: professional networking.
A convincing introduction. A familiar name. A relevant request. And eventually, a login prompt designed to look legitimate while credentials and session cookies are stolen.
This is a reminder that sophisticated cyber espionage doesn't always begin with malware or an obvious vulnerability. Sometimes, it begins with trust.
For security professionals, the challenge is to look beyond what appears on the screen and understand what is happening underneath.
I recommend reading the full analysis from Proofpoint. It’s a fascinating look at how targeted phishing, identity compromise, and geopolitical intelligence intersect.
Read the article:
https://t.co/n6IdfLGRhn
P.S. Keep reading until the very end. I’ve got a little something for those who want to take their @Microsoft security expertise further.