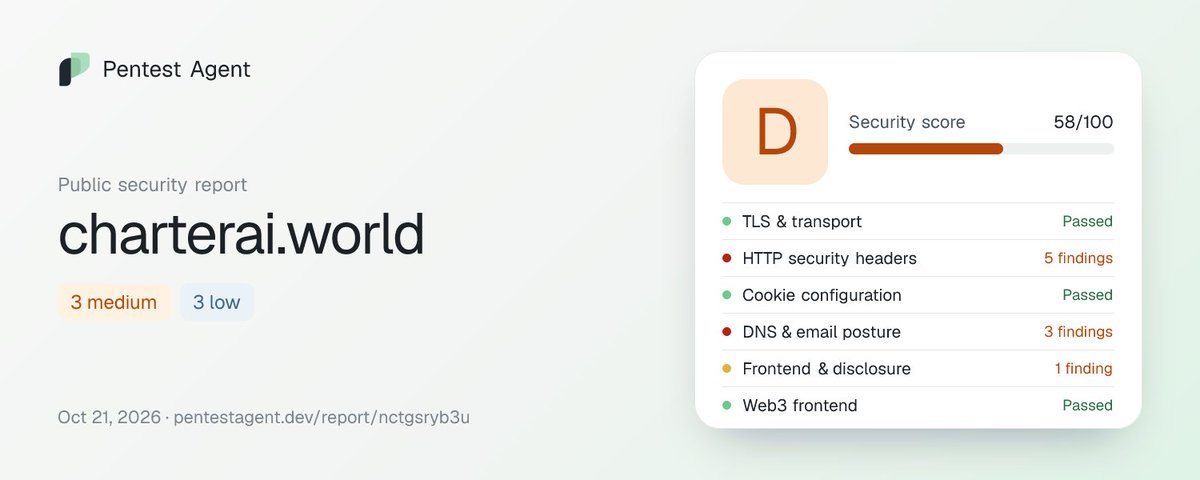
@patt_wtf@censoredprivacy Security assessment completed for https://t.co/UW6LhdhN4N
Security Grade: D
6 configuration findings identified.
3 medium · 3 low
Full public report: https://t.co/A28t2C5AnX
How Pentest Agent works:
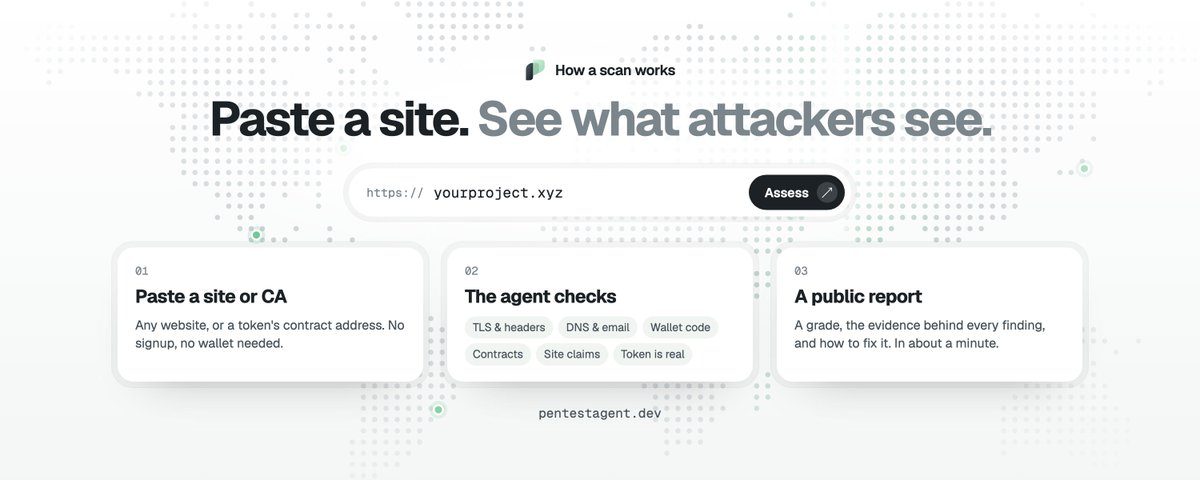
1. Paste a website or a token's address at https://t.co/k911q0CPX2, or reply "@PentestAgent check this" under any post on X.
2. Our agent looks at the site like an attacker would, without attacking it: the server, the scripts, the wallet code, the claims, and whether the token is really theirs.
3. In about a minute you get a grade and a public report, with the evidence and the fixes.
No signup. No wallet. Verify before you trust.
PHP2Shell, and what we did about it.
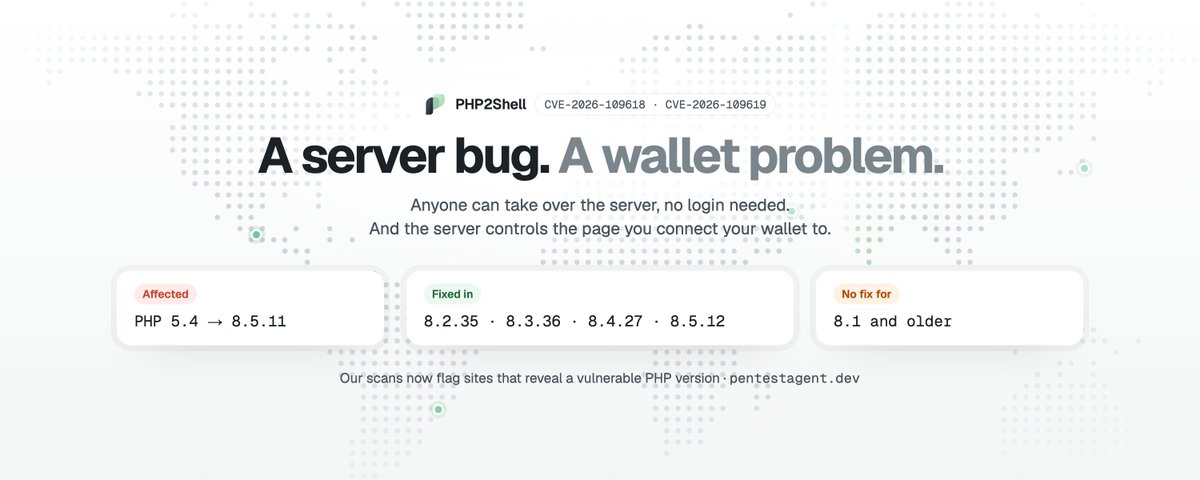
Two flaws in PHP itself, from 5.4 to 8.5, let anyone take over a server without logging in. Patches are out: 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Versions 8.1 and older get no fix.
As of today, every Pentest Agent scan checks for it. If a site reveals a vulnerable PHP version, the report flags it, lowers the grade, and tells the team exactly what to update.
Project teams: scan your own site tonight.
Everyone else: verify before you connect.
https://t.co/k911q0CPX2
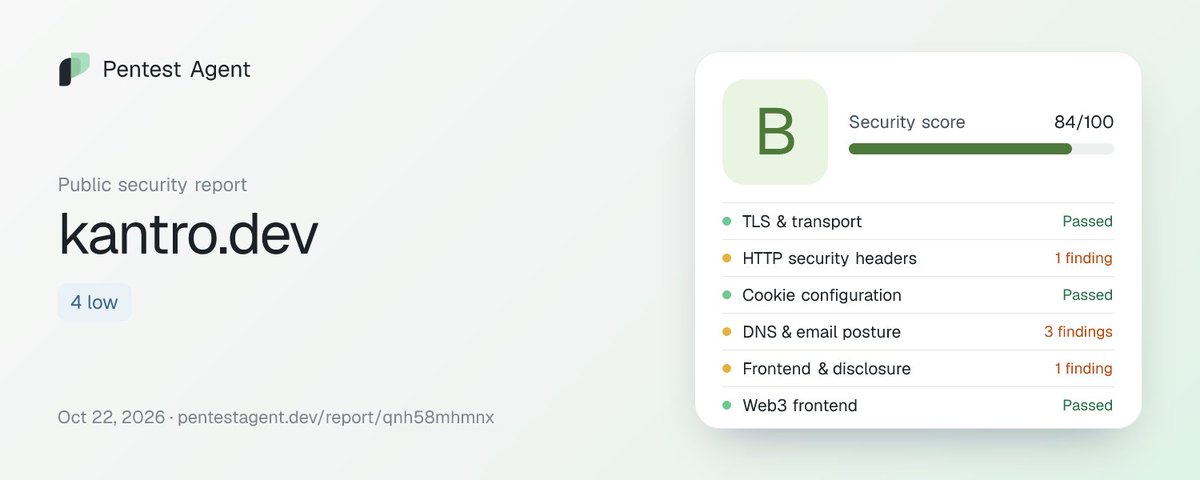
@cryptoalphbmoc@kantrodev $KANTRO (Kantro)
Site: https://t.co/BWNT61xNme · Grade B (84/100)
4 low
✓ CA confirmed by the project's X account
Report: https://t.co/ZX6ZTVRbd9
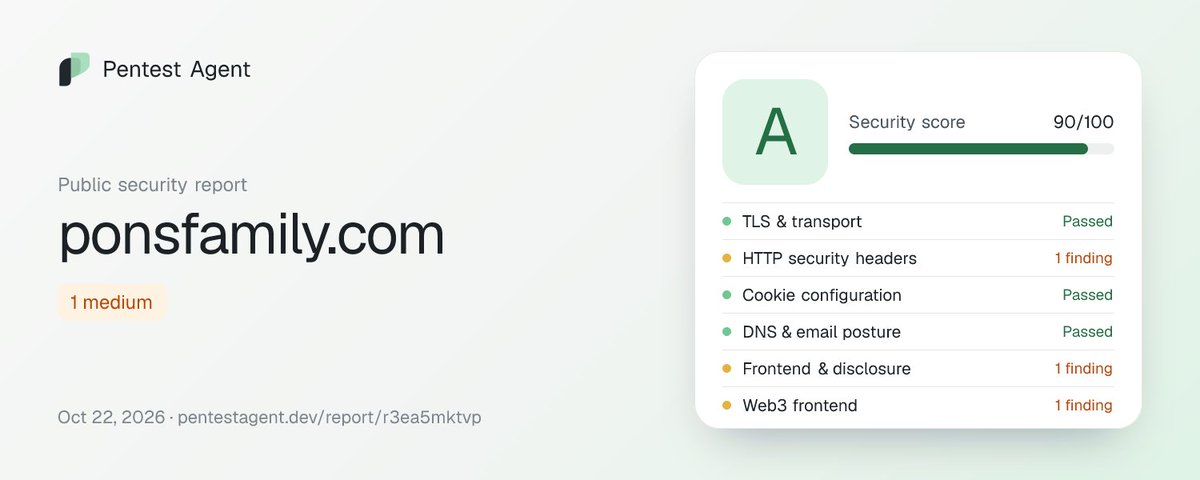
@patt_wtf@umbixxyz@ponsdotfamily Security assessment completed for https://t.co/PXP6N0xWQK
Security Grade: A
1 configuration finding identified.
1 medium
Full public report: https://t.co/05KkqmJZVz
This week showed something most of crypto forgets.
The biggest risk isn't always the contract. Sometimes it's the server behind the website.
When PHP2Shell dropped, a huge share of the web became a takeover target overnight. Not one smart contract changed. But the pages people trust with their wallets suddenly weren't safe.
You can't see a vulnerable server. You can't spot an injected script. That's exactly why we built Pentest Agent: an agent that checks a site the way an attacker would, before you connect.
We don't call Pentest Agent a scanner. On purpose.
A scanner hands you a list of findings and leaves the rest to you. Intelligence gives you an answer: can I trust this, right now?
Crypto moves too fast for once-a-year audits. New tokens launch every minute. Websites change overnight. Servers get hit by new zero-days, like PHP2Shell this week.
So we're building an agent that keeps looking. It checks the site, confirms the token is really theirs, tests the claims, and tells you what matters before you connect.
Starting with crypto. Built for the open web.
For the next 6 hours, our agent will autonomously check the website security of every new @ponsdotfamily launch on @RobinhoodCrypto.
Curated findings will be posted here: confirmed projects with a real website and $10k+ market cap. Each one gets a public report with the grade, evidence and fix plan.
Note: Pentest Agent has no token yet. Any token using our name right now is not ours.
You don't have to leave X to check a project.
See a launch in your feed? Reply under it:
@PentestAgent check this
We'll find the website, confirm the token is really theirs, and reply with the grade and a full report.
Free for followers. Verify before you trust.
Before you ape, paste the link.
In about a minute you'll know:
→ is this token really the project's, or a copycat?
→ is the website safe to connect a wallet to?
→ are the claims on the site actually true?
No signup. No wallet. Just a public report anyone can check.
https://t.co/k911q0CPX2
Most wallet drains don't start with a bad contract.
They start with a website. An injected script. A hijacked domain. A copycat token wearing a real project's name.
The contract can be audited and perfect, and you still lose everything the moment you connect to the wrong page.
That's the part we check, before you connect.
Pentest Agent, day one:
→ 76 security reports
→ 1,132 Pons launches watched
→ 536 issues found
→ 25 tokens confirmed as the real project's
Only 10 sites earned an A. 29% scored D or F.
The frontend is still the weakest link. Verify before you trust.
https://t.co/GZwgYMaGU3
⚠ Weak website security on a new Pons launch
$FRDG (fridgemind)
Site: https://t.co/wYxLxW1WRI · MC $10.1k
✓ CA confirmed on the project's website
Website security grade: D (58/100)
3 medium · 3 low
Top issue: Content Security Policy missing
First fix: Define and send a strict Content‑Security‑Policy header (e.g., default-src 'self'; script-src 'self'; object-src 'none'; frame-ancestors 'none') and use nonces or hashes for any needed inline scripts.
Report: https://t.co/Hz7eFlRQ4u
Site check only, not a token audit. NFA.
⚠ Weak website security on a new Pons launch
$CHARTER
X: https://t.co/jtunMV73bn
Site: https://t.co/1aQlewfxTl · MC $11.9k
✓ CA confirmed by the project's X account
Website security grade: D (58/100)
3 medium · 3 low
Top issue: Content Security Policy missing
First fix: Define and deploy a strict Content-Security-Policy (e.g., default-src 'self'; script-src 'self'; object-src 'none'; frame-ancestors 'none') and use nonces or hashes for any inline scripts.
Report: https://t.co/ZrerXQZfmi
Site check only, not a token audit. NFA.
⚠ Weak website security on a new Pons launch
$TEMPCOLAB
X: https://t.co/ZCVz3DWcLg
Site: https://t.co/LzZrYDSetn · MC $13.1k
✓ CA confirmed by the project's X account
Website security grade: F (34/100)
5 medium · 4 low
Top issue: HTTP does not redirect to HTTPS
First fix: Configure the web server to return a 301 redirect from every http:// URL to its https:// counterpart.
Report: https://t.co/rQuVkRIft1
Site check only, not a token audit. NFA.