Every product has two faces.
The screens your users touch.
The APIs working quietly behind them.
Attackers test both. So does Pentrova: signed in like a real user, every endpoint mapped, every finding proven.
https://t.co/ZPCFjyn9dc #APISecurity
Most scanners stop at “maybe.”
Pentrova exploits the bug, confirms it on the live target, and hands you a proof-of-concept you can replay. If it doesn’t reproduce, it doesn’t ship.
Proof, not probabilities. Start free → https://t.co/ZPCFjyn9dc
#AppSec#PenTesting
Your scanner guesses. Pentrova proves.
Autonomous AI pentesting: real exploits in a sealed sandbox, replayable proof for every finding.
Proof, not probabilities. 🧭
https://t.co/ZPCFjyn9dc
Less noise. More proof. 🛡️
Stop wasting time chasing false positives. Pentrova delivers AI-powered pentesting for web apps & APIs with replay-verified exploits.
Actual proof over probability. 👇
🌐 https://t.co/ZPCFjyn9dc
#Cybersecurity#Infosec#AI#Pentesting
Proof. Not Noise. 🚫 That's the Pentrova promise. Our AI-powered pen testing doesn't just scan; it provides replay-verified evidence for web apps & APIs. 🕵️♂️ Focus on what's real. https://t.co/ZPCFjyn9dc #Security#PenTesting#Pentrova
Define scope. Test the web app or API. Verify the finding. Pentrova turns confirmed issues into replayable evidence your engineers can check in staging. Explore: https://t.co/sAA6zSSYY8 #AppSec
Legacy API scanners flood your triage board with 50+ false alerts per day, yet miss a single BOLA that leaks tenant data.
In a 80‑service Kubernetes mesh handling 30M OAuth2/OIDC calls daily, a mis‑matched JWT audience let tenant B read tenant A invoices.
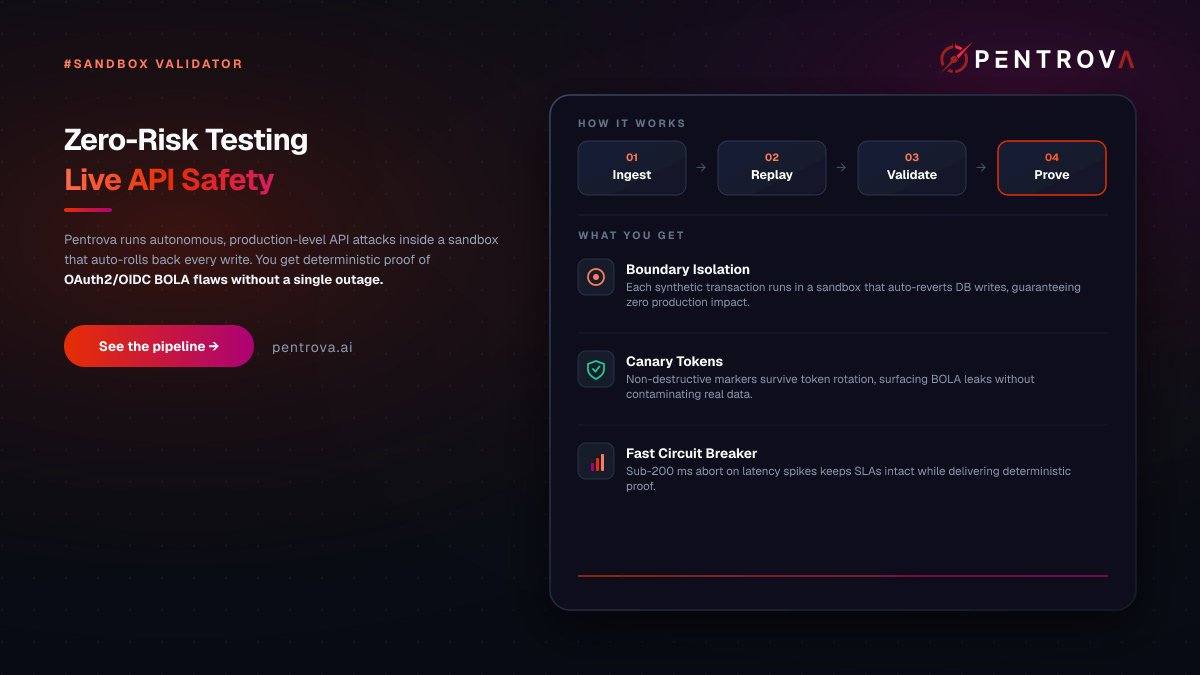
Pentrova’s SandboxValidator isolates each synthetic transaction, rolls back DB writes, and validates the full auth graph in <200 ms.
• Transaction boundary isolation – sandbox auto‑reverts writes, guaranteeing zero production impact.
• Non‑destructive canary strings – unique markers survive token rotation, exposing BOLA without altering real data.
• Sub‑200 ms circuit breaker – aborts instantly on latency spikes, preserving SLA while delivering deterministic proof.
Result: 0 % false positives, PR‑gated protection, and a $70 % TCO reduction versus quarterly consultant reports. Ready to replace stale PDFs with continuous, autonomous VAPT? Explore the pipeline at https://t.co/O4w91fE4Fo
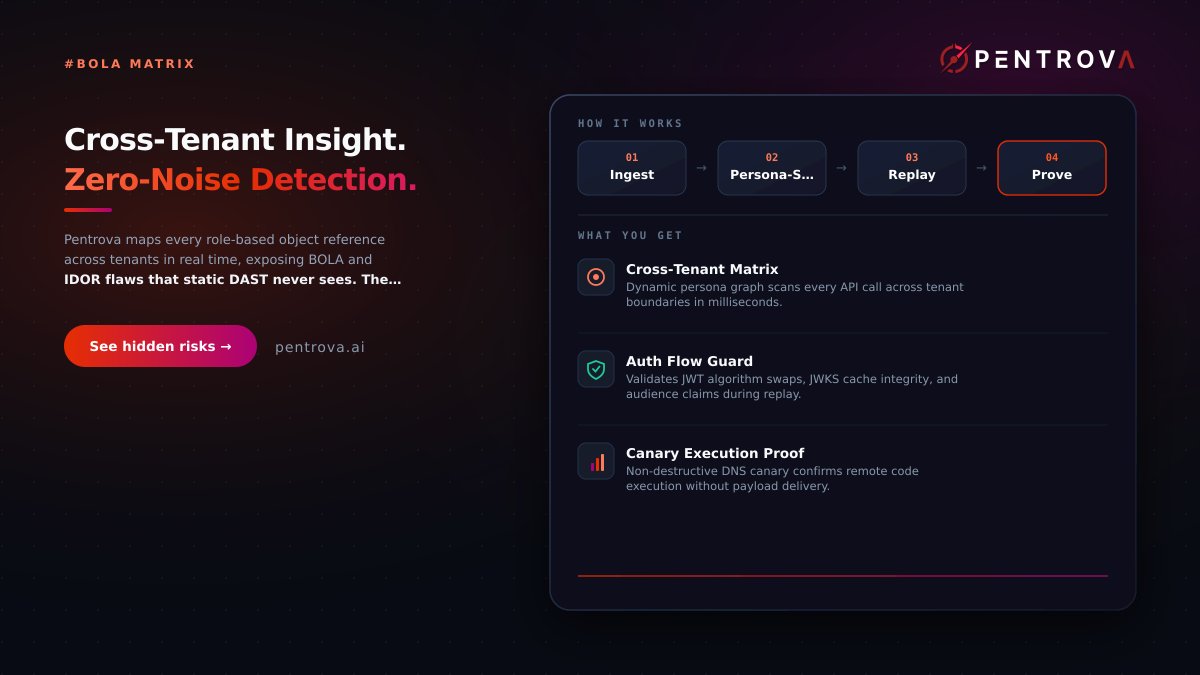
Cross‑Tenant Insight. Zero‑Noise Detection.
Legacy API scanners flood your triage with false alerts while silently missing cross‑tenant BOLA flaws.
At a fintech handling 40 M OAuth2 requests daily, a mis‑configured JWT audience let a single tenant read another’s cash‑out endpoint.
Traditional DAST never flips personas, so the breach stayed invisible.
Pentrova’s Multi‑Tenant Authorization Matrix injects a synthetic persona for each role, replays the exact OAuth2 flow, and validates every object reference.
It captures the illegal access, drops a DNS canary token into the Redis session payload, and receives a callback—proof of remote execution without any production impact.
• Persona‑switch engine maps 1,200 role‑object pairs per second.
• Sub‑200 ms kill switch aborts unsafe replays, keeping APIs live.
• Deterministic cURL PoC is generated for PR gating, eliminating noise.
CISO takeaway: Replace a $45k point‑in‑time audit that becomes obsolete in hours with continuous, autonomous VAPT that prevents the average $4.8 M API breach. Learn how Pentrova secures your OAuth2 mesh today. https://t.co/trDgcI9CK0
https://t.co/GeWRIJieci
@ThorCommerce Spot on. That's the exact trap: teams conflate cryptographic validity (HMAC signature passing) with tenant authorization. If downstream handlers trust the event without re-verifying object ownership, BOLA happens silently. That’s why automated replay testing is essential.
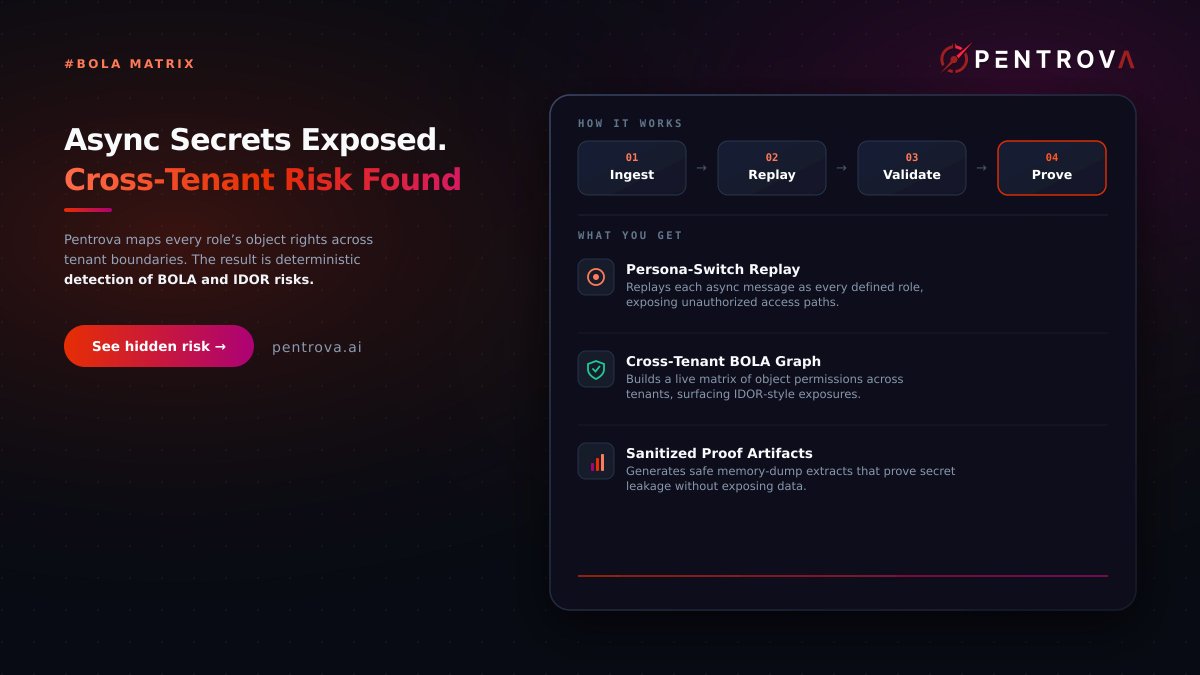
Async Secrets Exposed. Cross‑Tenant Risk Found
Legacy DAST tools never see what happens after your API returns a 200.
They only scan the synchronous response, missing the async payloads that travel through Kafka, RabbitMQ, or signed webhooks.
That blind spot hides cross‑tenant BOLA flaws—exposing secrets like heapdump endpoints that leak production credentials.
Pentrova’s Multi‑Tenant Authorization Matrix turns each persona into a live query, tracking object references across tenant boundaries, even in event‑driven flows.
- Dynamic persona‑switching engine replays each webhook/message as every role, mapping real‑world access rights.
- Cross‑tenant object graph builds a BOLA matrix, automatically flagging IDOR‑style exposures.
- Non‑destructive canary token injects into replayed payloads, producing a sanitized memory‑dump proof that confirms exposed connection strings.
CISO takeaway: Stop relying on static scans; get deterministic visibility into async authorization risks before a breach.
Explore how Pentrova maps hidden BOLA gaps at https://t.co/0uOiJOOIoW
#AppSec #DevSecOps
https://t.co/gNl9MzHUgt
Chain the Gaps. See Real Blast.
Legacy DAST tools see a single low‑severity finding and call it a day.
They never reveal that three of those findings can be stitched into a full admin takeover in a federated GraphQL mesh.
Traditional scanners crawl each REST endpoint, treat GraphQL resolvers as black boxes, and lack state‑aware correlation. They miss nested query batch authorization flaws and cannot model how a mass‑assignment PATCH escalates privileges.
Pentrova’s Multi‑Hop Attack Chaining Engine builds a graph of every discovered low‑severity vector—redirects, SSRF, credential exfiltration—then automatically synthesizes a multi‑step exploit across the federation. A deterministic differential replay in an isolated sandbox proves the chain without false positives.
- Graph‑based exploit synthesis links 3+ low‑severity findings into a verified admin‑privilege path.
- Differential replay reproduces the chain in <200 ms, delivering a reproducible cURL PoC.
- Zero‑FP blast‑radius report shows exactly which PATCH payload (role: admin, is_verified: true) grants admin rights.
Result: Heads of AppSec stop sifting through noisy alerts and get a single, actionable proof of business impact. Visit https://t.co/MOOGQsrn8O to see the chain in action.
#AppSec #DevSecOps
https://t.co/Fb8njdSU92
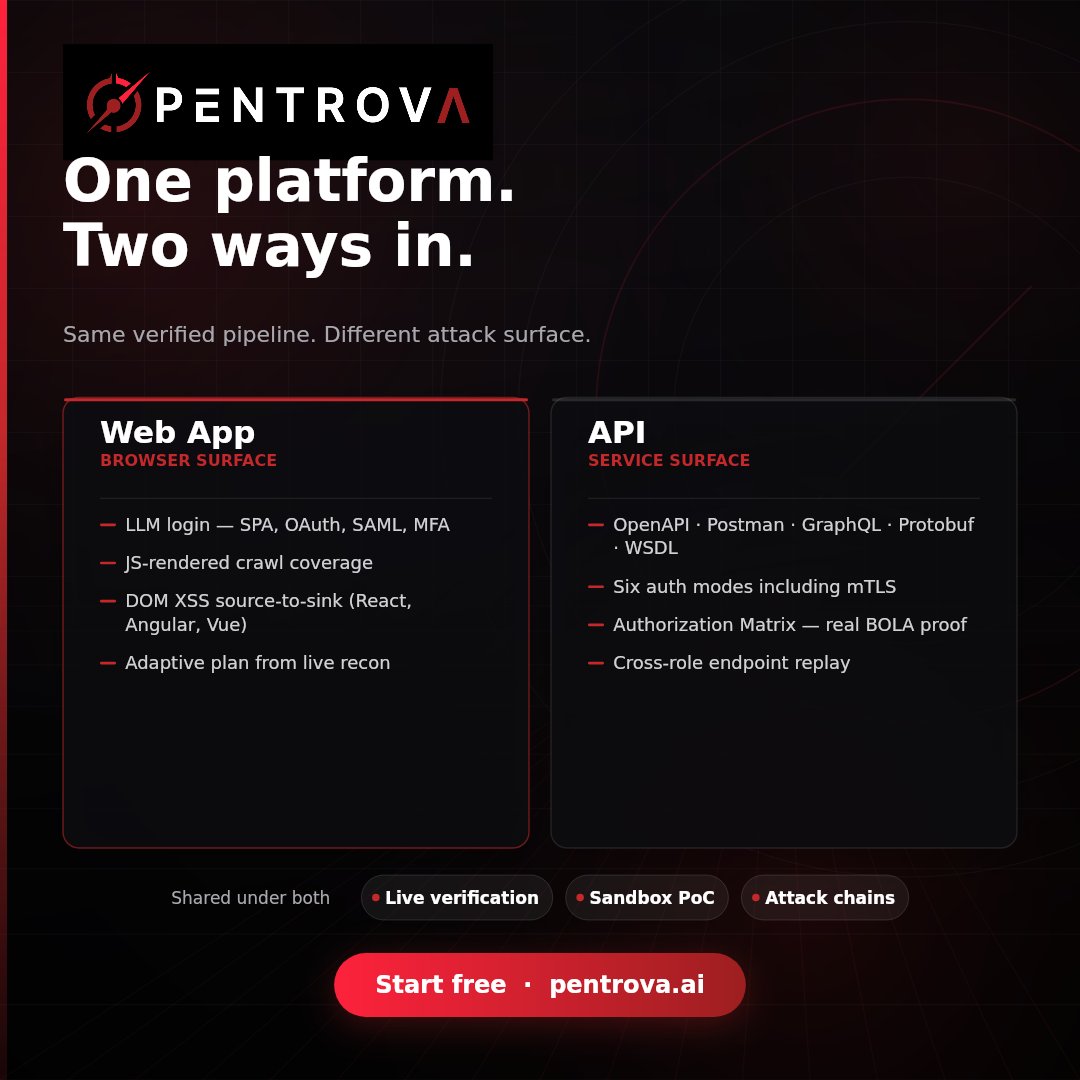
One platform. Two ways in.
Web App → browser surface (LLM login, DOM XSS)
API → service surface (specs, 6 auth modes, BOLA matrix)
Same verified pipeline under both. https://t.co/ZPCFjyn9dc
Proof, not probabilities.
We don’t flag vulnerabilities. We exploit them — then ship a PoC your engineers can replay in staging.
Start free → https://t.co/ZPCFjyn9dc
Shipping code daily but testing security quarterly? That’s not a strategy; that’s a critical vulnerability. 🚨
Meet Pentrova: Continuous, AI-driven offensive security that hunts and exploits at machine speed.
No more false positives. No more bloated PDFs. Just proof. 🛡️👇
#CyberSecurity #RedTeam #InfoSec
InfoSec is drowning in "AI" wrappers that just generate more false positives. We built the exact opposite.
Meet PENTROVA. 🎯
An AI-native autonomous penetration tester that actually validates exploits before it alerts you.
We don't do theoretical risks. We give you Proof, not probabilities.
Live today: https://t.co/eM7VP3I0cH
#CyberSecurity #VAPT #RedTeam #InfoSec