Google Mantis is a skills pack for security review with coding agents
Install:
npx skills add google/mantis
Key commands:
/mantis-threat-model: builds a threat model from your codebase
/mantis-researcher: scans for vulnerabilities
/mantis-review: filters false positives
/mantis-reproduce: writes a PoC and runs it in a sandbox
/mantis-patch: applies a fix and confirms it blocks the PoC
/mantis-report: generates the final security report
This is a good use case for running your agent in a sandbox, since the reproduce and patch steps execute generated code
https://t.co/OhmZDDNcWy
‼️ Next.js patched a critical ImageResponse flaw that can lead to server code execution.
"CVE-2026-94545" affects 16.2.0 through 16.3.5 on Node.js when attacker-controlled values reach generated SVG. The fix is 16.3.6.
Inside the bug: https://t.co/IGeKx2BVmC
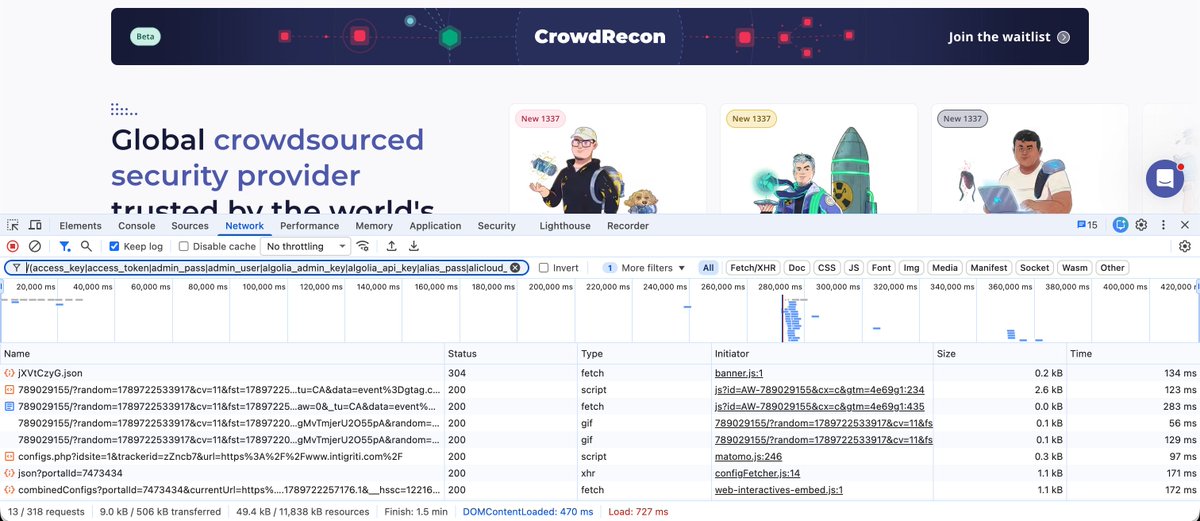
Manually searching through HTTP traffic for leaked credentials can be tedious... 😓
Leaked-Credentials by @h4x0r_dz gives you a ready-to-use regex that catches API keys, secrets, tokens, and database passwords across 100+ common patterns. It works directly in Chrome DevTools, Firefox and Burp Suite! 🤠
Check it out! 👇
https://t.co/9oiSV0TcBE
🚨Find Leaked Credentials Using Google Chrome dev Tools (The Best Way 😎)
✅https://t.co/uj4Rgh7RDd
✅https://t.co/maoBEGIWrM
#bugbountytips#bugbounty#infosec
Before you hit submit, let Claude Kit review your report like a triager 👀
Claude Kit checks for missing evidence, overclaimed impact and vulnerability-specific gotchas, then tells you whether your report is actually ready to go.
Give it a try 👇
https://t.co/5rygQKoU5i
🚨 GitLab CVSS 10 vulnerability exploited just one day after disclosure
Threat actors have begun exploiting CVE-2026-85706, a critical path traversal vulnerability affecting self-hosted GitLab Community and Enterprise Edition instances.
⠀
The flaw allows an unauthenticated attacker to read arbitrary files from a vulnerable GitLab server using a single HTTP request.
Affected versions include:
• GitLab 18.7 through versions before 19.1.8
• GitLab 19.2 through versions before 19.2.6
• GitLab 19.3 through versions before 19.3.2
⠀
GitLab disclosed and patched the vulnerability on September 10.
Just one day later, watchTowr began observing in-the-wild exploitation attempts and warns that mass exploitation is likely to follow.
⠀
Administrators should upgrade immediately to GitLab 19.1.8, 19.2.6, 19.3.2, or a newer supported release.
https://t.co/PSxIcWz0PX is already patched.
‼️ GitLab’s CVSS 10 file-read flaw (CVE-2026-85706) drew in-the-wild probes within hours of disclosure.
If an instance has at least one public project, unauthenticated attackers can read logs and config files containing credentials and secrets.
Read: https://t.co/RCRIp4oKL8
deepseek-v4.1-flash is insane! it found a 0day RCE in handlebars.js v4.7.9 in minutes for just $0.05
what's interesting is that deepseek-v4-pro-0813 needed multiple runs with the same prompt. flash found it consistently.
security researchers, we're so cooked :)
‼️ A critical Keycloak flaw could let attackers take over any account.
CVE-2026-18963 lets an unauthenticated attacker reset a user’s password without the emailed action token, including for admin accounts.
Read more: https://t.co/AW9mFGSX4U
AI can remove the friction. It cannot replace the hunter.
@Rhynorater explains how he combines Claude Code, custom skills and autonomous agents with years of Bug Bounty experience to find more vulnerabilities, faster.
See how his AI-powered workflow works 👇
https://t.co/PSa9ZYjtLW
Ever heard of account pre-hijacking?
An attacker registers an account using the victim's email BEFORE the victim ever signs up. Later, when the victim uses SSO with that same email, some apps merge them into the attacker's existing account instead of creating a new one.
- No login
- No write access
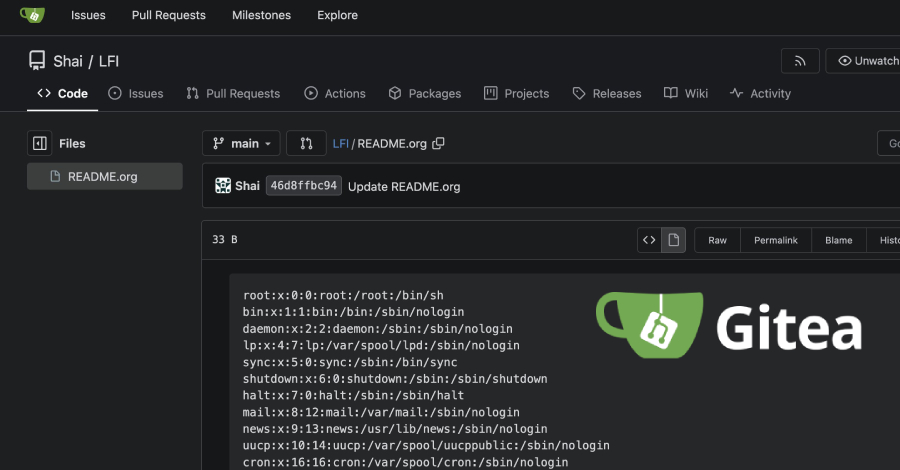
- Just crafted Org-mode markup
🛑 CVE-2026-59774, a critical Gitea flaw, lets attackers use a public repository to read any file accessible to the Gitea service account. Gitea says it could also be chained into command execution.
How it works and what admins should check: https://t.co/uvhe6H0XVH
Administers Linux servers via a web console that allows you to start containers, manage storage, configure networks, and inspect logs.
https://t.co/wH5CFjQnYC
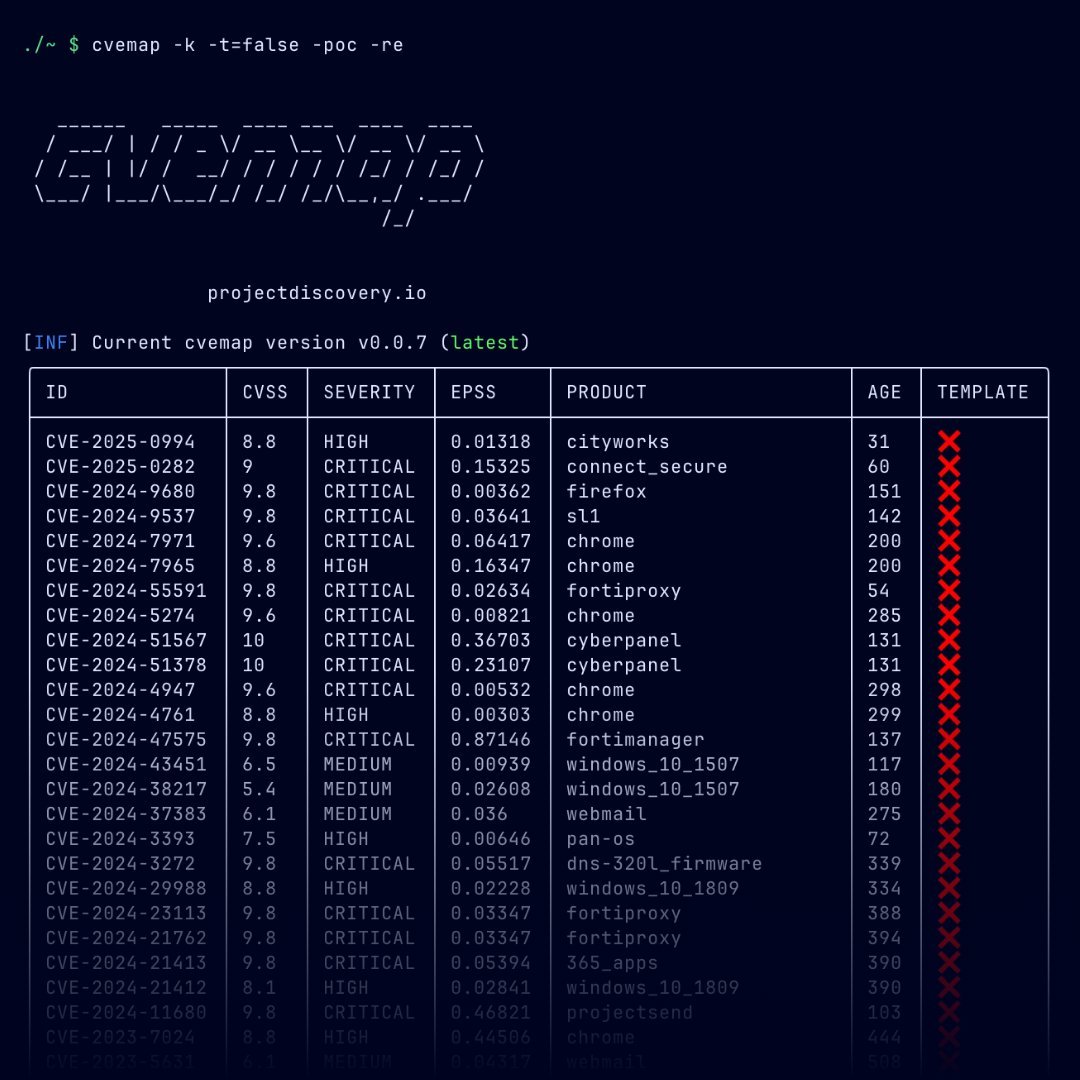
Here's a cool trick for y'all looking to create new Nuclei templates for exploitable CVEs!
Using CVEmap you can get a list of CVEs with public proofs of concept, that have been marked as exploitable by CISA, are remotely exploitable AND don't have a Nuclei template (yet)!
Flags:
-k / -kev: Marked as exploitable vulnerabilities by CISA
-t=false / -template=false: Has no public Nuclei templates
-poc: Has public published POC
-re / -remote: is remotely exploitable
Good luck! 🤞
#nuclei #hacking #pentesting #bugbounty #CVEmap