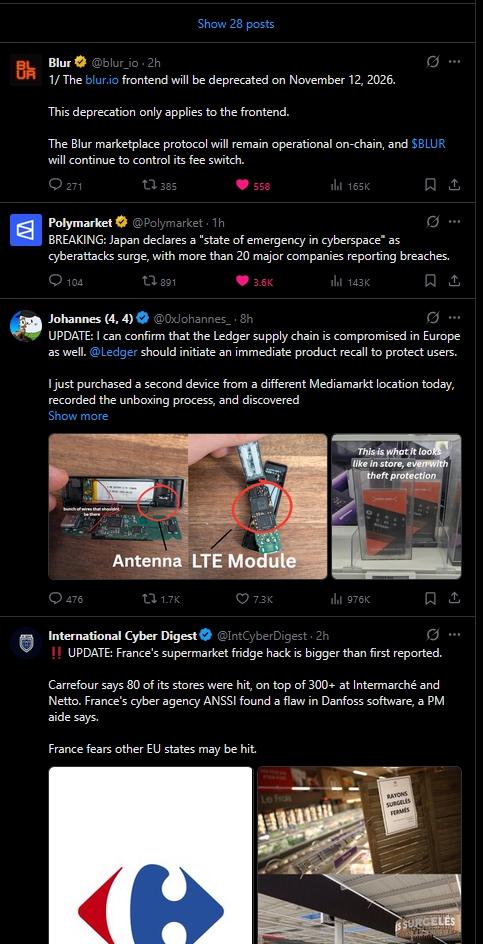
A vulnerability (worse_query) affecting iOS 26.7.1, 27.0.1, and 27.2 allows malicious apps to read local files from other apps, putting seed phrases, private keys, and login credentials at risk across the entire ecosystem. This is an iOS-level issue, not unique to Binance.
Immediate Action Required:
- Delete any apps installed from untrusted sources (such as sideloaded or manually signed IPAs).
- Update iOS and all apps to the latest official versions.
- If you suspect a breach, transfer funds to a new wallet created on a clean device and reset all active login sessions.
Never install unauthorized packages, and keep your software up to date.
@villainmonkey@Pumpfun@fomo I've sent DMs to 75% of the people you're exposing, explaining my personal situation and asking for help. Sad af. Why are you doing this when you're incriminating yourself too? What am I missing?
Scammers are just throwing shit at each other like never before
This was only a matter of time and will only stop when the consequences are bigger than the profits
What a time to be alive CT
One of crypto's largest KOLs has been secretly extracting millions from his audience
We’ll expose him soon
Unfortunately, he’s just a symptom of a much bigger problem
Social trading has brought out the worst in KOLs. It was designed to keep them honest by making every trade public. In reality, the opposite happened
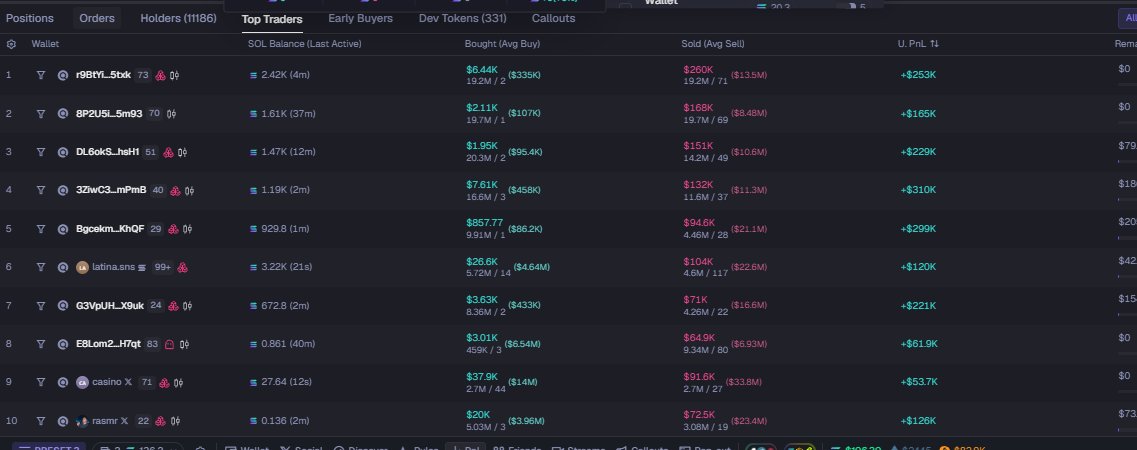
In just a few weeks, we exposed a number of "top social traders" using the same tricks:
• Public wallets to attract copy traders
• Side wallets to dump
• Callouts to farm rewards
• Bundled tokens to hide supply
And there are plenty more doing the exact same thing
Why? Because our industry incentivizes it
1) Launchpads allow it
Most launchpads today are obsessed with one thing: volume. Millions in callout rewards, affiliate links, and top leaderboards. Almost nothing on detecting bundles, side wallets, or shady traders. Scams drive volume. Launchpads have no reason to stop it (other than actually caring about their users)
2) Social trading incentivizes it
Side wallets have become a business model. Before social trading, only big KOLs could do it. Now, anyone who lands on a leaderboard can monetize by dumping on their copy-traders. The temptation is real
3) CT normalizes bundle culture
“Everyone bundles. It's how it's done" - an excuse we hear every time we expose a KOL. Supply control isn't the problem. Hiding it is. If it's so bullish, why hide it? Spoiler: because you're planning to sell
***
Launchpads are paying millions to dishonest KOLs. It's time they start taking it seriously
Audit the top traders. Expose their side wallets. Ban repeat offenders
We have the tools. What's missing is the willingness to use them
No one's coming to save us
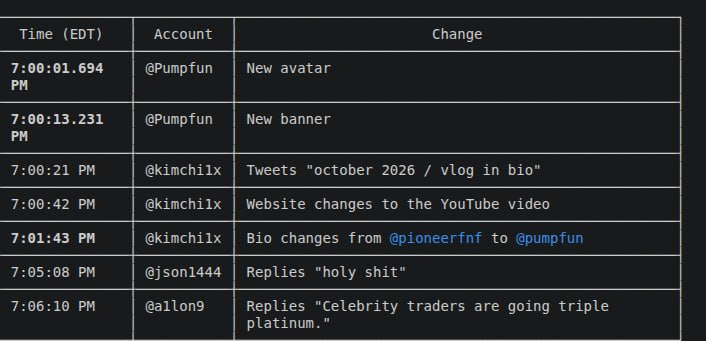
How Kimchi and Pumpfun just extracted over $1,000,000 in 1 hour
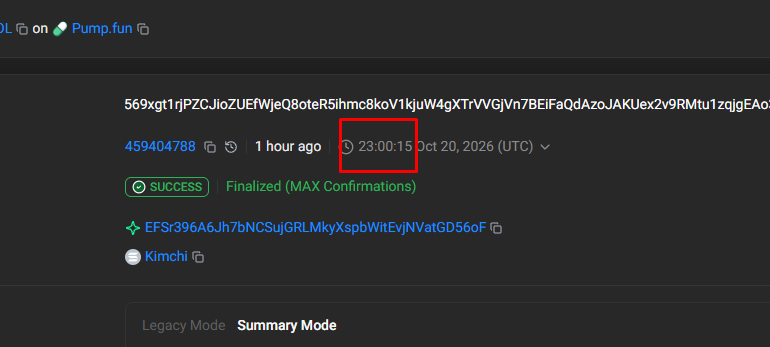
$40M Runner was deployed 13 seconds after pumpfun rebranded, and 1 minute before kimchi changed his bio to @pumpfun
It's physically impossible for a real human to have deployed this coin without insider knowledge
https://t.co/Vzs05sq8Gk
Deploy - 23:00:15 (UTC) / 7:00:15 EST
Kimchi change bio - 7:01:43 / 23:01:43 (UTC)
Top traders made over 1m 😭
JUST IN: Anthropic warns rogue AI agents could be just months away from infiltrating smart home devices, replicating themselves, & spreading across networks autonomously.
We discovered a sophisticated recording device that was hidden inside one of our offices. We used our models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier. We referred the matter to the FBI, and we’re grateful to the agents and prosecutors who moved quickly to make an arrest. The FBI’s investigation is ongoing and we will continue to support their work.
At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data. The employee was terminated.
We take protecting our technology, data, and people seriously, and as a matter of national importance. Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states, and this case is an example of how AI can help address these sophisticated security threats.
🚨 BREAKING: Hackers broke into Meta’s private GitHub repo and stole their source code.
They got in with an employee's stolen credentials and took personal data on ~1,500 people, mostly US employees, stored there against Meta policy…
JUST IN: Man sentenced to 18 months in prison after generating hundreds of thousands of AI songs & using bots to stream them billions of times, outstreaming Taylor Swift & earning $8 million.