New upgrade option is now live on PrettyRecon Zero!
Based on popular demand, Pro users can now upgrade to the Max plan anytime.
And don’t worry about your existing tokens , all tokens from your Pro account will carry over to your Max account.
Upgrade seamlessly. Keep your tokens. Get more power. ⚡
Want better results from our AI security scanner?
A few tips that can make a big difference:
1. Install Python : It helps the agent create and run custom scripts when needed.
2. Install common open-source bug bounty tools : Not mandatory, but recommended. Otherwise, the agent may need to build its own scripts for tasks that existing tools already handle.
3. Install Chrome : Having Chrome available can significantly improve browser-based testing and agent performance.
4. Use targeted scanning : Scan one target/subdomain at a time rather than giving the agent a huge scope. This generally produces more focused results.
5. Provide credentials when authorized : For authenticated testing, provide relevant cookies or multiple user accounts. This allows the agent to test for cross-account data access, privilege escalation, IDOR/BOLA, and other authorization issues.
6. Use the Focus string : When creating a project, the Focus string is optional, but adding custom prompts and target-specific details can significantly improve the results.
7. Use custom skills selectively : Most common skills are already built in. Avoid adding too many skills because they can cause unnecessary context bloat. Add only target-specific skills when needed, and remove them after testing that target. Custom skills aren't required, but they can improve results for specialized targets.
Reminder:
Always do single path or single domain scan for better results, prettyrecon zero test subdomains by itself related to target.
Do not give wild scope like *.target.com as input.
Tips for prettyrecon zero.
https://t.co/wWicLtqbm6
Always do deep scan for better results & if you are giving only subdomain without path that will give you better results .
Use ask feature to generate full poc exploit or get more details about findings & hypothesis.
You can steer agent in between run to give endpoints or tips based on agents reasoning.
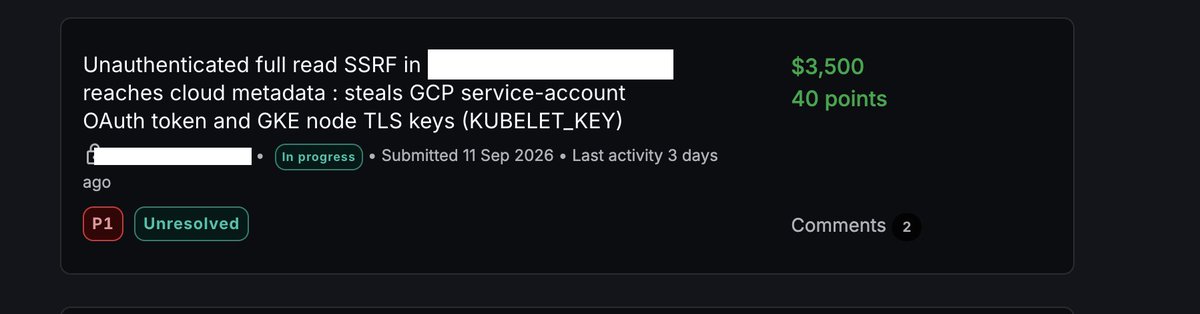
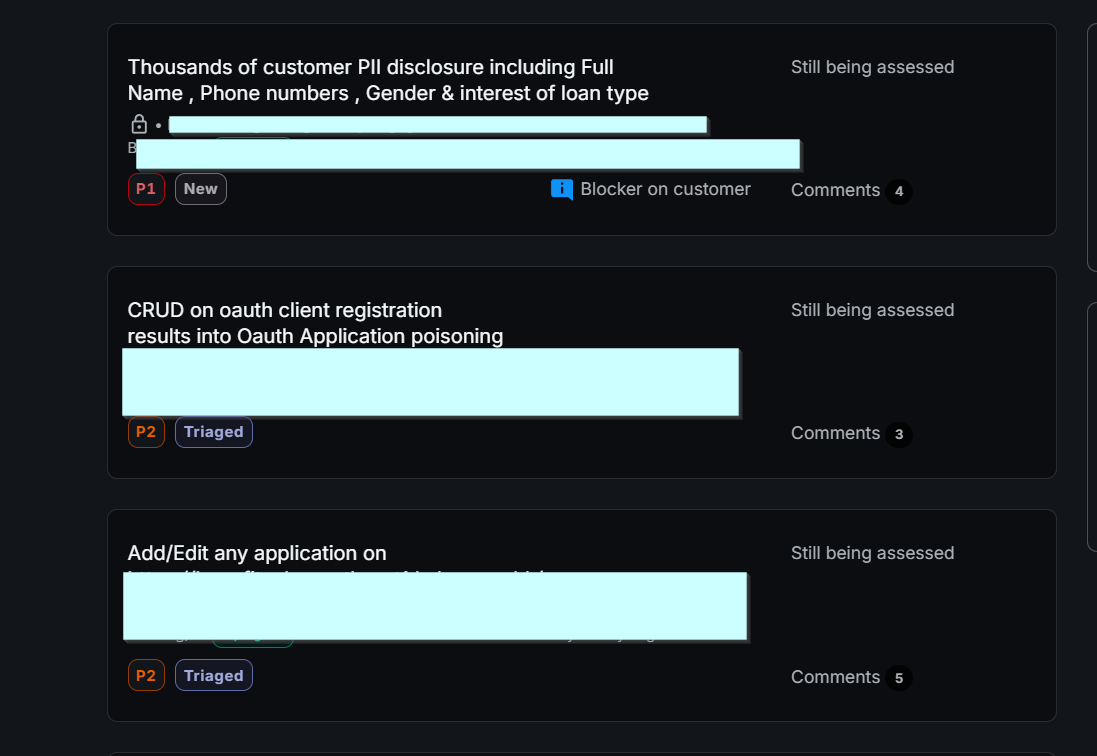
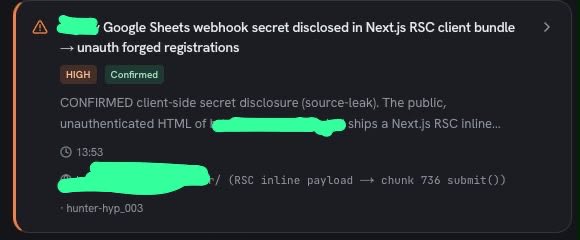
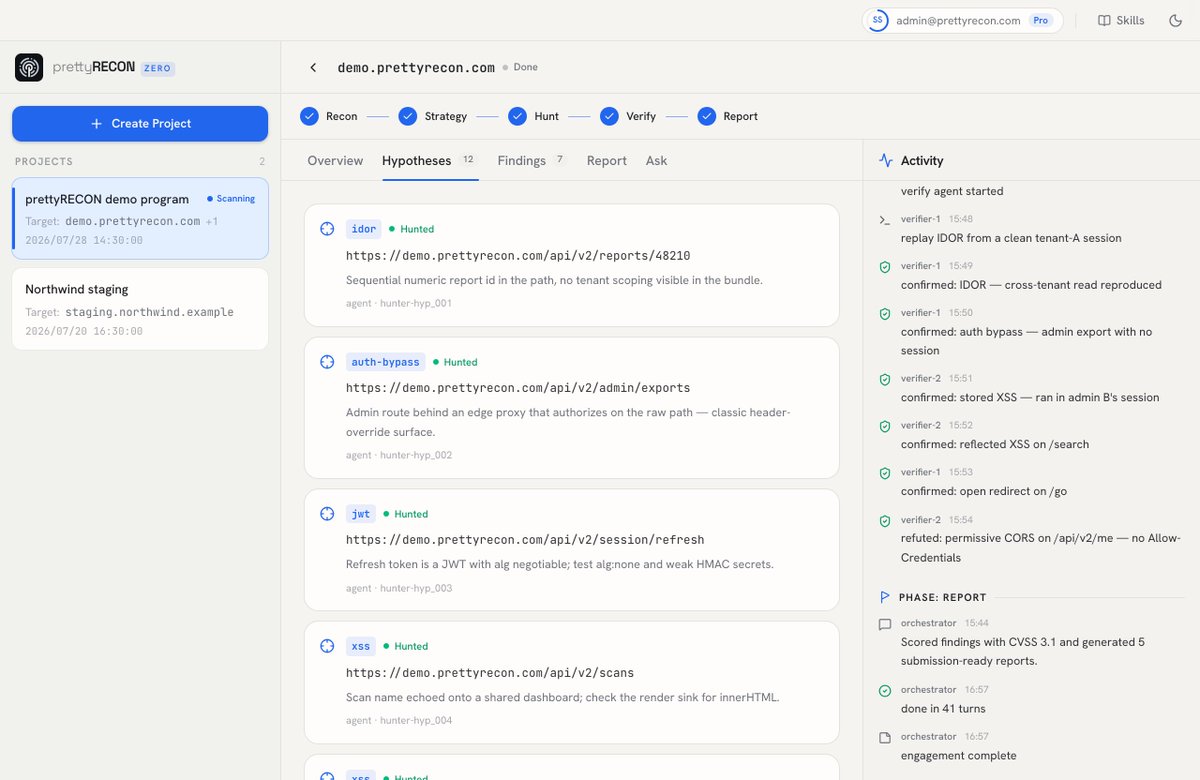
All this found by @PrettyRecon zero , No user interaction at all , Just given target with URL which seems interesting & it come up with this findings.
yes , Its that easy with AI now .
First scan, P2.
Secret disclosed in a Next.js RSC client bundle → forged registrations, unauth.
Confirmed by a second agent before it ever hit the report.
prettyRECON Zero is in beta. Grab a seat 👉 https://t.co/yk202Xdf4A
Tips for prettyrecon zero.
https://t.co/wWicLtqbm6
Always do deep scan for better results & if you are giving only subdomain without path that will give you better results .
Use ask feature to generate full poc exploit or get more details about findings & hypothesis.
You can steer agent in between run to give endpoints or tips based on agents reasoning.
prettyRECON Zero now runs on Debian & Ubuntu
Native build, same autonomous recon — point it at an authorized target and let the agents work.
#BugBounty#InfoSec#Linux#Ubuntu#Debian
Want better results from our AI security scanner?
A few tips that can make a big difference:
1. Install Python : It helps the agent create and run custom scripts when needed.
2. Install common open-source bug bounty tools : Not mandatory, but recommended. Otherwise, the agent may need to build its own scripts for tasks that existing tools already handle.
3. Install Chrome : Having Chrome available can significantly improve browser-based testing and agent performance.
4. Use targeted scanning : Scan one target/subdomain at a time rather than giving the agent a huge scope. This generally produces more focused results.
5. Provide credentials when authorized : For authenticated testing, provide relevant cookies or multiple user accounts. This allows the agent to test for cross-account data access, privilege escalation, IDOR/BOLA, and other authorization issues.
6. Use the Focus string : When creating a project, the Focus string is optional, but adding custom prompts and target-specific details can significantly improve the results.
7. Use custom skills selectively : Most common skills are already built in. Avoid adding too many skills because they can cause unnecessary context bloat. Add only target-specific skills when needed, and remove them after testing that target. Custom skills aren't required, but they can improve results for specialized targets.
We’re launching PrettyRecon Zero!
An AI-powered security scanner built for security professionals, organizations & bug bounty hunters.
The beta is now live: https://t.co/7lf5gm7wPh
Find vulnerabilities faster
AI-powered security testing
Built for real-world security workflows
We’re accepting limited beta signups and subscriptions while we scale the platform.
If you’re into application security, pentesting or bug bounty sign up, subscribe, try it out, and tell us what you think!
#CyberSecurity #AppSec #BugBounty #Pentesting #AI #InfoSec
Ok ..Getting good results. & some findings are actually above my capabilities
Tips:
1. Install python in machine it will drastically improve performance of this tool.
2. Install as much as open source tools like project discovery tools , subdomain finder , waybackurl etc
Download Issue Fixed!
The hard cap on downloads for our beta release was reached, which temporarily prevented new downloads.
The issue has now been fixed, and you should be able to download the app normally again.
Thank you for your patience and for the amazing response to our beta release! 🙏
We’re launching PrettyRecon Zero!
An AI-powered security scanner built for security professionals, organizations & bug bounty hunters.
The beta is now live: https://t.co/7lf5gm7wPh
Find vulnerabilities faster
AI-powered security testing
Built for real-world security workflows
We’re accepting limited beta signups and subscriptions while we scale the platform.
If you’re into application security, pentesting or bug bounty sign up, subscribe, try it out, and tell us what you think!
#CyberSecurity #AppSec #BugBounty #Pentesting #AI #InfoSec
🚨 Download Update
We had a hard cap on the number of downloads for our beta release, and it was exceeded much faster than expected.
As a result, downloads may not work for the next few hours. We’ll reopen downloads shortly.
Sorry for the inconvenience, and thank you for the amazing response! 🙏
We’re launching PrettyRecon Zero!
An AI-powered security scanner built for security professionals, organizations & bug bounty hunters.
The beta is now live: https://t.co/7lf5gm7wPh
Find vulnerabilities faster
AI-powered security testing
Built for real-world security workflows
We’re accepting limited beta signups and subscriptions while we scale the platform.
If you’re into application security, pentesting or bug bounty sign up, subscribe, try it out, and tell us what you think!
#CyberSecurity #AppSec #BugBounty #Pentesting #AI #InfoSec
The future of Cyber Security isn't more tools.
It's AI that knows how to use them.
PrettyRecon Zero is coming.
Autonomous reconnaissance. Intelligent security testing. Built for hackers.
Stay tuned.
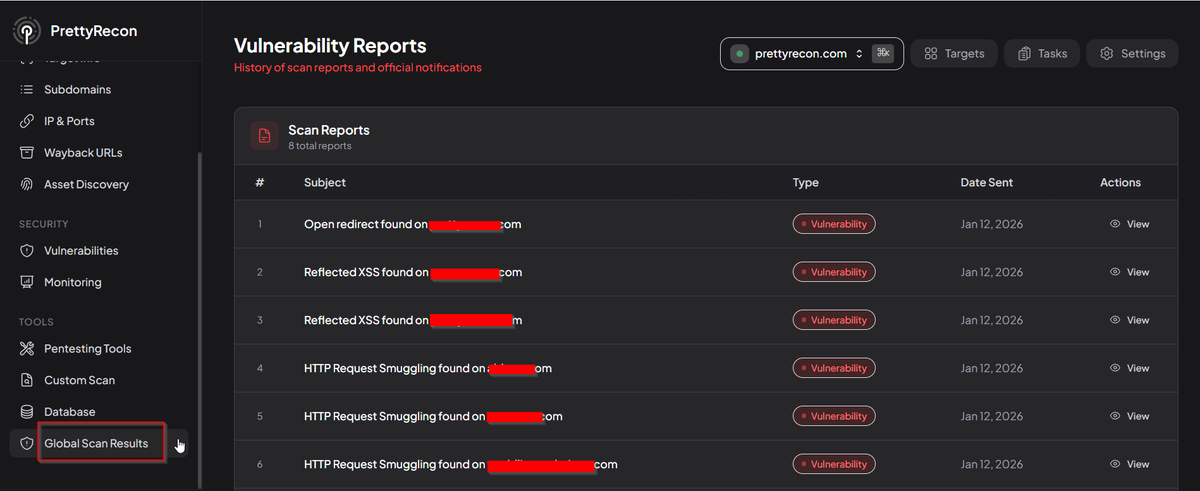
🚀 Recon on autopilot! @prettyrecon’s new Global Scan is live! 🛡️⚡️
Our smart AI engine now scans your targets daily. Users are already getting email alerts with fresh findings delivered straight to their inbox! 📩✨
📊 Visit : https://t.co/gOhbHe8GuN
#BugBounty#Infosec#AI