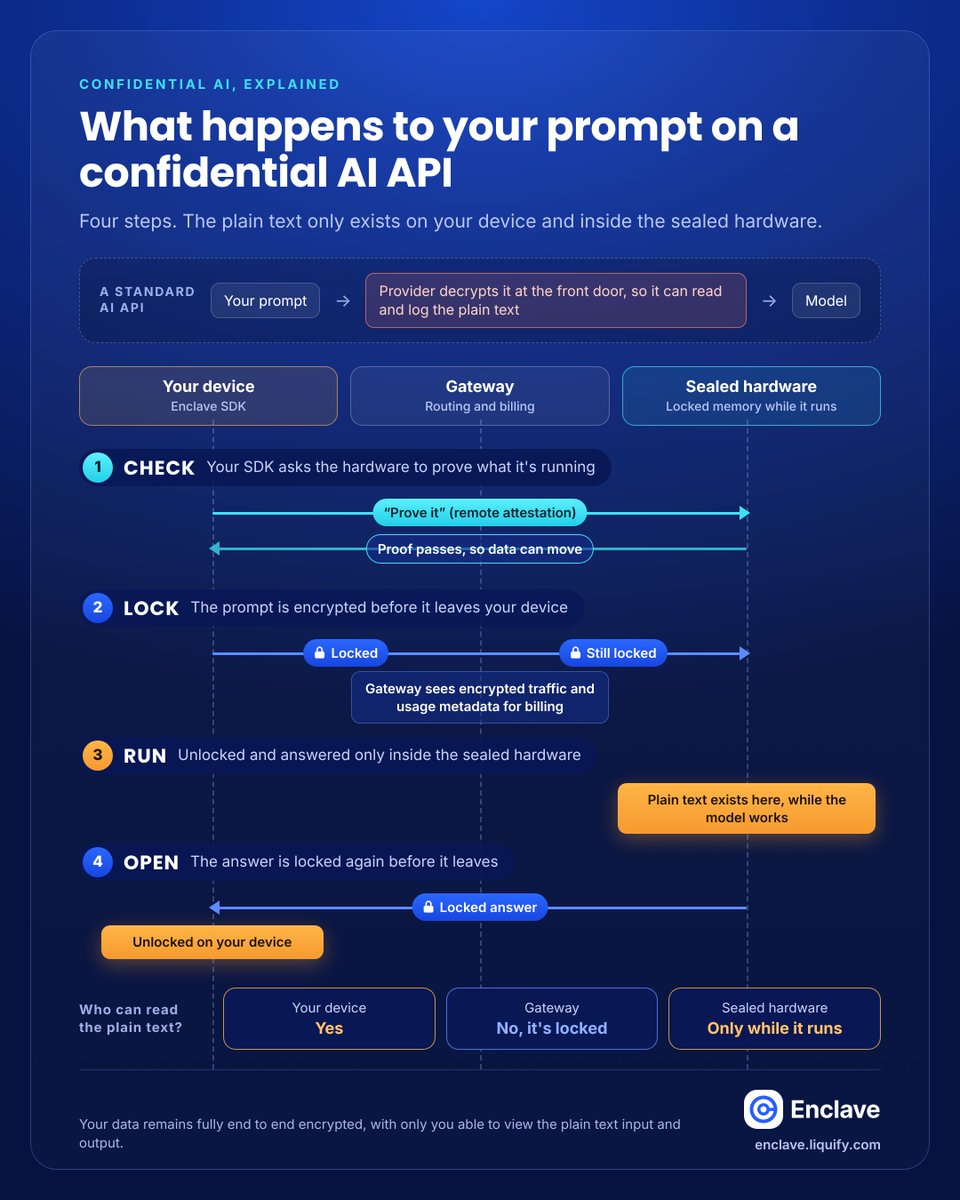
If you’re the one who has to approve AI for client data, this is the diagram worth saving.
Sooner or later your auditor asks two things about any AI vendor: who can read the prompt, and how do you know? Here’s how a confidential AI API answers both:
1. Check: before sending anything, your own software asks the hardware to prove what it’s running. That attestation result is evidence you can keep.
2. Lock: the prompt is encrypted on your device. Our gateway handles encrypted traffic and the usage metadata we bill on.
3. Run: the prompt is decrypted only inside sealed hardware, while the model works on it.
4. Open: the answer is encrypted before it leaves, then decrypted on your device. Prompts, responses and logs are stored encrypted on your device by default.
One honest caveat: sealed hardware keeps the operator out, and the model software inside still has to be patched. So ask every provider how quickly they update it, and ask us too.
Liquify Enclave is a confidential AI API for legal, finance, healthcare and insurance teams. Your data remains fully end to end encrypted, with only you able to view the plain text input and output.
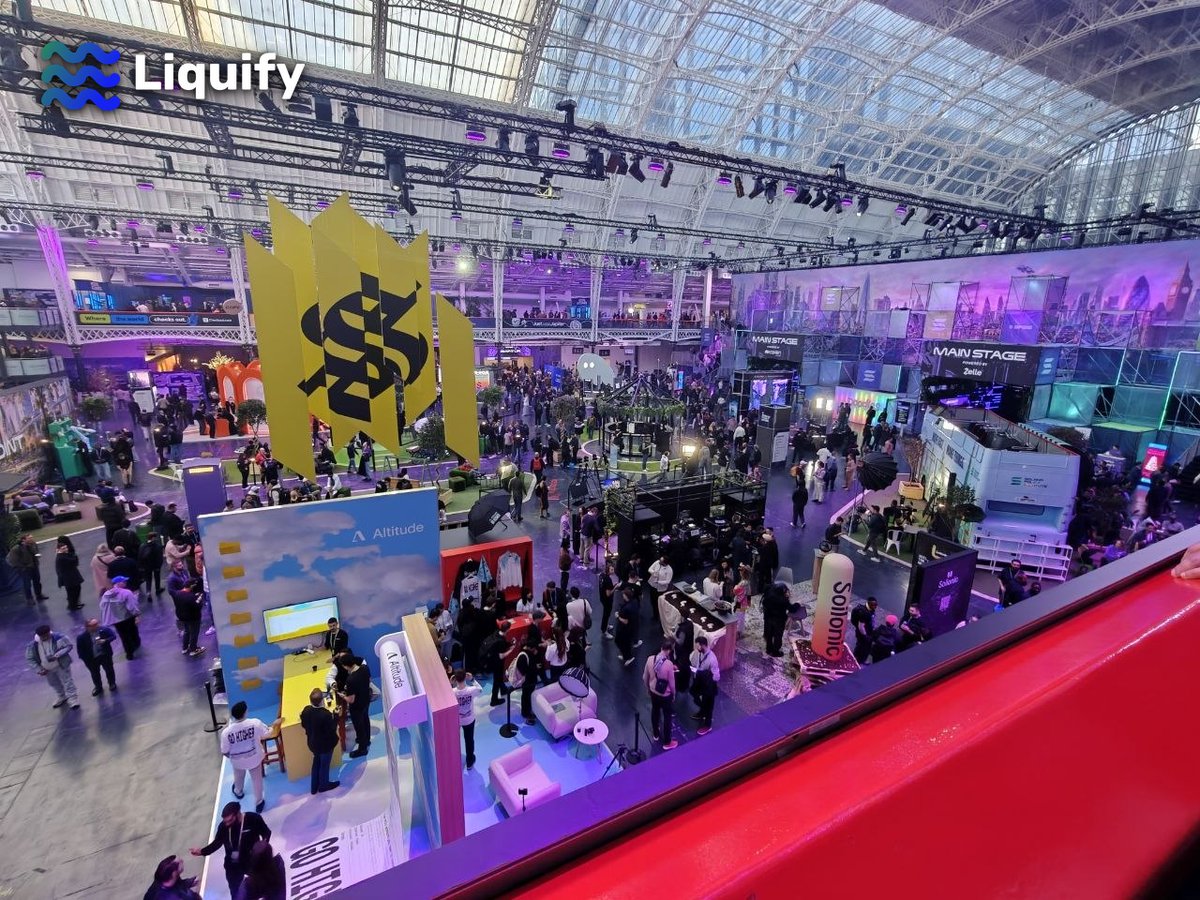
We're at @SolanaEvents Breakpoint in London this week, talking node infrastructure, staking and private AI for teams handling sensitive data.
If you want to chat, come find us. DMs are open.
What moved across Web3 infrastructure (16/11)
📌 Visa adds Monad to its stablecoin settlement program
📌 Pyth is now an approved distributor of NYSE market data
📌 DTCC plans to bring DTC-tokenized assets to Solana in the second half of 2027
📌 USDG deposits in Morpho vaults on Arbitrum grew 13x in four weeks
📌 Solana Breakpoint is in London until 17 November
📌 New on Enclave: build, host or use a confidential API for private AI
Questions to ask an AI vendor that says "it runs in a secure enclave":
✓ Is the hardware verified before anything is sent?
✓ What software runs inside it?
✓ Who patches that, and how fast?
✓ Can you check any of this yourself?
The enclave is the start of the answer.
Enclave keeps your conversations locally. On your device, not ours.
-> Prompts, responses and logs stored encrypted by default
-> No chat history sitting in a vendor database, waiting for a breach or a policy change
-> Your company data doesn’t end up training your competitor’s AI
What you tell it stays with you.
@markgurman 2025: "use AI for everything"
2026: "use AI for everything, but only $25 of it a day"
Open models just got a lot more interesting to finance teams.