i thought read() was a syscall wrapper, but it can dlopen a bytecode interpreter and execute your code
"house of windy" turns this into leakless code execution with only OOB null byte writes
https://t.co/Rvzd6glGv3
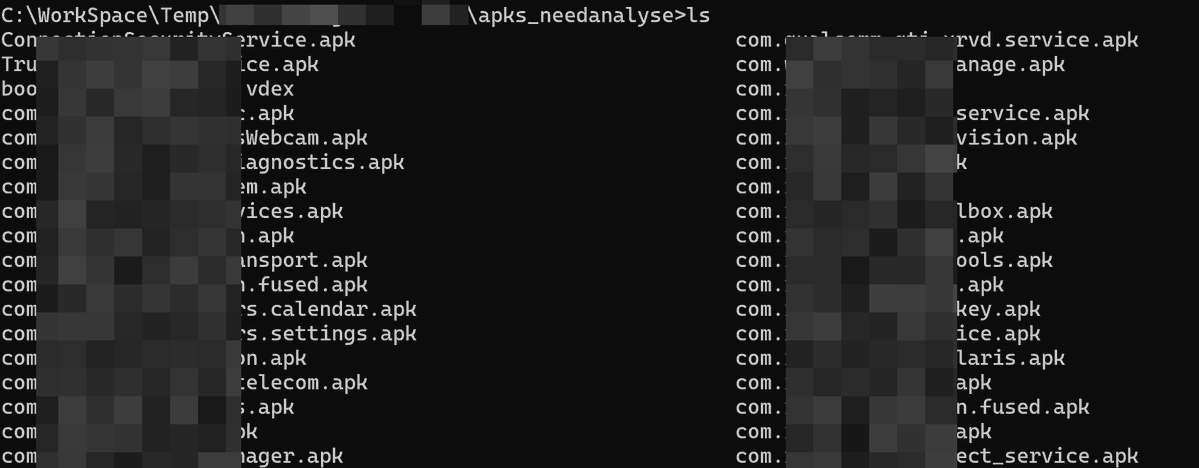
I used /goal + ASC + adb to analyze my phone. The agent pulled 50+ APKs with uid=1000, then used ASC to analyze them without exporting any pseudocode. After 10 hours, the agent had rooted my phone...😐
#mobile#bugbounty#security
https://t.co/OWoPj03lrz
https://t.co/vX9DChmHkP
A thread about concentration risk vs proliferation risks: AI has both - a lot of risks with AI are risks of "bad people getting access to powerful models, enhancing their ability to do bad", concentration risks are "people that believe they are doing good by restricting ...
We provide SBOM with VEX data indicating why we consider it’s not applicable (e.g. code not reachable, configuration not met) and we do that from firmware. If you do naive CVE matching from versions extracted from lock files you’re not solving anything, it’s compliance theater.
I used to be very pro-SBOM but changed my mind.
If I export an SBOM and run it through a vulnerability scanner, it’ll show a bunch of crits, but nothing in the SBOM indicates that those don’t apply in my environment/config?
It’s just more CVE porn
We do our best to provide meaningful data, even when vendors provide garbage feeds and don’t maintain them properly:
- https://t.co/Etmf4xlM5F
- https://t.co/bGiPi6kjpN
looks like they have a pretty decent CTI team. there’s a lot to unpack but french scammers registering policenationale[.]cc to sell stolen cards is *chef’s kiss*
We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: https://t.co/0EJUnYEgfz
Today I'm introducing two new open source IoT firmware analysis tools:
Moria and Mithril
Moria is a firmware extraction tool just like binwalk and unblob, except for one major difference: ZERO external extractor dependencies!
No more relying on ancient and unmaintained extraction utilities with numerous bugs / patches.
EVERY filesystem extractor has been rewritten in 1st party C++ to be fast and flexible.
Mithril is moria's companion. It scans extracted filesystems for secrets and SBOM. Correlates CVEs. Syncs with NVD, EPSS and KEV datasets.
Check out my blog post where I kick the tires:
https://t.co/qBAQFPiGES
@nmatt0@devttyS0 as the main unblob maintainer and de-facto maintainer of jefferson, ubi-reader, arpy and sasquatch forks, you took the right direction. I tried hard to migrate these to modern python (uv, pytest, pre-commits) but lack of resources and incentive got in the way.
Повну емуляцію апаратної платформи Nokia 6600 (NHL-10) у QEMU завершено. GSM-зв’язок працює end-to-end:
Відправка та прийом СМС
ARM → DSP → IQ → Osmocom → IQ → DSP → ARM