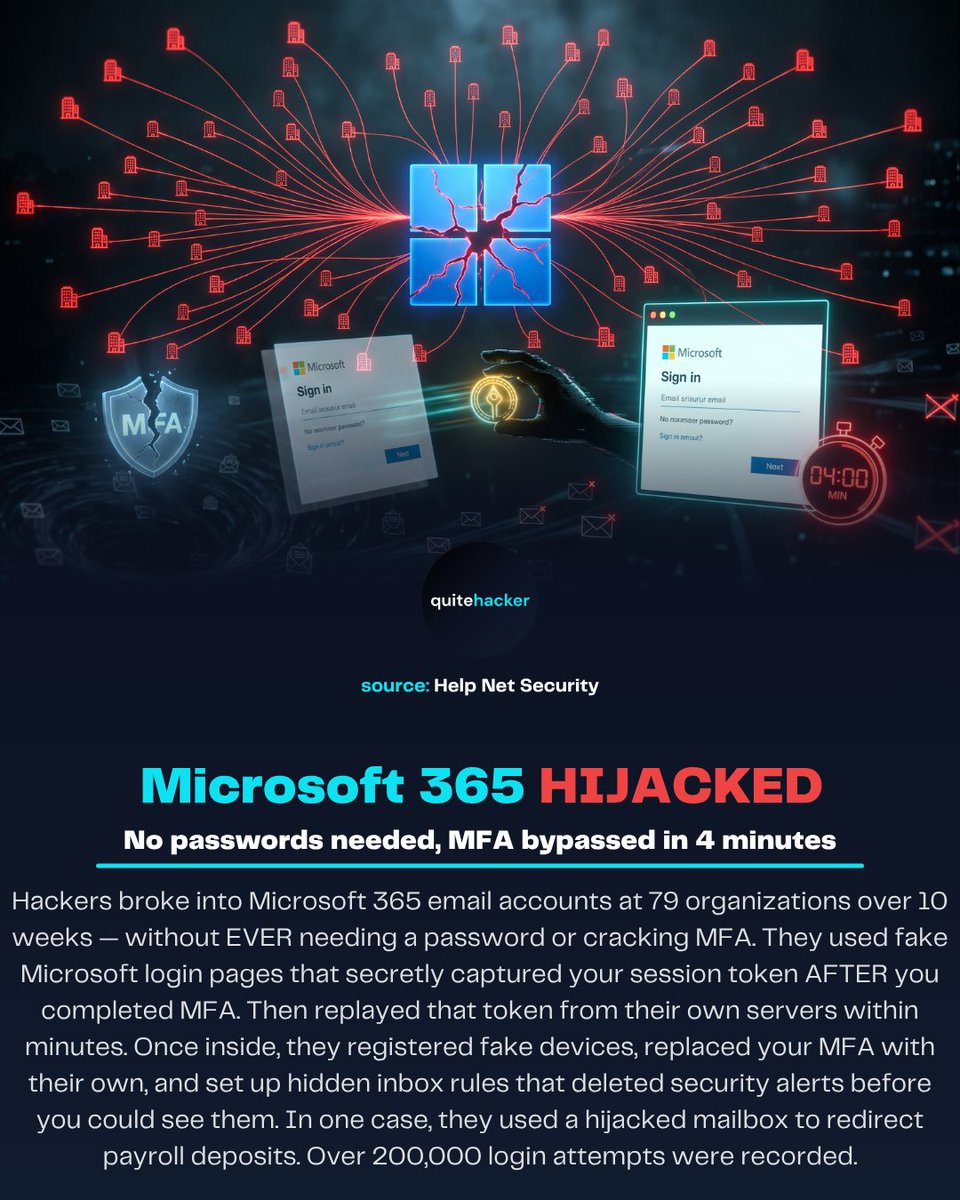
🔓 Hackers set up fake #Microsoft login pages. You type your real password, complete your real MFA — and the page secretly captures the session token Microsoft issues AFTER MFA. The #hacker replays that token from their own server within minutes. You're in? They're in too.
🏢 The dataset allegedly covers PwC offices across multiple countries — Mexico, Canada, and more — with records dating to 2026. They've given PwC 4 days to negotiate. PwC confirmed a "cybersecurity incident" but says it only involved employee learning records.
🔒Browsers are now patched. But here’s what nobody’s talking about: Python, Ruby, Go, Node.js, and most server-side tools DON’T check revocation. They still trust the compromised keys. The flaw was so catastrophic that Fedora delayed its entire OS release.
🔑☁️ Huntress confirmed unauthorized sign-ins in 173 partner and customer tenants using a compromised #Microsoft 365 credential belonging to #ConnectWise#Cloud#Backup.
The UK Legal Aid Agency, part of the Ministry of Justice, says attackers who breached its systems in April 2025 took records dating back almost five decades, including about 250,000 from before 2007. Stolen data includes criminal history, national ID numbers, debts and payments.
Stores had to throw away food, and some equipment began to catch fire. Danfoss says most affected units were older models that are end of life, with no security updates since 2021. How the attackers got in has not been confirmed.
🧊🔥 Hackers turned French supermarket fridges into ovens, heating them up to 50°C.
On the night of October 11, attackers took remote control of Danfoss refrigeration controllers at hundreds of French supermarkets, including 80 Carrefour stores and about 30 Monoprix stores.
An attacker reportedly abused IT company Pays' lawful access to Denmark's CPR register and pulled 8,749,975 records, including about 3.3 million people who have died. Access reportedly began September 10 and lasted 21 days and 17 hours. Pays confirmed its access was abused.
Here's where it gets wild — instead of filing an FIR, #IITKanpur is actually considering giving him a SECOND CHANCE. The institute wants to assess his technical skills rather than punish him.
https://t.co/3JTWVqcz4r
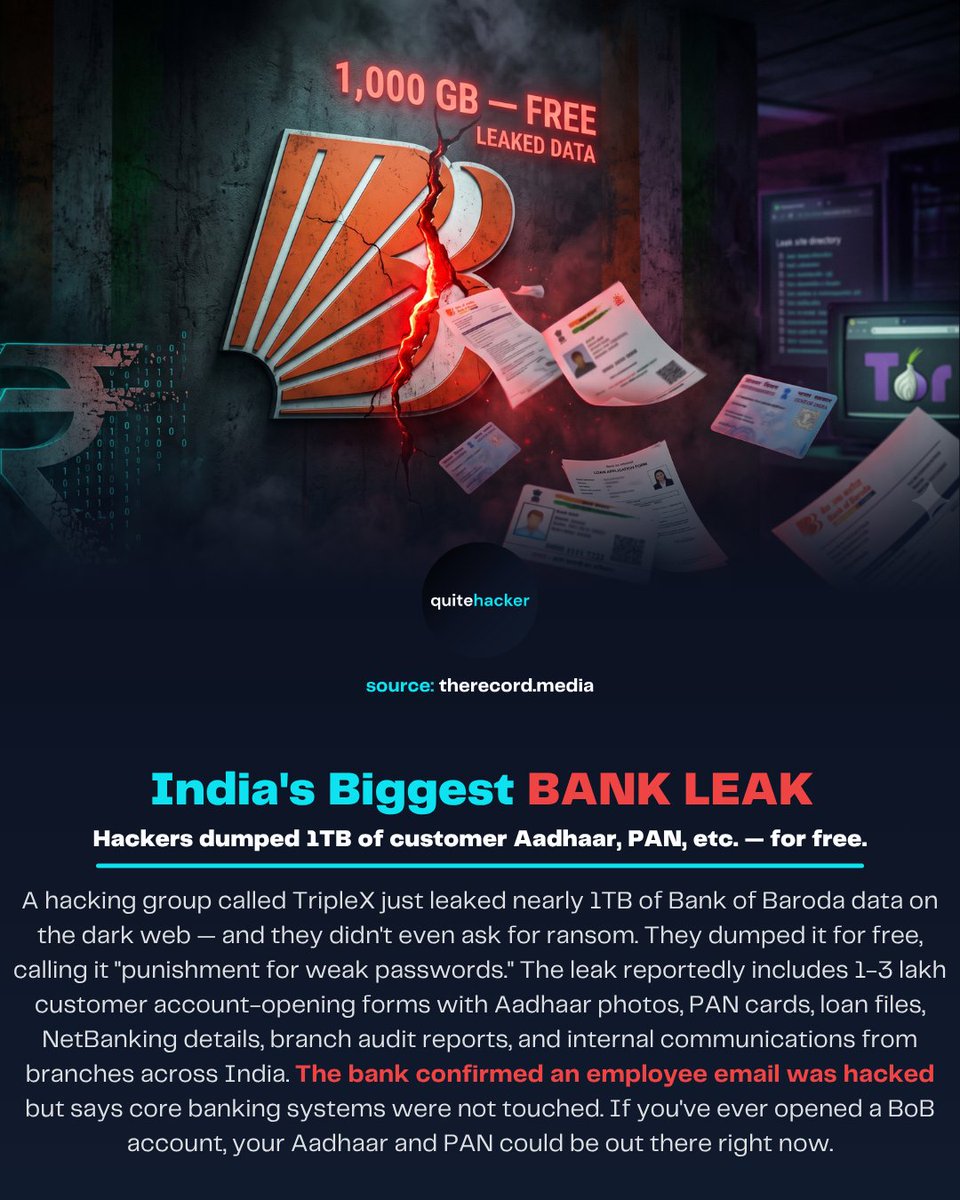
The leaked data includes 1-3 lakh account-opening forms with Aadhaar photos & PAN numbers, savings & loan account records, NetBanking user details, NRI & corporate banking files, branch audit reports, & internal communications from branches across India.
https://t.co/VhJ36yMApV