IT was a fun and challenging journey dissecting one of JavaScript's most incredible bugs. Here’s a detailed write-up for React2Shell (CVE-2025-55182): https://t.co/rI1sL8syjp
#JavaScript#React2Shell#CyberSecurity
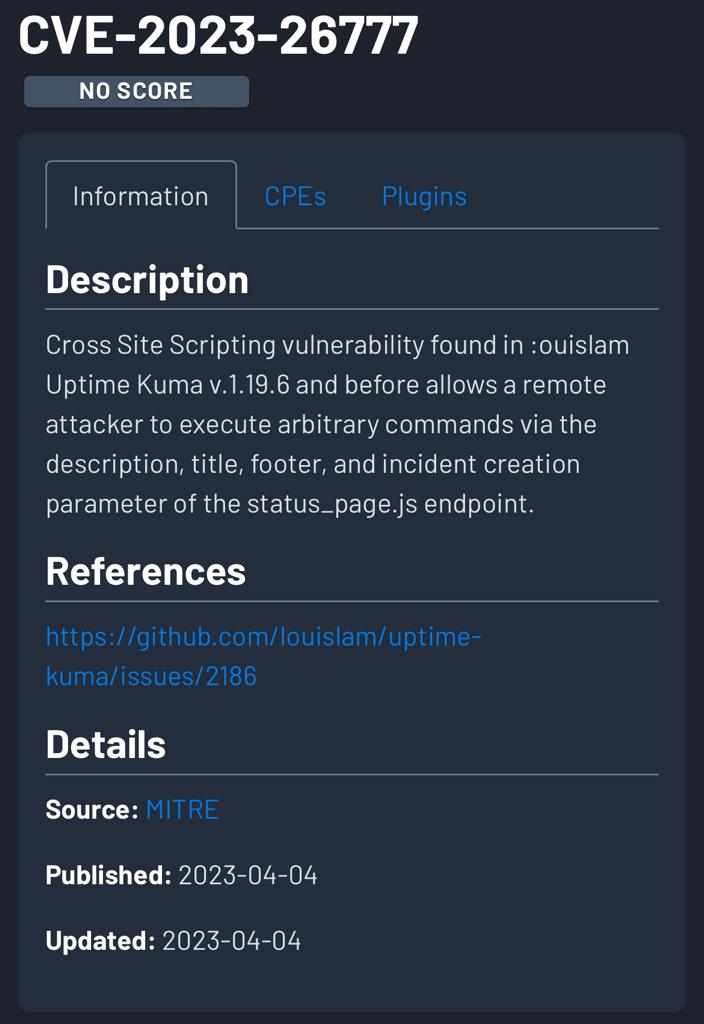
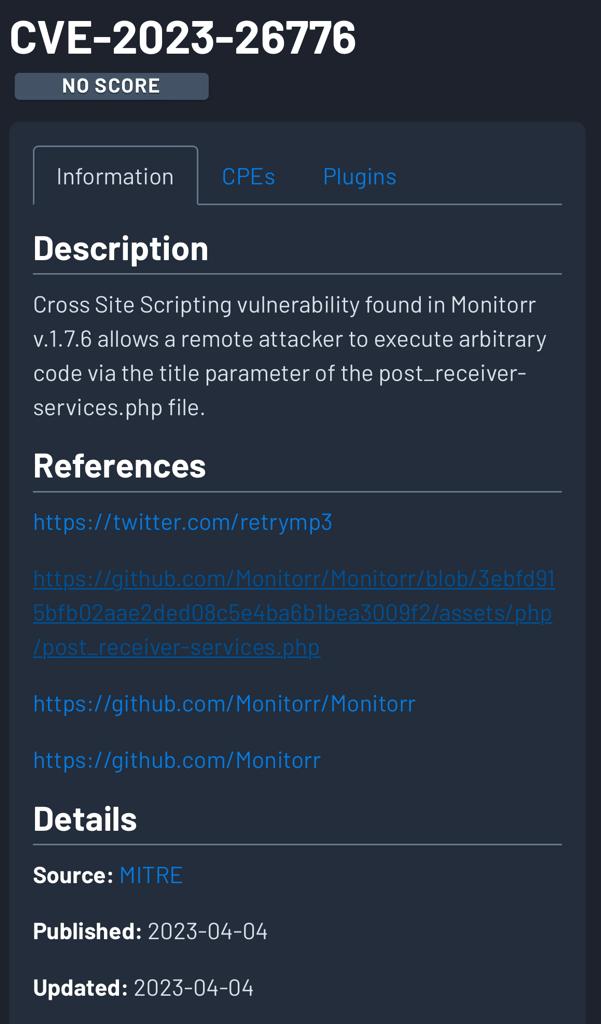
Got 5 CVE-id's assigned on my name(CVE-2023-26773 to 26777).
Started my research in February/2023 still doubting myself.
I ended up finding multiple vulnerabilities on different projects.
On 04/04/2023 I got 5 vulnerability reports verified and accepted by @MITREattack.
#CVE
7 hours left for the CTF
We still have two unsolved challenges: b3typer (Safari Pwn) and Blue Lock (Malware Reversing).
Play ctf @ https://t.co/kAha0ga8dk
We also still have cash prizes up for grabs!
Don't forget to join our discord at https://t.co/0pwR8iBQAF
4 hours into the CTF, and we have 171 teams on the scoreboard!
Want to reverse encrypted malware, or pwn the Linux Kernel and Safari Browser?
We still have first bloods up for grabs, and prizes to play for!
Hurry up and grab your flags @ https://t.co/KBmW0W9lLL
Don't miss out on the fun! #bi0sCTF is starting in just 24 hours. We invite you to register at https://t.co/TmyDME0rT8 and showcase your skills for a chance to win one of the following prizes:
- 1st place - $300
- 2nd place - $200
- 3rd place - $100
#ctf#cybersecurity
Exciting news! Registration for #bi0sCTF 2022 is officially open! Get ready to put your hacking skills to the test and compete against the best in the industry. Don't miss out - sign up now at https://t.co/TmyDME0rT8
#cybersecurity#ctf
CVE-2022-23475 daloRADIUS is an open source RADIUS web management application. daloRadius 1.3 and prior are vulnerable to a combination cross site scripting (XSS) and cross site request forgery (CSRF) vulnerability which leads to account takeover ... https://t.co/sRNYWUMWaD
CVE-2022-23475 daloRADIUS is an open source RADIUS web management application. daloRadius 1.3 and prior are vulnerable to a combination cross site scripting (XSS) and cross site request forgery (CSRF) vulnerability which leads to account takeover ... https://t.co/sRNYWUMWaD