A privilege to meet His Excellency the Ambassador of Israel to Kenya at #CyberWeekAfrica2026 in Nairobi.
We spoke about cyber security, artificial intelligence governance and building skills in Kenya. Grateful for the conversation, and looking forward to continuing it.
Nairobi did something to me I was not expecting.
I arrived with ideas I had been building quietly for years. Within weeks they had a team, a partner and a full room.
What happens when you put the right body of work in the right environment?
Nairobi, we are not done.
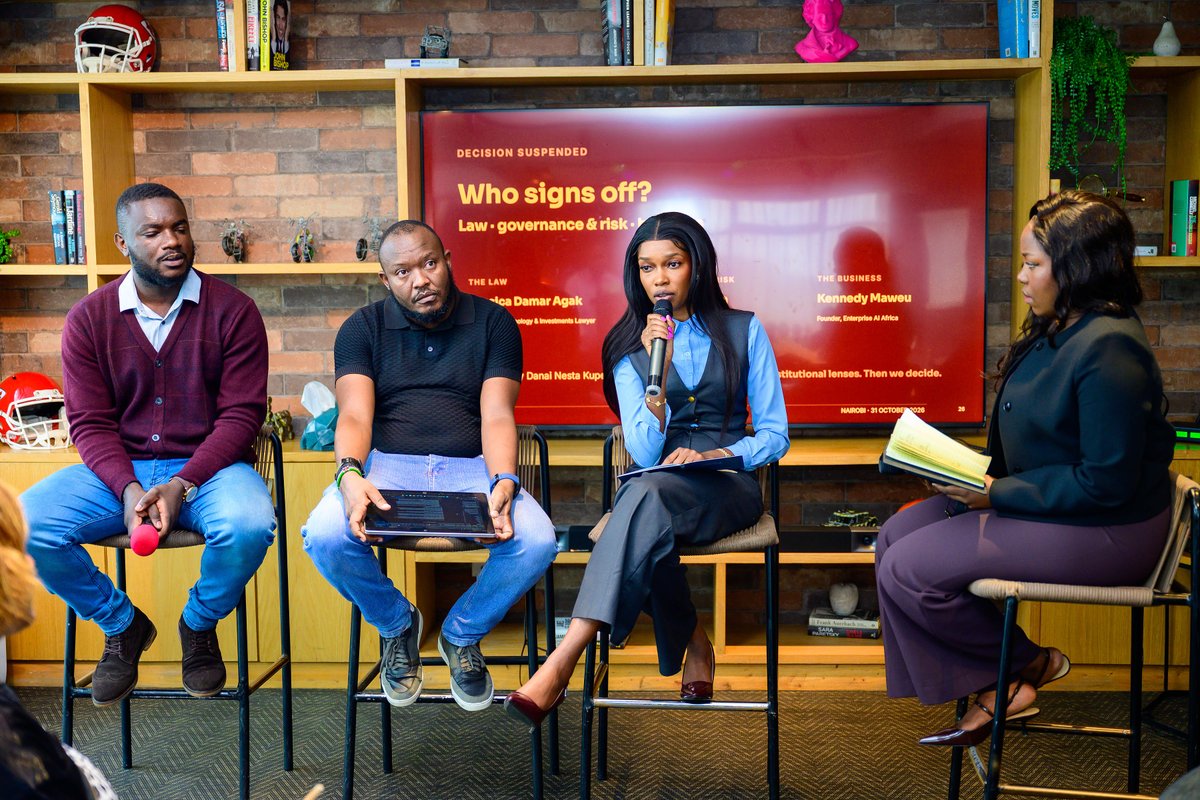
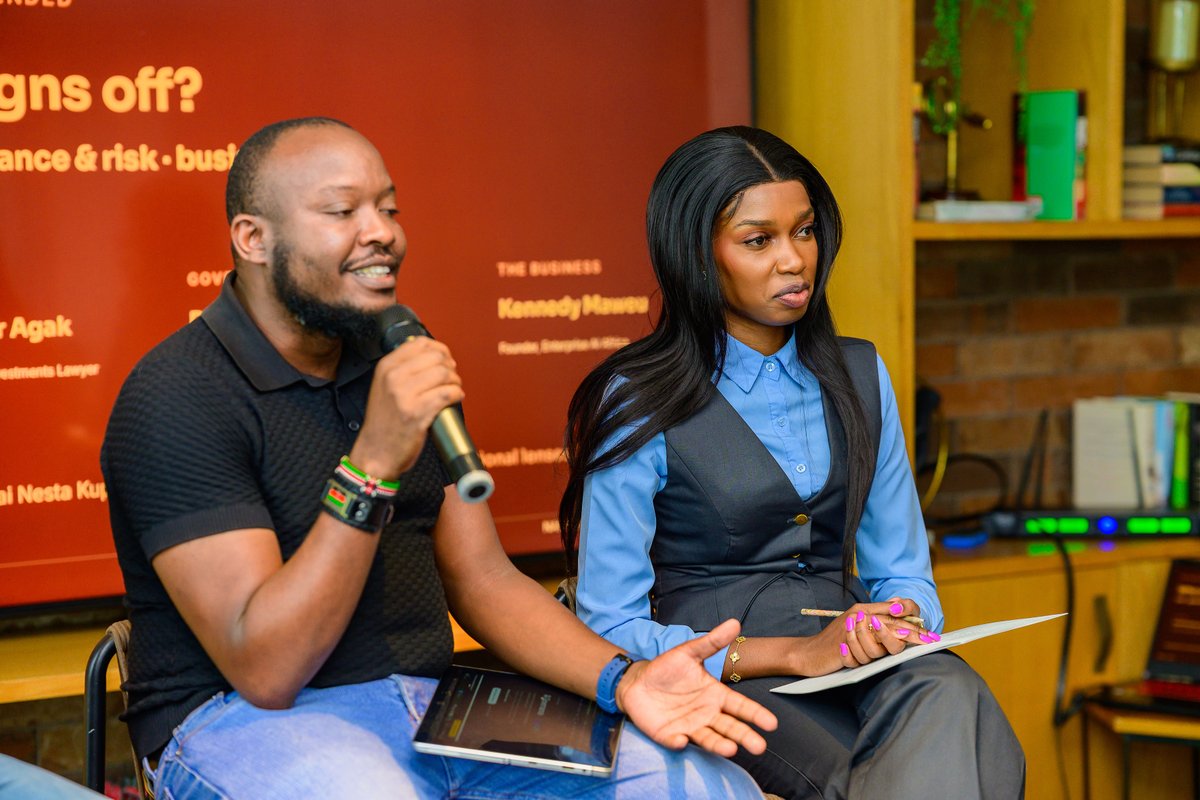
Saturday’s panel had one question:
When AI influences a decision affecting a customer, patient or citizen, who signs off, and on what evidence?
Law had one answer.
Business had another.
Risk had another.
They did not agree.
That was the point.
#AIGovernance#AIRisk#DICB
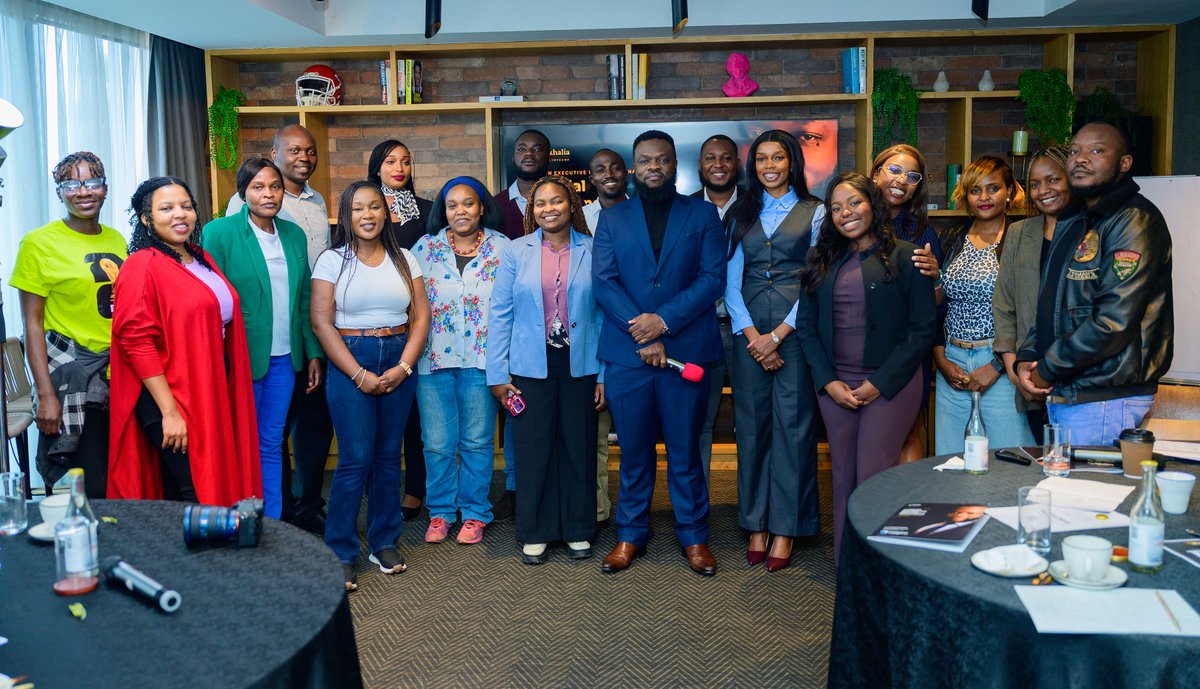
Three weeks ago this was an idea and a few WhatsApp messages in Nairobi.
On Saturday the room was full.
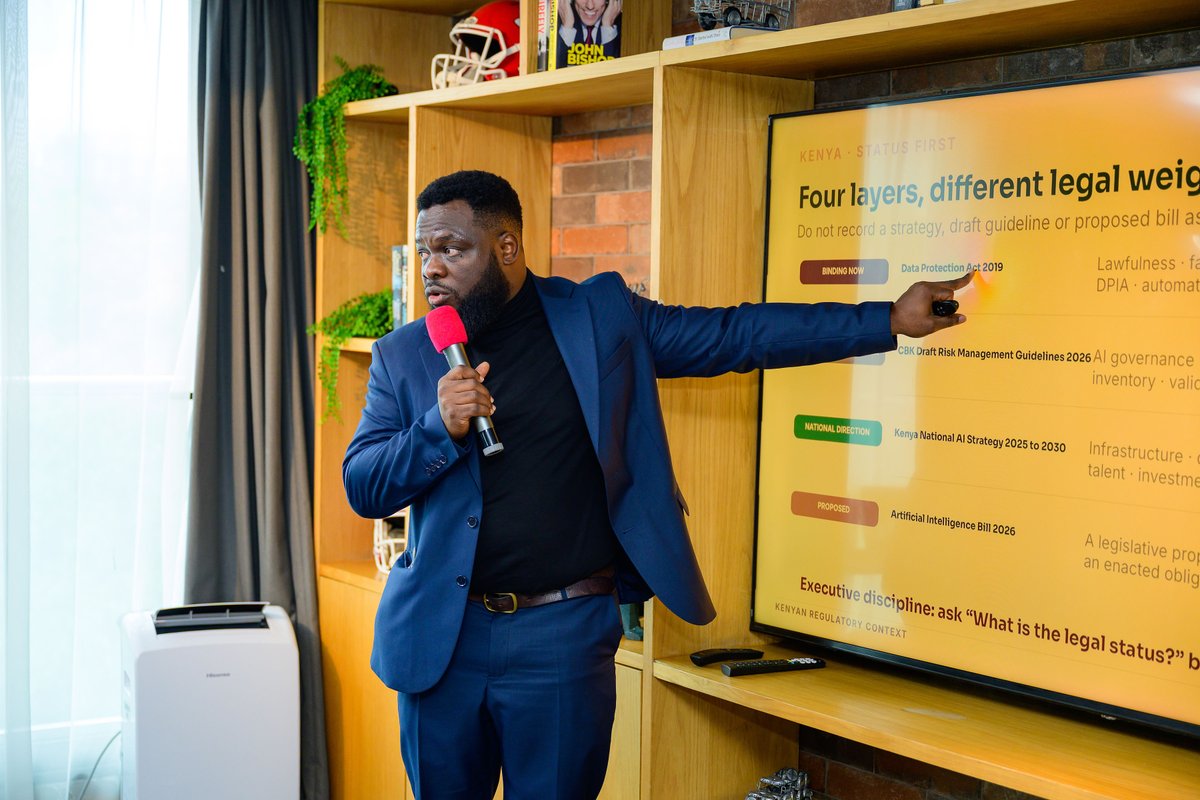
Lawyers, bankers, telecoms, government, academia and diplomats spent two hours pulling real AI use cases apart.
Who approved it? What evidence? Who is checking now?
That was DICB Nairobi. More soon.
#AIGovernance #DICB #Nairobi
On Saturday 31 October, 10am to 12pm, at The Social House Nairobi, 154 James Gichuru Road, Lavington, thirty leaders from banking, insurance, law and technology will work through what Kenya’s Artificial Intelligence Bill would require of the AI their organisations already run. Practical feedback from the people who will have to comply.
@karennyamunbo, as the Bill’s sponsor, we would be honoured to have you in the room. Programme details: https://t.co/hs8Rto3JN4
#DrIkhaliaCyberBootcamp #DICB #AIGovernance #AI #Kenya
On Saturday 31 October, 10am to 12pm, at The Social House Nairobi, 154 James Gichuru Road, Lavington, thirty leaders from banking, insurance, law and technology will work through what Kenya’s Artificial Intelligence Bill would require of the AI their organisations already run. Practical feedback from the people who will have to comply.
@karennyamunbo, as the Bill’s sponsor, we would be honoured to have you in the room. Programme details: https://t.co/hs8Rto3JN4
#DrIkhaliaCyberBootcamp #DICB #AIGovernance #AI #Kenya
This week, a few people messaged me the same question: “Doc, how do I actually book for the AI Risk and Governance training?”
Fair question. So here it is, as simple as I can make it:
Go to https://t.co/hs8Rto3JN4
Click Book your seat
Your confirmation arrives straight away
That is it. Two minutes.
Saturday 31 October, 10am to 12pm, The Social House, Lavington. Thirty seats, and the room is filling.
See you there.
A customer is denied credit. They ask why, and nobody can explain the decision beyond what the system returned.
That is an AI governance problem.
On 31 October in Nairobi, we will work through real AI use cases and what organisations should do about them.
https://t.co/zLVVtZCb7U
I am running a two-hour in-person session on this in Nairobi. Saturday 31 October, 10am to 12pm, The Social House, Lavington. Bring one AI system your organisation uses; leave with a register entry and a one-page board position. 30 seats. https://t.co/wztP6HCW2R
Ask a leadership team how many AI systems the organisation uses. The first answer is usually “one or two”.
Give them five minutes and a sheet of paper. The list passes ten.
The fraud rules. The CV ranker. The chatbot. The summariser in the email client. The tools staff use because they are quicker.
The gap between the first number and the list is the governance problem. You cannot govern what you have not listed. And if the name against a system is “nobody”, that is not a gap in the exercise. It is the finding.
A green status report doesn't mean you're safe. It means work got done.
Maersk found out the hard way in 2017. Audit-approved backups, and when NotPetya hit, no way to actually restore anything.
New article on the gap between what institutions believe and what they can prove. Link below.
Read: Every Audit Is an Archaeology Project — https://t.co/HPk9hIvOAq
It draws on my position paper, The Three Problems of Cyber Regulatory Compliance, free on SSRN: https://t.co/Kxv7k04K4N
I have written about why this is a structural failure, not a documentation problem, with a one-obligation test you can run this week, stopwatch in hand.
Full article linked in the reply.
Read: Every Audit Is an Archaeology Project — https://t.co/HPk9hIvOAq
It draws on my position paper, The Three Problems of Cyber Regulatory Compliance, free on SSRN: https://t.co/Kxv7k04K4N
A regulator asks: which systems carry this obligation? Who accepted the risk? When does the exception expire?
The answer should take minutes.
In most organisations it takes three weeks. Here is why.
I have written about why this is a structural failure, not a documentation problem, with a one-obligation test you can run this week, stopwatch in hand.
Full article linked in the reply.