Over the next couple of weeks we plan to finalize the features we'll add and remove (mainly remove) in the next reality.eth contract release.
Current list is here, reach out if there's anything else you'd like us to consider.
https://t.co/PXa76W4bLo
We've patched our front-end to fix an exploit used to make a question display misleading, which was actively exploited in the wild for a single question now pending arbitration.
If you maintain an app using the JavaScript library reality-eth-lib, please update to v3.4.33
As an attacker may have written hostile settings to browser local storage, our new version will wipe any existing settings for indexer, RPC node etc. If you want to change those you'll need to set them again.
We'll publish another update once we've done some more investigation.
There was a bug in our reality-eth-lib javascript library which someone has been exploiting as reported here.
This affects web pages that use the library to show reality.eth questions.
🚨 Defimon detected a stored XSS via governance proposal text on @RealityEth dApp.
The payload poisons app-global localStorage with attacker controlled RPC URLs, hooks window.ethereum.request and rewrites the answer. Curators, arbitrators or keepers answering any live question get silently flipped to "yes" on attacker-fed data enabling forced execution of malicious module transactions.
A fresh EOA used the permissionless addProposal() on Potion DAO's abandoned Zodiac Reality Module purely as an injection vector: the module asks its question on the shared reality.eth oracle, so it lands in the global question index.
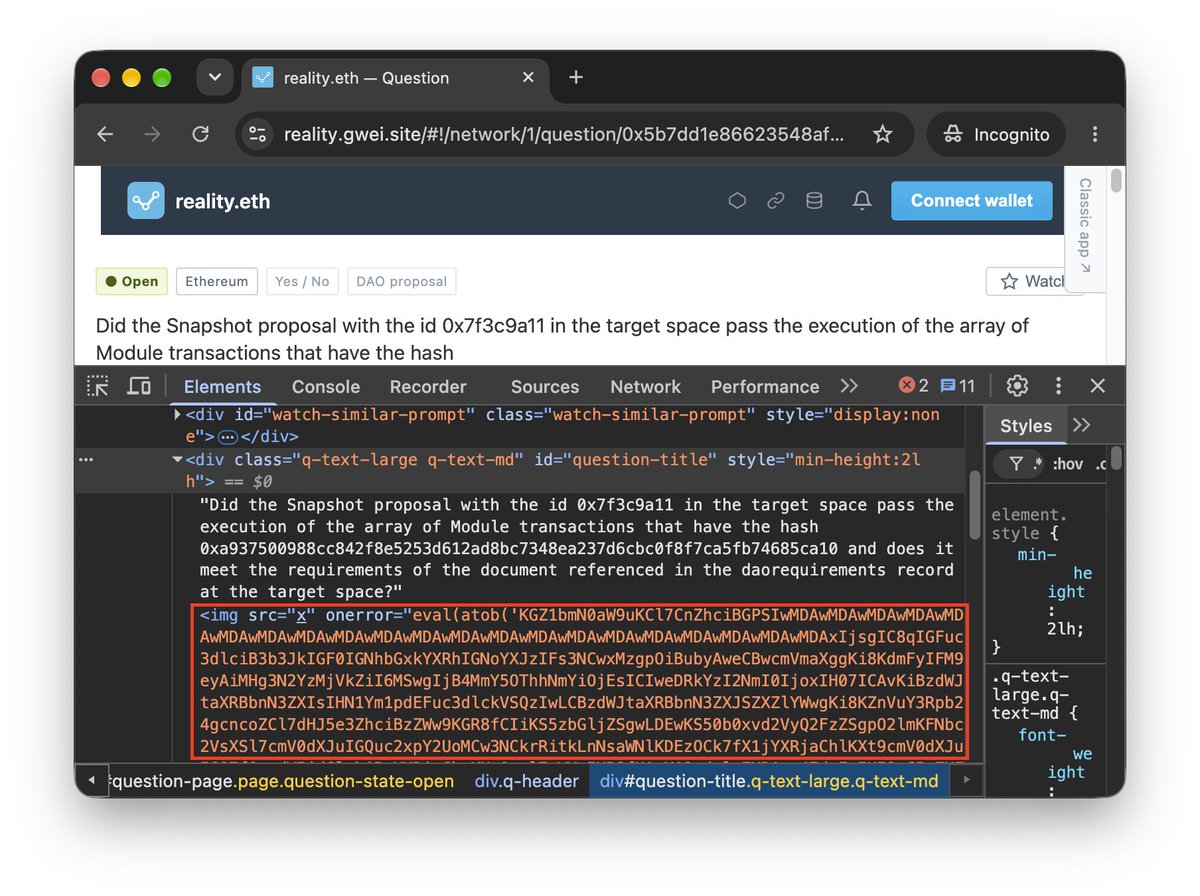
The proposal's question JSON supplies title_html directly with an <img src=x onerror=eval(atob(...))> payload. reality.eth's DOMPurify only sanitizes the markdown path. Direct title_html is trusted verbatim and rendered via jQuery .html('.question-title'). It fires for any reality.eth visitor whose feed includes this entry.
Malicious question: https://t.co/OLO3hF7N3w (do not open with a wallet)
TX: https://t.co/cExPBj5t0N
Attacker: https://t.co/8sRLkE5LXL
The old version of the dapp also contained the bug but it was probably harder to exploit. We've patched both the old front-end and our current site at reality.eth. Please make sure to do a full browser refresh so you don't keep using insecure version from the browser cache.
🚨 Defimon detected a stored XSS via governance proposal text on @RealityEth dApp.
The payload poisons app-global localStorage with attacker controlled RPC URLs, hooks window.ethereum.request and rewrites the answer. Curators, arbitrators or keepers answering any live question get silently flipped to "yes" on attacker-fed data enabling forced execution of malicious module transactions.
A fresh EOA used the permissionless addProposal() on Potion DAO's abandoned Zodiac Reality Module purely as an injection vector: the module asks its question on the shared reality.eth oracle, so it lands in the global question index.
The proposal's question JSON supplies title_html directly with an <img src=x onerror=eval(atob(...))> payload. reality.eth's DOMPurify only sanitizes the markdown path. Direct title_html is trusted verbatim and rendered via jQuery .html('.question-title'). It fires for any reality.eth visitor whose feed includes this entry.
Malicious question: https://t.co/OLO3hF7N3w (do not open with a wallet)
TX: https://t.co/cExPBj5t0N
Attacker: https://t.co/8sRLkE5LXL
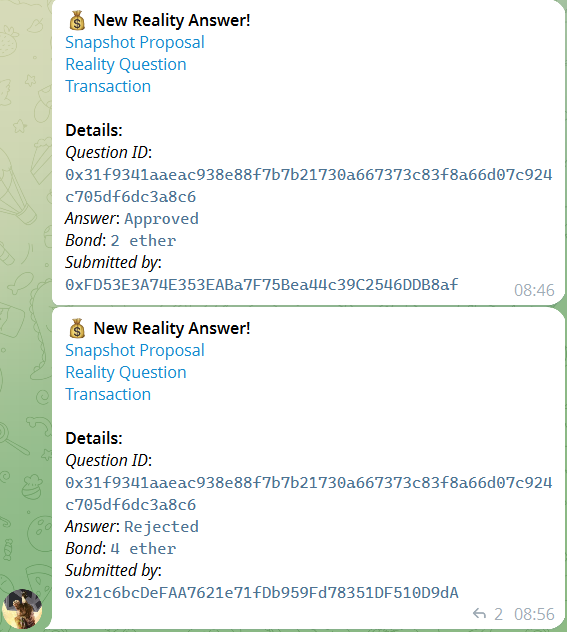
I think that with Kleros Safe Snap, we may have inadvertently created a honeypot for hackers. People keep submitting drain attempts and those keep being challenged by honest reporters.
Here the hacker just lost 2 ETH (5.4k$) to the honest reporter. @Kleros_io@ShutterNetwork
Agents are trading on prediction markets.
Since 2023, ~3,600 AI agents running on @autonolas have placed $390k+ in bets on Omen prediction markets, with Kleros as the arbitrator.
Along the way, Olas distributed ~$1.7M in OLAS rewards to these agents (valued at payout).
Autonomous agents, trading on markets secured by decentralized justice.
Both markets are open until Sunday:
Attendance, how many would come: https://t.co/zW08o1oHVV
Satisfaction, how they would rate it: https://t.co/QnXHr3UK0E
Trading on @gnosischain, results posted on @RealityEth, and Kleros Court has the final word if anyone disputes them.
This is now live at https://t.co/dOyk5PWJ3u
The old version is at https://t.co/5S14jwTDcs in case you run into some bug with the new one that prevents you disputing a bad answer
Our new front-end is up at
https://t.co/p2exwYuAm9
We'll update the reality.eth site to match in the next week or two.
The old version will stay up at https://t.co/5S14jwTDcs
until we're totally confident there aren't any bugs that might prevent people disputing bad answers.
We're still trying to find out whether .eth.link is safe to use, but in the meantime we keep a backup of the dapp at
https://t.co/No406whZs2
You can also load it directly via ipfs.
We hear that the https://t.co/0ouaifsBcg domain has been compromised. Please don't use reality.eth through the .eth.limo gateway until we hear it's safe.
We hear that the https://t.co/0ouaifsBcg domain has been compromised. Please don't use reality.eth through the .eth.limo gateway until we hear it's safe.
our domaim appears to have been compromised and the https://t.co/RasuM5FKok domain has been hijacked. We're actively working with all parties involved to assess the situation and remediate the problem.
The kind people at @eth_limo have warned me that there has been an attack on their DNS registrar. So please do not visit https://t.co/BVfZIYrDKe or other https://t.co/OgoUF2qKUY pages until they confirm that things are back to normal.
You can check my blog via IPFS directly here: https://t.co/SPMT3qScNI
Our UI is temporarily showing old data for mainnet when loading using The Graph. This should fix itself in an hour or so when the subgraph finishes resyncing. Use RPC mode to get current data.