Find your coordinating CSIRT in ENISA’s newly published list, and use the CRA Readiness Pack to prepare your reporting chain: https://t.co/nTQ9YDUC5v #CyberResilienceAct
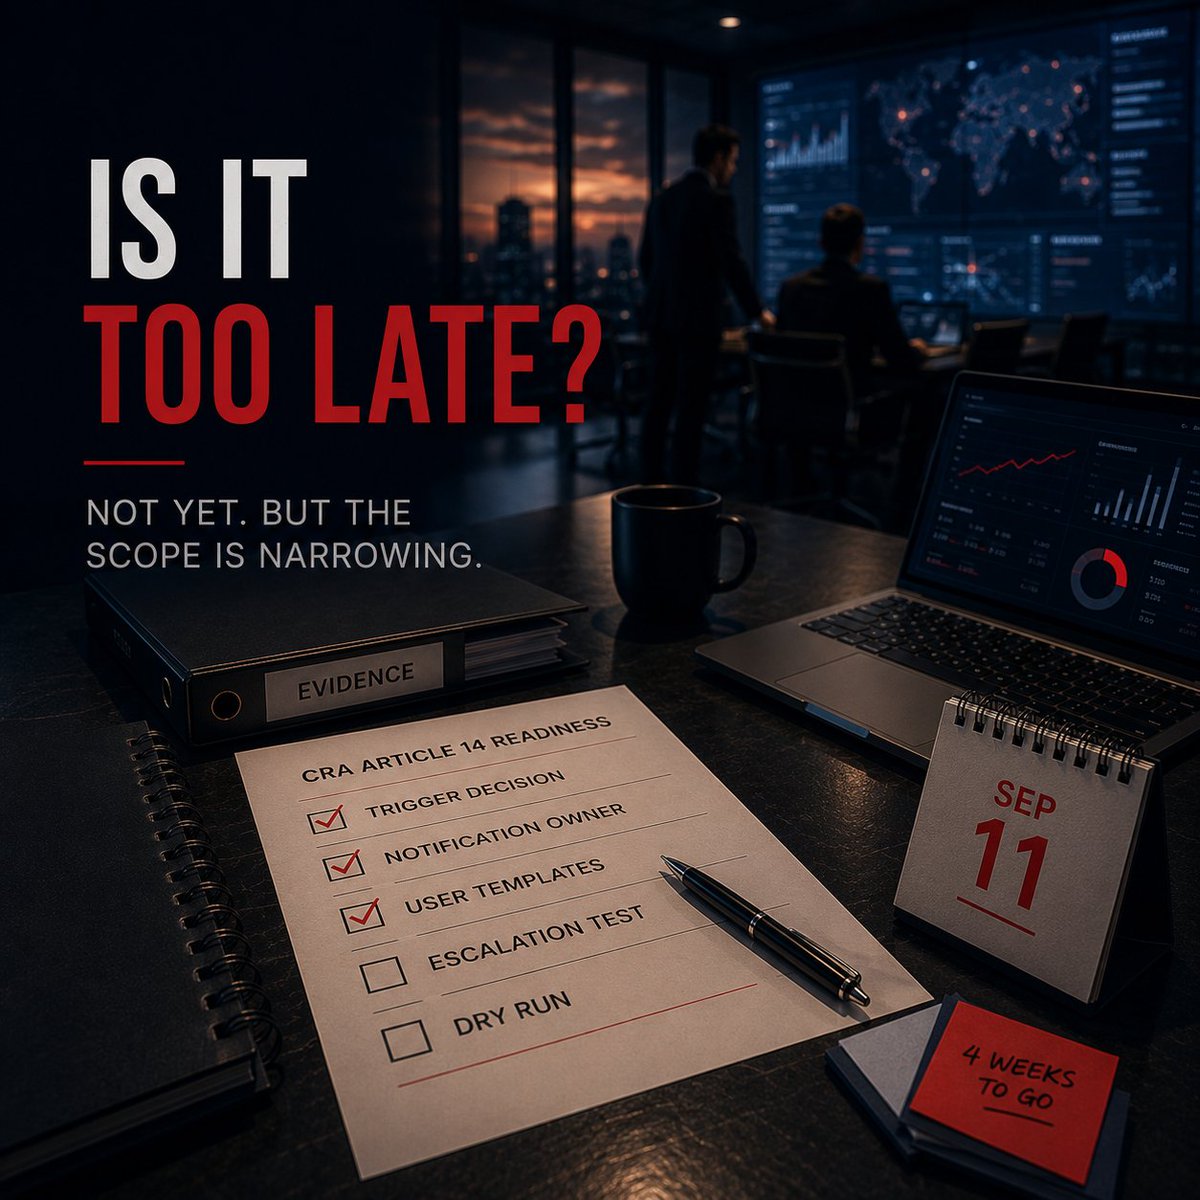
"Is it too late?" The question we hear most in August. Honest answer: no. But what a four-week sprint can deliver narrows every week.
What is still achievable before September 11, and what is not: https://t.co/Z9WCI1EF9B
Article 14 does not test your monitoring capability. It tests your decision capability under a clock.
Strong CVE feeds, two-day triage: the pattern our Technical Lead sees most in CRA readiness work.
He explains in 16 min: https://t.co/D7WRzKzIRo
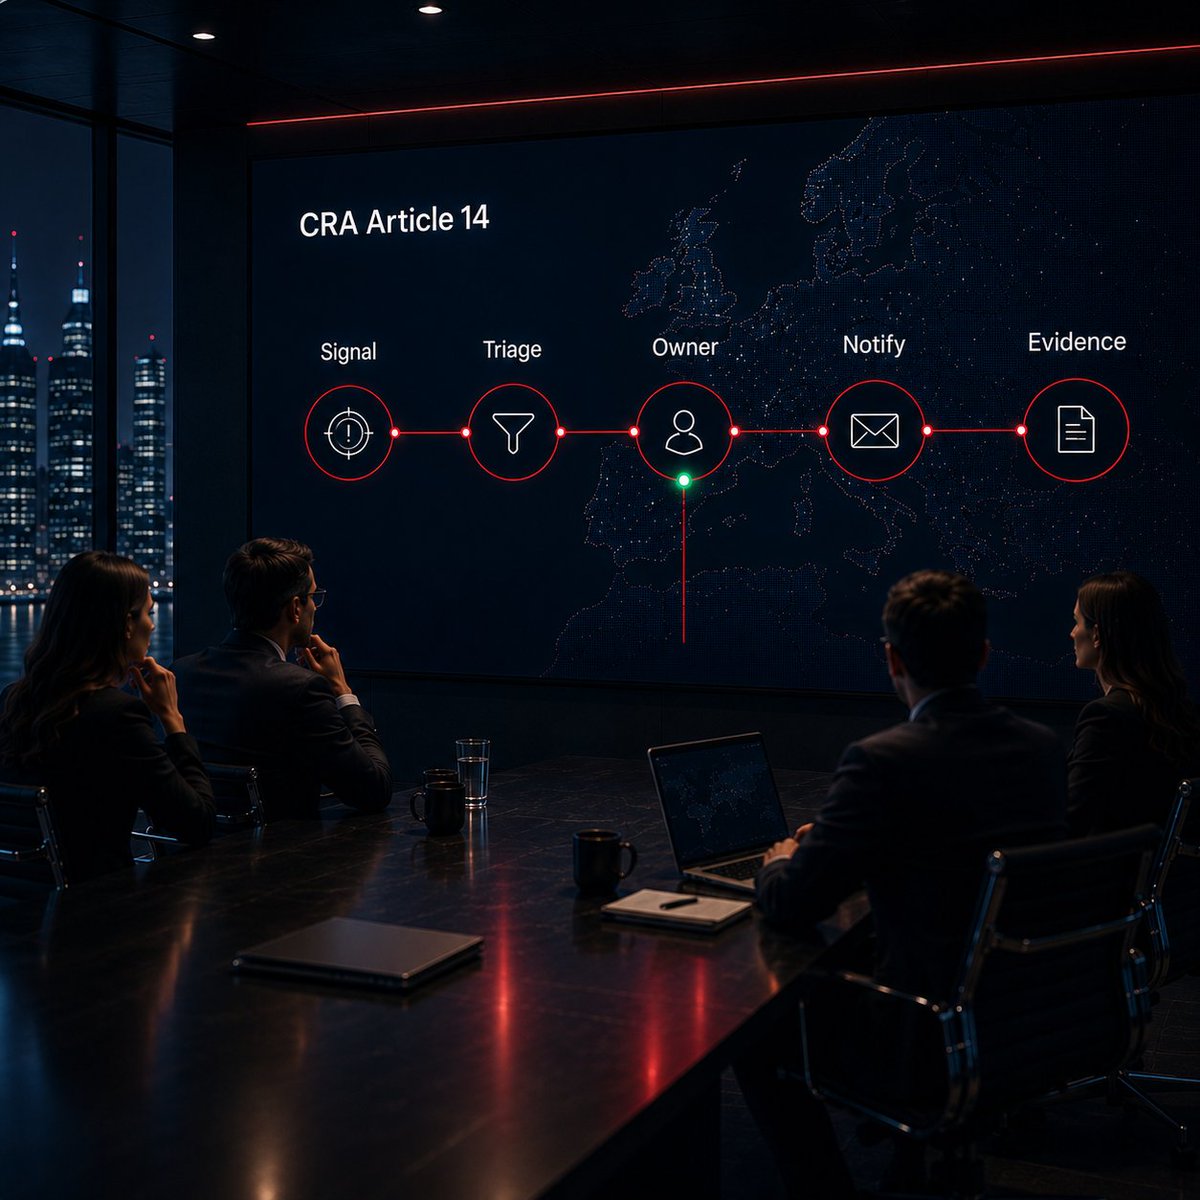
What does "ready for September 11" actually look like under CRA Article 14?
Not a policy on a shared drive. A tested intake, triage in hours, a named owner, an evidence trail, comms templates ready to send.
Isaac walks through it in 16 min: https://t.co/9J6QvbLnDw
The Reality Filter.
Why the CRA's "Becoming Aware" Clause Isn't a Get-Out-of-Jail-Free Card.
By Isaac Dangana, Technical Lead, Red Alert Labs
Our latest blog post: https://t.co/9KGMai8yM6
Vulnerability handling under the CRA is not about finding more bugs, but about what happens the moment one is reported. If a credible report landed on your flagship product this afternoon, who owns the first two hours?
We publish practical guidance on Article 14
#CRA
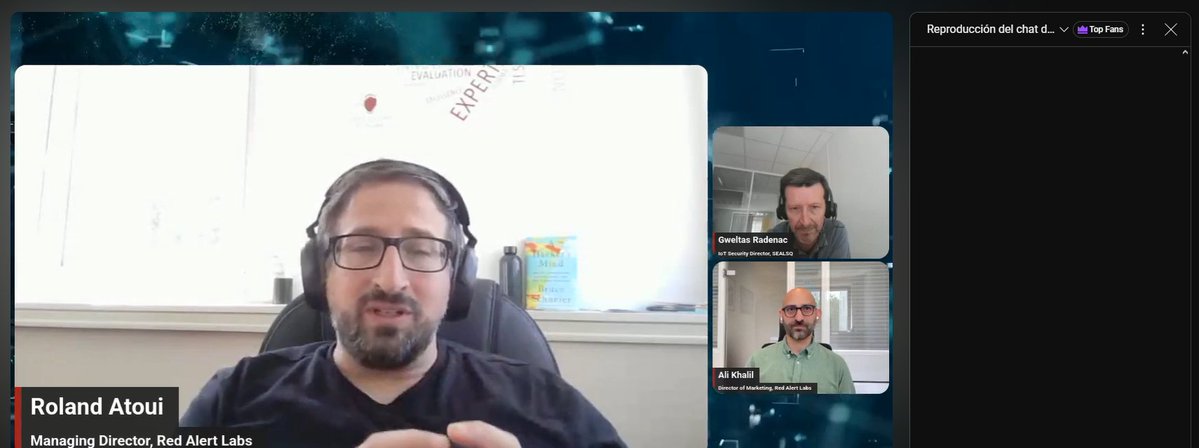
🎥#TELEMETRY_eu | Interview with Mr. Roland Atoui 🎙️
@Roritto, Managing Director of @RedAlertLabs, shares a new take on cybersecurity compliance with scoring & continuous monitoring to secure smart systems across their lifecycle.
https://t.co/lszbwBZFoM
@TheAirInstitute@certify_project Thank you for joining us! We're thrilled to have had the opportunity to discuss the RED Directive with you. If you have any further questions or need more information, feel free to reach out!
@FabAIQuantum@SEALSQcorp Thank you for highlighting the importance of cybersecurity compliance! At Red Alert Labs, we're committed to helping organizations stay ahead with robust security solutions.
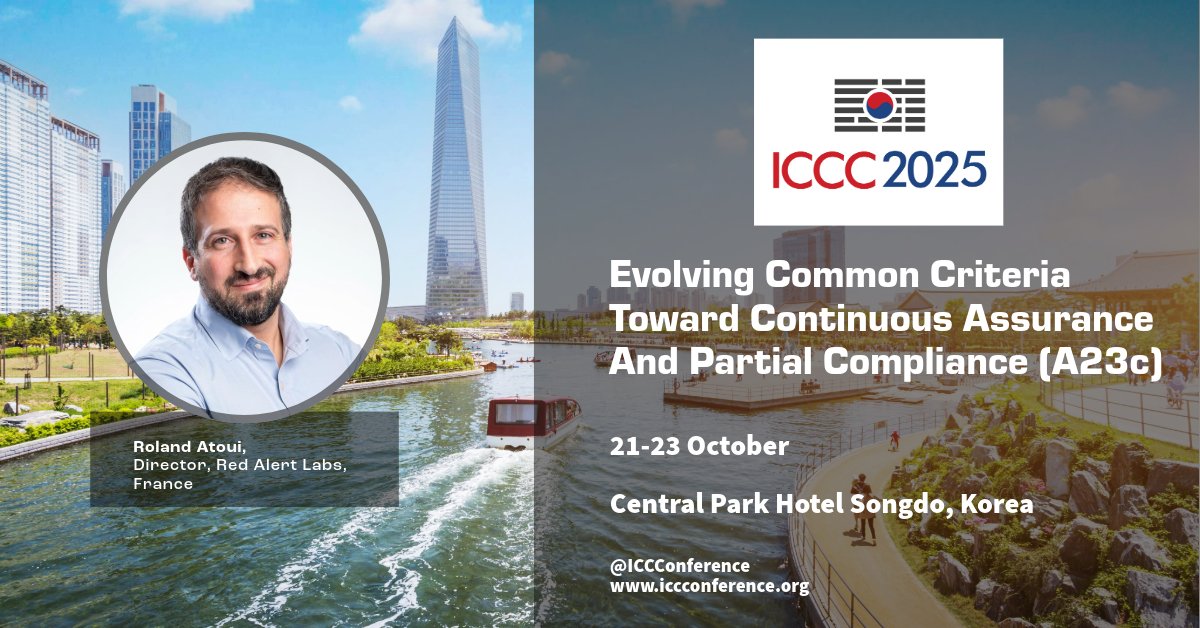
@ICCConference Thank you for the warm welcome! We're excited to have Roland Atoui share insights on advancing Common Criteria at ICCC 2025. Looking forward to an engaging session!
🎯Participamos en el webinar “RED Directive D-Day: From Prepare to Prove It!” organizado por nuestro socio @RedAlertLabs en el marco de @certify_project, donde se abordaron aspectos clave para cumplir con la Directiva RED, vigente a partir del 1 de agosto.
https://t.co/Hk0miPkUUm
💣⏲️The countdown is on !!
August 1, 2025 - the day the RED Directive cybersecurity requirements become enforceable.
Are you ready?
➡️Webinar: D-Day for RED Cybersecurity — Are You Compliant?
➡️Date: July 31, 2025 at 11:30 AM (CET)
Register now: https://t.co/umcpHSsAgt
🚨 Aug 1 = RED Directive enforcement day.
Still not ready?
🛡️ Join our expert webinar:
D-Day for RED Cybersecurity
📅 July 31, 11:30AM CET
🎙️ w/ @SEALSQcorp , @RedAlertLabs
👉🏻https://t.co/PHzwpCEUqn
🔍 Facts of ENTRUST – Featuring @RedAlertLabs ! 🛡️
Through their expertise, @RedAlertLabs is helping EnTrust Project build a reliable foundation for safer and more trustworthy digital healthcare.
🚨 Keynote Speaker Alert!
We’re excited to welcome Roland Atoui, Managing Director of Red Alert Labs, as the Keynote Speaker at the LIFESEC Workshop, part of IEEE SmartComp 2025!
More info 🔗 https://t.co/HXe1AhbAnc
#Telemetry_eu#SmartComp2025#Cybersecurity