Don’t normally post about non-tech stuff but couldn’t help but share an awesome experience.
I recently had the opportunity to view The Odyssey (totally recommend watching it) in a different light while in the company of a mastermind of all things Homer. Doing so helped me learn so much about the central themes and how they influenced each character's decisions throughout the story.
I wanted to share a link to his superb, detailed work on this subject in case anyone is interested!
https://t.co/5hFVokqvWC
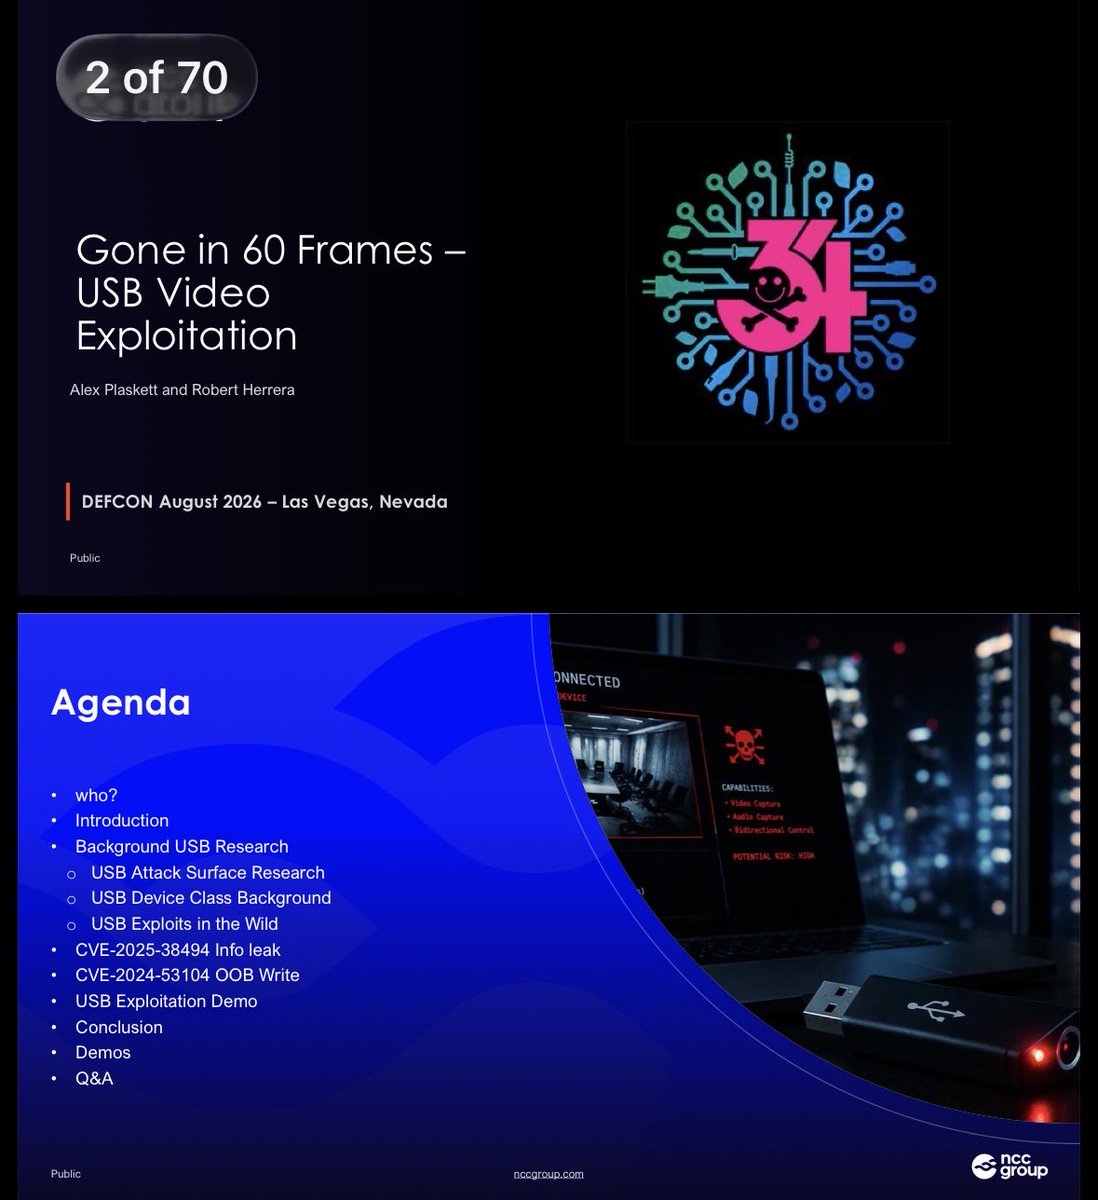
Slides and whitepaper of Gone in 60 Frames – USB Video Exploitation by @robHerrera_ and myself seem to be on the #defcon34 media server now!
Slides - https://t.co/AOkjWdO4vP
Whitepaper - https://t.co/CZ81C7TD8W
Looking forward to Sunday! Very humbling to be back at @DEFCON after a few years, and even more pumped to be giving my first DEFCON talk alongside @alexjplaskett!
Day 1 of @offensive_con
My team at NCC, exploit development group is recruiting an experienced researcher! If you’re looking for a new role and here feel free to reach out.
An analysis of CVE-2026-21236 - A heap based buffer overflow in the Microsoft Windows Kernel afd.sys - was just published by @ASN_Sinanju_06S a recent secondment with my team EDG!
Nice work for her first triage of a kernel memory corruption bug!
https://t.co/3QEM557kIC
What does it take to exploit Linux Kernel USB vulnerabilities against a modern Linux version? Learn more with @robHerrera_ and @alexjplaskett in their talk "Exploiting USB on a Tesla IVI".
Secure your ticket: https://t.co/CSVM5Ym0j5
#Infosec#INSO26#CyberConference
🏠🔓 Is your alarm system truly safe? #PowerG is used everywhere, but its secrets were locked tight—until now.
James Chambers and Sultan Qasim Khan reverse engineered the protocol, found a major flaw, and they’re sharing the results at #hw_ioUSA202
👉https://t.co/yj0ayMtbTu
Anybody fairly familiar with modifying or augmenting QEMU (specfically Avatar-QEMU) please DM me :) I'm trying to add onto it and failing miserably thus far and have a lot of questions.
My team EDG is looking for an experienced exploit developer! RT's welcome!
This is a full time research and development role, primarily contributing to the developing of capabilities for consultants, showcasing knowledge, collab with other teams etc.
https://t.co/YyayDlF1Te