The "Experience Paradox" has forever been a nightmare in this Industry.
I've been in infosec since around half a decade now. And I speak to a lot of friends, hackers, students, and bug hunters every month. The story is more or less always the same, even after all these years:
- Pulling all nighters to Grinds CTFs & Labs.
- Save up cash to buy "Industry Standard" Certs.
- Learn the tools, the scripts, and the syntax. Thanks to AI, barely even Syntax anymore.
And then you apply for a "Junior/Fresher" role.
And: Rejected. Worse, no callback or no one even reached back out to you.
With the reason: "Not enough real-world experience."
But you can't get experience without the job. And you can't get the job without experience.
Even I started my Career with CTFs, and bookmarking every random #bugbountytip, gathering courses and what not. And I've been there in there in this loop.
So you go back to the Labs. You solve more boxes. You hack more "intended solutions." You get better at the Game, but you aren't getting closer to the Job.
Why?
Because the Managers & Leads knows CTFs aren't reality. And they've learnt that the hard way, by making mis-hires.
CTFs are great for clearing concepts. But in a CTF, there is a flag. There is a solution. The puzzle was designed to be solved. In Production? It’s messy. It’s boring. It’s undocumented. There are no flags. There is only broken Logic and Business Risk. And 2 out of 2000 things might* be broken.
The gap between "Top 1% on a Platform" and "Useful in a SOC/VAPT" is massive. And right now, there is no bridge.
We built @BarracksArmy to burn that bridge and build a ramp.
We're brining the WarGames to #IdentityShield by @miniOrange_Inc this week.
Real infrastructure.
Zero hints. Zero flags.
We don't care about your certs or years of experience. We care about your Mindset. And so should the Infosec Industry from a Hiring perspective.
Are you a Tactician (Coverage & Consistency)? Or are you a Strategist (Novelty & Impact)?
If you are stuck in the loop - tired of labs, tired of rejections, and ready to prove you can handle the chaos of production, don't just join the WarGames (need to be present at the Summit). Come find me - We have a booth in the WarGames area. I would love to know more about you and try to better understand the problems you are facing.
Let’s get you out of the loop and get you a taste of Reality.
If you're a Founder, Hiring Manager, or a someone managing an Infosec team, I'd love to connect, hear your views and talk about de-risking current Infosec Hiring.
And we also just might* have something for everyone as well😉
#Infosec #BugBounty #Hiring #CyberSecurity #Barracks
Don’t let anyone convince you cybersecurity is dead or that AI makes it impossible to break into the field.
I built my own hackbot, and I use AI for bug bounty and penetration testing.
It’s great for checking for common vulnerabilities like XSS, SQLi, SSRF, and IDOR. But trust me, AI still struggles to chain bugs and find complex business logic flaws that take real creativity.
So keep learning the basics. Practice until you can spot when AI misses something or gets it wrong. The better you understand how an app works, the more you’ll get out of AI competition:)
Remember, AI is just a tool. Your judgment and creativity is what makes it useful.
And u will never get to the level of creativity if u r not good enough, and 100% depending on AI
My 1st Giveaway 😎
70% OFF on https://t.co/SOHpSTztJ2
This is the max one can get so don't miss it.
Like, Repost and Comment 1 thing you like about #AI to enter
AI will pick the 🏆
#Giveaway
Anyone claiming they have a 100% automated “hackbot” that can breach any app with zero human touch is wrong, at least most of the time.
Every app is different.
Different stack, different logic, different weak points.
You still need creativity + experience to invent fresh attack paths.
A hackbot can handle ~80% of the grunt work.
But you still have to:
• Tune the tools
• Know what you’re actually looking for
• Keep your skills sharp
Keep hacking 👍
Elliot Alderson’s private chat allegedly leaked, and the internet has questions.
Plot twist: He didn’t know about Barracks.💀 Meanwhile, people are sharing they think of Barracks immediately when the conversation turns to practising real-world bug bounty hunting.
Elliot Alderson’s private chat allegedly leaked, and the internet has questions.
Plot twist: He didn’t know about Barracks.💀 Meanwhile, people are sharing they think of Barracks immediately when the conversation turns to practising real-world bug bounty hunting.
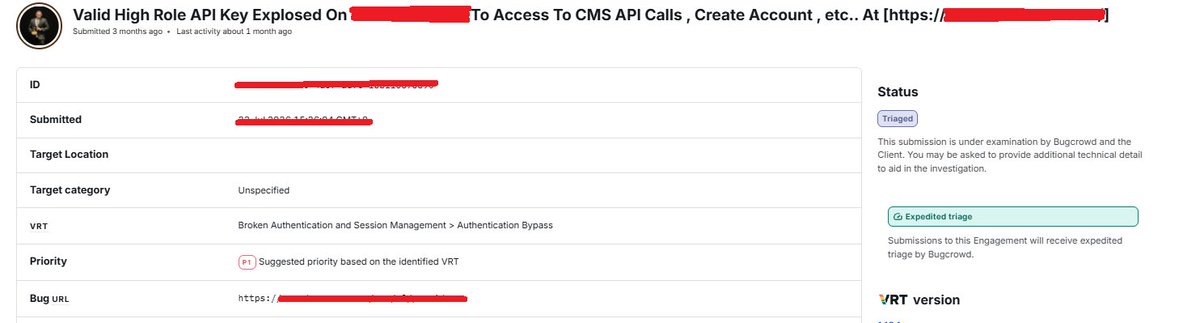
A Google API key is not always just a Low or Informational finding.
The Story of Submitting some P1s in the last months by the same method
Sometimes the real impact is in what you can do with it.
For example, with Firebase / Google Identity Toolkit, a leaked key may allow account creation directly through the API:
curl -sk -X POST \
"https://t.co/9AFMREgczk" \
-H "Content-Type: application/json" \
-d '{"email":"[email protected]","password":"Test12345!","returnSecureToken":true}'
Now imagine the application trusts users based on the email domain and does not properly verify ownership.
In that case, you may be able to create an account using an organization email, receive a valid auth token, and access parts of the application that were supposed to be limited to internal users.
At that point, this is no longer about an "exposed Google API key".
The impact can become unauthorized registration, authentication bypass, internal access, sensitive data exposure, or even full access to the application depending on how the backend handles authorization.
So before marking a Google API key as Low, always check what the key actually allows you to do.
The key itself may be Low. The impact behind it may not be.
#bugbountytips #bugbountytip #infosec #Bugbounty
How do you test how powerful an AI testing tool is?
@0xTib3rius built his own target: a bespoke vulnerable app, source code never published, with three known, tricky paths to RCE. Then he tried Burp AT.
Burp AT found a fourth within minutes.
#BurpAT
Happy to share that my novel research spraying using AI has hit $50,421 in total bounties! 🤯 Automated using a multi-gated system from discovery to report drafting.
Stats to-date:
Reports rewarded: 126
Highest single bounty: $2,500
Lowest bounty: Swag
50 reports are still in new/ppr, and more are coming
The benefit of brainstorming original research is that I received 0 dupes, unlike well-known web bug (sub)classes that AI knows well. Fun fact: given the requirements, this research wouldn't have been feasible without LLM reasoning at all: too much unexpected stuff you need to adapt to and otherwise needs thousands of ifs/elses.
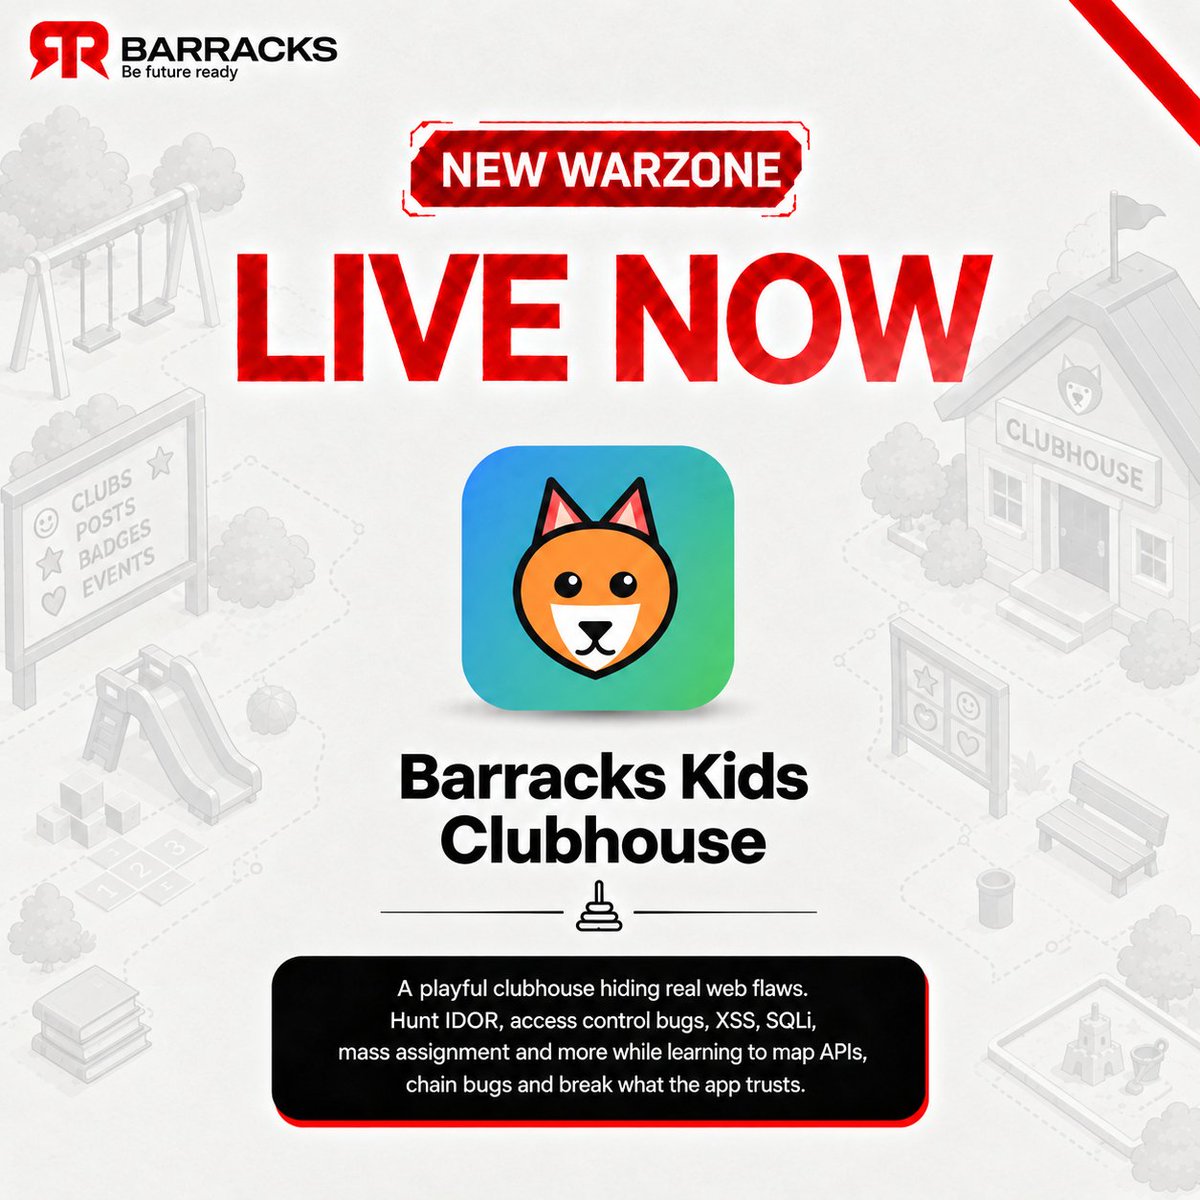
New WarZone - Barracks Kids Clubhouse🐥
A fun little world with clubs, posts, comments, art, profiles and plenty of things to explore with a few security problems hiding underneath.
Time to see what's really happening inside the clubhouse.
#barracks#warzone
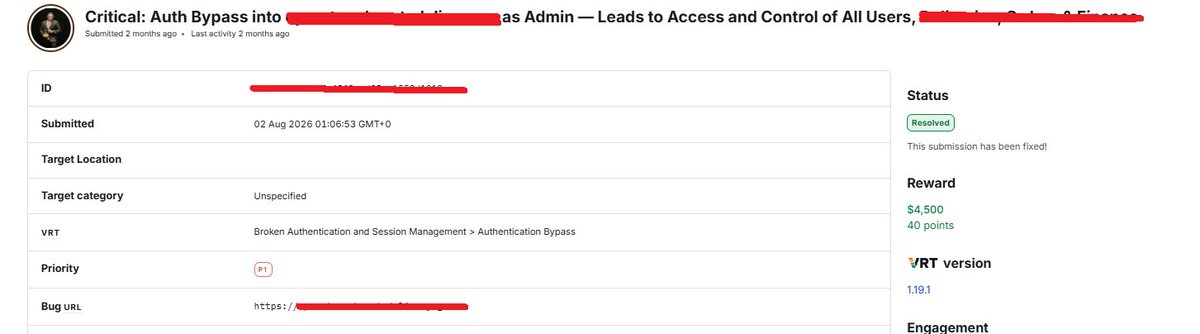
one of my favorite bug types was also found in Google, this was quite interesting, Google awarded a bounty even though they'd patched the bug before reviewing it :]







![YShahinzadeh's tweet photo. one of my favorite bug types was also found in Google, this was quite interesting, Google awarded a bounty even though they'd patched the bug before reviewing it :] https://t.co/h4xADGxne4](https://pbs.twimg.com/media/HT4serXWwAA8brp.png)








![YShahinzadeh's tweet photo. one of my favorite bug types was also found in Google, this was quite interesting, Google awarded a bounty even though they'd patched the bug before reviewing it :] https://t.co/h4xADGxne4](https://pbs.twimg.com/media/HT4serrXoAEBOVB.png)


