What can public information reveal about an organization's attack surface before a security assessment?
Join us at #OSINTSummit to explore reconnaissance, potential exposures & practical OSINT techniques.
🗓️ Feb. 1–2 | Alexandria, VA
➡️ https://t.co/gjOYDL8Qtl
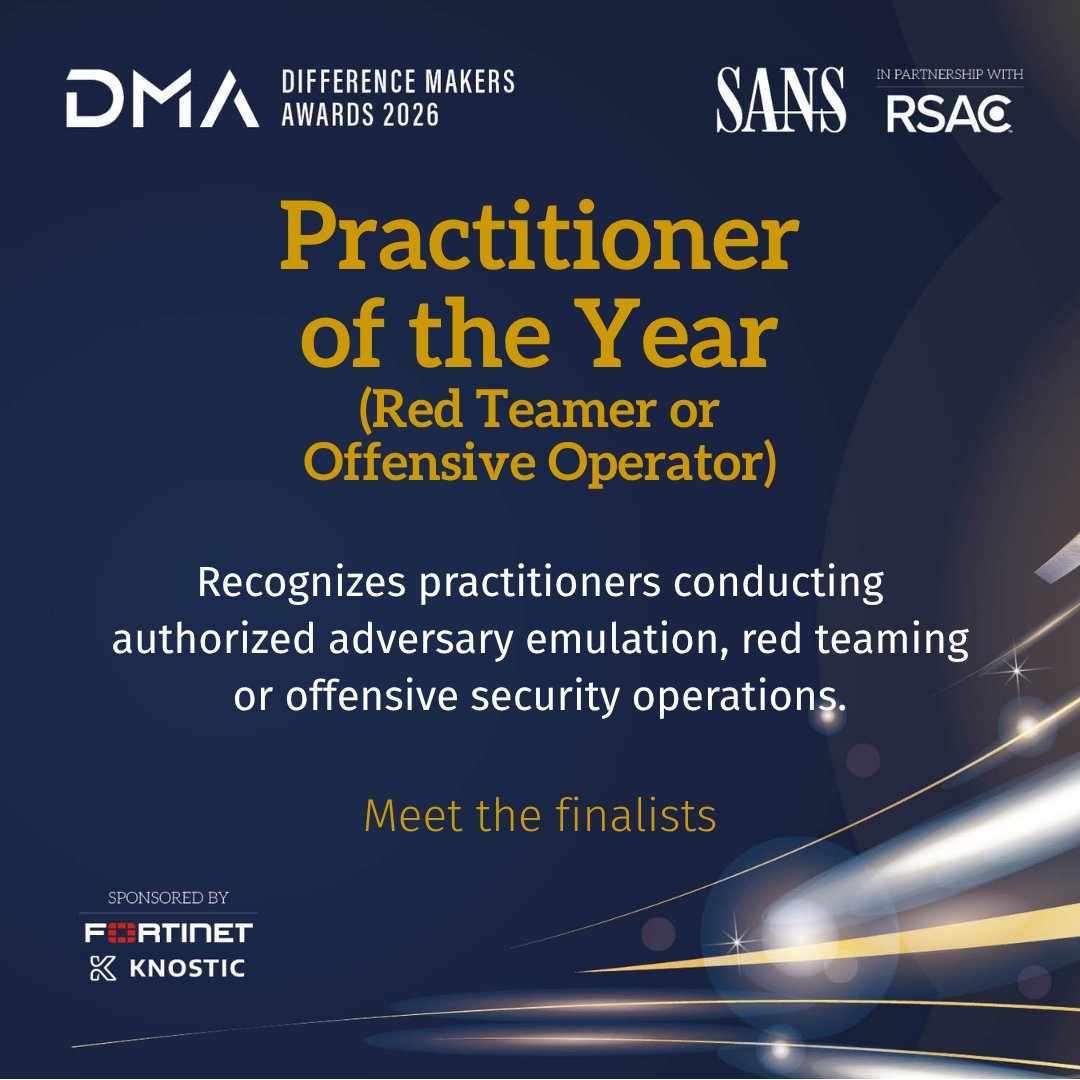
Congratulations to the Practitioner of the Year, Red Teamer, or Offensive Operator finalists:
David Bérard | Lachlan Davidson | Yara AlHumaidan | James Kettle | Sina Kheirkhah
Vote for the community's choice by Nov 9.
Cast your vote: https://t.co/McgbeiO0F7
Here a tap, there a tap, everywhere a tap-tap. 🎶 But can that office badge, hotel key, or any smart card be copied or impersonated? #SEC617 teaches practitioners to assess contactless cards through cloning and emulation techniques.
💳 Preview: https://t.co/SfYsDGOwDU
Excited for #UnpromptedII! Catch @dmay3r from @neuvik leading a @SANSOffensive Workshop on using AI to deliver C# payloads in constrained environments. Don’t miss this cutting-edge session tomorrow. #AI#Cybersecurity
https://t.co/PCkCBbs2O0
David Mayer will walk through how to set up and configure redirectors for Red Team operations while examining the decisions that shape traffic flow, backend exposure, and operational resilience.
📅 Nov 10 | 11:00 AM ET
🔗 https://t.co/hoFUvC0xfz
An AI assistant might have legitimate access to sensitive company data. But what happens when an attacker plants malicious instructions in a document the assistant is about to read?
SEC536 teaches practitioners to test attack paths and reduce exposure.
🦾 https://t.co/M2DAyxvbwp
Eight categories, and your vote picks the community's choice in each.
The 2026 SANS Difference Makers Awards celebrate practitioners, projects, and organizations. Which category do you know best? Voting closes Nov 9.
Cast your vote: https://t.co/cGDIfSaPMr
The way attackers get in has shifted, and credential theft is no longer leading the pack.
Phishing and exploited vulnerabilities are closing the gap fast, and most defensive strategies haven’t caught up yet.
What’s the #1 way in today?
📺 Now OnDemand: IoT and Wireless Penetration Testing: What’s New in SEC556 and SEC617.
Watch James Leyte-Vidal and Larry Pesce compare the two courses and cover new AI-assisted workflows, hardware kits, labs, and platform support.
🔗 https://t.co/XVt7VsiiPI
Not every redirector strategy fits every operation.
This session compares different approaches, where they fit within an engagement, and the operational tradeoffs Red Teams should consider when designing more resilient C2 infrastructure.
🔗 https://t.co/hoFUvC0xfz
🚨 LIVE in 1 hour.
See what’s new in SEC556 and SEC617, including AI-assisted analysis, updated labs, revised hardware kits, and the testing targets that separate IoT from wireless penetration testing.
📅 Oct 20 | 12:00 PM ET
🔗 https://t.co/XVt7VsiiPI
Tomorrow: IoT or wireless? Know the difference.
James Leyte-Vidal and Larry Pesce will compare SEC556 and SEC617 while covering new labs, AI-assisted workflows, hardware kits, and host-platform support.
🔗 https://t.co/XVt7VsiiPI
💜 🗞️ In this episode of The Weekly #PurpleTeam, @BRIPWN covers DLL sideloading using an Adaptix Beacon payload hidden inside python315.dll, a technique attackers use to execute malicious code under the cover of a legitimate, signed process.
👉️ https://t.co/S8gz8pnncH
Connected devices demand a different testing approach than wireless environments. James Leyte-Vidal and Larry Pesce will break down where SEC556 and SEC617 differ so practitioners can match the training to their targets and responsibilities.
🔗 https://t.co/XVt7VsiiPI
Attackers are abusing vulnerable Windows kernel drivers to disable EDR, while #Microsoft is tightening driver security.
SEC665 teaches #RedTeam operators to investigate kernel internals and understand how security products monitor activity.
💻️ https://t.co/DLcTuYFHjQ
Your C2 server should not be so easy to find.
David Mayer will show how redirectors add separation between operators and backend infrastructure, helping Red Teams control how traffic reaches C2 while reducing unnecessary exposure.
🔗 https://t.co/hoFUvC0xfz
Give an AI agent a codebase, and you'll get answers.
Give it the right context, tools, and constraints, and you'll get something worth investigating.
#SEC543 teaches you how to configure and guide AI coding agents for penetration testing.
Learn more: https://t.co/tGSmDdBCaP
#SEC660 now incorporates AI into exploit research, vulnerability analysis, scripting, and bug discovery while preserving the technical depth needed to validate findings and understand what actually works.
🐍 Watch “Exploiting the Network” here: https://t.co/NFOYwIcHv1