New from the Tradecraft Academy 👇
Built in partnership w/ @OpenAI through OpenAI Daybreak Defense Network, Adversary Intelligence: LLM Tradecraft provides hands-on training to build, evaluate, attack, & defend LLM & agentic systems.
More from @harmj0y: https://t.co/zSqdrUX4rx
This is your sign to reserve your spot for @MGrafnetter's webinar this week!✨
Hear about Pass-the-Passkey, a novel & actively researched category of malware-initiated attack techniques targeting passkey auth that can enable cloud user impersonation.
�� https://t.co/NNXkvbBqcp
Introducing SpecterOps Skills: a public repository built to turn practitioner knowledge into reusable, reviewable workflows for AI-assisted security work.
@zinic shares what we're building, why we're building it, and how you can contribute ➡️ https://t.co/bZAkCFRSlg
ICYMI: @_wald0, @harmj0y & @CptJesus joined #KnowYourAdversary to take a look back at 10 years of BloodHound!
Tune in & hear about how BloodHound has evolved in the years since it was first unveiled at #DEFCON in 2016.
Listen to both parts ➡️ https://t.co/fTqqveeCoX
BloodHound is 10 🎉
To celebrate, creators @_wald0, @CptJesus & @harmj0y joined for a special two-part #KnowYourAdversary.
They reminisce on the first attack graphs and look ahead to what’s next for BloodHound.
1️⃣: https://t.co/eLDBpNRRt7
2️⃣: https://t.co/aAh6wphQzu
We're back with a new #BloodHoundBasics post from @SadProcessor!
Ready to take your #BloodHound skills to the next level?
Head over to the SpecterOps Tradecraft Academy and dive into our free BloodHound Basics Workshop.
(1/4)
There's still time to save your spot!
Join us TONIGHT at @BBowlVegas for a night of bowling, food, drinks, & conversation after the #BHUSA floor closes.
🎳 Register: https://t.co/mtNdZTL7w7
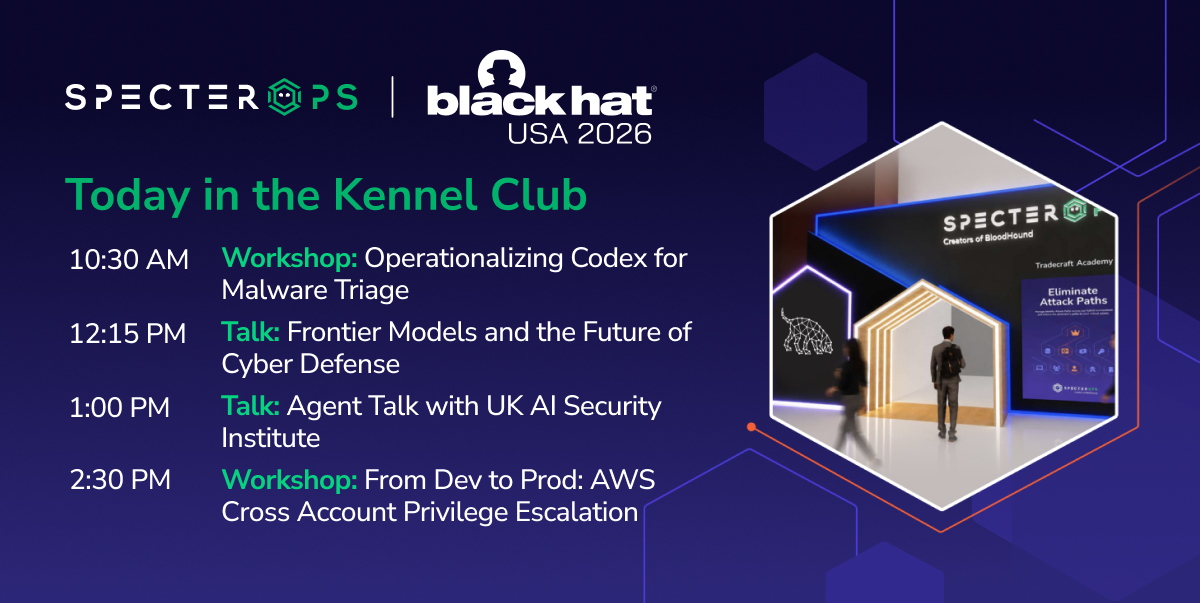
Good morning! Today at the Kennel Club! ⤵️
Stop by during #BHUSA to hear from SpecterOps researchers, as well as guests from @AISecurityInst and @OpenAI.
Learn more about the sessions: https://t.co/TJuAHp8ocD
Curious about BloodHound OpenGraph? @SadProcessor is running a crash course where you'll design your own data model and build an extension from scratch. Bring your laptop with BloodHound CE installed and get building. 💻
Have an idea for a BloodHound OpenGraph collector? Bring it to the Kennel Club!
@ScoubiMtl & @SadProcessor will intro OpenGraph, walk through a hands-on lab, answer your questions, and help you start bringing your idea into the graph.
Reserve a spot: https://t.co/TJuAHp8ocD
Come for the bowling. 🎳
Stay for the conversations. 🗣️
Join us for food, drinks, and a fun night with the security community at @BBowlVegas during #BHUSA.
🎟️: https://t.co/7LyzLfuEgY
LLM security and jailbreak testing gets messy fast.
I built Jailbreaker to make it easier to run and track jailbreak, prompt injection, and agent behavior tests.
Blog - https://t.co/kHftVWagBh
Github - https://t.co/ZgDwXq0hdM
Would love to hear what you think.
@SpecterOps
GitHub isn’t just a code platform anymore. It’s a security boundary.
New from @jaredcatkinson: how GitHub creates real attack paths into repos, secrets, CI/CD, and even cloud environments.
Read more: https://t.co/E8sLYPmEKL
Just in time for the holidays, I wanted to share something that a lot of people have asked for: https://t.co/DfXyf2TTBp
Short videos about Mythic development and customizations. This is just the start - I'll release a survey soon that'll get feedback for the next batch :)
In this post @_wald0 introduces PingOneHound, a BloodHound OpenGraph extension that allows users to visualize, audit, and remediate attack paths in their PingOne environment. The blog post also serves as an introduction to the PingOne architecture.
https://t.co/BjD5DPiih1
@bill_e_ghote@SpecterOps More feature will be added in the future, but this is already available in BHE and BHCE.
Everything covered in this post should work in both version of BloodHound 👍