@ajxchapman@joaxcar I'm curious about what the original use case or ultimate goal here was. Because for anything involving client-side decryption, there's often a more agile solution using existing or custom Burp extensions. It's pretty cool playing with the DOM that way but it could be troublesome.
@InsiderPhD Idk! An organization having a private event where they can invite whoever they wish. The fact that some are feeling entitled to it is just beyond me! It's kinda similar to feeling entitled to an invitation to someone's birthday party smh
@irsdl It is quite common. It comes down to companies' objective behind launching a bb program. A lot of programs follow the mindset of "if you can't do it, a malicious attacker can't do it either". If that's really in line with their objective, I usually don't mind it.
@infosec_au I'm recently falling in love with reviewing Java code. From Spring to Struts, it's been a wild ride. Had some success with less known frameworks and ERP applications, will be moving to more popular stuff next. Could use some suggestions actually, I'd be happy to collaborate too!
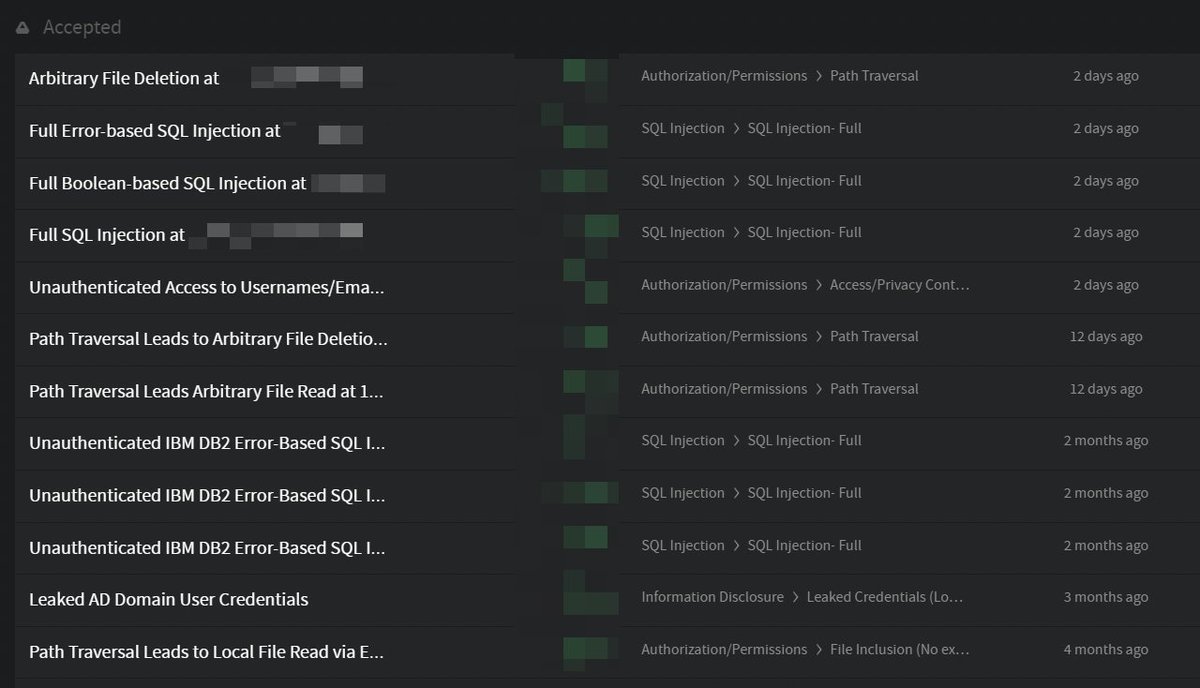
Finally having some time (or will?) for bug hunting again! Had a decent Q1 on the @SynackRedTeam
Anything that isn't an SQLi was stumbled upon while hunting for SQLi. Also almost all are CVE applicable "0days", but products aren't so widely used. Who's got time for CVEs anyways