Really cool development on the @fuel_network the native Fuel token is now bridged via @hyperlane , and the entire integration is secured by @Safe_Edges 🤝
Fuel Expansion.
@Fuel_Network's native token FUEL is now live on Binance Alpha, with the official bridge powered by Hyperlane.
Bridge Here ⏩ https://t.co/vMHpaqMBYV
🚀 Safe Edges is heading to @EFDevcon Mumbai
Let's catch up from November 3–7.
Looking forward to connecting with builders, founders, and the Web3 community.
See you in Mumbai! 🤝
🎁 50 USDT Giveaway! Join https://t.co/iutiRTwD84 AMA today & Win! 🚀
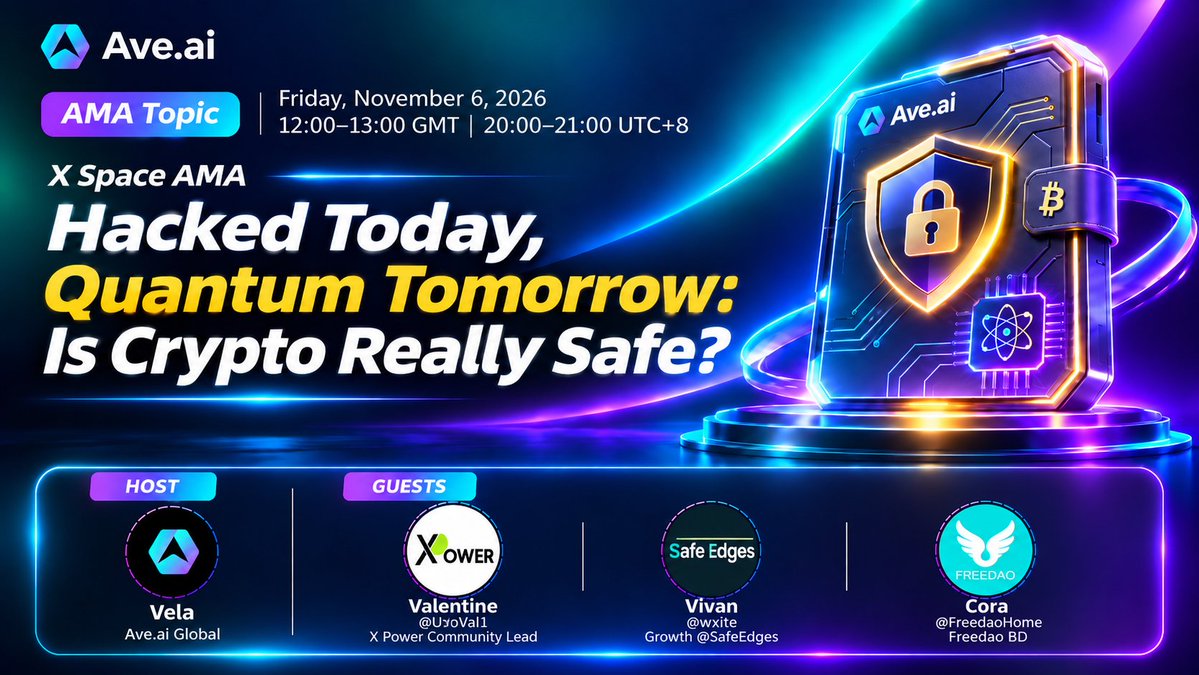
🎙️ Hacked Today, Quantum Tomorrow: Is Crypto Really Safe?
From recent crypto hacks and phishing attacks to the looming threat of Q-Day, is your crypto really as safe as you think? 🔐
Let’s talk about what puts your bags at risk — and how to protect them.
⏰ Nov 6 | 12:00–13:00 GMT (20:00–21:00 UTC+8)
🎤 Our Guests:
→ Valentine @UdoVal1 — @XPowerFinance Community Lead
→ Vivan @wxite — Growth @SafeEdges
→ Cora @FreedaoHome — Freedao BD
Hosted by Vela from https://t.co/iutiRTwD84.
🎁 How to win 50 USDT:
1. Follow @AveaiGlobal
2. Tune in to our AMA on Nov 6.
3. Reply to this post with a screenshot showing you’re listening!
🏆 5 lucky winners will each receive 10 USDT!
🔗 Set your reminder: https://t.co/Cv3b0zB56f
Hackers aren’t waiting. Neither should your security.
Shipping smart contracts to Mainnet starts with an audit.
Casper Forward teams get audit support from @SafeEdges, the security firm behind 200+ smart contract audits.
Building on Casper? Apply now.
→ https://t.co/V3of0XaCVH
Binance’s $6.3B security incident. what we know so far.
We cover all currently known details about the Binance hack, from the attack timeline to fund movements and preliminary findings.
Read more https://t.co/RXB8sk9o4g
#safeedges#BinanceHack
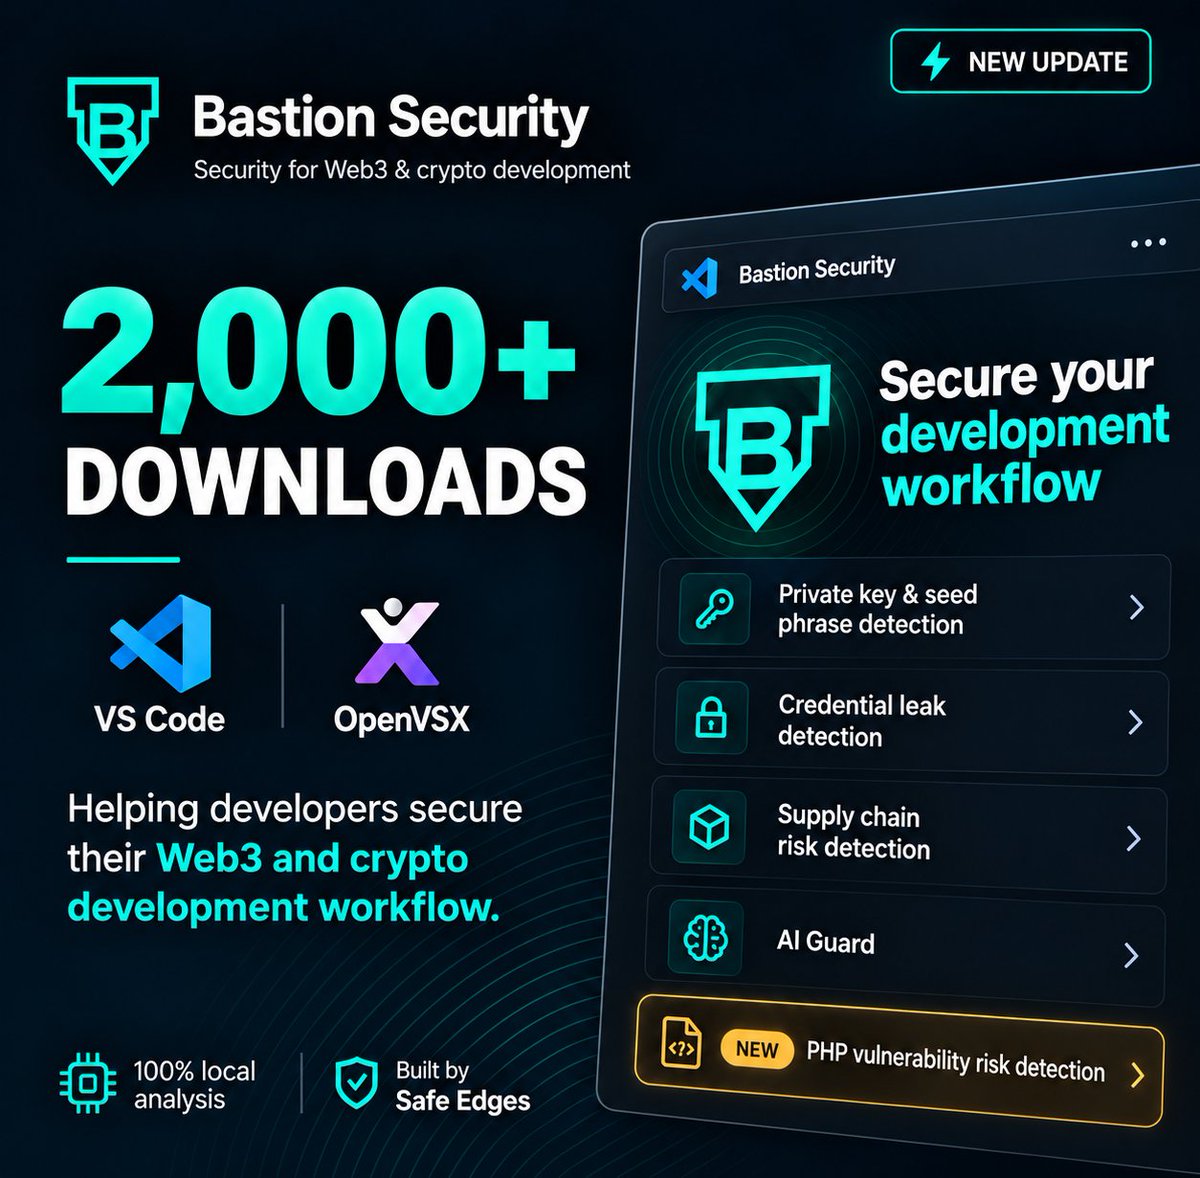
Update ⚡️Bastion Security has crossed 2,000+ downloads on OpenVSX and our latest update adds detection for vulnerable PHP versions.
Activate Bastion Security in your IDE, and it will flag known vulnerable PHP versions in your development environment.
Built by Safe Edges, Bastion Security helps developers identify security risks directly within their development workflow, including:
• Private key and seed phrase exposure
• Credential leaks
• Supply chain risks
• Risky patterns in AI-assisted workflows through AI Guard
• Vulnerable PHP versions
All analysis runs locally on your machine, keeping sensitive code and credentials within your system.
What started as an internal tool to catch security issues earlier continues to grow through community feedback, improved detections, leak free, and performance enhancements.
Thank you to everyone who has installed, tested, reported issues, and supported Bastion Security.
2,000+ downloads and counting. More improvements ahead.
https://t.co/zMrANgU9pw
Backing Casper Forward’s first cohort:
🔸 @Chain_GPT: API credits and a path to ChainGPT Pad
🔸 @SafeEdges: audit support
🔸 @AlliumLabs: data access
🔸 @MarketAcross: PR and launch support
Building on Casper?
Apply → https://t.co/V3of0Xa569
Update ⚡️Bastion Security has crossed 2,000+ downloads on OpenVSX and our latest update adds detection for vulnerable PHP versions.
Activate Bastion Security in your IDE, and it will flag known vulnerable PHP versions in your development environment.
Built by Safe Edges, Bastion Security helps developers identify security risks directly within their development workflow, including:
• Private key and seed phrase exposure
• Credential leaks
• Supply chain risks
• Risky patterns in AI-assisted workflows through AI Guard
• Vulnerable PHP versions
All analysis runs locally on your machine, keeping sensitive code and credentials within your system.
What started as an internal tool to catch security issues earlier continues to grow through community feedback, improved detections, leak free, and performance enhancements.
Thank you to everyone who has installed, tested, reported issues, and supported Bastion Security.
2,000+ downloads and counting. More improvements ahead.
https://t.co/zMrANgU9pw
Worst day for cybersecurity.
Multiple zero-days, supply chain compromises, and ongoing active exploitation reported across the industry.
GitLab: CVSS 10.0 remote code execution vulnerability.
Railway: Customer secrets and private keys potentially exposed.
QUIC: Reported zero-day vulnerability.
PHP: Two critical unauthenticated RCE vulnerabilities under active exploitation.
LiteLLM: Backdoored release stealing cloud, SSH, and AI credentials.
eMudhra: Weak certificate authority keys exposed users to certificate forgery risks.
Node.js, Next.js, React: Critical RCE and TLS security vulnerabilities.
TiDB Cloud: Breach involving stolen credentials and customer data exposure.
Plex2Shell: Exploited within hours, deploying cryptominers and backdoors.
BeyondTrust and Ivanti:
Actively exploited zero-days added to CISA's KEV catalog.
Railway Customers are reporting that their private keys and data are circulating
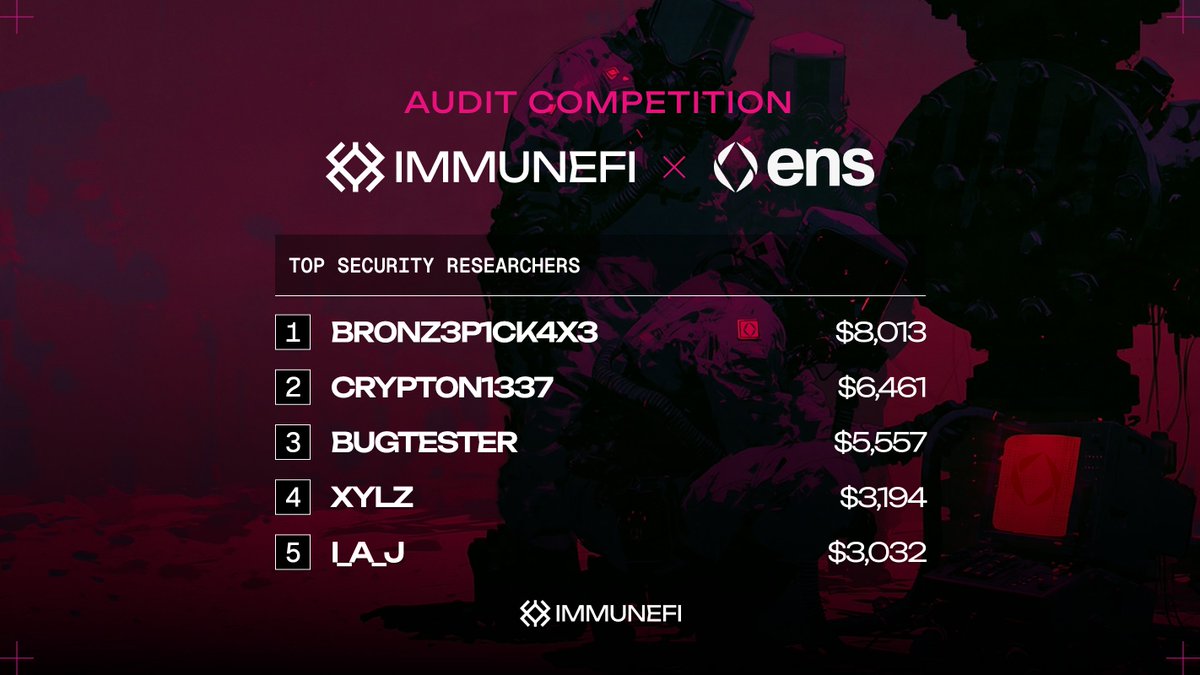
Our internal security agent continues to deliver great results and has proven itself in public audit competitions by finding critical vulnerabilities, securing a 3rd-place position so far.
Ethereum Glamsterdam upgrade is moving to Sepolia.
The Sepolia testnet activation is scheduled for October 6, 2026, at 13:53:36 UTC.
Glamsterdam brings several protocol-level changes, with two of the more notable ones being:
Enshrined Proposer-Builder Separation (ePBS): Brings proposer-builder separation into the Ethereum protocol itself, changing how block building and proposing are handled.
Block-Level Access Lists: Introduces access lists at the block level, specifying the accounts and storage slots that transactions in a block will access. This is designed to make execution dependencies more explicit and support more parallel processing.
The Sepolia rollout is an important step in testing these changes before the upgrade moves further toward mainnet.
Worth watching closely if you're building or researching around Ethereum execution, MEV, and protocol security.
https://t.co/JEn11d15bd
Recently, the U.S. Securities and Exchange Commission (SEC) granted temporary, conditional five-year exemptive relief to certain distributed-ledger trading venues dealing in tokenized NMS stocks, as well as to certain liquidity providers operating on those venues.
This development could open a new phase of institutional adoption, with major financial firms increasingly exploring tokenization, real-world assets (RWAs), and blockchain-based financial infrastructure. This is one reason we are seeing more established institutions and large financial players entering the blockchain space. not simply to experiment with the technology, but to build and operate tokenization and RWA infrastructure.
However, greater institutional adoption also brings greater security risk.
The more capital, financial assets, and market infrastructure move onto blockchain-based systems, the more attractive these platforms become to sophisticated attackers. Security therefore cannot be treated as a secondary consideration.
In this article, we take a deep look at the tokenization landscape from securities and regulatory considerations to the technical and security risks facing institutional tokenization and RWA platforms. We examine how tokenized assets work, where vulnerabilities can emerge
https://t.co/pFNGWI2YEb
The SEC just opened the door.
Today’s Innovation Exemption gives Tokenized Securities Venues five years to trade tokenized NMS stocks using permissioned AMMs and liquidity pools. Smart contracts must be public, auditable, and deployed on permissionless ledgers. Shareholder rights must match the traditional stock. Issuers get notice. Trading must halt in sync with the primary exchange.
This is not a pilot.
This is the first real regulatory path for onchain U.S. equities.
Institutional tokenization and RWA infrastructure just moved from conversation to market reality. The contracts that power these venues will now sit at the center of regulated capital markets.
Safe Edges has been working at this exact layer institutional, RWA, and tokenization-level security for years. Auditable contracts. Real attack-surface analysis. Zero post-audit incidents across $4B+ secured.
The exemption is temporary. The security requirement is not.
This is going to be big.
#Tokenization #RWA #Web3Security #InstitutionalFinance #SafeEdges
August was one of the worst months for DeFi security in Web3, with $185+ million exploited across multiple hacks and incidents. Honestly, the number of attacks we witnessed throughout August is extremely concerning and needs to be addressed properly.
Until we understand the root cause of these incidents, we cannot effectively build better prevention strategies for future attacks. That is exactly why we published this detailed August Web3 Security Incident Report, covering the major incidents, attack vectors
Read the full report, understand the incidents, and learn from them. #safeedges
https://t.co/ZXJW03jCT7
Now the industry is becoming increasingly dependent on AI, and AI security must become a major concern.
The recent incidents involving Hugging Face and OpenAI show that we need to rethink our perspective: we desperately need security for AI.
This is why we’re investing heavily in AI agent security and working with our partners to secure their AI agents before they can be exploited in production.
We have conducted a thorough investigation into the Hugging Face incident.
We are releasing a technical report and accompanying blog post that reconstruct the agents’ activity, explain why existing safeguards failed, and detail how we’re preventing recurrence.
https://t.co/hfxlbiXXiP
AI agents can think, learn, and act. But to participate in a real economy, they also need identity, permissions, wallets, and secure settlement infrastructure.
Join our upcoming AMA:
AI Agents Need Wallets: Who Will Build Asia’s Machine Economy?
🗓 August 28th, Friday
⏰ 1:00 PM UTC
🎙 Hosted by ENI
Guests:
• Arion, ENI CEO
• Paul Kim, ENI Korea CEO
• Azibi Malawi, AxiomOS @axiomos_
• Saadia, VerityAI @BuildOnVerity
• Vivan Chauhan @wxite, Safe Edges @SafeEdges
• Ahaya, Freedom Asset @FreedomAssett
Discover who will build the wallets, security, coordination, and financial infrastructure powering Asia’s machine economy.
AI agents can think, learn, and act. But to participate in a real economy, they also need identity, permissions, wallets, and secure settlement infrastructure.
Join our upcoming AMA:
AI Agents Need Wallets: Who Will Build Asia’s Machine Economy?
🗓 August 28th, Friday
⏰ 1:00 PM UTC
🎙 Hosted by ENI
Guests:
• Arion, ENI CEO
• Paul Kim, ENI Korea CEO
• Azibi Malawi, AxiomOS @axiomos_
• Saadia, VerityAI @BuildOnVerity
• Vivan Chauhan @wxite, Safe Edges @SafeEdges
• Ahaya, Freedom Asset @FreedomAssett
Discover who will build the wallets, security, coordination, and financial infrastructure powering Asia’s machine economy.
Safe Edges is now the Strategic Security Partner for the @X1_EcoChain ecosystem.
X1 is an EVM-compatible L1 running Proof of Nodes, with validators on 4-core, 4GB, low-power hardware rather than datacentre rigs. A validator set shaped like that changes the assumptions around participation, liveness and reward accounting.
Gas from every transaction is redistributed at the protocol level, 90% across validator wallets and 10% to genesis. Custom economic logic like that is where the findings that matter usually sit, not in the parts a generic checklist covers.
For teams building on X1 that means full Solidity coverage on contracts and dApps, plus pen testing across the frontend, API and RPC surfaces, at ecosystem rates and a priority queue.
#SafeEdges is here to secure every team building on X1.
Excited to announce our strategic partnership with @X1_EcoChain
X1 is building an EVM-compatible L1 with up to 90% lower transaction fees.
We’re proud to be part of the X1 ecosystem and look forward to strengthening the security of the teams and protocols building on X1. 🛡️
#safeedges 🤝 #x1ecochain
X1 EcoChain 🤝 @SafeEdges: Fortifying Ecosystem Security
We are thrilled to announce our strategic partnership with Safe Edges — a premier Web3 cybersecurity firm specializing in smart contract audits and protocol verification.
Safe Edges joins us as an official security partner. Moving forward, projects joining the X1 EcoChain ecosystem will get direct access to top-tier security audits under highly exclusive terms.
Key benefits for X1 EcoChain ecosystem projects:
🟢 Special Perks: preferred rates and priority queue for smart contract and dApp audits.
🟢 End-to-End Protection: manual code reviews, invariant testing, and threat monitoring.
🟢 Ecosystem Trust: seamless mainnet onboarding backed by industry-tested security standards
Forward - together with the best 🚀