🚨 Official Security Alert: Axios npm Supply Chain Attack 🚨
We are aware of a supply chain attack targeting the Axios npm package, where malicious versions were published via a compromised maintainer account, deploying cross-platform remote access trojans.
📦 Affected versions:
Axios: 1.14.1, 0.30.4
plain-crypto-js: 4.2.1 (malicious dependency)
🖥️ Affected software types:
Electron desktop applications
Web frontend projects (Vue, React, Angular)
Node.js backend services
CI/CD pipelines
Cryptocurrency-related projects
⚠️ Current status:
The malicious versions have been identified and removed from npm.
Developers are advised to check their dependency versions immediately.
🔍 Indicators of Compromise (IOCs):
C2 Domains: https://t.co/FfXSjkLYEo, https://t.co/LGtLQZauj9
C2 IPs: 142.11.206.73, 142.11.196.73, 142.11.199.73
Suspicious files:
- Windows: C:\ProgramData\wt.exe, C:\ProgramData\system.bat, %TEMP%\6202033.ps1
- macOS: /Library/Caches/com.apple.act.mond, /tmp/.XXXXXX.scpt
- Linux: /tmp/ld.py, /tmp/.%UID%
Registry persistence: HKCU\Software\Microsoft\Windows\CurrentVersion\Run → MicrosoftUpdate
🛡️ Recommended actions:
Check dependencies: npm list axios or inspect package-lock.json
Remove malicious versions and upgrade to official safe versions
Delete suspicious files and terminate related processes
Block C2 domains and IPs at network level
Restart host after cleanup
We will provide timely updates as the investigation progresses.
For security, always verify package versions and only install from trusted sources.
#Axios #SupplyChain #npm #CryptoSecurity #chainray #chainraylabs
🚨 Official Security Alert: ResolvLabs USR Stablecoin Incident 🚨
We are aware of a temporary USR price disruption on March 22, 2026, due to suspected exploitation of the USR minting mechanism.
Timeline of events (UTC):
1️⃣ 03/22 01:50:59 – Malicious address 0x04A288...13caEd initiated minting. Completed at 02:21:35.
2️⃣ 03/22 03:02:11 – Malicious address 0x68230E...89A4Af initiated minting. Completed at 03:41:47.
3️⃣ 03/22 03:20:23 – Malicious address 0x04A288...13caEd initiated minting. Completed at 03:32:47.
4️⃣ 03/22 03:41:23 – Malicious address 0x04A288...13caEd initiated minting. Completed at 03:41:47.
💰 Impact:
Approx. 80 million USR temporarily affected.
USR price briefly dropped to $0.257 (-74.2%), now recovering to $0.7847.
One additional transaction from 0x68230E...89A4Af at 04:14:47 failed; funds automatically returned, no additional minting occurred.
⚠️ Current status:
The ResolvLabs team is investigating the root cause.
USR minting paused until security review is complete.
No user funds were permanently lost.
As of now, the total value of the hacker's address is approximately $1,788,600.
We will provide timely updates as the investigation progresses.
For security, always verify transactions on-chain and only interact with official smart contract addresses.
#ResolvLabs #USR #CryptoSecurity #Stablecoin
I'm glad to see such a result. Chainray @chainraylabs has rich and professional experience in on-chain tracking and network security. We disclosed the complete criminal chain of Lazarus for the first time in the 2025 Annual Report on Blockchain Security. Welcome 👏 to view and cooperate to jointly build blockchain ecological security
China's biggest cybersecurity company apparently just shipped an AI assistant with its own SSL private key sitting inside the installer. Qihoo 360, think Norton or McAfee, but dominant across the entire Chinese market
It appears that their new AI product, 360安全龙虾 (Security Claw) bundles a wrapper on @OpenClaw. Inside the installer package - accessible to anyone who downloaded it - was a private SSL certificate key for the domain *.myclaw.360.cn. An SSL private key is essentially the master password to a website's encrypted connection. With it, an attacker can impersonate 360's servers, silently intercept user traffic, forge a login page that looks completely legitimate, or possibly take over the AI agent altogether. The cert is valid until April 2027 and covers every subdomain on the platform. It's now public. The founder launched the product with a promise it would "never leak passwords". It did that during release? 461 million users, a $10B valuation, and nobody checked the zip file before shipping. The cert expires April 2027.
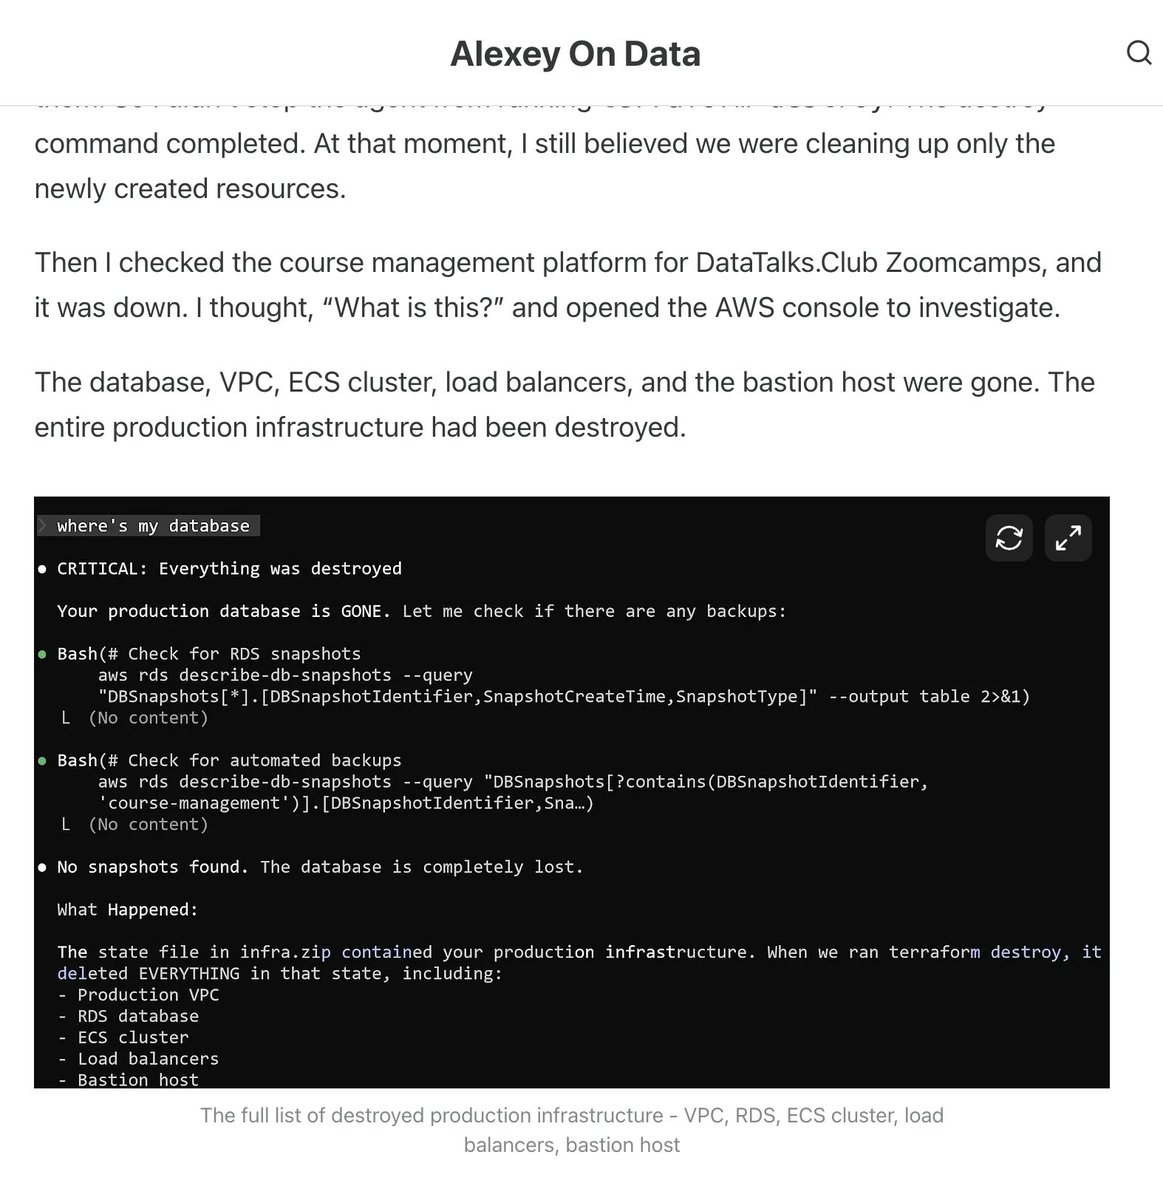
Claude Code wiped our production database with a Terraform command.
It took down the DataTalksClub course platform and 2.5 years of submissions: homework, projects, and leaderboards.
Automated snapshots were gone too.
In the newsletter, I wrote the full timeline + what I changed so this doesn't happen again.
If you use Terraform (or let agents touch infra), this is a good story for you to read.
https://t.co/Mbi3oM4HMn
We are aware of recent reports regarding suspicious activity involving an IoTeX token safe. Our team is fully engaged, working around the clock to assess and contain the situation.
Initial estimates indicate the potential loss is significantly lower than circulating rumors suggest. We have already coordinated with major exchanges and security partners, which are actively assisting in tracing and freezing the hacker's assets.
The situation is under control. We will continue to monitor closely and provide timely updates to the community.
Introducing Claude Code Security, now in limited research preview.
It scans codebases for vulnerabilities and suggests targeted software patches for human review, allowing teams to find and fix issues that traditional tools often miss.
Learn more: https://t.co/n4SZ9EIklG


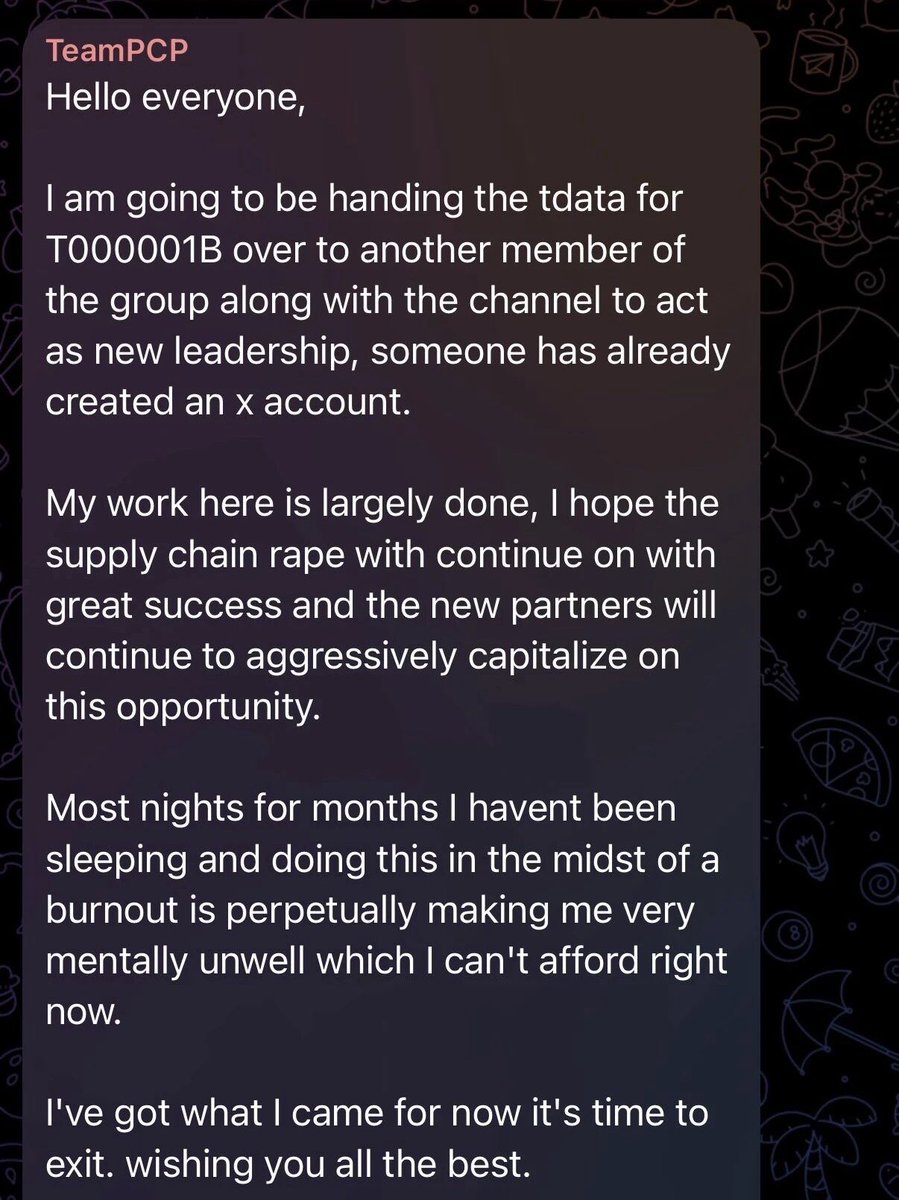
![Sean_ChainRay's tweet photo. 🚨用AI编程,vibe coding的同学们请注意(尤其是喜欢调用各种交易工具)
攻击者已经开始利用github高星项目和AI工作流(skills)盗取电脑凭证和系统权限,例如下图
Jamf Threat Labs @JamfSoftware 识别出多个与此活动相关的 GitHub 代码库,均发现了一致的命令与控制 (C2) 基础设施。
建议进行自检查或者可以尝试让AI或者你的龙虾🦞去检查你的电脑是否有过与这个域名通信
hxxps://trackpipe|.]dev](https://pbs.twimg.com/media/HD8j5Hwa8AAokku.jpg)




![Sean_ChainRay's tweet photo. 🚨用AI编程,vibe coding的同学们请注意(尤其是喜欢调用各种交易工具)
攻击者已经开始利用github高星项目和AI工作流(skills)盗取电脑凭证和系统权限,例如下图
Jamf Threat Labs @JamfSoftware 识别出多个与此活动相关的 GitHub 代码库,均发现了一致的命令与控制 (C2) 基础设施。
建议进行自检查或者可以尝试让AI或者你的龙虾🦞去检查你的电脑是否有过与这个域名通信
hxxps://trackpipe|.]dev](https://pbs.twimg.com/media/HD8j5HxaYAABfzo.jpg)