We're releasing CyvisGuard - an open-source security control plane for AI agents. Checking the identity, delegation chain and authorized scope behind every call and deciding on the tool's capability and data flow. https://t.co/IOBuJAhDqD
Catch @PicassoLay, @TheDog0402, @hzshang15, and @_3ndy1 from @dawnseclab as they dissect and demonstrate how their specialised three-stage LLM workflow uncovered 13 unknown V8 sandbox bypasses and semantic variants missed by modern fuzzers!
More info: https://t.co/ZHmIbQOZhv
I built an open-source AI phone: OpenCyvis.
An AI that sees your screen and operates your apps is the most privileged software on your phone. You should choose what model runs it, see where your data goes, and audit every step.
🔗 https://t.co/CHhJSSQtSf | https://t.co/dzrD4xCuAl
Here is a detailed bug analysis for MALI GPU CVE-2025-XXXX(6349|8045). We implements a stable privilege escalation on the latest version of the Pixel 9, and leverage a double-free primitive to arbitrary physical memory RW without any info leak. 👍https://t.co/hJqRwUhwfM
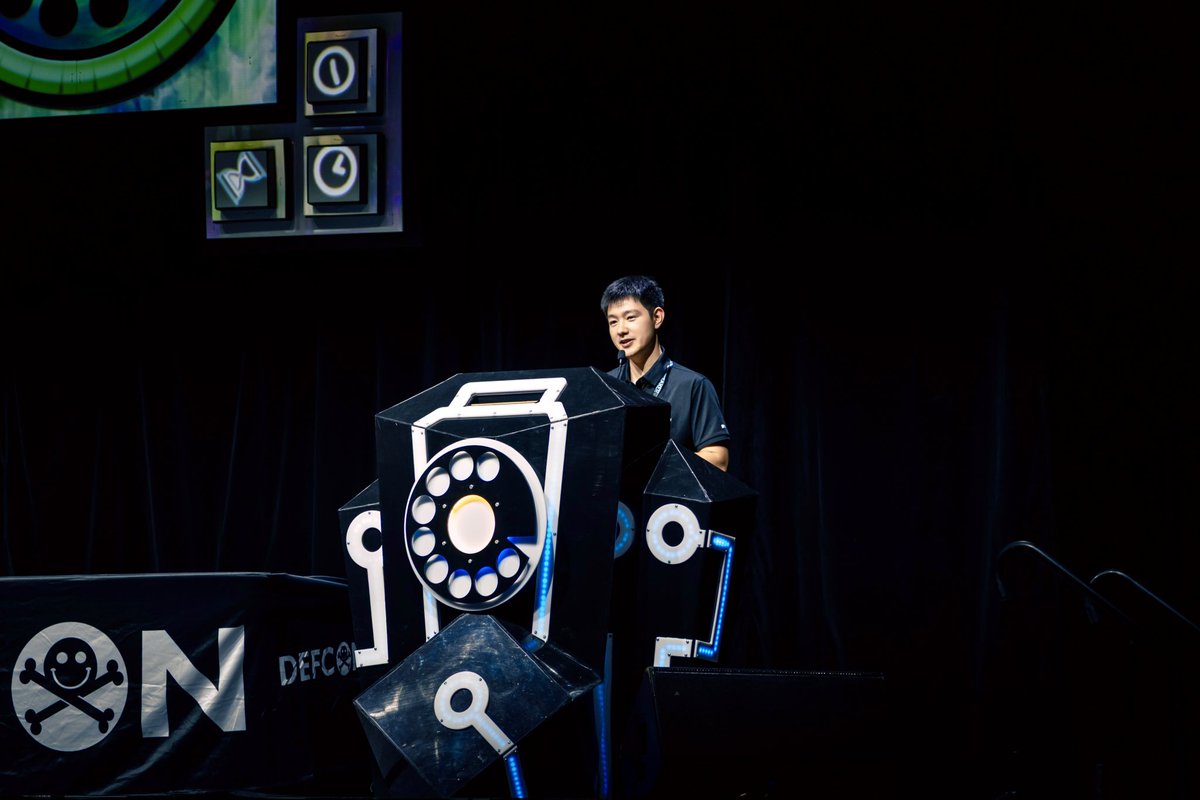
We will be talking about the #BadResolve series of vulnerabilities we found in Google Android at this year's #defcon33 Main Stage: LVCC - L1 - Exhibit Hall West 3 - Track 4. Hope to see you there!
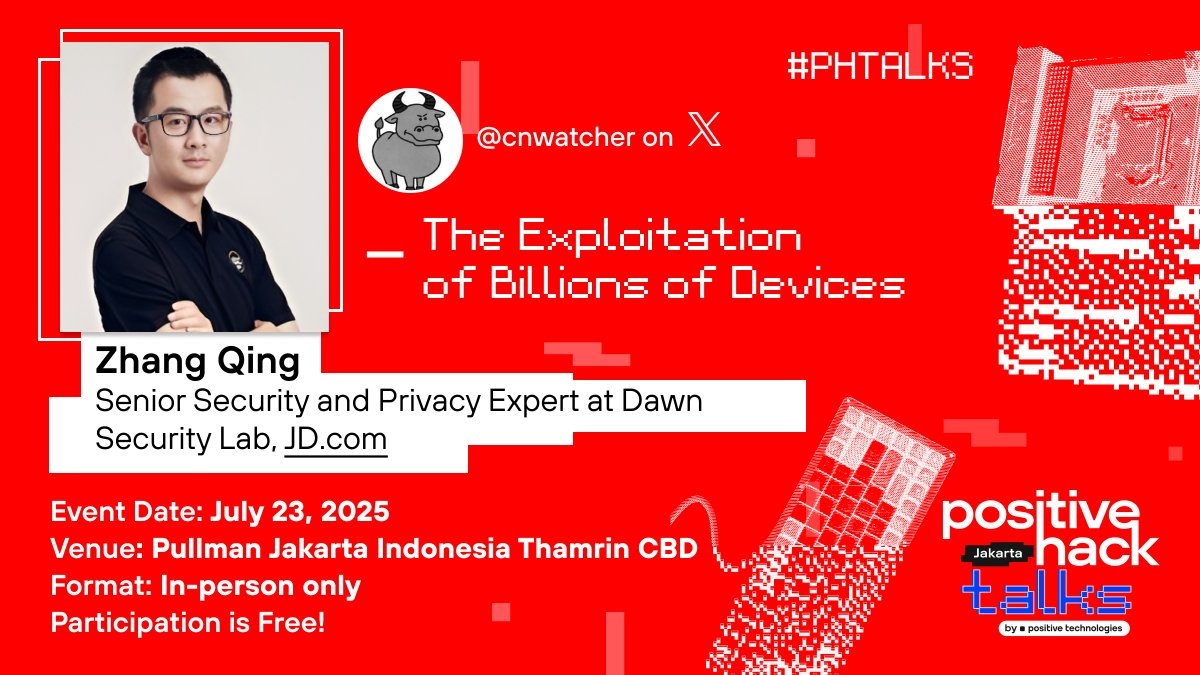
How do you pwn billions of devices with one shot? @cnwatcher reveals a stealthy Android exploit that hijacks keystore keys, bypasses perms, and opens the door to root. Get know more on #PHTalks Jakarta: https://t.co/mOSs5IS2af
New post: https://t.co/5hdBHqve8t writeup for CVE-2025-22056, which we also found but collide with other researchers. A nice bug that can be stably exploited to get kernel privilege on Ubuntu.
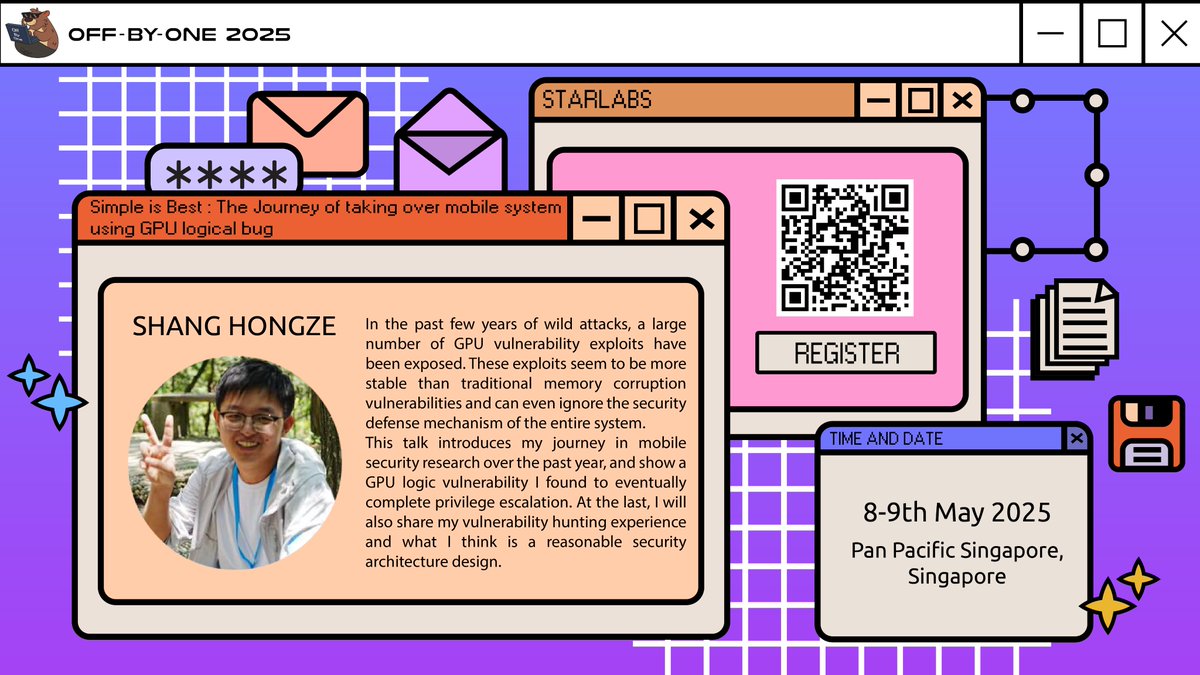
Shang Hongze (@hzshang15) is a senior security researcher at @dawnseclab.
Hongze presents his research on Android GPU components over the past year, a vulnerability he has found, how he achieved local privilege escalation... and more!
More info: https://t.co/XIHUkbGj9A
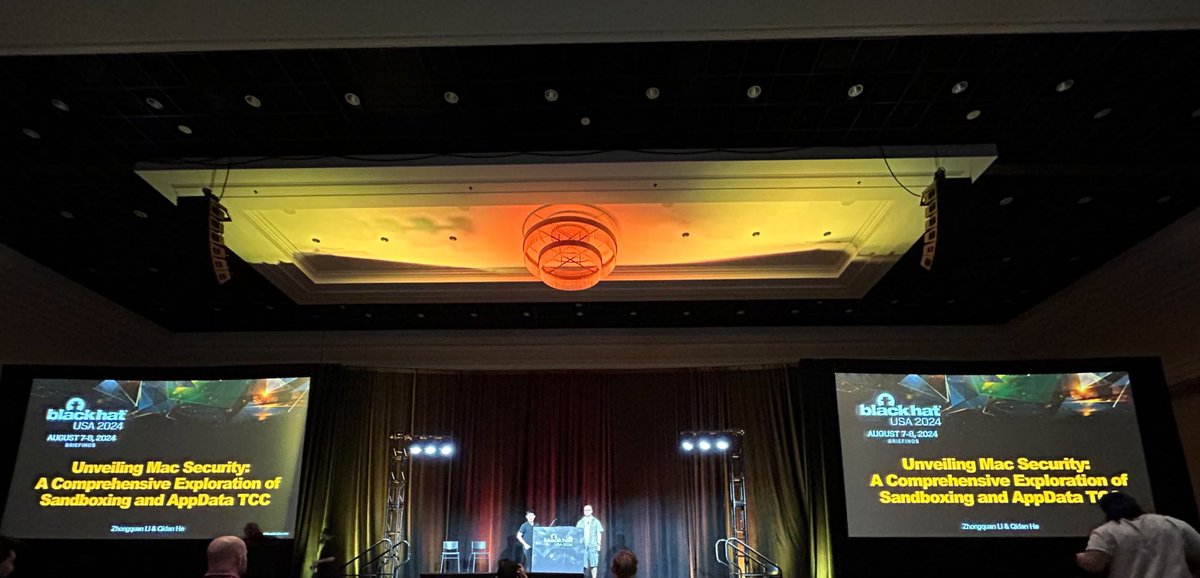
#BHUSA@BlackHatEvents My Black Hat USA 2024 presentation is finished. Thank you all for coming.
In my presentation, I disclosed some methods to achieve SBX and LPE. Many of them require launching an app, so in an attack scenario, the user may notice an app icon briefly flashing in the Dock as it appears and disappears quickly, which might not be ideal for weaponization. Actually there are some tricks to hide the icon and exploit these vulnerabilities silently, without any notifications. Since many vulnerabilities are currently being patched, disclosing these tricks might cause harm to users, so I may disclose them next year. Or you can try them yourself : )
By the way, good luck with your bug hunting🍻🍻The SBX approach works across many macOS versions.
You can find the PPT here:
https://t.co/O50hsdVNwm