🚨 CRITICAL
The Salt Typhoon APT group; a state-sponsored threat actor, is actively targeting telecoms, government, and critical infrastructure networks worldwide.
Assume you're a target if your organization operates in these sectors.
Read the full advisory on our website
https://t.co/WtR3ptURci
#SaltTyphoon #APT #CyberEspionage #CriticalInfrastructure
🚨 CRITICAL
A critical authentication bypass vulnerability (CVSS 9.8) has been found in Esri Portal for ArcGIS and needs no credentials to exploit it.
Patch now.
Read more on our website
https://t.co/GjCWL46mEq
#ArcGIS#CyberSecurity#VulnerabilityAlert
🚨 CRITICAL
BEC & social engineering attacks are actively targeting Nigerian govt agencies and critical institutions.
Attackers are impersonating officials to steal funds and data.
✅ Verify before you act
✅ Check sender addresses
Visit our website to read more
https://t.co/7hmmbeizEV
#BEC #CyberSecurity #SocialEngineering
Federal Government Extends NYSC Orientation Camp to Six Weeks, Scraps Military Drills and Passing Out Parade
The Federal Government has approved a major overhaul of the National Youth Service Corps (NYSC), extending the orientation camp programme from three weeks to six weeks as part of wide-ranging reforms aimed at repositioning the scheme.
As part of the changes, military drills and parade activities during the orientation camp have been scrapped. The traditional Passing Out Parade at the end of the one-year service will also be replaced with a graduation ceremony.
The reforms are designed to make the NYSC more skills-driven and better equipped to prepare corps members for the workforce and entrepreneurship.
The government also approved the introduction of a redesigned NYSC uniform to reflect professionalism and give the scheme a renewed identity.
The changes form part of the Federal Government’s broader plan to modernise the NYSC and align it with the country’s economic and youth development objectives.
ngCERT is aware of a high-severity vulnerability affecting Apache HTTP Server version 2.4.66 dubbed CVE-2026-23918.
All public and private organisations operating affected systems are advised to take immediate action.
Read more on our website
https://t.co/JhlHhcZdOS
ngCERT has issued an advisory on a Critical Zero-Click Vulnerability, tracked as CVE-2026-0073 on its website.
Organisations are strongly advised to take necessary steps to safeguard their systems.
For further technical details, visit
https://t.co/UOvblx5Iz5
ngCERT strongly advises the Government, private organizations, and the general public to urgently apply the relevant security updates to mitigate potential exploitation
Further technical details can be found on our website
https://t.co/YjENINePRn
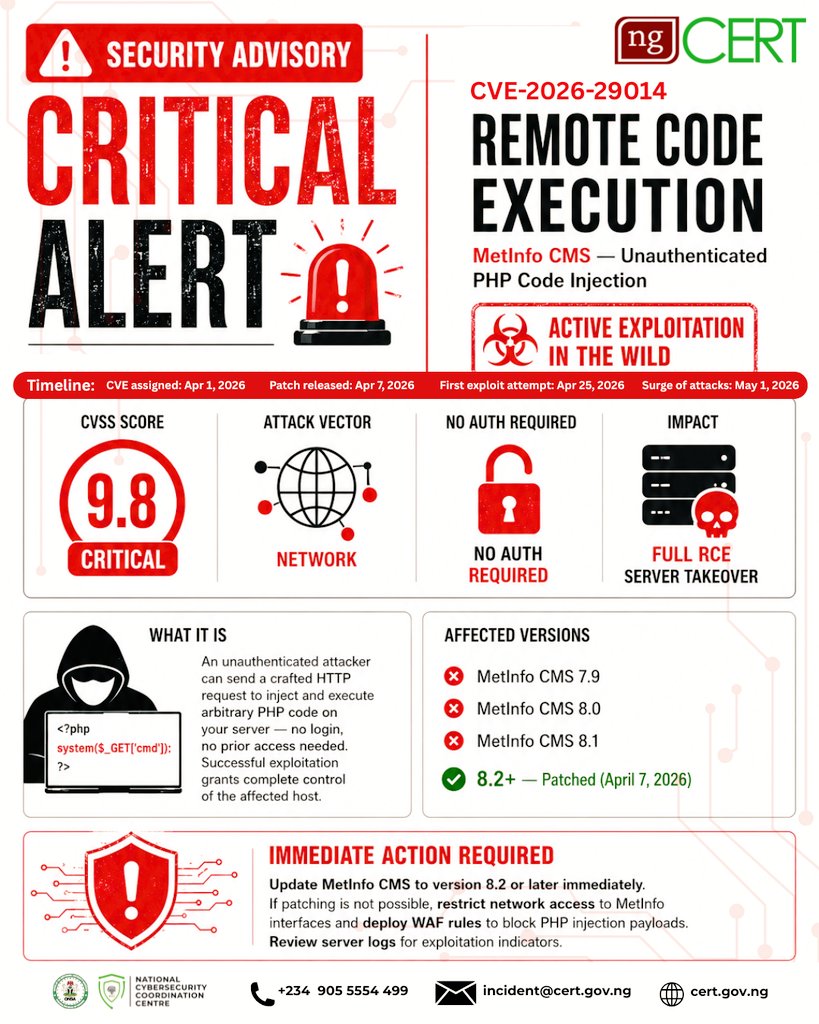
🚨 CVE-2026-29014
Active exploitation targeting vulnerable MetInfo CMS installations has been observed in the wild.
Attack activity is increasing, patch now and monitor exposed systems closely.
Security Alert 🚨
A directory listing exposure (CWE-548) has been identified within a web application storage directory, potentially exposing sensitive files configurations, and application resources to unauthorized users.
#CyberSecurity
CVE-2024-6387 🚨 (RegreSSHion)
A critical flaw in OpenSSH sshd may allow unauthenticated remote code execution with root privileges on vulnerable systems.
Further technical guidance will be provided soon
#CyberSecurity#Linux
Security Alert 🚨
Expired and mismanaged digital certificates are more than an IT issue, they are a serious cybersecurity risk
Further technical guidance will be provided soon
#CyberSecurity
CRITICAL 🚨
ngCERT identified RegreSSHion (CVE-2024-6387) as a critical unauthenticated Remote Code Execution vulnerability in OpenSSH's sshd on Glibc-based Linux systems which can be exploited through specially crafted requests......
More details below
https://t.co/qm46tmfpYn
ngCERT alerts stakeholders to the threat posed by SniperDz, a long-running Phishing-as-a-Service (PhaaS) platform that enable cybercriminals conduct large-scale phishing campaigns with minimal technical expertise.
More details on our website https://t.co/mK8IOAUVjF
ngCERT issues this advisory on a major Cyber-enabled ATM Cash-out operation targeting financial institutions across Africa.
More details on our website
https://t.co/RKzeoPEfEn
Rotary Club of New Lagos Ikeja Commissions Borehole Project to Boost Access to Clean Water in Ogun Community
Read the full story on Facebook via this link 👇
https://t.co/zhCss4OmJE
Rotary Club of New Lagos Ikeja Commissions Borehole Project to Boost Access to Clean Water in Ogun Community
Read the full story on Instagram via this link 👇
https://t.co/TtLOMZWEC3
Rotary Club of New Lagos Ikeja Commissions Borehole Project to Boost Access to Clean Water in Ogun Community
Read the full story on Instagram via this link 👇
https://t.co/U7dw0gb643
The project, commissioned on Sunday, June 7, 2026, attracted community leaders, residents, Rotarians and other stakeholders for the official handover of the facility, expected to improve access to clean water in the community.