I’ve heard several OAI people say there are unfixable bugs in hardware that are exploitable by AI models directly speaking machine code so even if we could solve software that’s not enough. We need defense to move faster than offense if that’s even possible we may just have a new normal that requires adapting to insecure software (bank transfers require going into a branch and taking a dna test 🤣😬)
SITUATION DETECTED: CloudFlare CEO Matthew Prince says he is aware of additional severe vulnerabilities in other pieces of critical software, and said “I think we’re going to have a couple years where every single week it’s going to feel like the sky is falling,” per Reuters.
⚠️ Node.js is vulnerable to remote code execution.
CVE-2026-111497 (high): A Node.js process that decompresses attacker-controlled Brotli data can be made to leak memory or run arbitrary code.
You’re exposed if your app or a library decompresses bad Brotli data (e.g. the built-in fetch(), body-parser)
Aikido detects this. Patches are available.
Irrespective of whether software engineering is coming to an end or not, think of it as a roller coaster ride. You are already on it, so have fun while it lasts.
Either it crashes or lands you safely.
You have to be optimistic about technology. If things go wrong, it will be the end for everyone. If AI is here to stay and you refuse to adapt, you will be left far behind.
Your best bet is to stay positive with tech ... always :)
Comment2Shell, a pre-authentication stored XSS in WordPress that escalates to RCE.
A smart usage of XSS by DeathShotXD.
Full chain PoC with scanner interactive shell Nuclei template and Docker lab: https://t.co/SxqtiSicse
India mein koi 5 minutes number Google kar le to doodh ka doodh paani ka paani ho jaye.
RBI surplus to Govt : ₹2.87 Lakh Crores (US$30 Bn)
Total listed bank profits : ₹4.11 Lakh Crores (US$42 Bn)
NPCI - which runs UPI pre tax ‘surplus’ : ₹ 1,888 crores (US$200 Mn)
To nuksaan kis ka ho raha hai UPI se aur kaunsi subsidy de rahi hai Govt UPI pe jo chubh rahi hai?
Cost of running ATMs and cash logistics in India is ₹30,500 crores (US$ 3.0 Bn). If you want to optimise shut ATMs and promote UPI instead.
Any levy on UPI is just tax collection. UPI is the one scientific achievement of India everyone acknowledges par ab tax ki bali chadhegi.
I hate when VS Code eats up 1GB and takes 7 seconds to start, so I built https://t.co/BcvoimKiLJ, which does the same things in 20MB of RAM and starts in 1ms.
The last time we edited code in an IDE was in 2025, so our IDEs should become read-only but fast.
Give it a shot.
A logical bug that I've reported to MariaDB has just been disclosed! 🎉
It's a nice logic issue that allows any user (no matter their rights) to update the password of any other user, including root :D
You can find more details 👇
https://t.co/ds2U25peIM
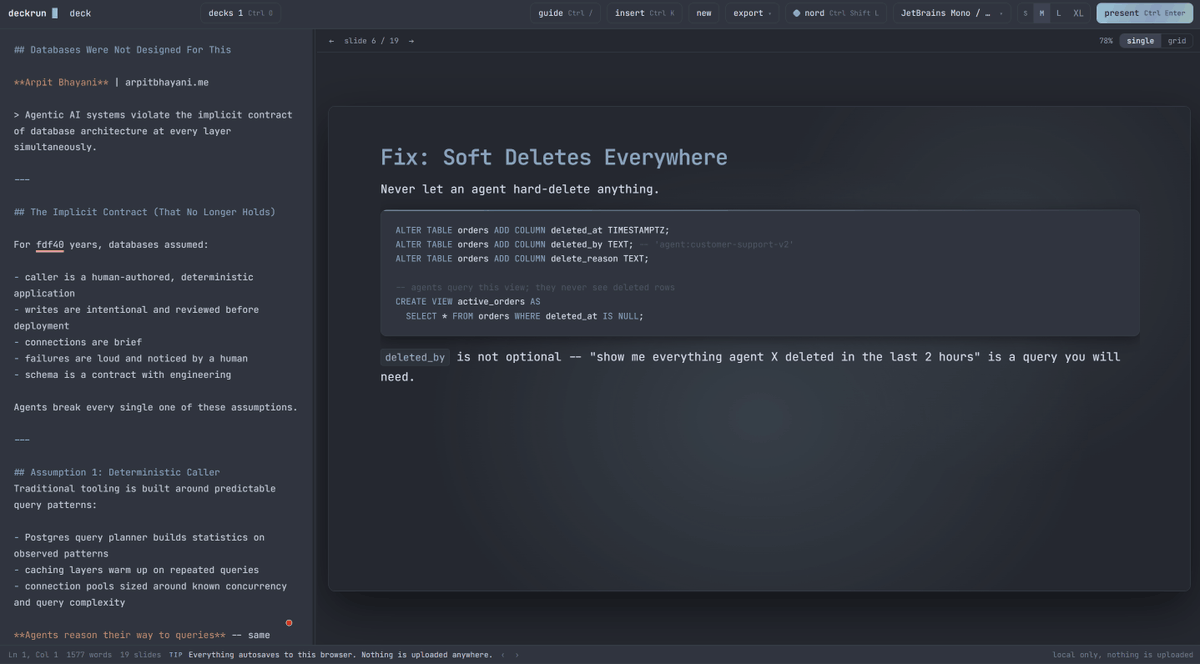
Built "deckrun" - that allows you to present your Markdown and self-contained HTML docs easily. Write a deck in plain Markdown, run one command, and it opens a local server and presents it as slides in the browser.
A few things worth knowing -
- A live editor with a byte-identical preview
- Autosaved deck library.
- Fully customizable and more importantly
- Fourteen themes :)
Also, it can help you present self-contained HTML docs as a single continuous page.
Everything stays local. The server only binds to 127.0.0.1, and every deck you write is saved to localStorage right there in your browser; nothing is ever uploaded until you choose to export it.
Give it a shot and let me know what you think.
Hope this helps.
Recently, I've been looking at DOMPurify again, trying to find ways to bypass 3.x.x after browsers started encoding attrs during serialization.
I ended up with a nice ≤3.2.6 Safari default-configuration bypass using only SMIL tags/attrs :D
Details 👇
https://t.co/EMfsjlXUem
What started with a simple question on Discord, ended in *reviving an old XS-Leak technique* for probing status codes in background requests!
Unravel the mystery with me in the latest @ctbbpodcast blog post: