Introducing SharpWSUS!
SharpWSUS is a .NET exploitation tool by @The_Keeb, which allows red teamers to laterally move via Windows updates. It builds on existing tools to allow easy use over C2 channels.
https://t.co/C9ENSHbX9G
Public exploit is out for the Linux 'PwnKit' privilege elevation vulnerability!
BleepingComputer has confirmed the exploit for CVE-2021-4034 works and granted us root privileges on Ubuntu.
🚨 Patch now if you can! 🚨
https://t.co/Jh7uoHP5FS
New #mimikatz release to test new ts::logonpasswords feature (experimental)🥝
- Only with active users
- Only tested on 2012R2/2016/2019 + some Windows 10 LTSC
> https://t.co/Wzb5GAfWfd
* Do not hesitate to make some tests @awakecoding@jonasLyk@FuzzySec@n00py1 etc. 🤪
💰Introducing MoneyScope💰
A simple tool to extract all domains and TLDs of public programs with paid bounties for easy wide scope recon including:
https://t.co/L7VJVwidsv
- Chaos
- HackerOne
- YesWeHack
- BugCrowd
- Intigriti
#bugbountytips#100DaysOfCode#CyberSecurity
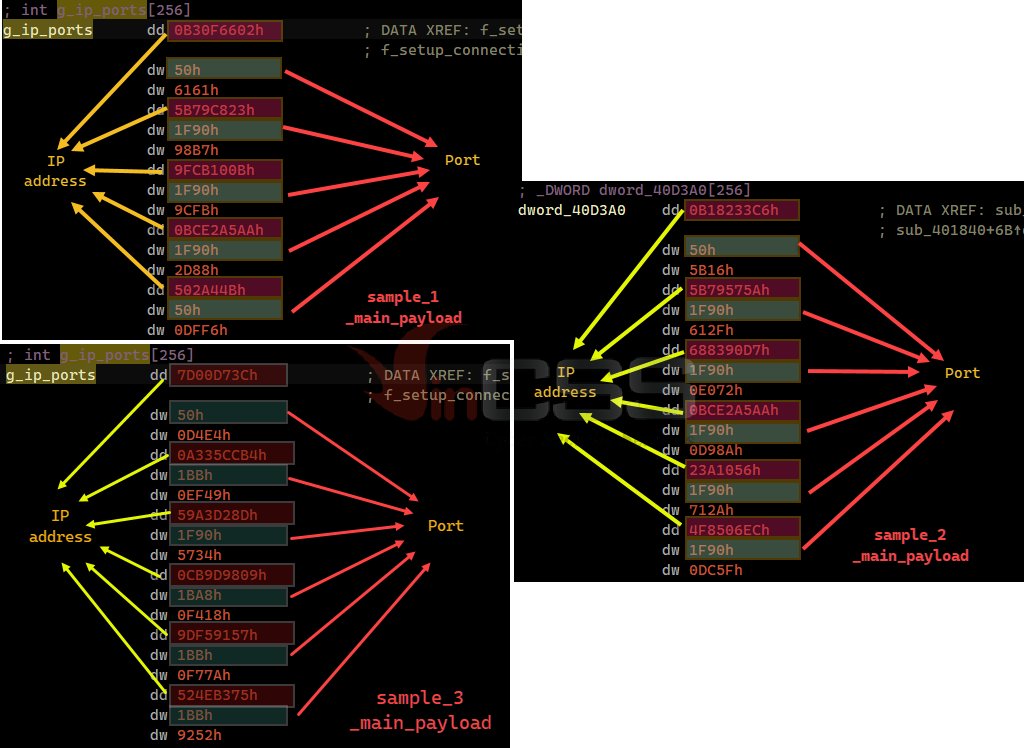
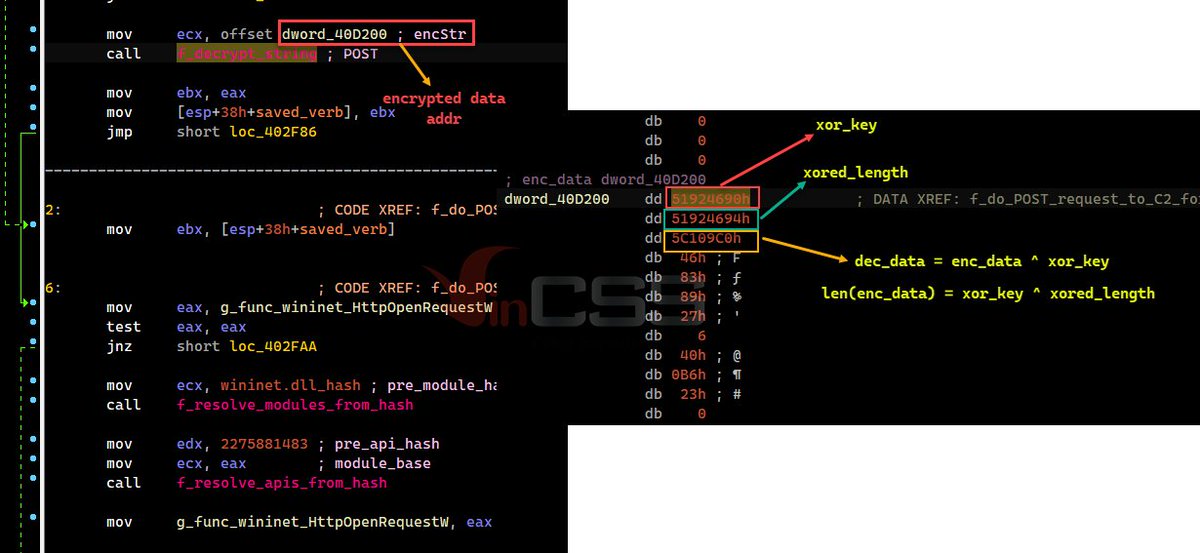
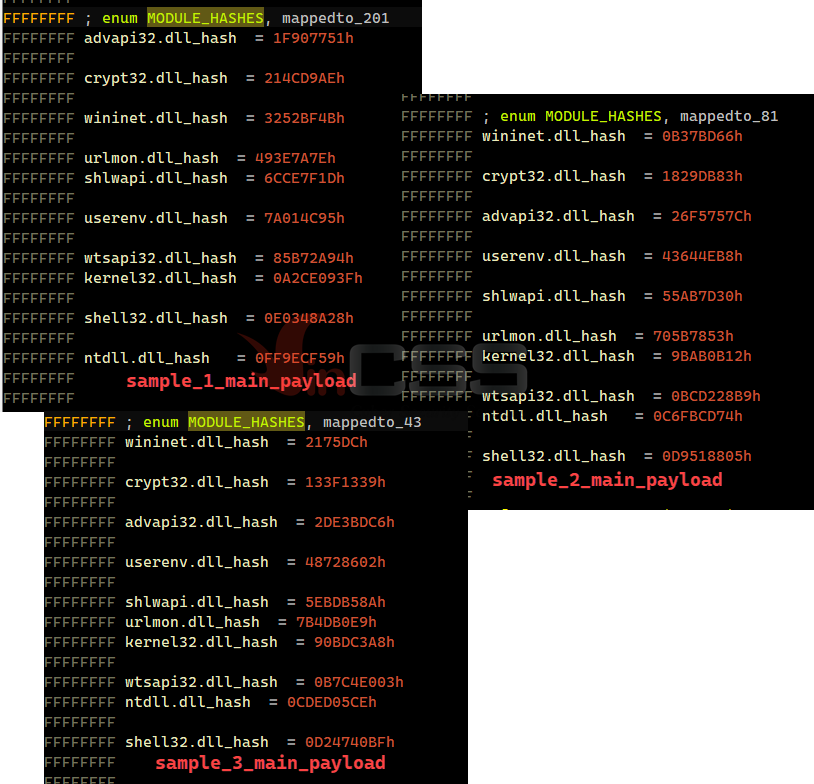
#Emotet is one of the most dangerous Trojan today. In this article, we analyze in detail full attack flow in some real cases of recent #Emotet samples which were discovered and handled by us while providing #cybersecurity services to our customer.
https://t.co/bFSblcPNnF
Did you know? We can unlock LUKS encrypted root/boot disk using Dropbear SSH keys in Linux at boot time. Useful when you don't have a KVM console or keyboard/monitor. Useful for a remote Linux server or cloud server too.
https://t.co/egMz59qFfR
Cleaning out my office I found my ‘attack mouse’, a mouse I had badly wired a USB hub into for ‘bad USB’ attacks. This has a great story to go with it.
/1
Unauthenticated Arbitrary File Read vulnerability in VMware vCenter before version 6.5u1
PoC for extracting passwords from https://t.co/CNYO5LTdBB file - /eam/vib?id=C:\ProgramData\VMware\vCenterServer\cfg\vmware-vpx\https://t.co/CNYO5LTdBB
#bugbounty#cybersecurity#security