Fraud used AI to scale. Fraud, risk & compliance teams didn't.
$100B/year spent on FRC ops. AI-driven attacks up 8,000% in a year. Headcount can't keep up.
Today we're closing that gap:
Anthropic begins trading today, and its IPO filing includes a warning every business with a signup form should read.
Bad actors have already used frontier models to find vulnerabilities, write malware, and evade detection. It also warns that Anthropic’s own agents could send communications and complete transactions with limited human oversight.
And it reported $17.0 billion in revenue in a single quarter, which shows how fast AI became business infrastructure.
So when a new user or agent signs up, requests more access, or moves money, “is this a real person?” is no longer the only question. Identity tells you who authorized an action. It doesn’t tell you whether to trust what happens next.
AI made fraud easier. Trust has to be smarter, and built to outpace threats that learn.
Fraud scaled. So did we.
Most systems, government included, can’t tell a legitimate AI agent apart from a bot trying to get in.
Our new report with @govtechnews looks at what happens when residents start using AI agents to access government services, and what agencies need in place before it happens at scale.
Blocking all bot traffic used to be the default. That doesn’t work in a world of consumer agents, and a legitimate agent can still take an action a resident never authorized.
The report breaks down a four-part framework: distinguish agentic traffic, identify who an agent represents, assess risk session by session, keep it all auditable.
Read the full report: https://t.co/XLhOpJ1vyT
More than half of all web activity is no longer human.
Some of it’s fraud but a lot of it is just real people sending AI agents to book a flight for them.
Agent Detection on RiskOS tells you which is which by reading signals like typing rhythm and mouse movement before a click, with 99.9% accuracy. Then you decide: approve, step up with an OTP, or stop it.
Watch an agent book a flight, get recognized, get verified. 👇
Tokenized markets need more than a verified person. They need to know which wallet that person actually controls before anything moves.
Today, @SocureID is partnering with @WalletConnect to make that one credential instead of two separate checks. Socure verifies the person. WalletConnect verifies the wallet.
Wall Street is already moving on-chain, DTCC, Nasdaq, NYSE, all building toward tokenized markets, and every institution arriving needs to know who they’re dealing with and which wallet is really theirs.
→ Banks confirm a receiving wallet belongs to their verified customer
→ Exchanges meet Travel Rule obligations with a verified person-to-wallet link
→ Platforms stop multi-accounting by tying every wallet to one real person
Read the full announcement. ⬇️
BREAKING: WalletConnect and @SocureID partner to link verified identity with verified wallets through Wallet Verification.
Socure’s bank, fintech and exchange clients can let their customers connect any of 700+ wallets through WalletConnect, with no separate wallet integration.
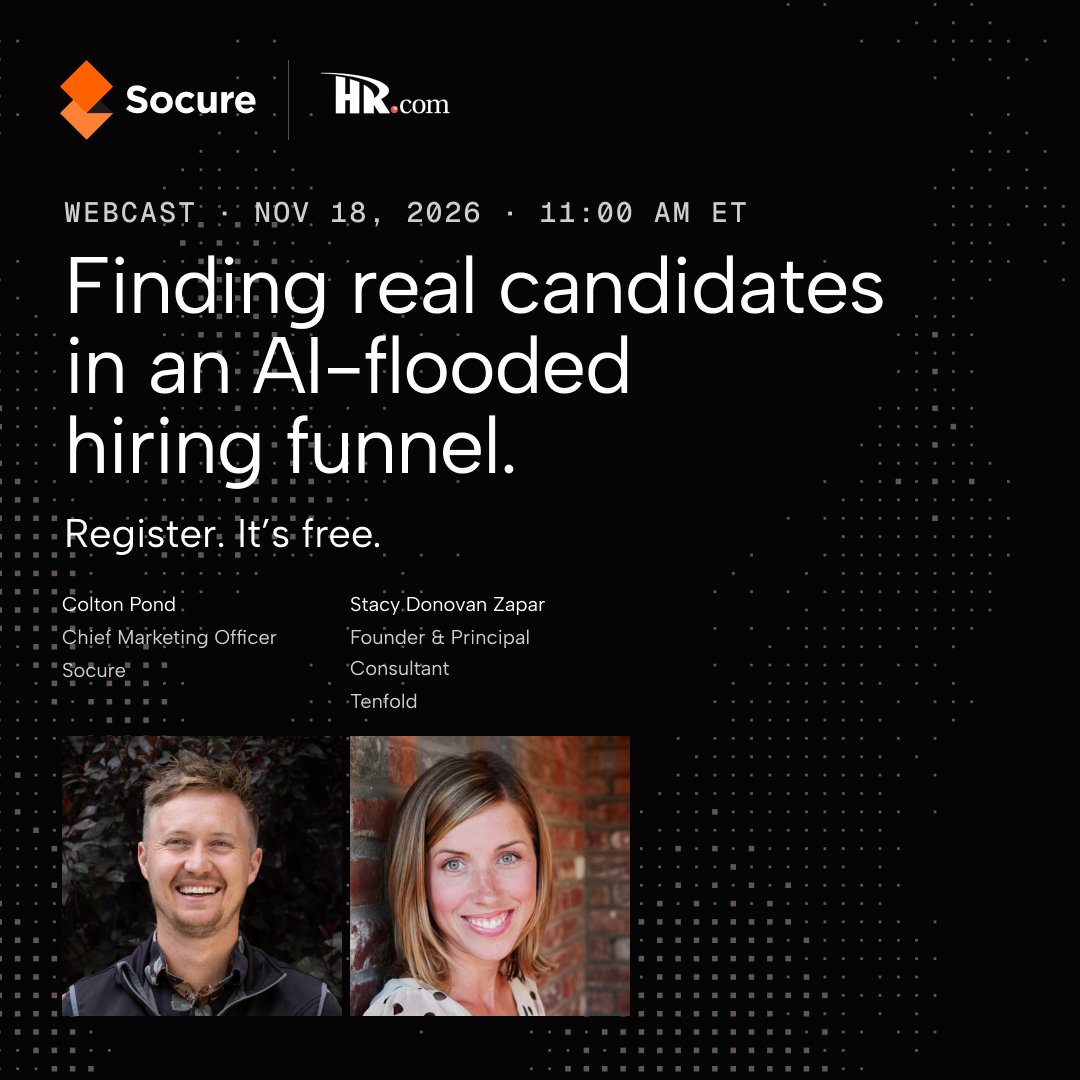
If you’re on a talent or security team wondering whose job this actually is, this session answers that too.
Nov. 18, 11am. Save your seat: https://t.co/JxTV0LGy4l
Your hiring funnel is now a fraud funnel too.
AI-generated applications. Bots. Impersonation. Synthetic identities. All moving through the same pipeline as your real candidates. ⬇️
The usual fix, a stronger background check at the end, happens too late. By then, a bad actor already cost a recruiter’s time, took a real candidate’s slot, and sometimes got the offer.
In 2 days, our CMO Colton Pond joins Stacy Donovan Zapar, founder of Tenfold and Fraud Squad, to break down where the funnel actually breaks:
→ Which moments are worth adding friction
→ Which aren’t
→ How to authenticate the person, not just the paperwork
The playbook for trust in digital assets is still being written. We’re bringing together the people shaping it.
Sol Noir. An intimate dinner were co-hosting with @WalletConnect , during Breakpoint London.
Nov 16. 30 seats. Invite-only.
What gets decided at a 30-person table shows up on a stage a year later.
Request your seat ⬇️
The Binance hack wasn’t an inside job. In June, an engineer downloaded a tampered AI coding tool installer. Binance caught it, but attackers had already mapped the wallet infrastructure team.
More than half of AI-Fluent Fraudsters show no evidence of committing fraud without AI.
AI isn’t just making existing fraudsters faster. It’s turning ordinary people into fraudsters.
That’s fraud’s Napster moment.
New report from Socure. ⬇️
Built on the same identity graph behind 11B+ identity decisions a year. An agent stops being an anonymous session it becomes a known entity, attached to a known person, with history. 🔗 https://t.co/uwsmGT6oqg
More than half of internet traffic is now agents.
Introducing Agent Intelligence: detect AI agents, score whether to trust them, and tie each one to the person or business behind it. @SocureID ⬇️
Crypto super apps hit $600B in volume this year, up ~100x. Buy bitcoin. Swap into a stock. Trade a perp. Bet on a game. One login, endless regulators. We asked @okx , @eToro , @kucoincom how they’re solving for it. Full report by @TheBlockCo x @SocureID ↓