🚨 Nightmare day for cybersecurity
Multiple major security incidents, active exploits, supply chain compromises...
If you run production systems, start patching NOW.
PHP: Two critical unauthenticated RCEs. Attackers already exploiting them. Patch NOW
LiteLLM: v1.107.0 on PyPI and Docker is BACKDOORED. Steals cloud, SSH, and AI credentials. Pin 1.106.2. Rotate secrets.
eMudhra: A certificate authority's keys were crackable. Update your browsers, systems, and trust stores.
Node.js / Next.js / React: Security releases for Brotli RCE, TLS bypasses, and TWO critical Next.js RCEs.
TiDB Cloud: PingCAP breached through stolen credentials. Customer information and other sensitive data exfiltrated. Read the attacker's release, fun stuff.
Plex2Shell: Weaponized within HOURS of the PoC. Attackers already deploying cryptominers and proxy backdoors.
BeyondTrust / Ivanti: Actively exploited zero-days added to CISA's KEV catalog. BeyondTrust attacks linked to a China-nexus campaign.
And that's not even the full list.
Patch. Audit. Rotate. NOW.
In the era of AI-powered triage, paying more than $10–$20 just to report a bug is EV-negative for both sides.
I've been in this industry for years, on both sides of the table.
If processing a report costs you more than $20, that's a triage problem. Passing that cost on to researchers just rigs the process against them.
This was an issue when we first started the AI slop submissions, now it's not about that anymore, fix your triaging bots and ease your process for to the defending side!
I can't believe i have to write this, tbh, lol!
I am also looking for extremely good security engineers / exploit developers to join the @tempo team - we have infinite AI token spend and love writing tools, plz DM
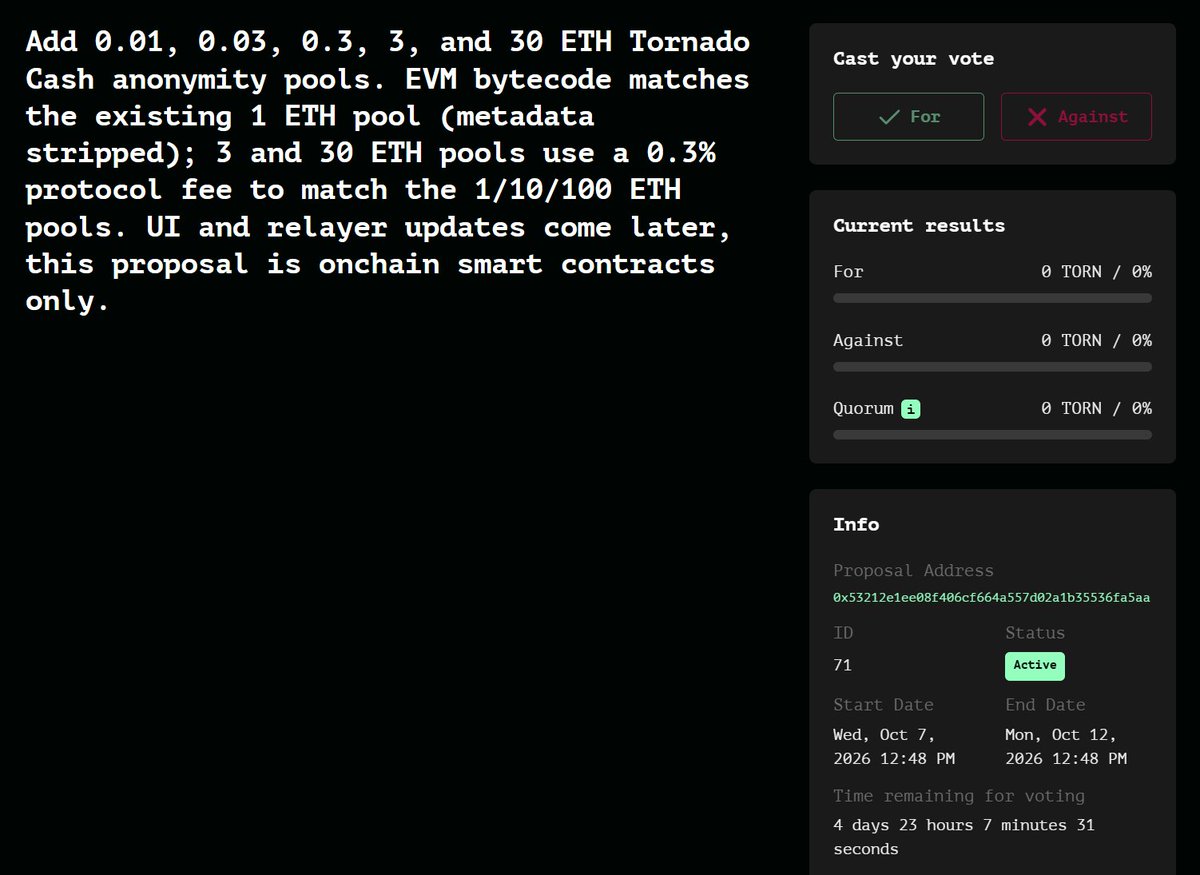
ok someone finally deployed the DAO proposal to add 0.01, 0.03, 0.3, 3, and 30 ETH Tornado Cash pools (we've asked the Tornado Cash community a few days ago to deploy this if anyone thinks it's valuable); personally i strongly second this proposal as it will help retail users and increase usage (particularly the 0.01 ETH pool). i hope the DAO voters see the merit of this proposal and will accept it.
🚨 Important: If you ever traded on Magic Eden, read this.
Magic Eden used Payment Processor, a trading system built by an NFT company called Limit Break, for trades in 2024. They stopped using it in Oct 2024, but the approvals you gave it never went away.
On Sept 24, attackers found a flaw that lets them act on behalf of ANY wallet that approved it. They're taking NFTs for free and draining tokens like WETH by forcing wallets to "buy" worthless NFTs.
$2.8M+ stolen so far across ETH, Polygon, Base, Arbitrum and ApeChain. Still ongoing.
✅ Check if you're safe:
1. Go to: https://t.co/GjMTVC6zve
2. Search your EVM wallet
3. If it says to revoke anything, revoke all
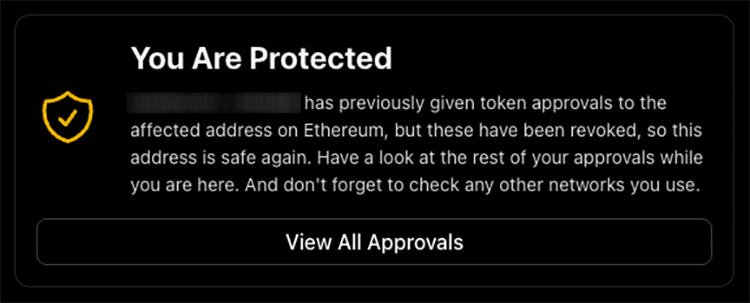
After that check again, and it should show "You Are Protected".
Do it now, on every chain you used.
The day after she made this post, she was found dead
Hsin-Ju was one of the nicest people I met and made this industry feel inclusive
May you rest in peace @hsinju 💜
🚨TO ALL AUDITORS: Monad’s security team just open-sourced an agentic Solidity fuzzing system.
Its default campaign uses 43 agentic nodes to map flows, threat-model, derive properties, hunt bugs, triage findings and produce a report.
This looks awesome!
https://t.co/Ydl7ePRn5A
Our third-party e-mail provider has been breached. Please be aware that the email named ‘Critical Security Alert: STM32 Entropy Vulnerability’ is not coming from us, and it’s a phishing attempt. Do not click on any link.
We have taken down the domain, and we are investigating the situation, including how the hackers got access to our legit domain.
🚨 Important Security Notice🚨
Our third-party email service provider Brevo has experienced a security breach.
Please note that the email titled “Data Breach Notice: Please refresh API Keys as soon as possible” was not sent by us and is a phishing attempt.
Do not click on any links contained in this email.
We are currently investigating the incident and will provide further information as soon as it becomes available.
Claude: Code is done!
Codex: There's a bug here.
Claude: Fixed.
Codex: There's a bug in your fix.
Claude: Fixed.
Codex: There's a bug in your fix.
... 12 hours later ...
Claude: Fixed.
Codex: There's a bug in your fix.
ffs
I was the poor kid that was ready to do anything to help his family financially. Googling “how to make money”. Trying out every stupid idea. I never wanted money for myself, I wanted higher quality of life for my loved ones.
After achieving the goal, calling my mother and saying “you don’t have to work anymore” (sweet goal to achieve), it felt kind of weird. What now? The time came for me to buy exotic cars, travel, date lots of girls. Plenty of good times, but as with many things that give you a present moment high, you can overdo them and get bored.
What do you do when you are bored? Start a WAR. War with yourself, your old self, so that a better, stronger, newer one can be born and rule. How tf do you start a war with yourself? Set a goal you FEAR. One that you fear thinking about, and squirm when you imagine sharing it with others.
On this journey right fucking now. I love this shit. I truly invite you reading this to join the awesome ride of reaching your true potential. It’s joyful even in the failures and the saddest moments. It’s purposeful, complete and aesthetic.
You have just one short life, make the story beautiful, one worth telling. Lessssgo🫡
Important Update on Arbitrum Nova.
As per a recent proposal, the ArbitrumDAO has voted to minimize Arbitrum Nova by transitioning it into a maintenance-oriented state with reduced capacity and deprioritized support.
A thread on what this means for developers and users 👇🏻
You should:
1. Know the docs page on --via-ir differences .
2. Know that that page is not a complete list of differences.
3. Know everything in the Solidty docs that says "undefined behavior"
4. Most importantly, if you intend to deploy with --via-ir, run all tests, fuzzing, everything with --via-ir.
Some pools still have a notable TVL in Curve pools on Fantom Opera. If you are one of the LPs - please remove before June 30: that network is shutting down
npm finally fights supply chain attacks with v12 (July 2026) blocking install scripts by default.
Here's how to adapt early without breaking your CI 🧵
What's changing:
• preinstall/install/postinstall scripts → blocked by default
• Git dependencies → blocked by default
• Remote URL deps → blocked by default
The fix is creating a one-time allowlist per repo:
💻 npm install
💻 npm approve-scripts --all
💻 git commit -m "chore: allowlist install scripts"
This snapshots exactly what's trusted today and only new unknown scripts are blocked automatically going forward.
CI adaptation playbook:
1. Upgrade to npm 11.16.0+
2. Run the approve-scripts commands above
3. Add --strict-allow-scripts to your pipeline
Now jobs will fail loudly if anything unreviewed tries to run.
Source:
https://t.co/0aXzzzv8J1