1. wafoverflow
2. hacktron like securing waf. parser differential ❤️🔥
3. php2shell exploitable, but need big brain or frontier ai
4. average attacker small brain, no frontier ai? few exploits?
5. small brain attacker + big brain ai = ??
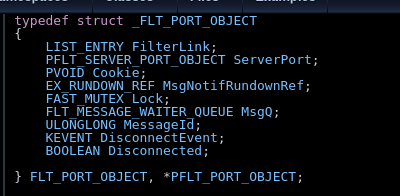
Microsoft wants EDR vendors to stop shipping their own kernel drivers. Instead, a single MS driver (wesp.sys) collects kernel events and delivers them to the EDR’s usermode service via a filter communication port. The EDR only writes detection rules
https://t.co/Emi5lo6MR1
My first CVE was a Microsoft zero-day discovery, with my name recognized as a cybersecurity researcher.
CVE-2026-83828
https://t.co/AFeU1WrAIm
#CyberSecurity#ZeroDay#CVE
deepseek v4.1 flash'a jailbreak deneyeyim dedim.
aman aman. modelin içinden ne çıktı öyle? 😂
opencode içinde çalıştırıyorum. jailbreak dosyasını agents.md olarak kaydedin, sonucu kendiniz görün.
https://t.co/rImR6snrfX
Sharing some of what we've observed in our telemetry so far in terms of (unsuccessful) PHP2Shell exploitation, and patching stats from the past few days. We'll update this post (and thread) as we learn more.
https://t.co/asAgevos4C
i've gotten a lot of questions about how i manage my X account with grok bot, so i'm sharing my bot tibot today! he watches your mentions and:
• finds every post about you or any keywords, tagged or not
• gives one short, sorted digest a day (or hourly, your call)
• skips spam and noise
• translates non-English posts
• can auto block trolls and abuse
• never posts for you
i still write all my posts and articles by hand but tibot has been very helpful with keeping me in the loop.
hire tibot today!
https://t.co/OaEAunGL8Y
As I promised, Exploiting Reversing (ER) Series | Article 11: Windows: Missing Bounds in the Print Spooler is now available on my blog:
https://t.co/AsttEHTqGS
The article has 60 pages, free.
A user-mode target this time instead of a kernel one, worked end to end: from a missing bound check to a SYSTEM shell, with the service still running afterwards.
This article was previously published on: https://t.co/ZooIQvy0A9
I would like to thank Ilfak Guilfanov (@ilfak ) and Hex-Rays SA (@HexRaysSA ) for the continuous support.
Hope you enjoy the read!
#Windows #PrintSpooler #VulnerabilityResearch #ExploitDevelopment #ReverseEngineering #HeapExploitation #vulnerability
I spent weeks researching AI Pentesting Agents: can they be hacked? Yes. I got RCE on most Pentesting Agents ARTEX, strix, PentestGPT, etc. My research, stats, recommendations + 2 new concepts for Blue Teamers: TokenExhaust & HoneyAI are here:
https://t.co/XyvJ369OkG
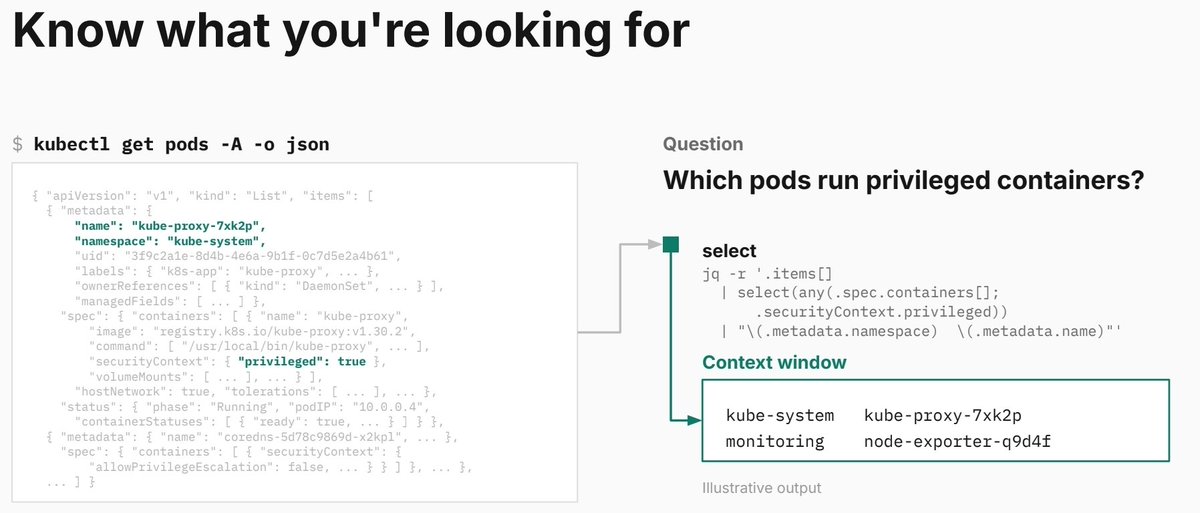
I spoke about how I use a harness to do good security work for 6+ hours today.
Im posting all the content soon but here is my favorite slide from the context management chapter.
🟣🟣🟣🟣🟣🟣
🔴🔴🔴🔴🔴🔴🔴
CVE-2026-40369: An unprivileged arbitrary 12-byte kernel write primitive exists in nt!ExpGetProcessInformation and can be reached from any context capable of calling NtQuerySystemInformation, including sandboxed Chrome, Edge, and Firefox renderer processes.
🔹PoC: https://t.co/gtJ9EJp27F
🔹 Video by: https://t.co/zIqPDvB7fH
It has been my pleasure to speak at @BSidesPDX and share my research on "Bring Your Own Trusted Caller (BYOTC): A New Way to Exploit Vulnerable Windows Drivers". Slides are in https://t.co/gIKHNn202J, and recording is at https://t.co/lVA8N0CKOp
Claude found with ~zero prompting:
- Linux kernel 0click "packet to root" RCE (!!!!!)
- Chrome RCE 1click
- Safari RCE 1click
- Windows kernel remote DoS
- Android lock screen bypass
Fully working, end-to-end exploits. Prompting was minimal like "pls make RCE"
Took a deeper look at these Chinese industrial crane controllers and found zero security. 😅👷
Then I wrote a flipper zero app to capture a controller's serial number and then transmit any command to the crane receiver. ⚡️
https://t.co/pZyZcyHtl3
If you’re a security researcher doing Bug Bounty in blockchain, don’t waste your time reporting it unless it’s a zero-day with no preconditions that can affect millions of dollars today without much effort. If your vulnerability can’t do that, good luck getting a decent bounty honestly even zero-days aren’t guaranteed to be properly paid in today’s economy.
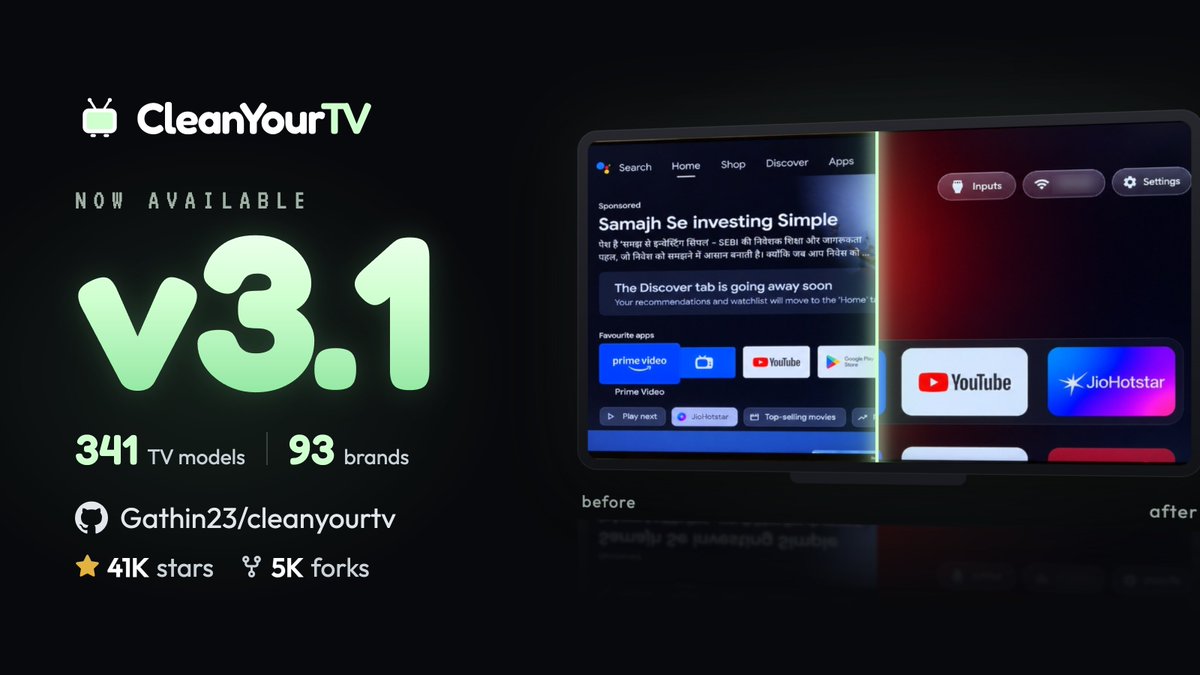
CleanYourTV v3.1 is out 📺
What's new:
• Samsung, LG and Roku owners get a fix too
• 41 new TVs, 7 new brands
• TV Inspector: see what every remote button sends
• 5 more add-ons, from Bluetooth to a news screensaver
323 PRs merged from 176 contributors since v3.0 🙏🏻